The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Performed a read-only Microsoft 365 security assessment for an 11-user UK logistics company, uncovering two Critical findings: MFA disabled on Global Administrator accounts and an active email forwarding rule on the Finance Manager's mailbox consistent with Business Email Compromise. Delivered a clear priority action plan, all remediable within 72 hours using tools already included in the client's existing M365 licence along with SharePoint sharing controls and Conditional Access policy configuration to close legacy authentication gaps.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Related posts

Casemate: making malware analysis feel calm instead of scary
Cybersecurity websites usually look the same: black background, green code, a hooded guy. I wanted to try the opposite for Casemate, a concept for a malware analysis tool.
The idea is simple: the product keeps a suspicious file in a sealed chamber and watches what it does. So I put a bug frozen in amber in the middle of a canyon. It’s dangerous and under control at the same time, and you get it without reading a word.
Then I made sure the page still works for a security lead who wants facts. The stats sit right next to the headline: threats isolated, latency, endpoints covered.
The hardest part was keeping it warm without losing trust. I stayed with one terracotta colour, wide capitals and mono labels, so it reads like a serious tool and not a poster.
I’m taking on new projects for SaaS and tech teams. If you have a product that’s hard to explain in one glance, send me a message.
What do you think, would you trust a security product with a canyon on the homepage?


I love it! It feels so calm, and I would definitely try it! This is amazing, Kris. I never thought cybersecurity could be this cool ❤️🔥

Instructor wise students dues analysis. Organisation head can easily define the weakness and take decisions.
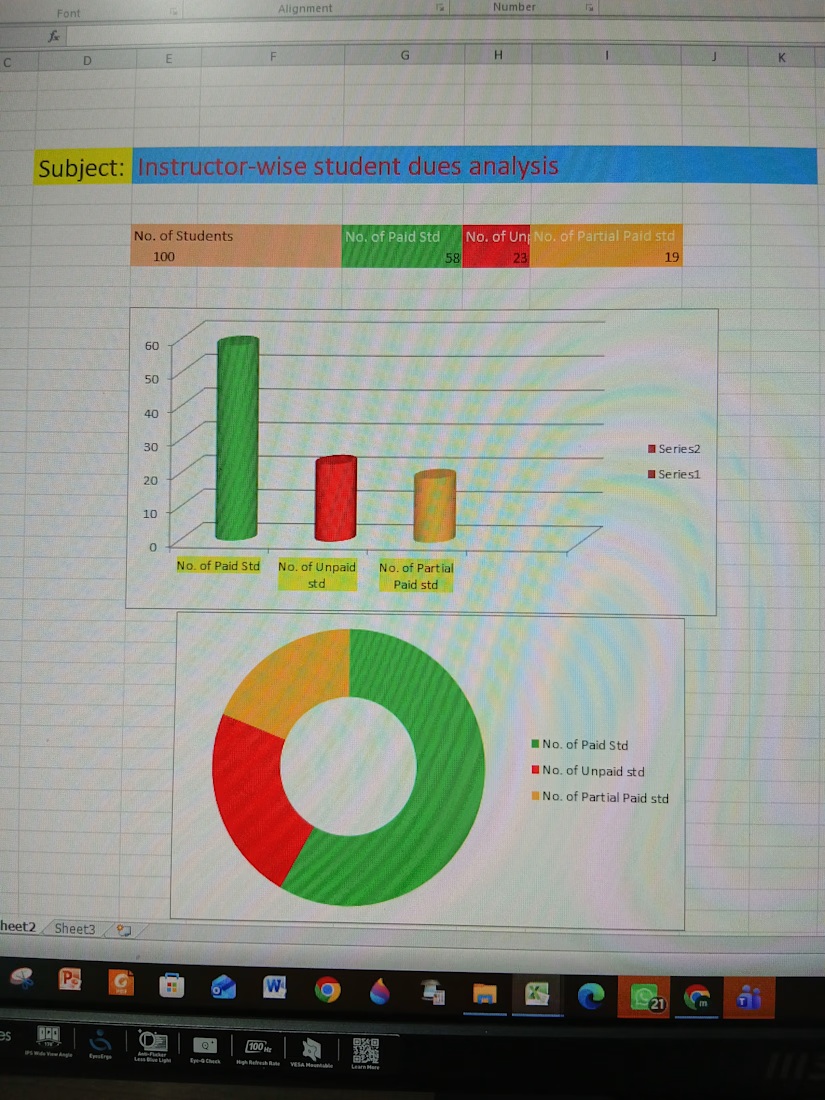
My first work😊
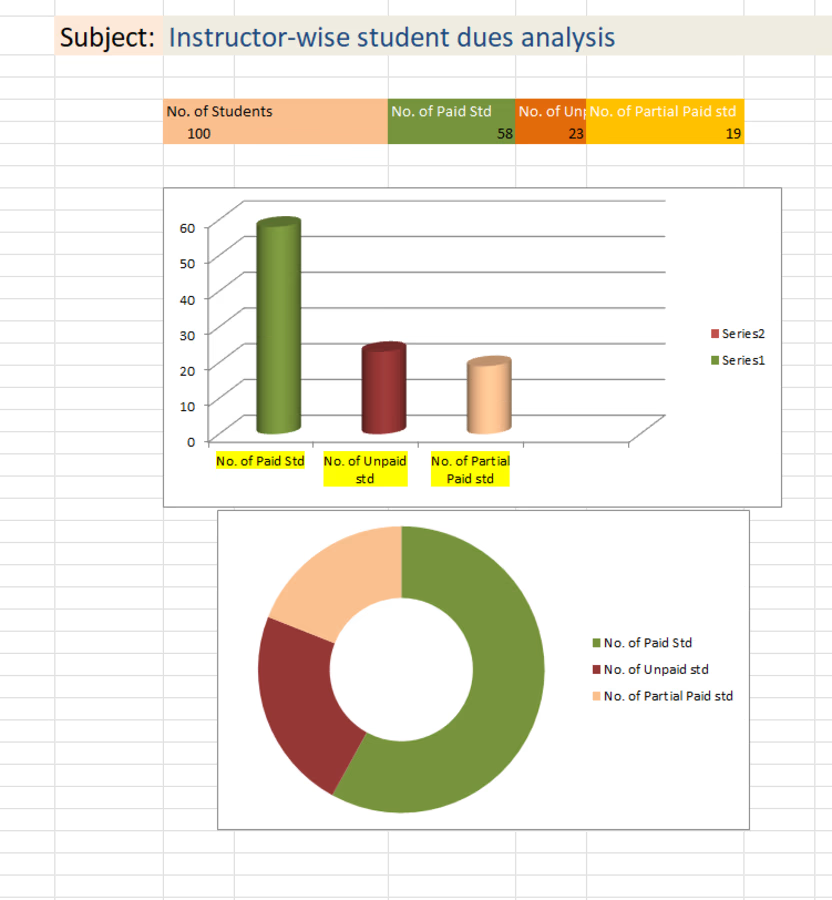
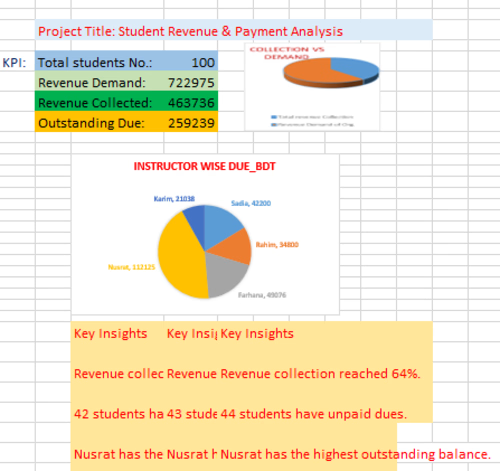
Analyzed a dataset of 100 students using Microsoft Excel to evaluate revenue collection, outstanding payments, and instructor-wise performance. Created charts and a dashboard to visualize key findings and provide actionable recommendations for improving payment recovery.