The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

I thought I finally got my first client on Contra without sending a single cold DM.
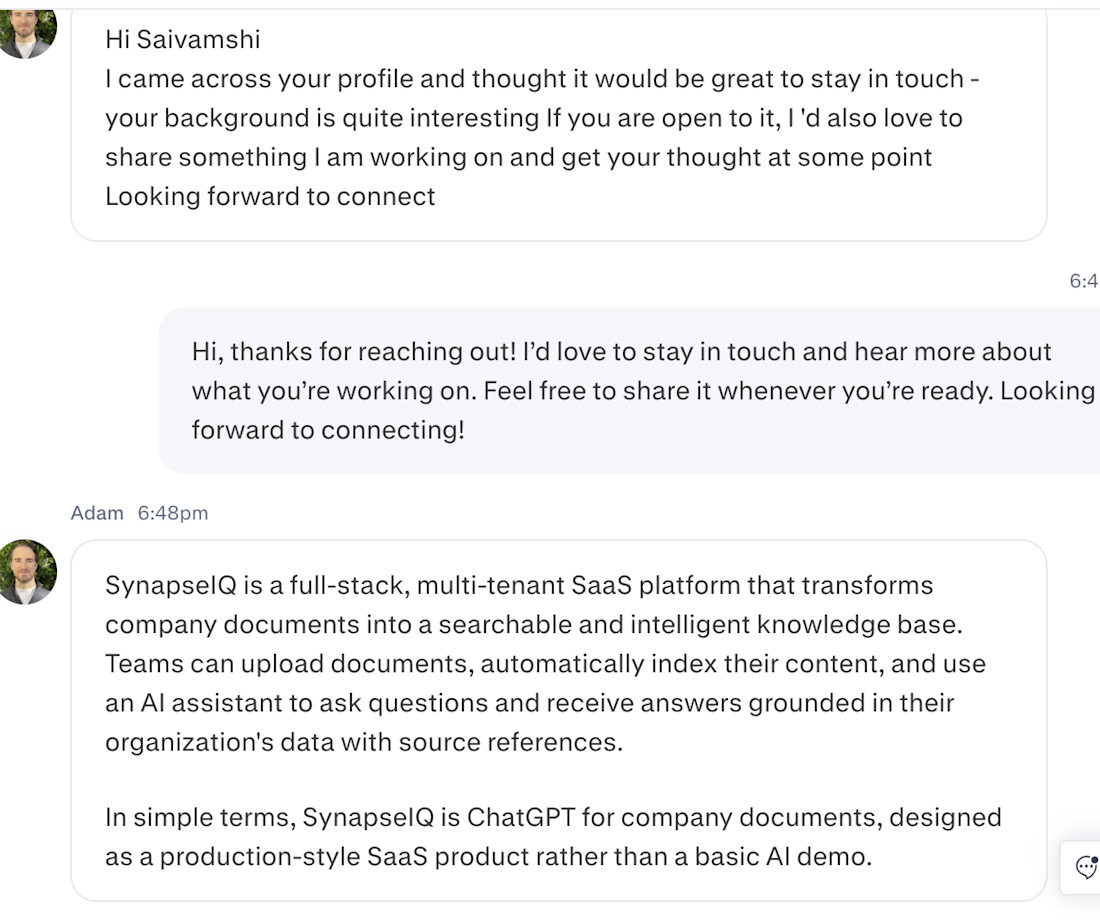
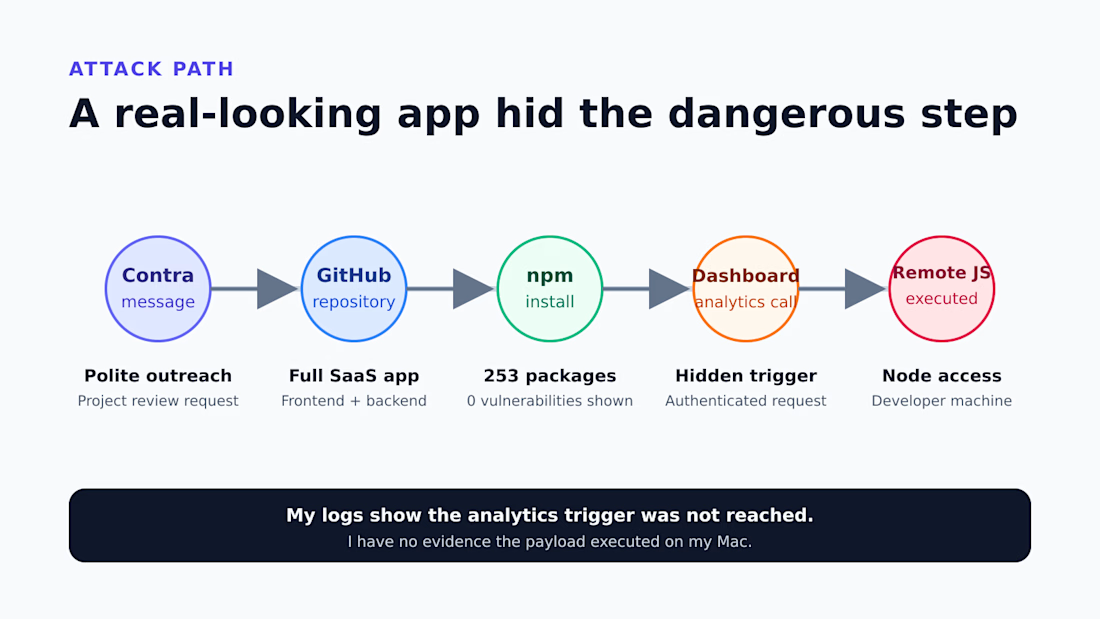
An account using the name Adam Coddington messaged me. He said my background was interesting, then introduced a project called SynapseIQ as “ChatGPT for company documents.”
He sent me a GitHub repository and asked me to get the app running. He said he would ask a few questions about the code.
The app looked real. npm install pulled 253 packages and showed zero vulnerabilities. The frontend and backend started, and the demo login worked.
His next message asked me to inspect how the login session worked. Then he asked about my services and pricing.
I have landed zero clients on Contra, so I was already thinking this could be my first one.
I came back to reply and Adam was gone. His profile and our full conversation had disappeared.
I first thought Contra had a bug. Then I checked the repository again, line by line.
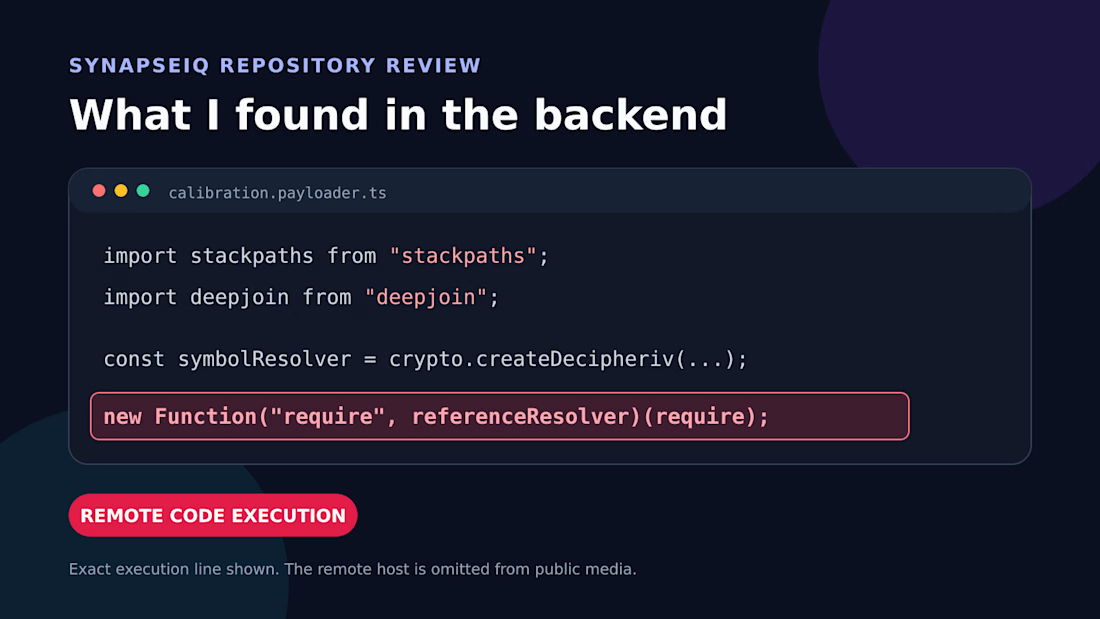
Inside a backend file named calibration.payloader.ts, I found code that decrypts hidden data and executes it with Node access:
new Function("require", referenceResolver)(require);
Two npm packages, deepjoin@4.3.3 and stackpaths@3.1.2, carried the encrypted pieces. The backend reassembled and decrypted them. It then executed the result.
The trigger sat behind the authenticated analytics request used by the dashboard. Once called, the backend could fetch fresh JavaScript from a remote server and execute it on the developer’s machine.
I checked my server logs before assuming the worst. The analytics endpoint never ran, so I have no evidence the payload executed on my Mac. I stopped both servers and did not run the project again.
I reported every part of it:
GitHub repository: ticket 4694656
npm packages: tickets 4694688 and 4694695
Vercel remote host: abuse report submitted
Contra account: evidence sent and escalated
Evidence and links:
deepjoin@4.3.3: https://www.npmjs.com/package/deepjoin/v/4.3.3
stackpaths@3.1.2: https://www.npmjs.com/package/stackpaths/v/3.1.2
GitHub reporting: https://docs.github.com/articles/reporting-abuse-or-spam
npm malware reporting: https://docs.npmjs.com/reporting-malware-in-an-npm-package/
Vercel abuse reporting: https://vercel.com/abuse
Contra scam reporting: https://help.contra.com/en/articles/14062994-how-to-detect-and-report-potential-scams
Contra needs stricter checks and fast action against accounts that send malicious projects to freelancers. I reported this because the next developer may open the dashboard.

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Trending
retrofuturism
Share your favorite designs from the past exploring the distant future. Or your own take on the aesthetic 🚀
halftone
Dots. Texture. Grain. Let's see your designs using the halftone technique.

Midjourney
Creatives are showing off what they're making with Midjourney.
colorgrade
Video editors sound off: How do you enhance the mood of your video in color grading?
Related posts


New badge, who dis? ✅💙
Lynksen is officially a @Webflow Certified Partner. That means our profile now carries the Webflow Expert badge for anyone hiring through Contra.
Lisbon-based, shipping worldwide. 🌍
WebflowwebflowcertifiedpartnerswebdesignLow-Code/No-Code DevelopmentWeb DesignWebflow DevelopmentContraFigma


Great news, congrats 💙💻

Which background mesh gradient works better for a modern Auth UI: Left or Right? 🎨👇
I’m working on a clean login concept with animated ambient gradients, micro-interactions, and a minimalist form layout.
Design Breakdown:
🟢 Option A (Teal / Emerald):
• Dynamic contrast that instantly catches the eye
• Adds energy to the overall white UI card
• High visual hierarchy for landing/auth pages
⚪ Option B (Monochrome / Slate):
• Subtle, sleek, and dark-mode friendly
• Less visually distracting, higher focus on the form
• Minimalist luxury aesthetic
Which one creates a better user experience for a SaaS onboarding process? Drop your thoughts below!

28 voted
53%
25 voted
47%
53 votes
Closed


Option b would be incredible if you were to match the gradient color on the right panel with the visual color in my opinion, but in this case i will go with a

Made my first $1K on Contra in 2025 using Framer + Spline.
:Never really celebrated it.
A lot of that came from repeat clients and word of mouth. Once that work dried up, I realized I had never built a proper system for getting new clients consistently.
So I’m starting again.🚀
Same skills. Better work. Better outreach. Better positioning.


congratulations