The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Pulled DNS on two real client domains this week for something unrelated, and the gap was stark. One had SPF and DMARC both set up properly. The other had no SPF record and no DMARC record at all, the root domain was wide open.
Here's why that matters for a store. Order confirmations, abandoned cart emails, and shipping updates all leave your domain constantly. Without SPF and DKIM, inbox providers have no way to confirm the mail actually came from you, so more of it lands in spam. Without DMARC, nothing stops someone from spoofing your domain in a phishing email sent straight to your own customer list.
Thirty second self check: look up a TXT record on your root domain, then look up a TXT record on _dmarc.yourdomain.com. No result on either one means you're unprotected.
The fix is usually quick. SPF and DKIM records come from whatever sends your mail, your store platform, Klaviyo, Google Workspace, and get added as TXT records through your domain registrar or DNS host. DMARC is a separate TXT record you add yourself, most people start at p=none to monitor traffic before moving to quarantine or reject.
Ecom Swift LLC

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started





Related posts


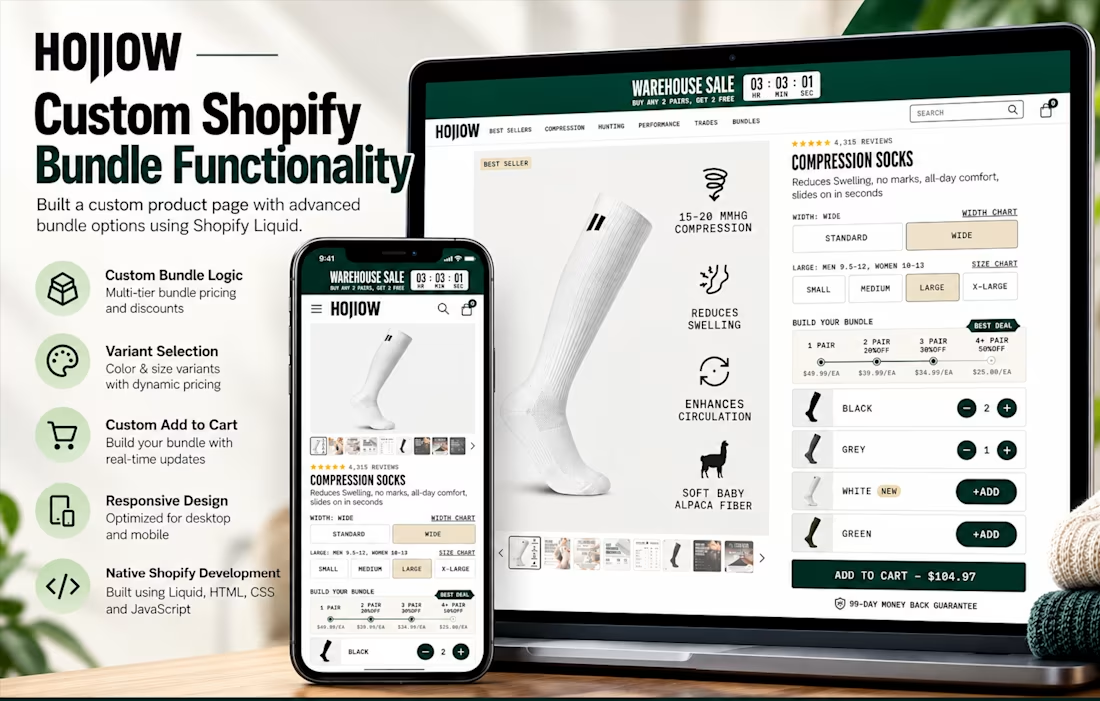
Multi-tier pricing that updates live as you add pairs is the hard part to get right in native Liquid, most builds either hardcode the tiers or end up calling an app API on every quantity change. Curious whether the discount math runs client-side off a price map or you're hitting a line-item script/function on the backend for it.

A Shopify homepage has a few seconds to answer one important question:
“Am I in the right place?”
A beautiful design helps, but the homepage also needs to guide the visitor toward the next step.
Here are 5 things I think every Shopify homepage should have:
1. A clear value proposition
Visitors should quickly understand what the brand sells and what makes it relevant to them.
2. A strong hero section
Use compelling imagery, a focused message, and a clear CTA instead of overwhelming visitors with too much information.
3. Easy product discovery
Featured products and collections should help shoppers find what they're looking for without having to search through the entire store.
4. Trust signals
Reviews, shipping information, return policies, guarantees, and secure checkout indicators can answer important questions before someone buys.
5. Clear navigation
Your navigation should make the store easy to explore. Customers shouldn't have to figure out where products or collections are hidden.
The goal isn't to put everything on the homepage.
It's to put the right things in the right order.
Good Shopify design isn't only about how the store looks. It's also about how easily someone can understand it and move through it.
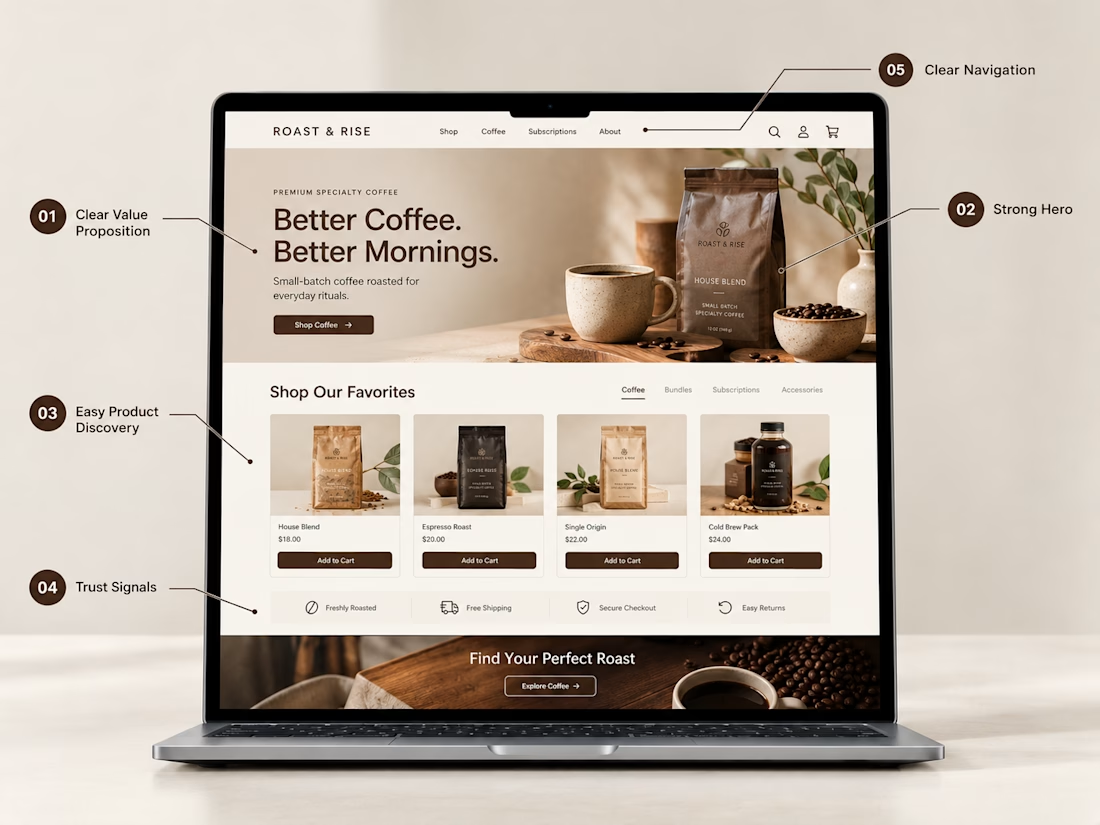

100% agree! A great Shopify homepage is not just about design—it’s about clarity, trust, and guiding customers to the right next step. 👏

Hi Contra! I’m Daniyal, an SEO specialist working with e-commerce and service businesses.
Lately, I’ve been focusing on a problem I see often: businesses publish more content, but the pages that could bring in customers still have technical issues, weak internal links, or unclear search intent.
My work starts with finding those gaps, then fixing the pages that matter most. I work across technical SEO, content strategy, and Shopify and WordPress sites.
If you’re working on an online store or a service website, what’s your biggest SEO challenge right now? I’d be happy to share a practical suggestion.
Great approach. Fixing the right pages can make a big difference in SEO.