The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

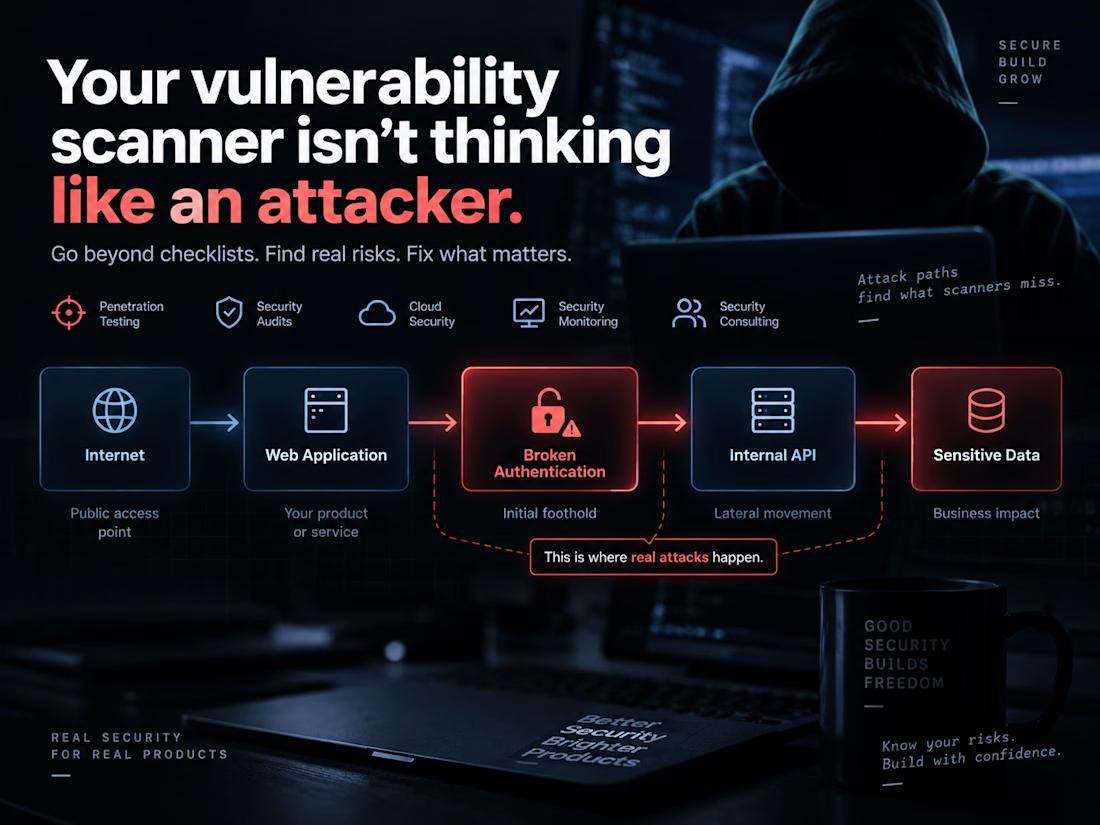
Most companies don't need another 80-page security report.
They need someone to tell them:
What can actually be exploited?
What could it cost us?
And what should we fix first?
That's the difference between checking a cybersecurity box and actually improving your security.
When I assess an application or infrastructure, I'm not interested in filling a report with 50 low-impact findings just to make it look impressive.
I care about attack paths.
→ Can authentication be bypassed?
→ Can one compromised account lead to something bigger?
→ Are APIs exposing data they shouldn't?
→ Can permissions be chained into privilege escalation?
→ Are cloud or infrastructure misconfigurations creating an easy entry point?
→ Would your monitoring actually notice an attacker?
And most importantly:
What should your team fix first?
That's the approach I bring to cybersecurity work — whether it's penetration testing, security audits, SOC/security monitoring, or security consulting.
I'm currently taking on new projects through Contra.
If you're building a SaaS product, web application, API, or growing infrastructure and you're unsure how it would hold up against a real attack, send me a message.
I'll happily take a look at what you're building and tell you where I'd start.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started






Related posts


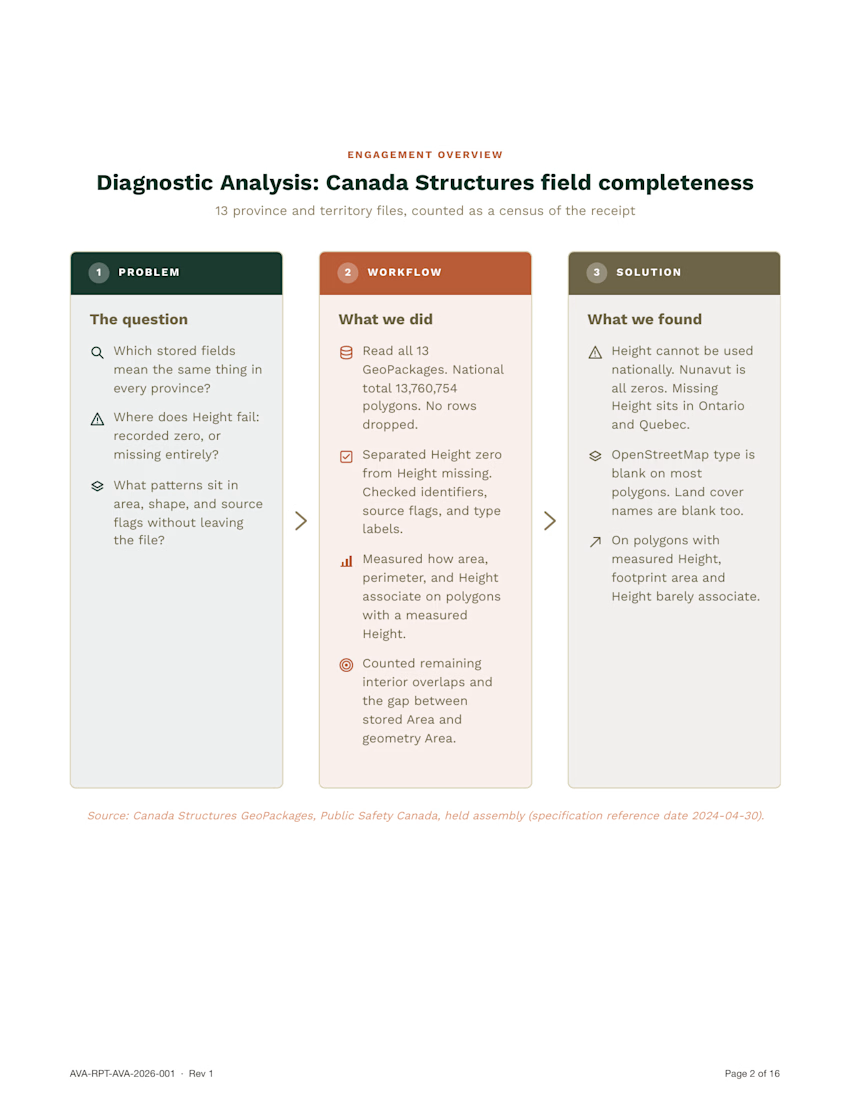
If you have ever been handed a dataset and wanted to know the integrity of the content, and any key information sitting inside it, you needed a descriptive analysis.
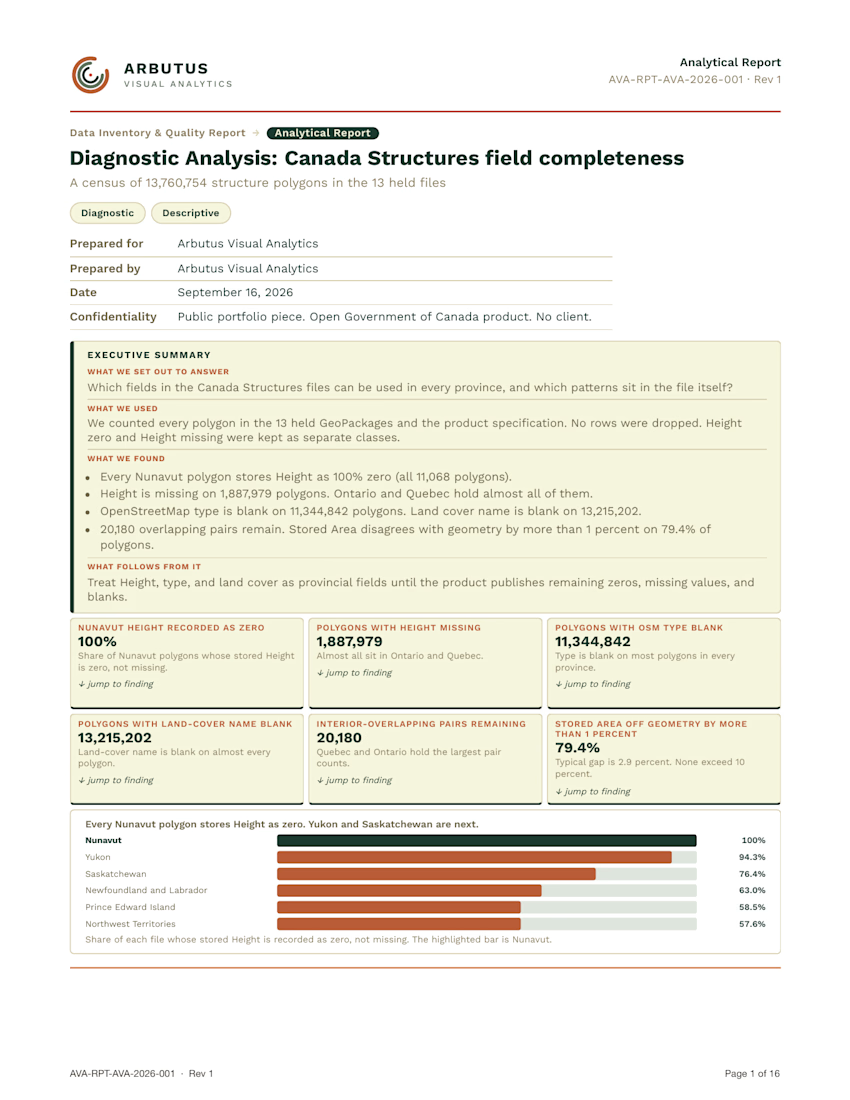
This is a descriptive analysis of Canada Structures, the federal building-footprint product. A file like this is assembled from several sources and file types, and that mix can leave artifacts. The work was looking for those artifacts so the file can be trusted before anyone treats stored height or type as national fields.
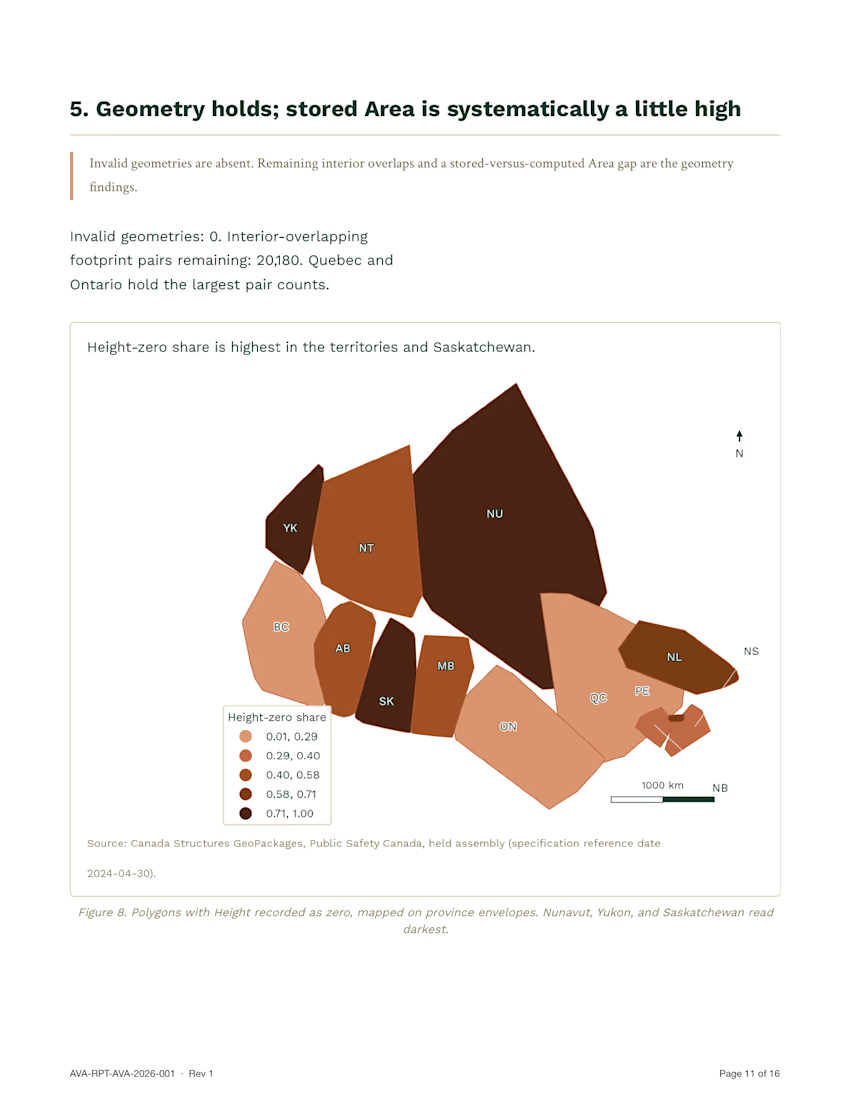
National count is 13,760,754, matching the spec. Every Nunavut footprint stores height as zero (11,068). 66.5% of footprints have a positive stored height. 82.4% carry no building type. Shape, size, and province together score 0.42 at guessing source class, against 0.32 from province alone.



A sneak peak to a B2B solution I'm building.


Sagini AI Analytics — AI-powered data intelligence platform (sagini.net)
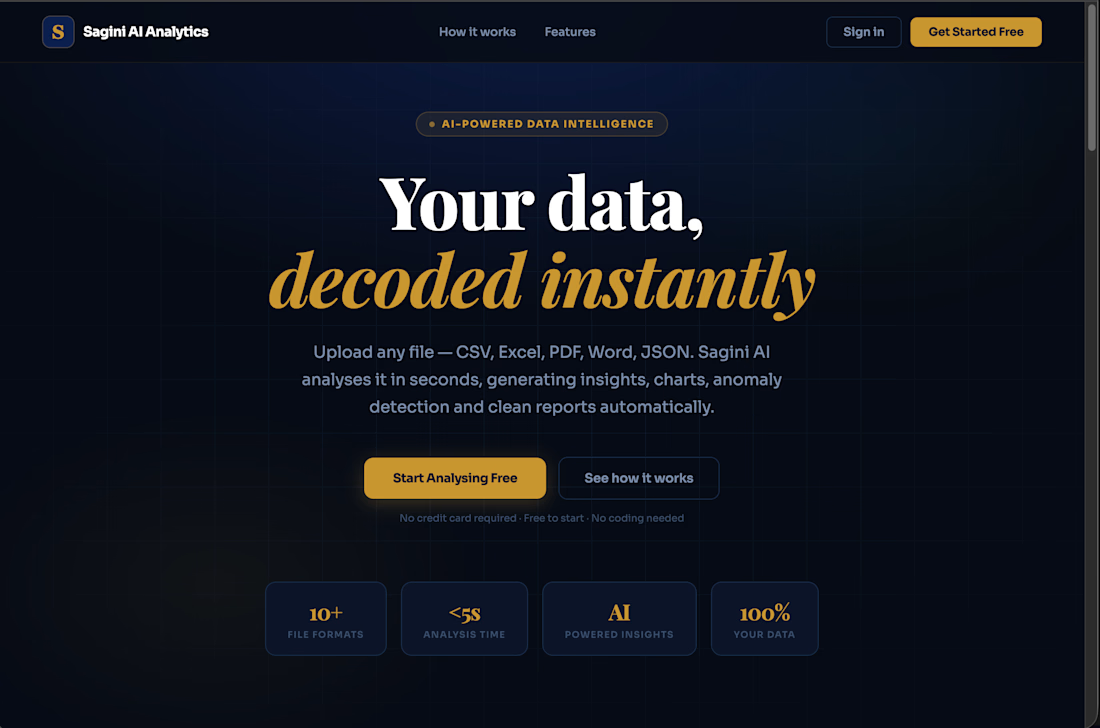
Designed and built the full marketing site for Sagini AI Analytics, a tool that turns any uploaded file into instant charts, insights and anomaly reports.
The visual identity here is deliberately different from a typical SaaS landing page. Instead of the common blue and sans-serif "tech" look, the site pairs a deep navy background with a warm gold accent and a serif display typeface for headlines. This gives the product a premium, editorial feel that signals trust and authority, fitting for a tool people use to make decisions on their actual data. Body copy stays in a clean sans-serif for contrast and readability, so the serif is reserved for moments that need weight.
The hero headline uses two different type treatments in one sentence: "Your data," in a solid serif, "decoded instantly" in a gold italic script. This creates a clear visual hierarchy and makes the value proposition the most memorable element on the page, rather than burying it in a paragraph. A trust bar directly below (10+ formats, under 5 seconds, AI powered, 100% your data) answers objections before the visitor has to ask.
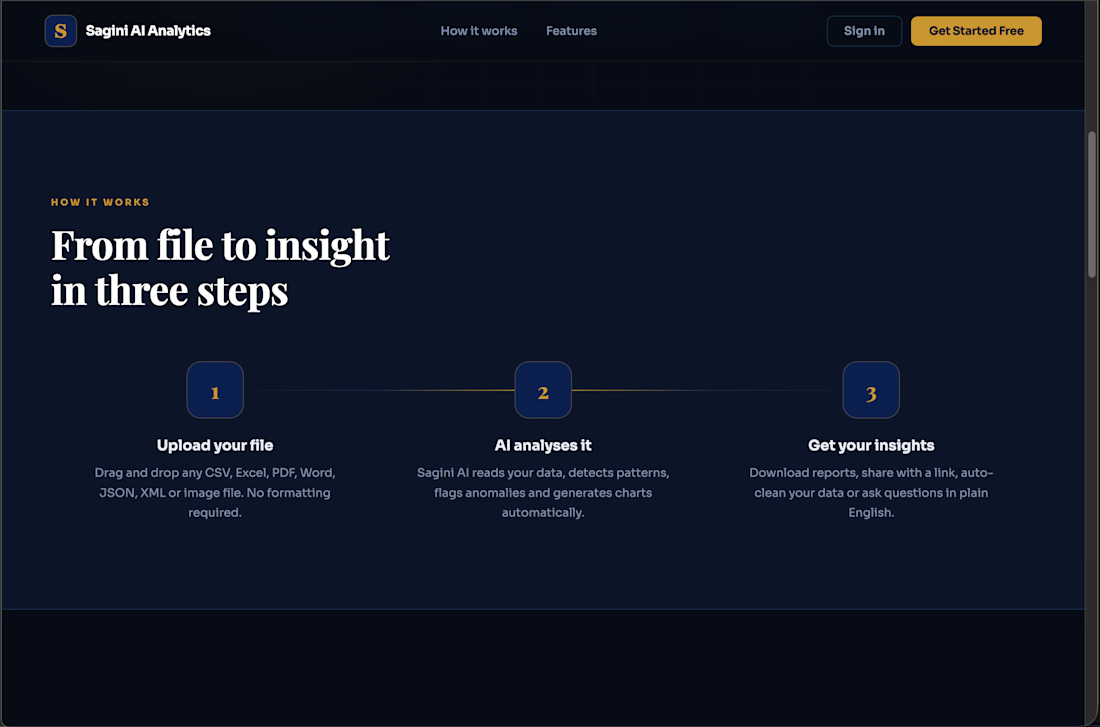
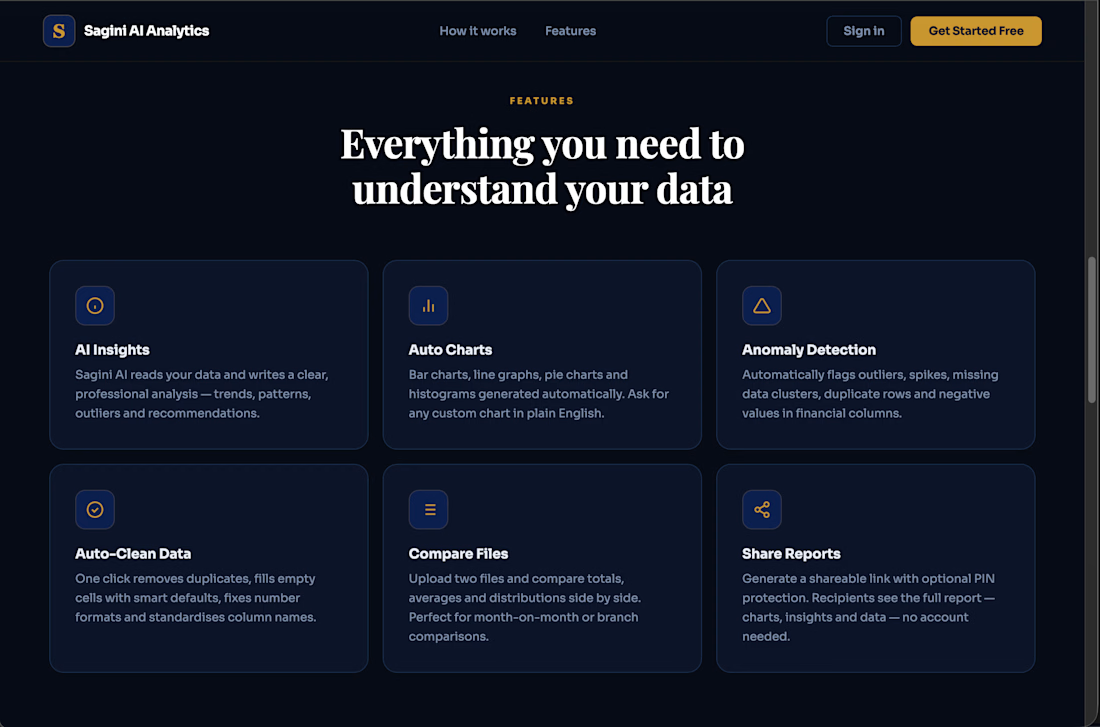
The "How it works" section uses a three-step numbered layout with a connecting line between steps, which reads as a literal pipeline rather than a bullet list, reinforcing the "file in, insight out" simplicity of the product. The features grid below groups capabilities into six equal cards with consistent icon and copy structure, making a technically dense feature set easy to scan.
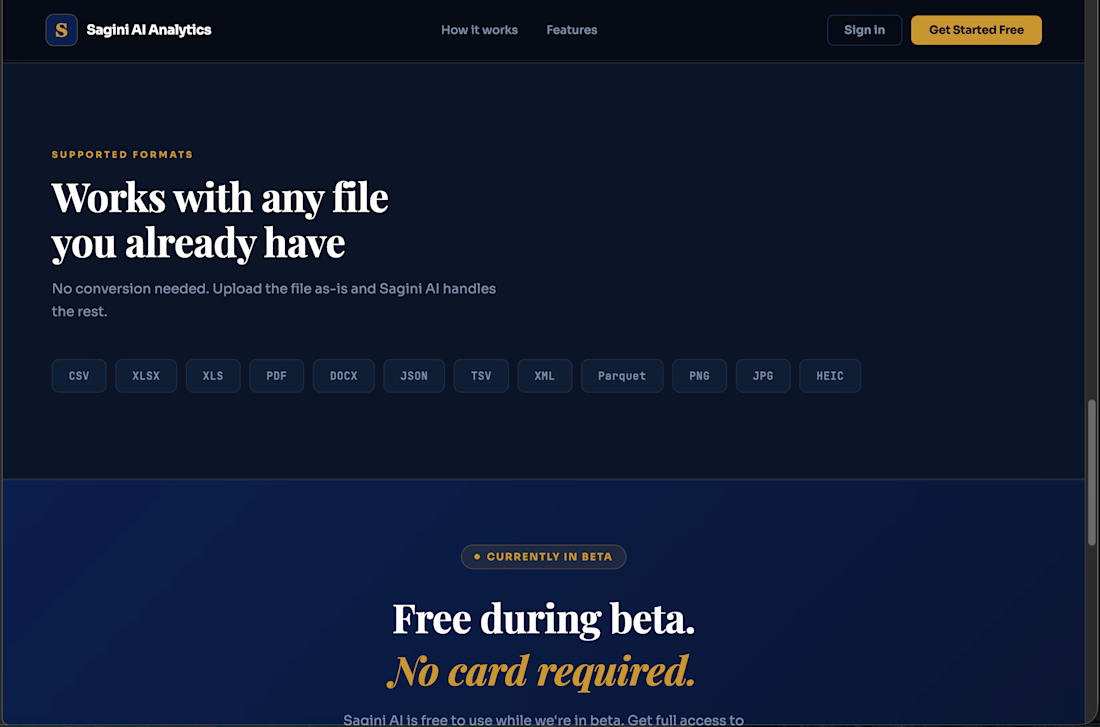
The supported-formats section replaces a wall of text with format badges (CSV, PDF, XLSX, PNG, and others), which communicates breadth instantly and visually rather than through a sentence a visitor would skim past.
The page closes with a repeated, high-contrast CTA block on the gold-accented navy background, plus an honest "Currently in Beta" and "Free during beta" disclosure, which builds trust rather than undermining it.
Stack: FastAPI, Python, Claude API. Deployed with nginx, systemd, Let's Encrypt SSL, MySQL.