
Do you actually own your website?
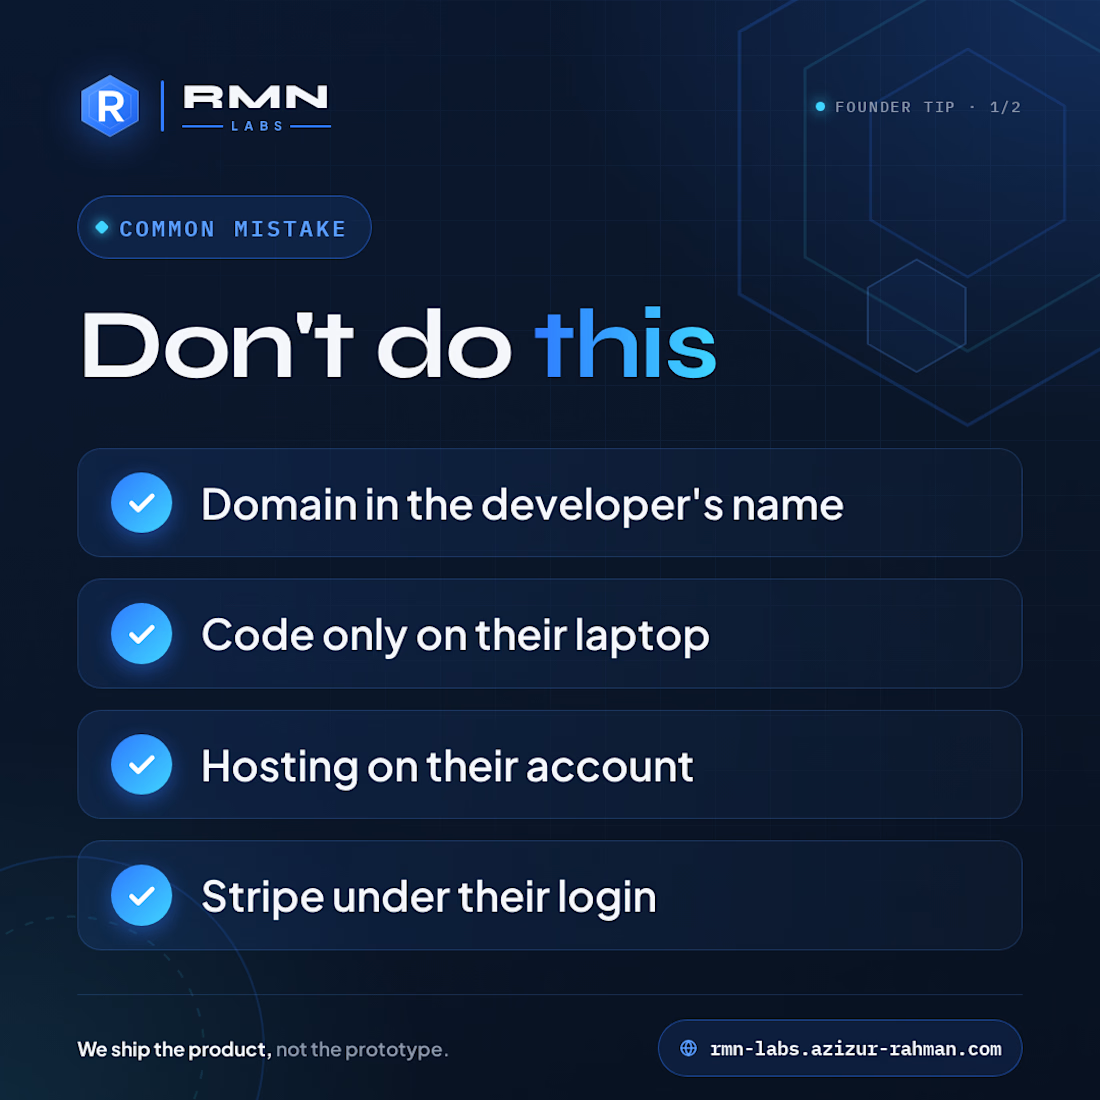
Many devs set up the domain, hosting, code and Stripe under their own logins, so the owner gets locked out later.
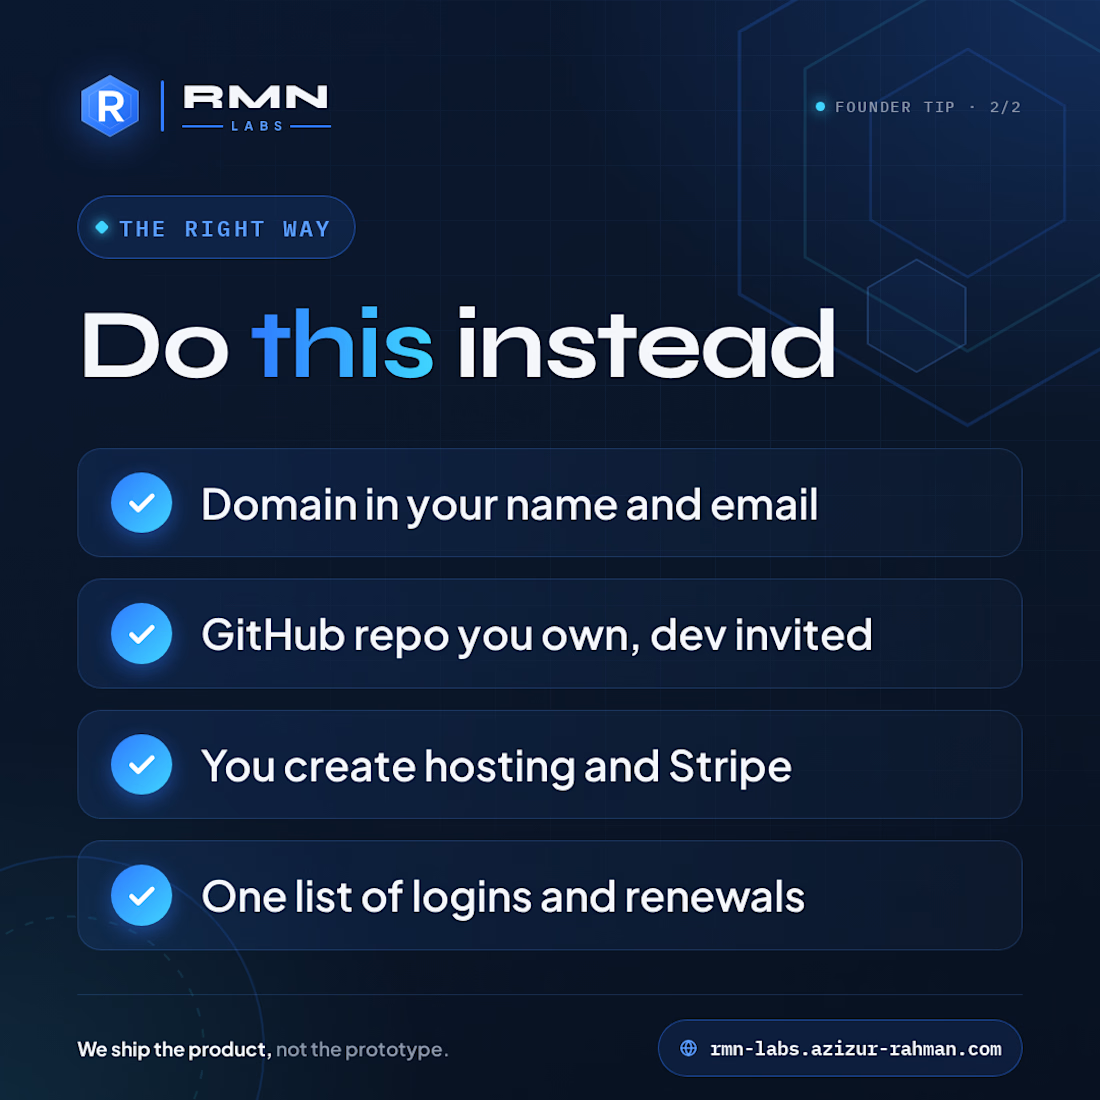
Do this instead:
1. Domain in your name and email
2. GitHub repo you own, dev invited
3. You create hosting and Stripe, then invite the...
Is your MongoDB query getting slower?
Most developers skip this step. Here's what we do instead. 1) No index on the fields you filter by means MongoDB scans every document in the collection to find a match. 2) Build an index that matches the query; for compound indexes, put...
Is your MongoDB query getting slower?
Most developers skip this step. Here's what we do instead. 1) No index on the fields you filter by means MongoDB scans every document in the collection to find a match. 2) Build an index that matches the query; for compound indexes, put...
Is your MongoDB query getting slower?
Most developers skip this step. Here's what we do instead. 1) No index on the fields you filter by means MongoDB scans every document in the collection to find a match. 2) Build an index that matches the query; for compound indexes, put...
Still trusting req.body in your API?
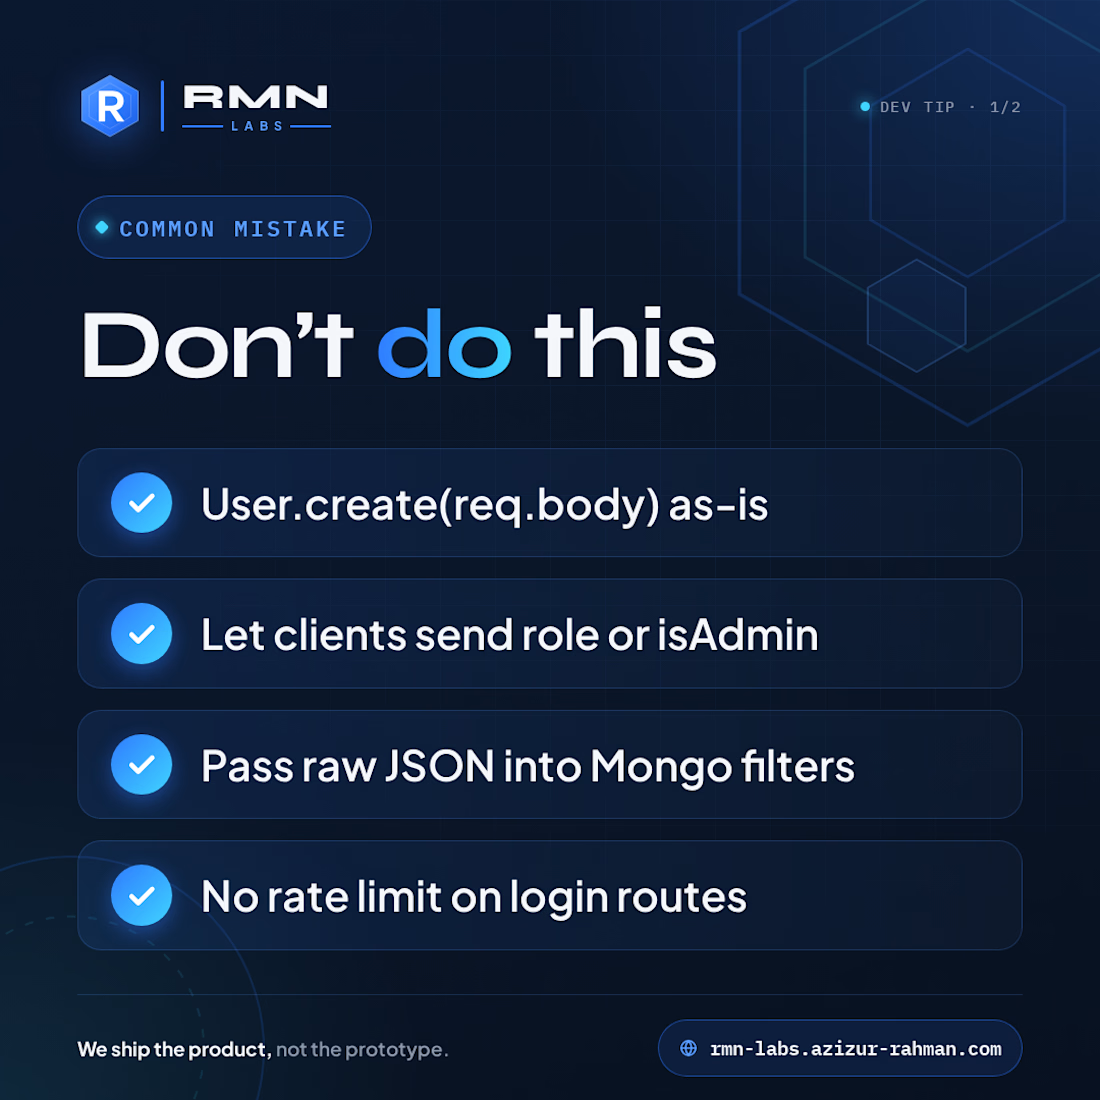
Most devs pass it straight to the database, so a client can slip in "role": "admin" or a $ operator.
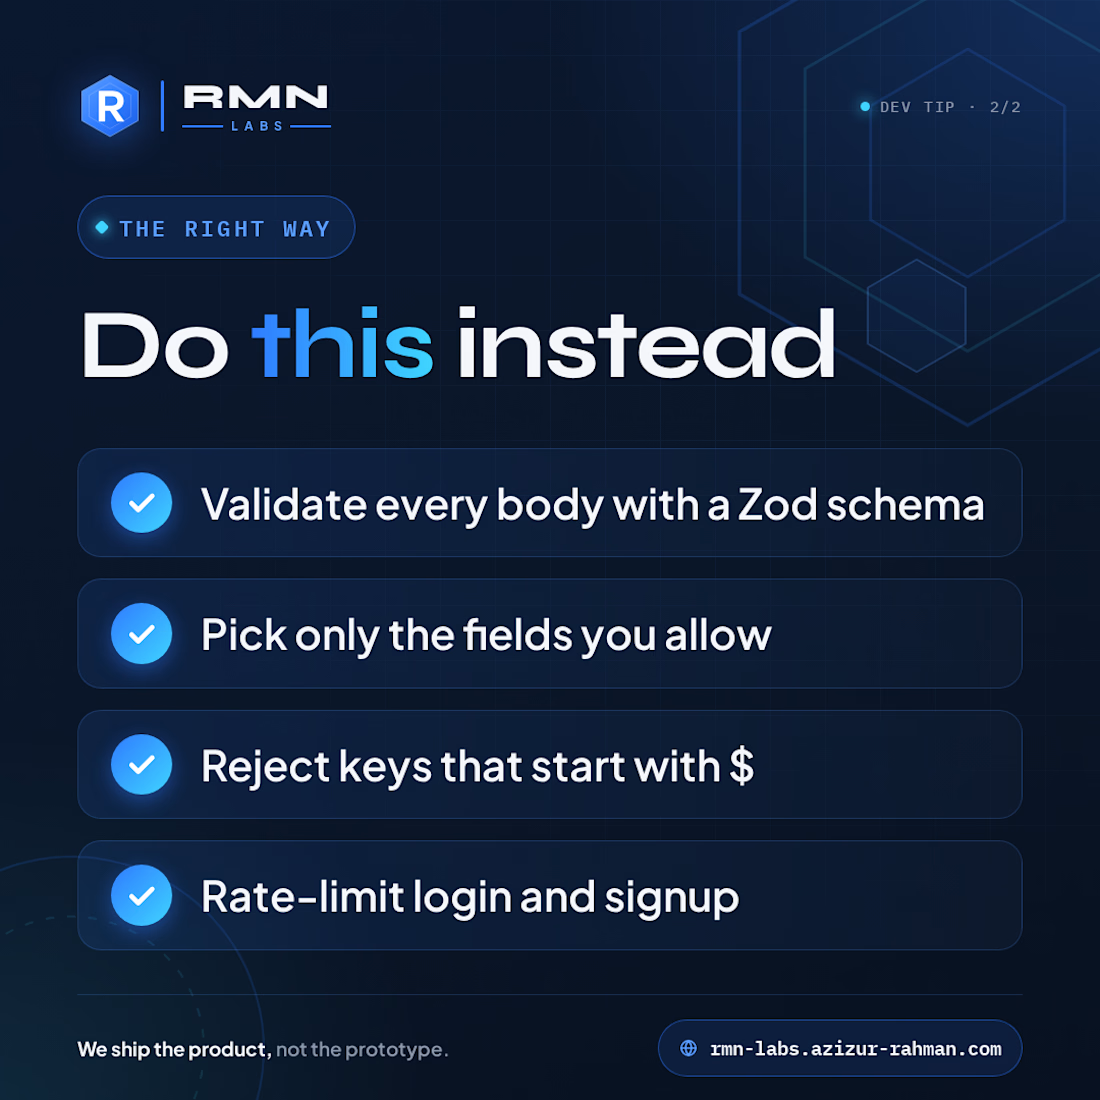
Do this instead:
1. Validate every body with a schema (Zod)
2. Pick only the fields you allow
3. Reject keys that start with $
4. Rate-limit login and signup
Save this for your next API.