Core Sovereign Network Services: BIND9 DNSSEC, Kea DHCP & Chrony NTPRené Bon Ćirić
Flawed DNS resolution, fragile DHCP single points of failure, and unsynchronized system clocks cascade into catastrophic outages, broken TLS handshakes, distributed database split-brains, and invalid audit logs.
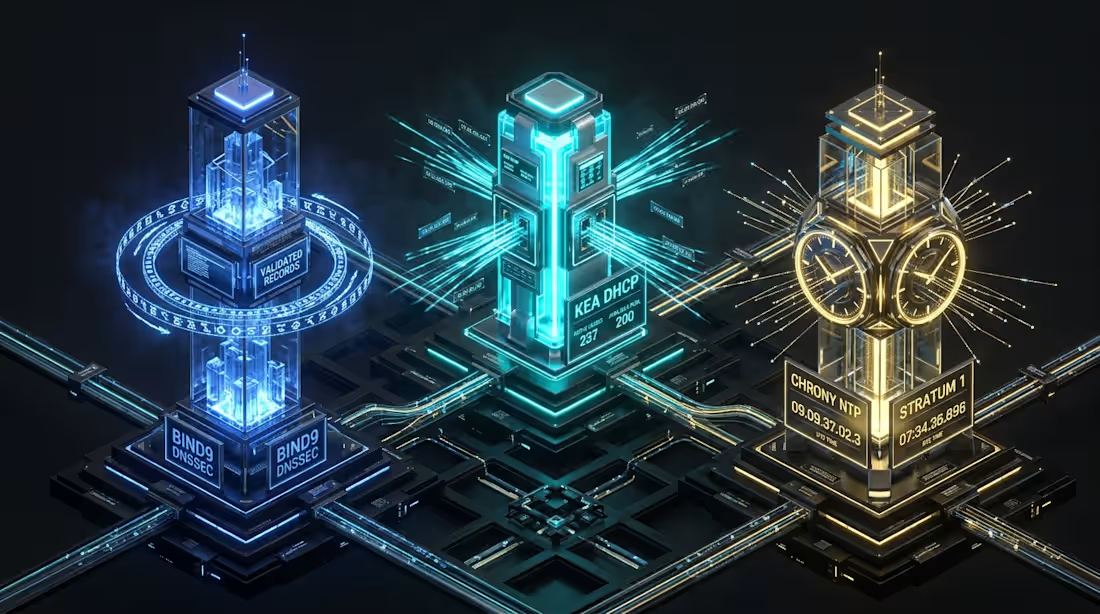
We engineer sovereign, enterprise-grade core network infrastructure built on the gold standards of Internet engineering: authoritative and recursive BIND 9 with automated DNSSEC signing, high-throughput Kea DHCP with active-active High-Availability database clustering, and sub-millisecond precision Chrony NTP time synchronization. This triad provides the rock-solid, resilient foundation required for modern datacenter, campus, and hybrid cloud operations.
Architecture & Safety Invariants
Cryptographic DNS Integrity: BIND9 with automated DNSSEC key management (inline signing, KASP policies) protects internal and public zones against DNS cache poisoning and spoofing.
Resilient Active-Active DHCP: Kea DHCP with PostgreSQL HA backends and native High-Availability hooks eliminates lease contention and provides instant failover without lease loss.
Nanosecond-Scale Clock Synchronization: Chrony NTP synchronized against Stratum-1 hardware/PTP or atomic sources prevents Kerberos ticket failures and Raft consensus timeouts.
Hardened Operating Posture: Strict SELinux enforcement, systemd sandboxing (ProtectSystem=strict, NoNewPrivileges=yes), and minimal network attack surfaces.
Tangible Engineering Deliverables
Authoritative & Recursive BIND 9 DNS with DNSSEC: Split-horizon BIND 9 cluster with automated DNSSEC inline signing (KASP policies), Response Rate Limiting (RRL), and DoT upstream caching.
High-Availability Kea DHCP Cluster: ISC Kea DHCPv4/DHCPv6 servers with active-active PostgreSQL HA backend, sub-second lease synchronization, and TSIG Dynamic DNS (DDNS) integration.
Precision Chrony NTP Infrastructure: Redundant Chrony NTP servers calibrated against curated Stratum-1 sources with kernel-level PPS discipline and frequency drift tracking.
Prometheus Observability Exporters: Native Prometheus monitoring for BIND9 and Chrony tracking query volumes, cache hit ratios, lease pools, and clock offset.
Core Network Operations Runbook & Recovery Drill: Step-by-step documentation for zone reconstitution, manual DNSSEC key rollovers, and database recovery.
FAQs
Example work
Starting at$3,500
Duration1 week
Tags
DNS
Linux
Architect
DevOps Engineer
Infrastructure
Security
Service provided by
René Bon Ćirić Ixtlahuacán de los Membrillos, Mexico
- 2
- Followers
Core Sovereign Network Services: BIND9 DNSSEC, Kea DHCP & Chrony NTPRené Bon Ćirić
Starting at$3,500
Duration1 week
Tags
DNS
Linux
Architect
DevOps Engineer
Infrastructure
Security
Flawed DNS resolution, fragile DHCP single points of failure, and unsynchronized system clocks cascade into catastrophic outages, broken TLS handshakes, distributed database split-brains, and invalid audit logs.
We engineer sovereign, enterprise-grade core network infrastructure built on the gold standards of Internet engineering: authoritative and recursive BIND 9 with automated DNSSEC signing, high-throughput Kea DHCP with active-active High-Availability database clustering, and sub-millisecond precision Chrony NTP time synchronization. This triad provides the rock-solid, resilient foundation required for modern datacenter, campus, and hybrid cloud operations.
Architecture & Safety Invariants
Cryptographic DNS Integrity: BIND9 with automated DNSSEC key management (inline signing, KASP policies) protects internal and public zones against DNS cache poisoning and spoofing.
Resilient Active-Active DHCP: Kea DHCP with PostgreSQL HA backends and native High-Availability hooks eliminates lease contention and provides instant failover without lease loss.
Nanosecond-Scale Clock Synchronization: Chrony NTP synchronized against Stratum-1 hardware/PTP or atomic sources prevents Kerberos ticket failures and Raft consensus timeouts.
Hardened Operating Posture: Strict SELinux enforcement, systemd sandboxing (ProtectSystem=strict, NoNewPrivileges=yes), and minimal network attack surfaces.
Tangible Engineering Deliverables
Authoritative & Recursive BIND 9 DNS with DNSSEC: Split-horizon BIND 9 cluster with automated DNSSEC inline signing (KASP policies), Response Rate Limiting (RRL), and DoT upstream caching.
High-Availability Kea DHCP Cluster: ISC Kea DHCPv4/DHCPv6 servers with active-active PostgreSQL HA backend, sub-second lease synchronization, and TSIG Dynamic DNS (DDNS) integration.
Precision Chrony NTP Infrastructure: Redundant Chrony NTP servers calibrated against curated Stratum-1 sources with kernel-level PPS discipline and frequency drift tracking.
Prometheus Observability Exporters: Native Prometheus monitoring for BIND9 and Chrony tracking query volumes, cache hit ratios, lease pools, and clock offset.
Core Network Operations Runbook & Recovery Drill: Step-by-step documentation for zone reconstitution, manual DNSSEC key rollovers, and database recovery.
FAQs
Example work
$3,500