Custom Linux Distribution & Immutable OS Engineering: mkosi & UKIRené Bon Ćirić
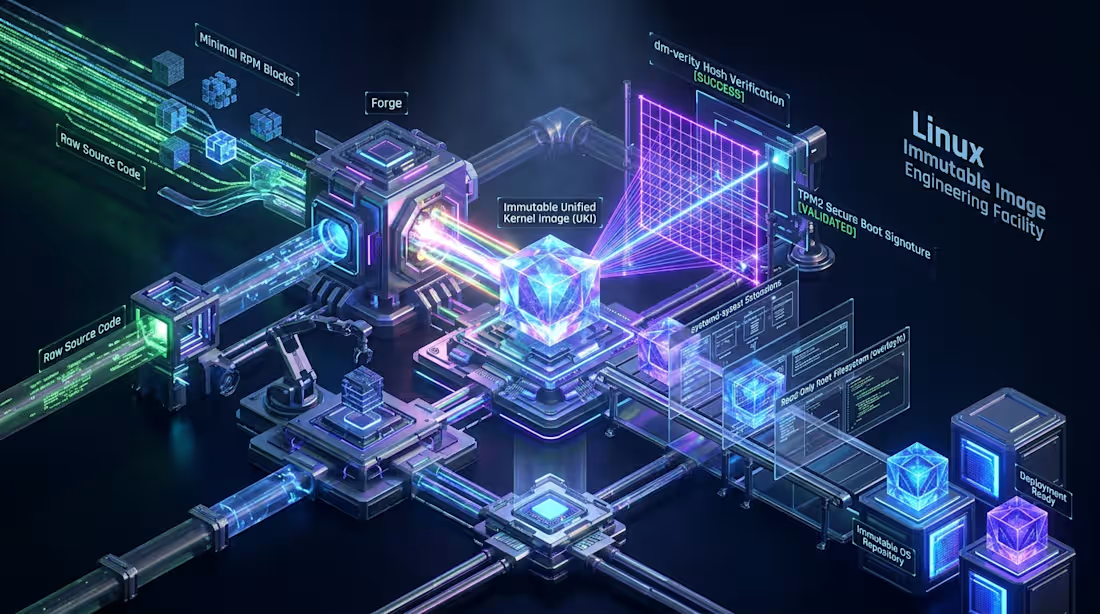
Traditional mutable operating systems suffer from configuration drift, silent package corruption, unauthorized tampering, and slow, non-deterministic recovery workflows.
We architect and build tailored, reproducible, and cryptographically verified Linux operating system distributions and appliances from source or upstream RPM repositories. Powered by modern mkosi, Unified Kernel Images (UKIs), systemd-repart, and dm-verity, our immutable operating system images boot directly into read-only, cryptographically authenticated environments with hardware-backed TPM2 Secure Boot sealing, guaranteeing total platform integrity from bare-metal firmware to application runtimes.
Why Custom Immutable Linux Distributions?
Zero Configuration Drift: The root filesystem is strictly read-only and sealed with dm-verity hashes, ensuring that every deployment across edge, virtualization, or bare-metal is mathematically identical.
Tamper-Proof Boot Chain: Unified Kernel Images (combining Linux kernel, initrd, and kernel cmdline into a single PE binary) signed with private SecureBoot keys and sealed to TPM2 PCR registers.
Atomic A/B Upgrades: Dual-bank partition layouts orchestrated by
systemd-sysupdate and systemd-repart provide instantaneous, fail-safe updates with automated fallback upon boot failure.Modular System Extensions: Granular customization and zero-reboot runtime extension delivery via signed
systemd-sysext and systemd-confext images.FAQs
Example work
Starting at$6,000
Duration2 weeks
Tags
CentOS
Linux
Architect
DevOps Engineer
Infrastructure
Security
Service provided by
René Bon Ćirić Ixtlahuacán de los Membrillos, Mexico
Custom Linux Distribution & Immutable OS Engineering: mkosi & UKIRené Bon Ćirić
Starting at$6,000
Duration2 weeks
Tags
CentOS
Linux
Architect
DevOps Engineer
Infrastructure
Security
Traditional mutable operating systems suffer from configuration drift, silent package corruption, unauthorized tampering, and slow, non-deterministic recovery workflows.
We architect and build tailored, reproducible, and cryptographically verified Linux operating system distributions and appliances from source or upstream RPM repositories. Powered by modern mkosi, Unified Kernel Images (UKIs), systemd-repart, and dm-verity, our immutable operating system images boot directly into read-only, cryptographically authenticated environments with hardware-backed TPM2 Secure Boot sealing, guaranteeing total platform integrity from bare-metal firmware to application runtimes.
Why Custom Immutable Linux Distributions?
Zero Configuration Drift: The root filesystem is strictly read-only and sealed with dm-verity hashes, ensuring that every deployment across edge, virtualization, or bare-metal is mathematically identical.
Tamper-Proof Boot Chain: Unified Kernel Images (combining Linux kernel, initrd, and kernel cmdline into a single PE binary) signed with private SecureBoot keys and sealed to TPM2 PCR registers.
Atomic A/B Upgrades: Dual-bank partition layouts orchestrated by
systemd-sysupdate and systemd-repart provide instantaneous, fail-safe updates with automated fallback upon boot failure.Modular System Extensions: Granular customization and zero-reboot runtime extension delivery via signed
systemd-sysext and systemd-confext images.FAQs
Example work
$6,000