High-Availability Ingress & Hardened Reverse Proxies: HAProxy & CaddyRené Bon Ćirić
Ingress bottlenecks, ungraceful configuration reloads, single-point-of-failure load balancers, and flawed TLS setups degrade application performance and expose critical backend services to public exploitation.
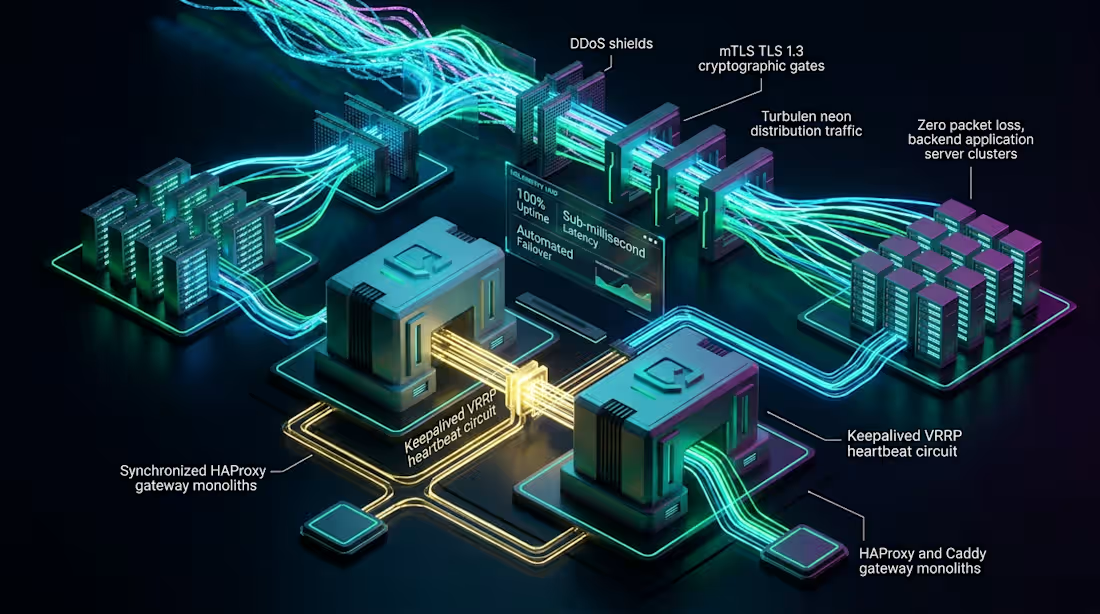
We design and deploy high-throughput, resilient ingress gateways utilizing synchronized HAProxy and hardened Caddy reverse proxies. Backed by Keepalived Virtual Router Redundancy Protocol (VRRP) for sub-second IP failover, our edge architectures feature automated Let's Encrypt / ZeroSSL TLS certificate lifecycles, intelligent DDoS mitigation rate limiting, dynamic backend health probing, and hitless graceful configuration reloads.
Why Enterprise Ingress with HAProxy & Caddy?
Sub-Second Failover & High Availability: Redundant gateway pairs sharing Virtual IP (VIP) addresses via Keepalived ensure that host crashes or network drops trigger transparent, zero-downtime client failover.
Peak Layer-4 & Layer-7 Performance: HAProxy handles millions of concurrent TCP/HTTP connections with sub-millisecond dispatch latencies and micro-architectural CPU affinity tuning.
Automated Modern Cryptography: Caddy provides out-of-the-box, zero-maintenance automated TLS 1.3 certificates, HTTP/3 (QUIC) performance, and modern cipher suite negotiation.
Hitless Maintenance: Zero-packet-drop runtime state synchronization and seamless reload mechanics ensure continuous uptime during configuration adjustments and security patching.
FAQs
Example work
Starting at$3,500
Duration1 week
Tags
Caddy
Linux
Architect
DevOps Engineer
Infrastructure
Security
Service provided by
René Bon Ćirić Ixtlahuacán de los Membrillos, Mexico
High-Availability Ingress & Hardened Reverse Proxies: HAProxy & CaddyRené Bon Ćirić
Starting at$3,500
Duration1 week
Tags
Caddy
Linux
Architect
DevOps Engineer
Infrastructure
Security
Ingress bottlenecks, ungraceful configuration reloads, single-point-of-failure load balancers, and flawed TLS setups degrade application performance and expose critical backend services to public exploitation.
We design and deploy high-throughput, resilient ingress gateways utilizing synchronized HAProxy and hardened Caddy reverse proxies. Backed by Keepalived Virtual Router Redundancy Protocol (VRRP) for sub-second IP failover, our edge architectures feature automated Let's Encrypt / ZeroSSL TLS certificate lifecycles, intelligent DDoS mitigation rate limiting, dynamic backend health probing, and hitless graceful configuration reloads.
Why Enterprise Ingress with HAProxy & Caddy?
Sub-Second Failover & High Availability: Redundant gateway pairs sharing Virtual IP (VIP) addresses via Keepalived ensure that host crashes or network drops trigger transparent, zero-downtime client failover.
Peak Layer-4 & Layer-7 Performance: HAProxy handles millions of concurrent TCP/HTTP connections with sub-millisecond dispatch latencies and micro-architectural CPU affinity tuning.
Automated Modern Cryptography: Caddy provides out-of-the-box, zero-maintenance automated TLS 1.3 certificates, HTTP/3 (QUIC) performance, and modern cipher suite negotiation.
Hitless Maintenance: Zero-packet-drop runtime state synchronization and seamless reload mechanics ensure continuous uptime during configuration adjustments and security patching.
FAQs
Example work
$3,500