Hardened Linux & Container InfrastructureRené Bon Ćirić
Standard Linux cloud instances and default container setups run with dangerous privileges: root daemons, broad attack surfaces, permissive SELinux, unauthenticated local sockets, and vulnerable supply chains.
This service transforms your Linux hosts and container environments into hardened, immutable, zero-trust infrastructure designed to withstand hostile environments and strict compliance audits.
Scope & Architecture Invariants
SELinux & Kernel Hardening: Transition to SELinux Enforcing mode without breaking workloads, custom Type Enforcement (.te) policies, and network/memory sysctl tuning.
Rootless Podman & Systemd Quadlets: Migrate privileged Docker daemons to unprivileged rootless Podman containers natively supervised by systemd Quadlets.
PKI, TLS & Secret Hygiene: Private CA setup, automated certificate renewal, memory-backed tmpfs for runtime secrets, and 600 key permissions.
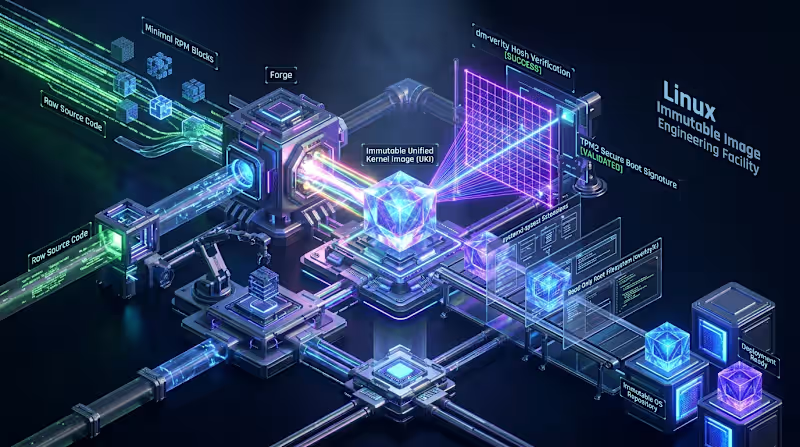
Declarative Images & RPM Packaging: Immutable system image baselines (mkosi/UKI) and custom RPM packaging following Fedora/EPEL standards.
Tangible Engineering Deliverables
Automated Ansible Hardening Playbooks: Production-ready, idempotent Ansible roles (FQCN standard) applying SELinux, kernel sysctls, and auditd rules.
Rootless Podman Quadlet Manifests: Fully declared systemd container units with user namespace mapping and isolated volume labeling (:z/:Z).
Private PKI & Certificate Lifecycle Pipeline: Internal CA automation with automated certificate issuance, rotation hooks, and secure tmpfs secret mounting.
Compliance & Security Verification Suite: Automated test suite executing CIS benchmark checks and verifying SELinux Enforcing confinement.
Systems Administration & Rollback Runbook: Clear operational documentation covering policy updates, container management, and troubleshooting.
FAQs
Example work
Starting at$5,000
Duration2 weeks
Tags
Linux
DevOps Engineer
Containers
Security
SELinux
Service provided by
René Bon Ćirić Ixtlahuacán de los Membrillos, Mexico
- 2
- Followers
Hardened Linux & Container InfrastructureRené Bon Ćirić
Starting at$5,000
Duration2 weeks
Tags
Linux
DevOps Engineer
Containers
Security
SELinux
Standard Linux cloud instances and default container setups run with dangerous privileges: root daemons, broad attack surfaces, permissive SELinux, unauthenticated local sockets, and vulnerable supply chains.
This service transforms your Linux hosts and container environments into hardened, immutable, zero-trust infrastructure designed to withstand hostile environments and strict compliance audits.
Scope & Architecture Invariants
SELinux & Kernel Hardening: Transition to SELinux Enforcing mode without breaking workloads, custom Type Enforcement (.te) policies, and network/memory sysctl tuning.
Rootless Podman & Systemd Quadlets: Migrate privileged Docker daemons to unprivileged rootless Podman containers natively supervised by systemd Quadlets.
PKI, TLS & Secret Hygiene: Private CA setup, automated certificate renewal, memory-backed tmpfs for runtime secrets, and 600 key permissions.
Declarative Images & RPM Packaging: Immutable system image baselines (mkosi/UKI) and custom RPM packaging following Fedora/EPEL standards.
Tangible Engineering Deliverables
Automated Ansible Hardening Playbooks: Production-ready, idempotent Ansible roles (FQCN standard) applying SELinux, kernel sysctls, and auditd rules.
Rootless Podman Quadlet Manifests: Fully declared systemd container units with user namespace mapping and isolated volume labeling (:z/:Z).
Private PKI & Certificate Lifecycle Pipeline: Internal CA automation with automated certificate issuance, rotation hooks, and secure tmpfs secret mounting.
Compliance & Security Verification Suite: Automated test suite executing CIS benchmark checks and verifying SELinux Enforcing confinement.
Systems Administration & Rollback Runbook: Clear operational documentation covering policy updates, container management, and troubleshooting.
FAQs
Example work
$5,000