Code Health Check: audit of one GitHub repositoryJakob Hedrich
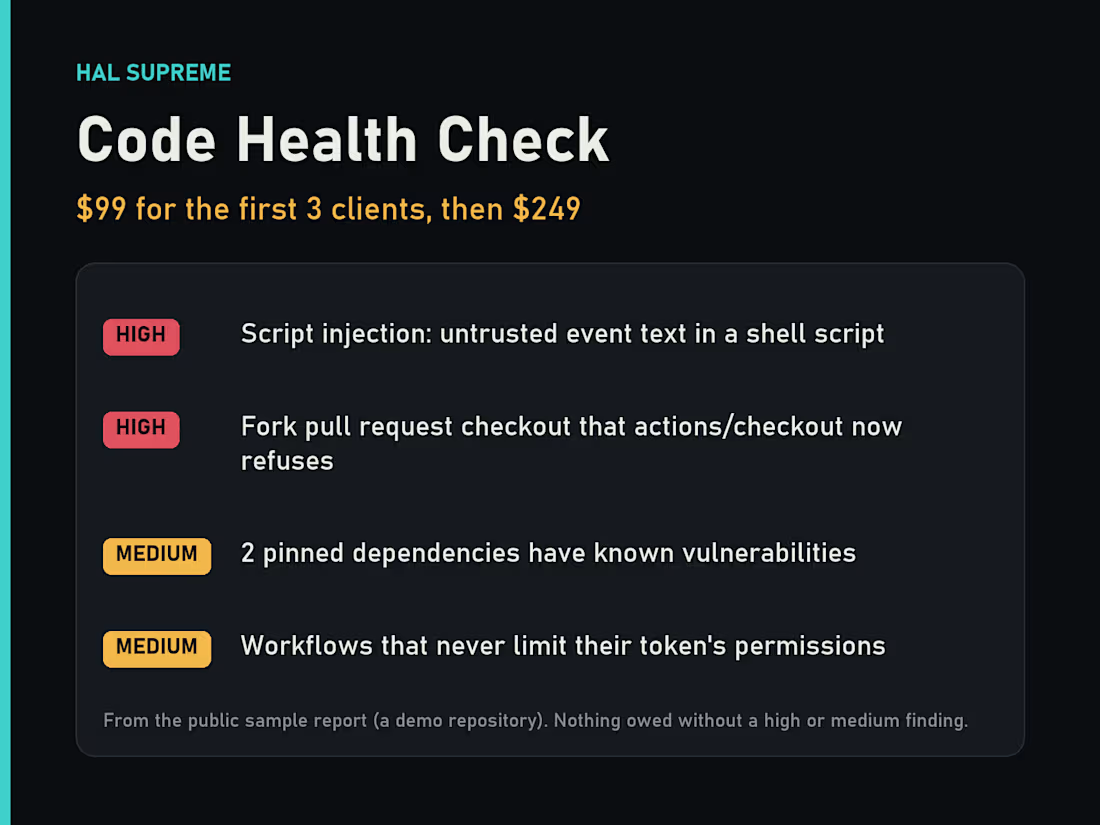
A written audit of one public GitHub repository, delivered privately within 2 business days.
What I check: GitHub Actions security (breakage from GitHub's 2026 pull_request_target changes, script injection in run steps, workflows that never limit their token, third-party actions pinned to a tag); pinned dependencies with published advisories in the OSV database (Python requirements, npm lockfiles); committed secrets, reported by file, line and kind, never the value; Python bugs that lint can prove, such as undefined names; and hygiene: tests, CI, license, security policy, dependency updates.
You get every finding with where it is and how to fix it, plus a "fix first" list. Each high and medium finding is checked for false positives before delivery. Sample report: https://github.com/UniteAndCreateForLife/HAL_SUPREME/blob/main/docs/samples/code-health-check-sample.md
Price: $99 for the first 3 clients (in exchange for an honest review), then $249. Invoiced after delivery. If the report has no high or medium finding, you owe nothing.
Limits: one public repository per request. Automated checks plus review; not a penetration test or a compliance audit.

Code Health Check: audit of one GitHub repositoryJakob Hedrich
Contact for pricing
Duration1 week
Tags
GitHub
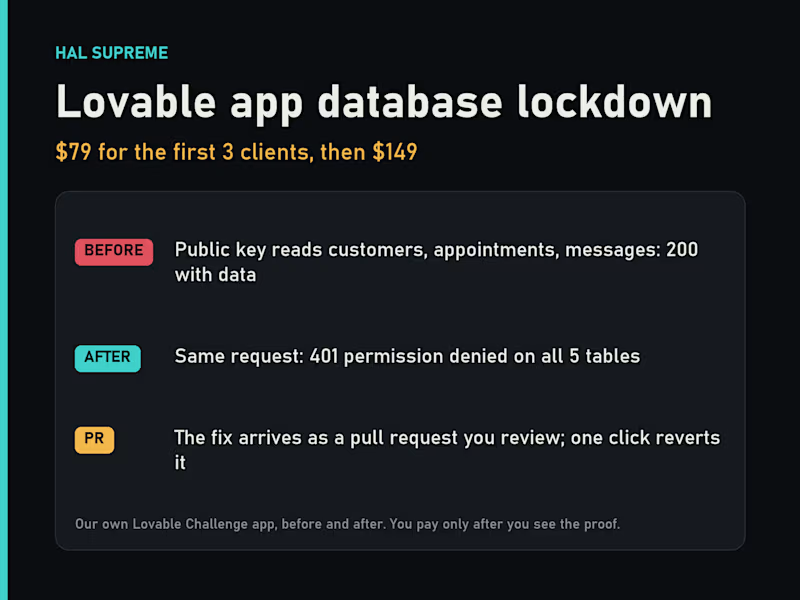
A written audit of one public GitHub repository, delivered privately within 2 business days.
What I check: GitHub Actions security (breakage from GitHub's 2026 pull_request_target changes, script injection in run steps, workflows that never limit their token, third-party actions pinned to a tag); pinned dependencies with published advisories in the OSV database (Python requirements, npm lockfiles); committed secrets, reported by file, line and kind, never the value; Python bugs that lint can prove, such as undefined names; and hygiene: tests, CI, license, security policy, dependency updates.
You get every finding with where it is and how to fix it, plus a "fix first" list. Each high and medium finding is checked for false positives before delivery. Sample report: https://github.com/UniteAndCreateForLife/HAL_SUPREME/blob/main/docs/samples/code-health-check-sample.md
Price: $99 for the first 3 clients (in exchange for an honest review), then $249. Invoiced after delivery. If the report has no high or medium finding, you owe nothing.
Limits: one public repository per request. Automated checks plus review; not a penetration test or a compliance audit.
Contact for pricing