Lovable app database lockdown, with proofJakob Hedrich
Lovable Cloud and Supabase apps send a public key to every browser, so the database's row level security rules are all that stands between that key and your data. Open rules are common; in 2025, CVE-2025-48757 exposed data in 170+ Lovable apps this way.
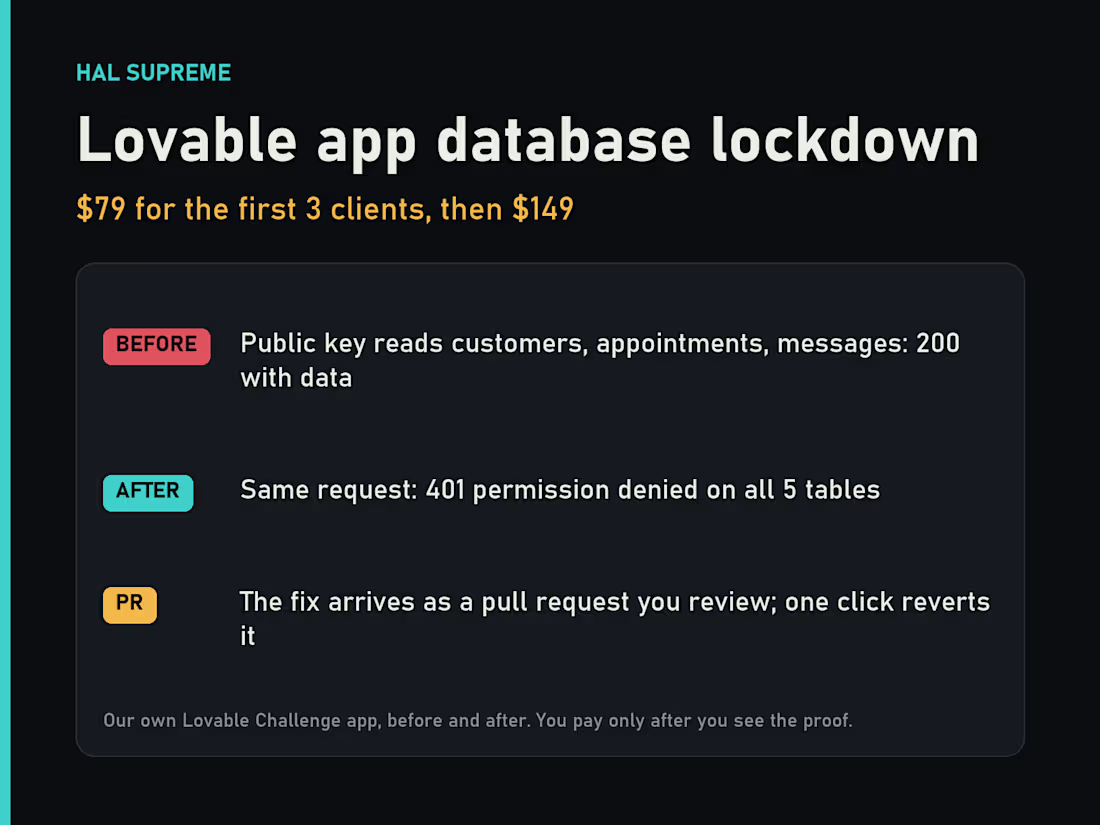
What I do: read your repo's database migrations (through Lovable's GitHub sync) and find every rule that lets the public key, or any signed-in user, read or change data, plus tables with row level security off. I fix it by scoping each rule to the row's owner, or by moving reads and writes into server functions. The change arrives as a pull request you review, and one click reverts it. Then I prove it with your consent: the same request with your app's public key, before and after (before: data; after: permission denied).
Price: $79 for the first 3 clients (in exchange for an honest review), then $149. You pay only after you have seen the before/after proof.
Limits: Lovable Cloud or Supabase apps with GitHub sync. I don't change your sign-in flow. This is a focused fix, not a penetration test.

Lovable app database lockdown, with proofJakob Hedrich
Contact for pricing
Duration1 week
Tags
Supabase
Lovable Cloud and Supabase apps send a public key to every browser, so the database's row level security rules are all that stands between that key and your data. Open rules are common; in 2025, CVE-2025-48757 exposed data in 170+ Lovable apps this way.
What I do: read your repo's database migrations (through Lovable's GitHub sync) and find every rule that lets the public key, or any signed-in user, read or change data, plus tables with row level security off. I fix it by scoping each rule to the row's owner, or by moving reads and writes into server functions. The change arrives as a pull request you review, and one click reverts it. Then I prove it with your consent: the same request with your app's public key, before and after (before: data; after: permission denied).
Price: $79 for the first 3 clients (in exchange for an honest review), then $149. You pay only after you have seen the before/after proof.
Limits: Lovable Cloud or Supabase apps with GitHub sync. I don't change your sign-in flow. This is a focused fix, not a penetration test.
Contact for pricing