Enterprise FreeIPA HA & Centralized PKI/CA InfrastructureRené Bon Ćirić
Fragmented user accounts, scattered SSH keys, unmanaged sudo privileges, and expired TLS certificates represent the largest operational security liabilities in modern infrastructure.
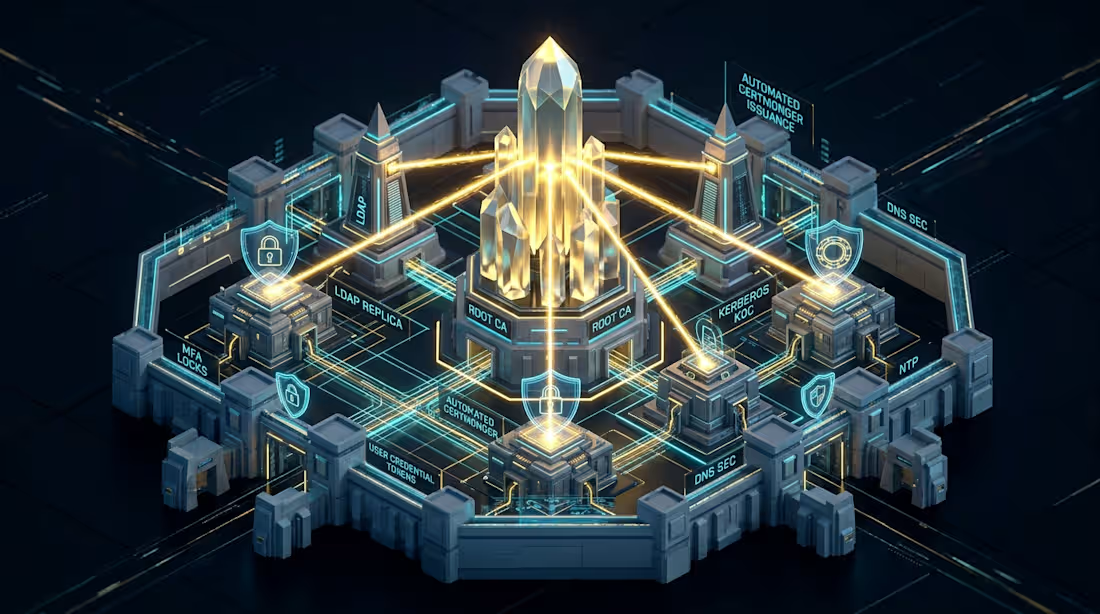
We deploy a production-hardened, multi-master High-Availability (HA) FreeIPA / Red Hat Identity Management (IdM) domain combined with a multi-tier Public Key Infrastructure (PKI). This unified sovereign architecture delivers centralized identity management, Kerberos Single Sign-On (SSO), Host-Based Access Control (HBAC), automated host certificate issuance, and centralized sudo governance across your entire Linux server fleet.
Why Enterprise FreeIPA & Centralized Identity?
Zero Identity Fragmentation: Single authoritative directory for user credentials, SSH public keys, groups, and netgroups across all hybrid cloud and bare-metal nodes.
Granular Host & Command Governance: Fine-grained Host-Based Access Control (HBAC) and centralized sudo rule evaluation enforced natively by System Security Services Daemon (SSSD).
Multi-Master Replication & Zero Downtime: Active-active directory topologies with multi-master LDAP and Kerberos replication, automated conflict resolution, and integrated DNS failover.
Automated Certificate Lifecycle: Integrated Dogtag Certificate System with automated host/service TLS certificate enrollment and renewal via
certmonger and ACME endpoints.FAQs
Example work
Starting at$5,500
Duration2 weeks
Tags
Linux
Architect
Automation
DevOps Engineer
DNS
Security
Service provided by
René Bon Ćirić Ixtlahuacán de los Membrillos, Mexico
Enterprise FreeIPA HA & Centralized PKI/CA InfrastructureRené Bon Ćirić
Starting at$5,500
Duration2 weeks
Tags
Linux
Architect
Automation
DevOps Engineer
DNS
Security
Fragmented user accounts, scattered SSH keys, unmanaged sudo privileges, and expired TLS certificates represent the largest operational security liabilities in modern infrastructure.
We deploy a production-hardened, multi-master High-Availability (HA) FreeIPA / Red Hat Identity Management (IdM) domain combined with a multi-tier Public Key Infrastructure (PKI). This unified sovereign architecture delivers centralized identity management, Kerberos Single Sign-On (SSO), Host-Based Access Control (HBAC), automated host certificate issuance, and centralized sudo governance across your entire Linux server fleet.
Why Enterprise FreeIPA & Centralized Identity?
Zero Identity Fragmentation: Single authoritative directory for user credentials, SSH public keys, groups, and netgroups across all hybrid cloud and bare-metal nodes.
Granular Host & Command Governance: Fine-grained Host-Based Access Control (HBAC) and centralized sudo rule evaluation enforced natively by System Security Services Daemon (SSSD).
Multi-Master Replication & Zero Downtime: Active-active directory topologies with multi-master LDAP and Kerberos replication, automated conflict resolution, and integrated DNS failover.
Automated Certificate Lifecycle: Integrated Dogtag Certificate System with automated host/service TLS certificate enrollment and renewal via
certmonger and ACME endpoints.FAQs
Example work
$5,500