Web Application Penetration TestingZubair Usman
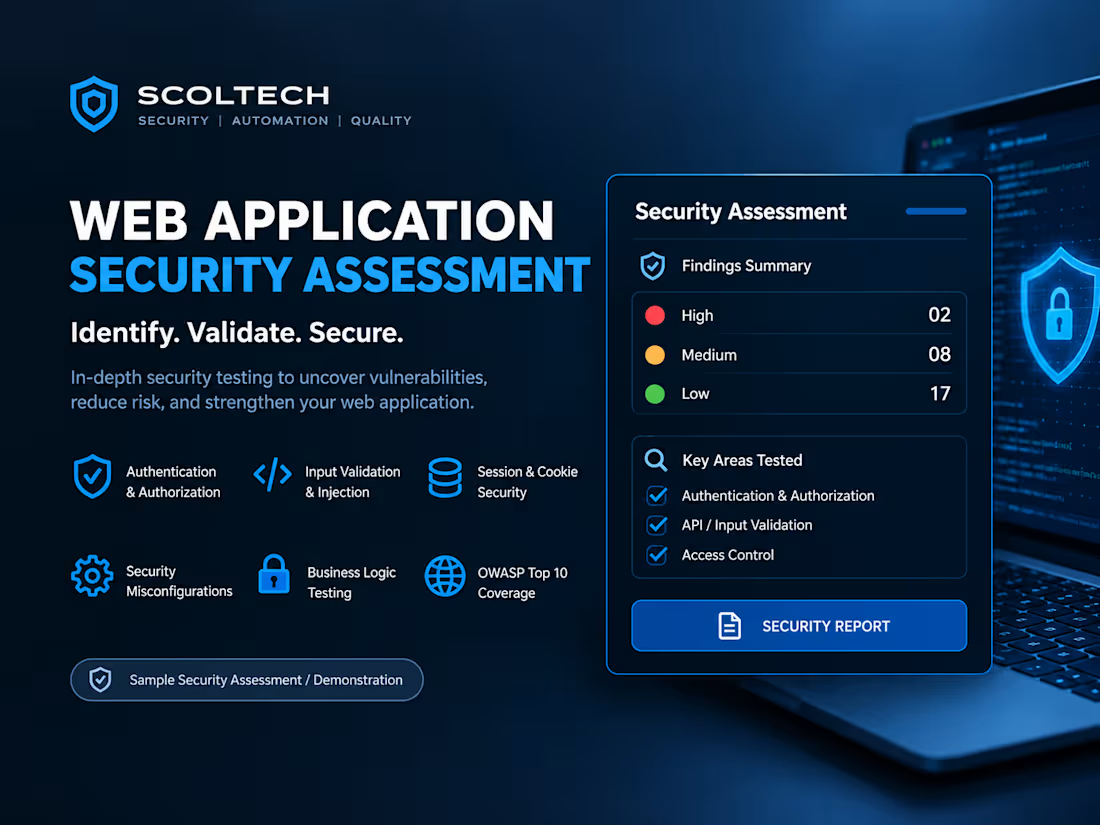
I will perform a structured security assessment of your web application to identify, validate, and document security vulnerabilities before they can become real business risks.
WHAT I TEST
• Authentication & authorization
• Access control / IDOR
• Input validation
• XSS and injection vulnerabilities
• Session and cookie security
• Security misconfigurations
• Sensitive data exposure
• Business logic weaknesses
• Common OWASP security risks
MY PROCESS
Define scope and testing requirements
Perform reconnaissance and application mapping
Combine automated scanning with manual testing
Validate potential vulnerabilities
Assess security impact and severity
Document evidence and reproduction steps
Provide practical remediation guidance
Retest fixes when included in scope
DELIVERABLES
• Professional security assessment report
• Confirmed vulnerability findings
• Severity and risk classification
• Technical evidence
• Reproduction steps
• Remediation recommendations
• Executive-level summary
CLIENT REQUIREMENTS
Before testing begins, I need written authorization, the application URL/environment, agreed testing scope, test accounts where required, and any relevant testing restrictions.
All testing is performed only against systems and applications that the client is authorized to have tested.
FAQs
Zubair's other services
Starting at$25 /hr
Tags
Burp Suite

OWASP ZAP
Python
Cybersecurity Specialist
Penetration Testing
Software Engineer
Technology
Security Testing
Service provided by
Zubair Usman Pakistan
- 1
- Followers
Web Application Penetration TestingZubair Usman
Starting at$25 /hr
Tags
Burp Suite
OWASP ZAP
Python
Cybersecurity Specialist
Penetration Testing
Software Engineer
Technology
Security Testing
I will perform a structured security assessment of your web application to identify, validate, and document security vulnerabilities before they can become real business risks.
WHAT I TEST
• Authentication & authorization
• Access control / IDOR
• Input validation
• XSS and injection vulnerabilities
• Session and cookie security
• Security misconfigurations
• Sensitive data exposure
• Business logic weaknesses
• Common OWASP security risks
MY PROCESS
Define scope and testing requirements
Perform reconnaissance and application mapping
Combine automated scanning with manual testing
Validate potential vulnerabilities
Assess security impact and severity
Document evidence and reproduction steps
Provide practical remediation guidance
Retest fixes when included in scope
DELIVERABLES
• Professional security assessment report
• Confirmed vulnerability findings
• Severity and risk classification
• Technical evidence
• Reproduction steps
• Remediation recommendations
• Executive-level summary
CLIENT REQUIREMENTS
Before testing begins, I need written authorization, the application URL/environment, agreed testing scope, test accounts where required, and any relevant testing restrictions.
All testing is performed only against systems and applications that the client is authorized to have tested.
FAQs
Zubair's other services
$25 /hr