
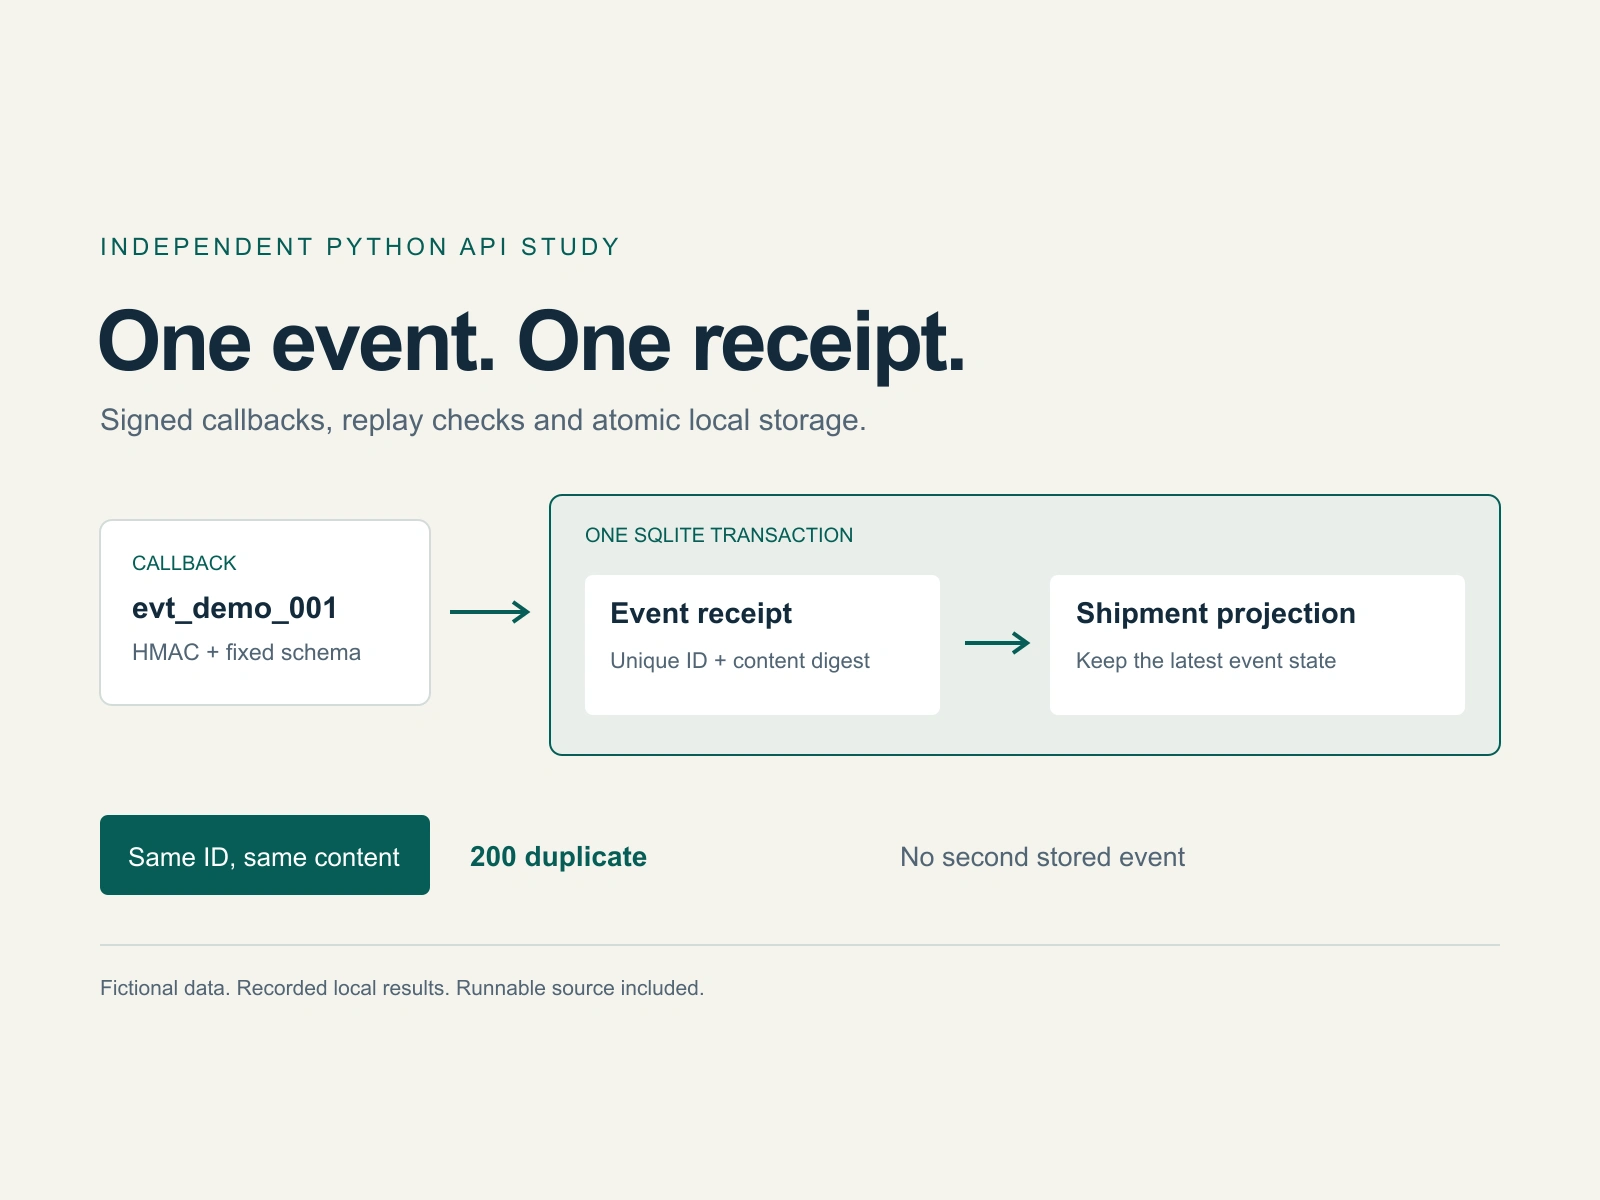
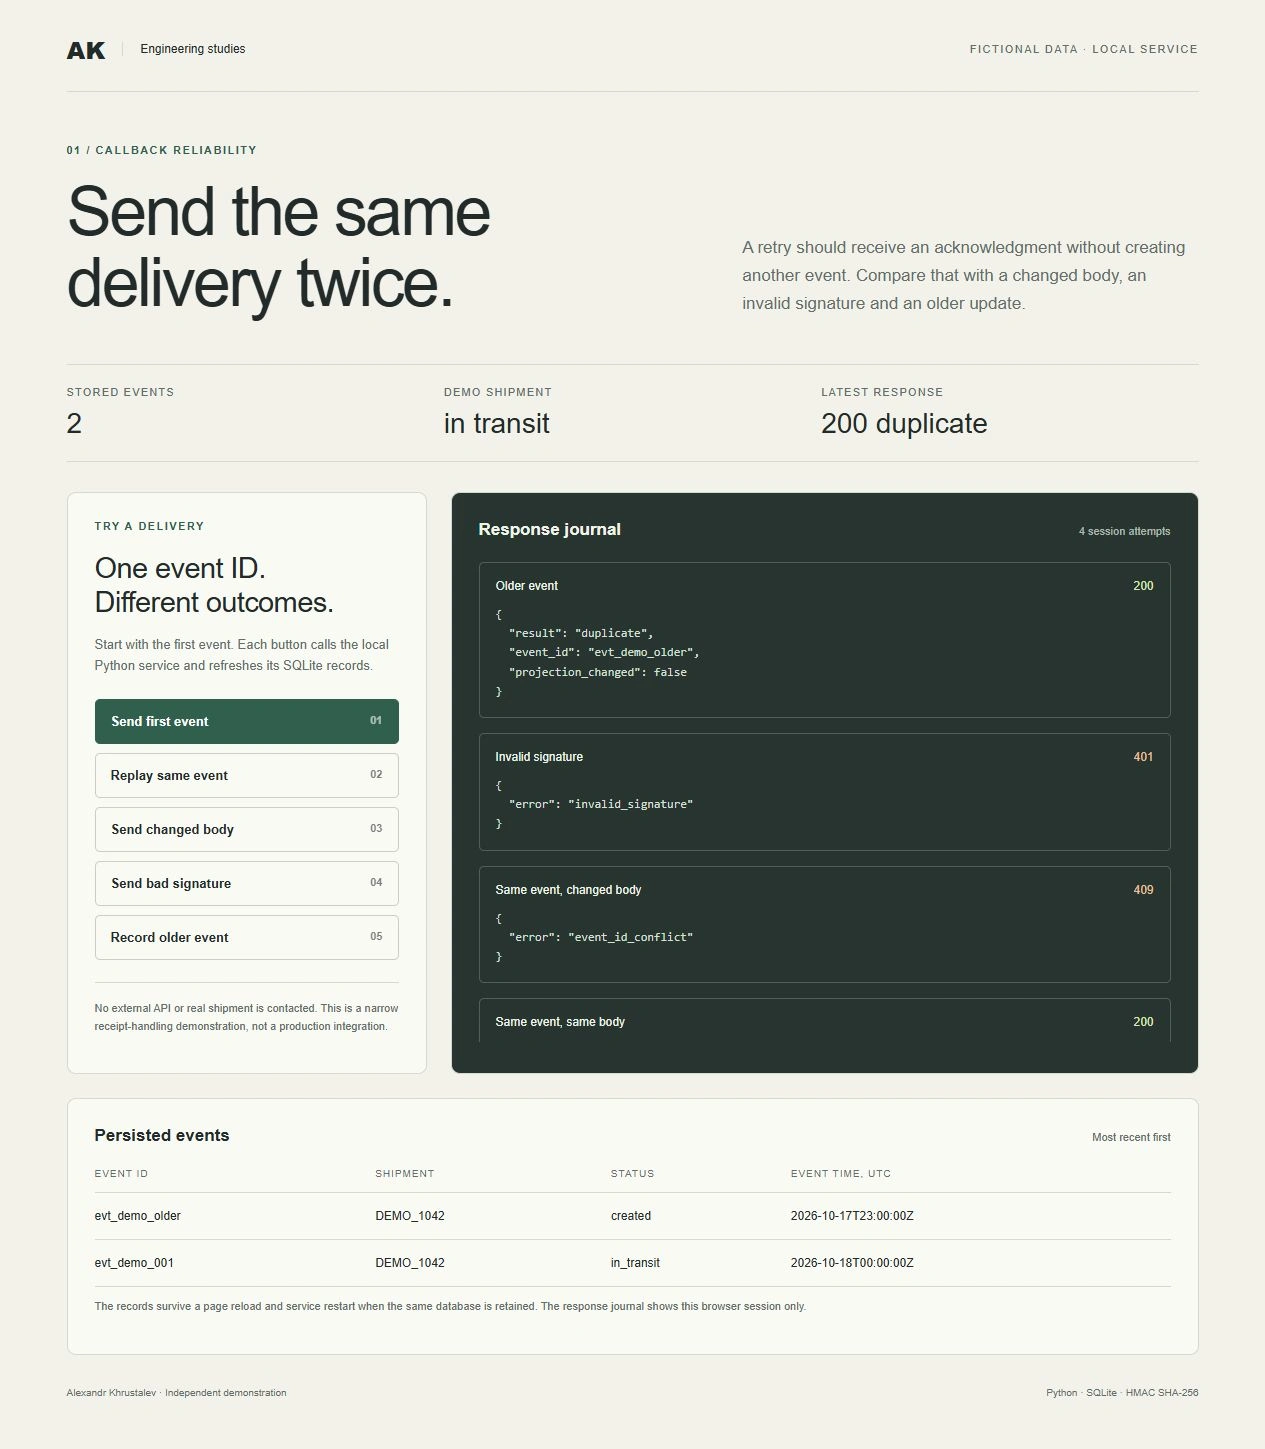
Independent Python API study using fictional shipment events. The service checks signed callbacks, acknowledges duplicate event IDs and commits each receipt with its shipment projection in one SQLite transaction.
A repeated delivery should not create another event. A changed body under an existing event ID should be rejected, and an older event should not roll the shipment back.
I built a local HTTP service with HMAC signature checks, fixed-schema validation, canonical content digests and a small browser interface for inspecting outcomes. The receipt and projection are stored together. The response journal is session-local, while the stored events survive reload and a service restart with the same database.
Version 1.0.1 passed 32 unit and HTTP tests from a fresh ZIP extraction. Five browser request cases and a real service restart were also checked. Testing exposed deeply nested JSON returning an internal error. I changed that path to a validation response and added direct-store and HTTP regressions.
This is a runnable local demonstration, not a production provider integration or client delivery. It uses fictional data and makes no claim about live shipment systems.
Open the recorded study and runnable source: https://sandersaxbuilds.github.io/selected-work/webhook-receipt-study.html
0 likes · 2 views · Oct 17, 2026
Independent Python study of signed callbacks, duplicate detection and atomic SQLite storage, with 32 unit and HTTP tests. Fictional shipment data.

