
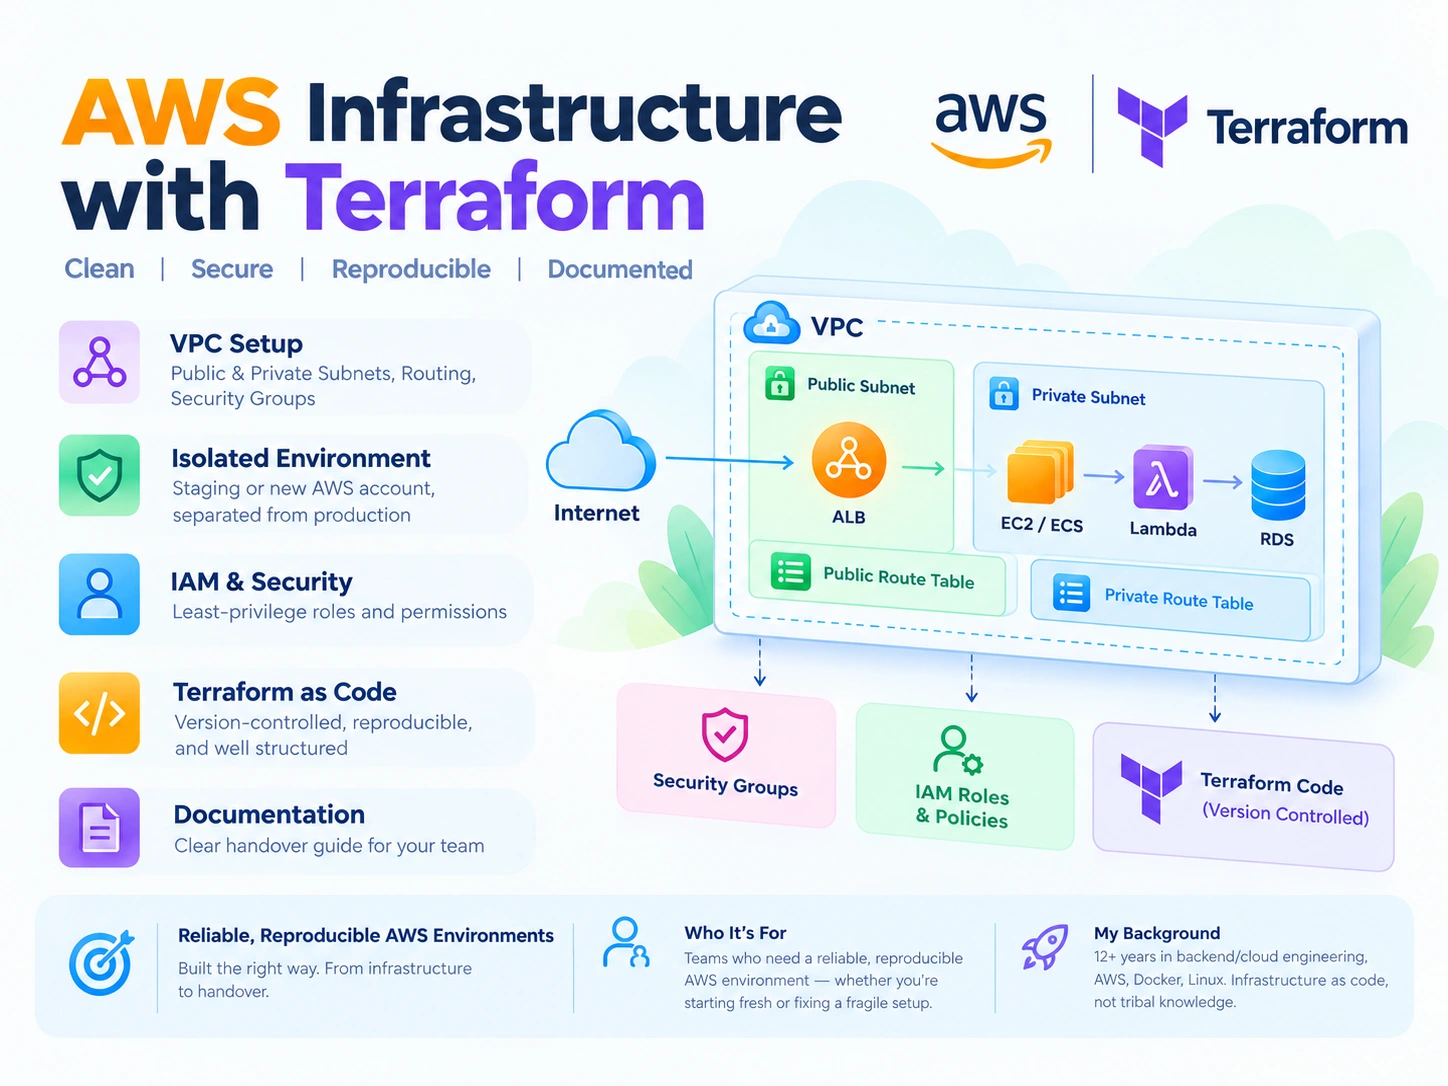
I just opened a service for teams who need a clean, isolated AWS environment - done right the first time, with Terraform so it's actually reproducible (not a pile of manual console clicks only one person understands).
What I set up:
✅ Isolated staging/prod environments (proper VPC structure)
✅ IAM roles with least-privilege access
✅ Everything in Terraform — version-controlled, documented
✅ A handover doc so your team isn't locked to me
Background: 12+ years in backend & cloud engineering, hands-on with AWS (Lambda, API Gateway, EC2), Docker, and Linux infra.
If your AWS environment feels fragile, undocumented, or "nobody really knows how this was built" — that's exactly what I fix.
0 likes · 0 views · Oct 3, 2026
I just opened a service for teams who need a clean, isolated AWS environment - done right the first time, with Terraform so it's actually reproducible (not a...


