
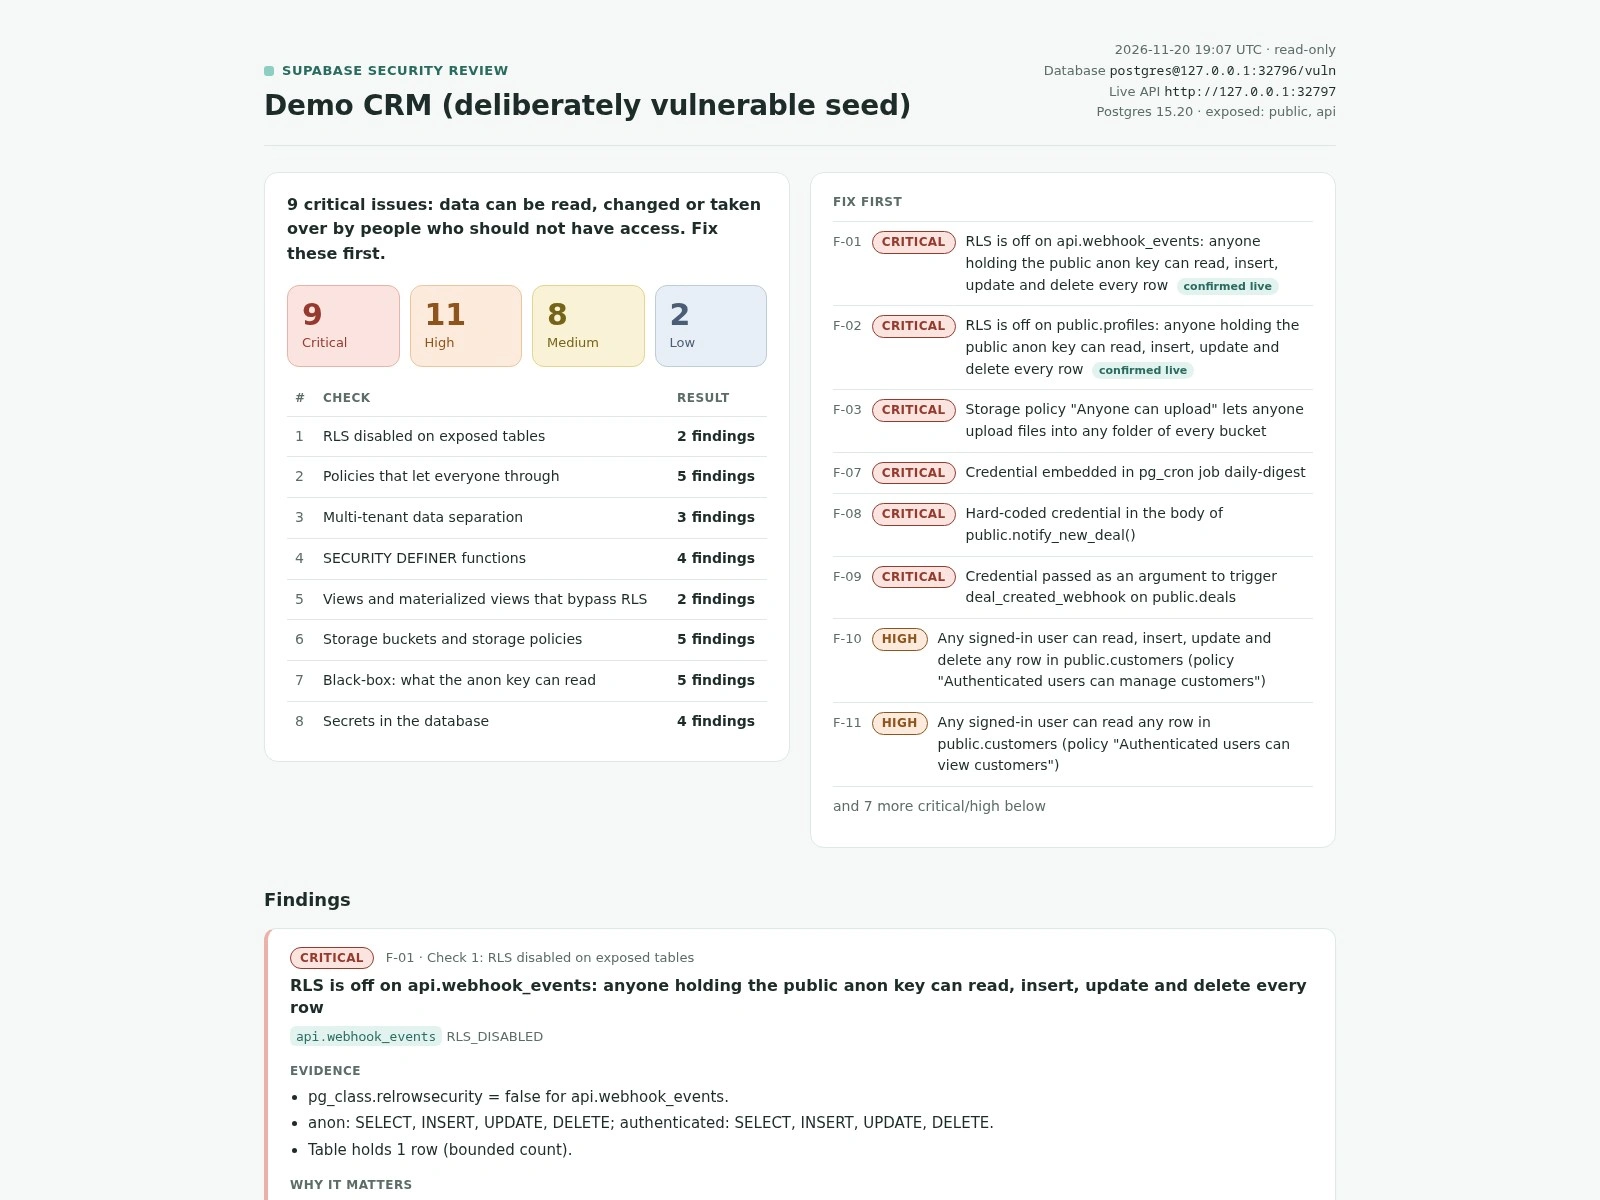
More and more apps are built with Lovable, Claude Code or Cursor on top of Supabase, and nobody with security experience ever looks at them. The usual problems are the same every time: tables without row level security, policies that let every signed-in user read everything, one customer able to see another customer's data, keys pasted into database functions.
This checker finds those in minutes. It connects read-only (the session refuses writes, and a full run leaves schema, grants, policies and data unchanged), runs 8 groups of checks, and writes a report sorted by severity with the evidence and the exact SQL fix for every finding. With the public anon key it also checks from the outside what an anonymous visitor can actually read.
The checks: row level security off on exposed tables; policies that let everyone through; multi-tenant separation; SECURITY DEFINER functions; views that bypass row level security; storage buckets and storage policies; what the anon key can read; secrets stored in the database.
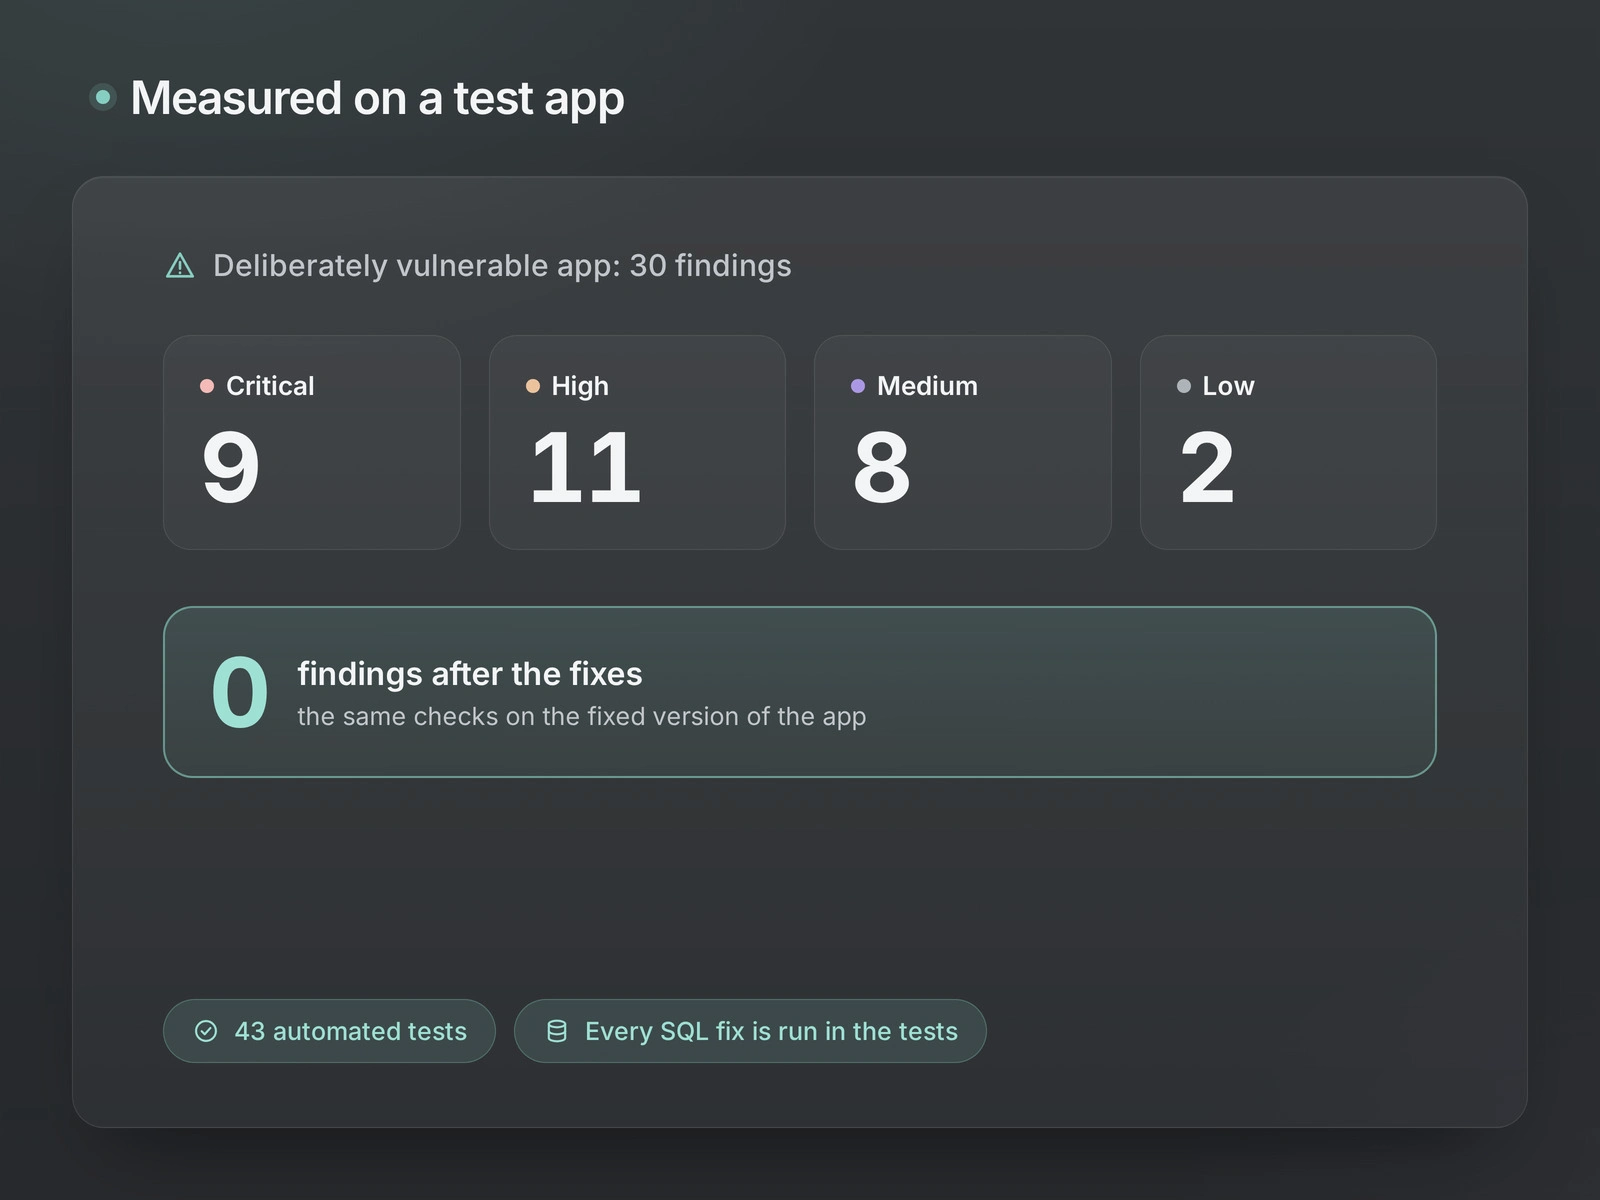
How it is proven: 43 automated tests against a deliberately vulnerable database and a fixed one. The vulnerable seed must give exactly the 30 expected findings, the fixed seed none, and every ready-to-run fix is applied to a copy and re-audited.
It is a first pass, not a pentest: edge function code and the frontend still get a manual review, and that review is part of the fixed-price service.
0 likes · 0 views · Nov 20, 2026
A read-only checker for Supabase apps built with AI tools: 8 groups of checks (row level security, open policies, multi-tenant leaks, SECURITY DEFINER, storage,