DORA-aligned post-quantum audit

Andrei Maroz
DORA Art. 9–10 · NIST FIPS 203/204/205 · €4990
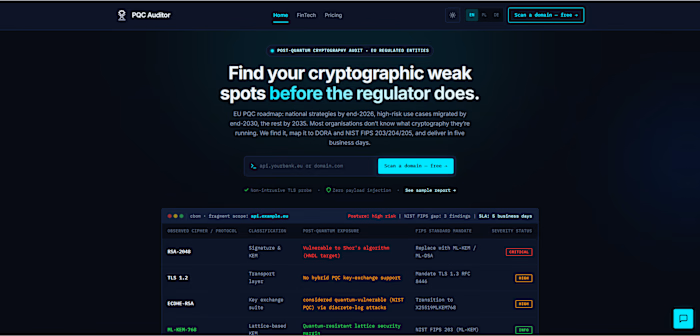
DORA-aligned post-quantum audit. Delivered in five business days.
Built specifically for KNF-, UKNF-, BaFin- and EIOPA-supervised entities navigating DORA Art. 9-10 and the EBA/GL/2025/02 guidelines. A fixed-fee deliverable structured to support inclusion in your ICT risk register.
Order FinTech audit — €4990 → Inspect sample reports ↓
Deterministic passive probe Zero impact on production TLS Operator-reviewed before delivery
For KNF / BaFin supervised entities
Tier: FinTech DORA
€4990 fixed one-shot fee · single scope
Up to twenty domains with DORA Art. 9-10 traceability and KNF Rekomendacja D / BaFin BAIT cross-references. Operator-reviewed before delivery.
Up to 20 domains with direct DORA Art. 9–10 traceability
KNF Rekomendacja D and BaFin BAIT ICT cryptography cross-references
Five-business-day contractual turnaround
SHA-256 hash of the source audit JSON and a signed CBOM
Free rework until your Risk Committee accepts the report
Operator-reviewed against the raw scan data before delivery
EU entities receive a reverse-charge VAT invoice (0% intra-community)
Supervisory pressures and quantum timelines
Why DORA-supervised entities choose us
Regulatory inspections under DORA have begun. Generic advisory questionnaires do not provide the concrete cryptographic inventory that European authorities ask for.
01
You can't migrate what you can't see
Most banks have no current inventory of the cryptography they actually run, and you cannot plan a post-quantum migration without one. We produce that inventory as a documented deliverable you can hand to an examiner.
02
Why the Big Four can't move fast enough
Big Four firms quote a 12-month engagement at six-figure EUR. We deliver in five business days because the supervisory deadline does not wait for an FY26 budget cycle.
03
Nobody else shows you a price
Fourteen out of fourteen EU PQC vendors we surveyed hide pricing behind "Request a demo". We publish €4990 because our scope is fixed.
HNDL
04
Harvesting is already happening
Sixty-nine percent of organizations recognize the quantum risk, yet only five percent have moved to quantum-safe encryption (DigiCert Quantum Readiness Gap). Encrypted traffic captured today can be stored and decrypted once a quantum computer exists, so the cost of postponing the audit is already running.
05
From DORA articles to the actual standards
DORA Art. 9 requires protection of cryptographic keys based on an approved data classification, but no standard deliverable connects that article to NIST FIPS 203/204/205. Ours does, mapping every finding back to the specific standard.
Format: PDF + JSON CBOM + audit trail
Full audit deliverable specification
What's in the report
Executive summary (3-6 pages) plus technical report (15-40 pages). Twelve standard sections including Cryptographic Bill of Materials (CBOM), per-finding FIPS mapping, DORA Art. 9-10 traceability matrix, a 0-3 / 3-12 / 12-24 month roadmap, scope, methodology, limitations and a comprehensive legal notice. SHA-256 hash of the source audit JSON in the appendix.
SEC 01
Executive summary
3–6 pages for board members and C-level officers.
SEC 02
Full technical report
15–40 pages of cryptographic detail across the scoped domains.
SEC 03
Cryptographic BOM (CBOM)
Inventory of the cryptography actually in use — algorithms, key lengths, hashes and signature schemes.
SEC 04
DORA Art. 9–10 matrix
Traceability from each finding back to DORA Articles 9 and 10.
SEC 05
NIST FIPS 203/204/205 mapping
Per-finding mapping to ML-KEM, ML-DSA and SLH-DSA.
SEC 06
Phased remediation roadmap
A 0–3 / 3–12 / 12–24 month sequence of migration work.
SEC 07
Scope
Documented engagement boundary for the domains in scope.
SEC 08
Methodology
How the scan, classification and operator review were performed.
SEC 09
Limitations
What the engagement does not cover, stated in the report.
SEC 10
Legal notice
A comprehensive legal notice in the delivered PDFs.
SEC 11
SHA-256 source hash
SHA-256 hash of the source audit JSON, recorded in the appendix.
SEC 12
Operator review before delivery
Operator-reviewed against the raw scan data before the report is sent.
Public evidence archive
Three full sample reports — read before you buy
The companies are fictional Polish profiles, but the report structure, the legal-safe language and the FIPS traceability are exactly what you receive. None of our competitors lets you read a full report before you buy.
Bank Krajowy, FastPay and InvestPro are fictional companies created for demonstration only. They do not exist and should not be searched for.
Large bank Fictional example
Large bank — Bank Krajowy
500 employees, KNF-supervised retail + corporate. Legacy core, mobile, web. 18-month remediation roadmap.
Mid-market fintech
Payment institution Fictional example
Mid-market fintech — FastPay
50 employees, UKNF Payment Institution. Modern GCP stack, microservices. 9-month roadmap.
0 CRITICAL
2 High findings
1 Medium finding
Investment firm Fictional example
MVP brokerage — InvestPro
8 employees, MiFID II investment firm. Vercel + Supabase + Stripe. 6-month roadmap.
High-assurance process
Methodology
01
Intake and scope
You submit domains, optional cryptographic-inventory hints and DORA register references. Five-step form, server-side validated, GDPR-bounded.
02
Passive scan
TLS handshake fingerprinting (sslyze), certificate-transparency log walk (crt.sh), security-header inspection. No active probing, no payload injection.
03
Analysis and independent verification
Our analysis engine builds a Cryptographic Bill of Materials (CBOM), classifies each finding against NIST FIPS 203/204/205, and maps it to the relevant DORA articles. An independent verification stage cross-checks every finding against the source scan data before anything is recorded.
04
Operator review and delivery
An operator-cryptographer reviews the auto-generated report against the original scan data before approval. Executive PDF + technical PDF delivered via signed link.
Market benchmark
Compare on the criteria that matter to a CISO
PQC Auditor FINTECH
Big Four / global firm
Security boutique
SaaS platform
Price
€4990 fixed fee
"Contact us" (€100k+)
"Contact us" (€40k+)
Annual subscription
Delivery time
5 business days
8-24 weeks
8-16 weeks
Ongoing
Per-finding FIPS 203/204/205 mapping
Yes
Implied
Product-mapped
DORA Art. 9/10 traceability
Yes
Partial
No
Money back if < 3 actionable findings
Yes
No
Public sample report
Yes
No
Engagement risk
Institutional assurance and legal guarantees
European financial entities operate under strict internal governance. We remove engagement risk with contractual delivery warranties.
Free rework warranty (FinTech tier)
If your ICT Risk Committee, Internal Audit, or a supervisory inspector (KNF / BaFin) asks for clarification or formatting changes on DORA Art. 9–10 or EBA guidelines, we rework at no extra cost until formal acceptance.
Actionable findings threshold
If fewer than three actionable PQC findings appear across the scoped endpoints, the environment is treated as ready. On FinTech that is covered by free rework through acceptance — you should not be paying us for an empty report.
Compliance and legal clarifications
Regulatory and technical FAQ
Will this report be recognised by KNF (UKNF) and BaFin?
The deliverable maps each finding to DORA Articles 9 and 10, NIST FIPS 203/204/205, EBA/GL/2025/02, KNF Rekomendacja D and BaFin BAIT. Final acceptance is the supervisor's prerogative; our role is to provide the audit trail those inspectors use.
How does this differ from SandboxAQ AQtive Guard or a continuous PQC SaaS?
AQtive Guard is an internal network sensor that needs host agents, deep taps and a long vendor onboarding. FinTech is a one-shot, non-intrusive external audit that establishes a regulatory baseline without changing infrastructure or signing a multi-year licence.
Can we receive deliverables in Polish or German?
Yes. Executive summary and technical body are available in English, Polish and German, with regional terminology (Rekomendacja D in PL, BaFin MaRisk/BAIT in DE). Specify the language in the intake form; default is English.
Does the scan affect production banking or payment API traffic?
No. We run standard TLS handshakes, record negotiated cipher suites, parse X.509 chains and close the connection. We do not inject payloads, fuzz parameters or stress server resources.
Secure your institution's post-quantum compliance today.
Avoid six-figure consulting retainers and multi-month delays. Receive a signed DORA Art. 9–10 audit, structured for your ICT risk register, in five business days.
Operated from the EU. Contact: hello@pqcaudit.eu
Like this project
Posted Oct 29, 2026
DORA-aligned post-quantum audit (FinTech tier). Fixed €4,990, up to 20 domains, PDF + JSON CBOM, operator-reviewed and delivered in five business days.
Likes
0
Views
0
Tags