Yōjin: Fine-Tuned LLM for Cybersecurity GRC (Client Project)

Tran Tien Van


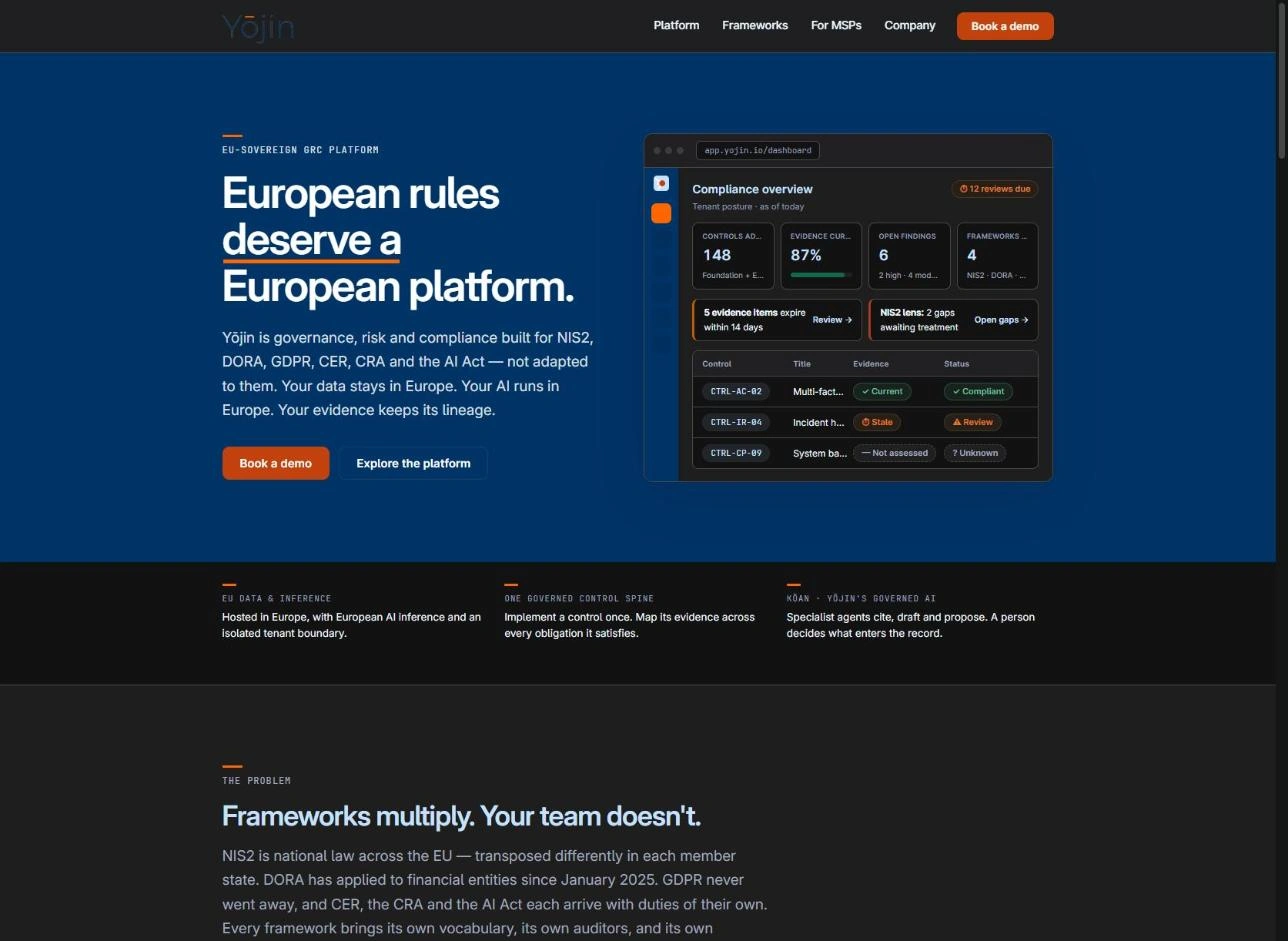
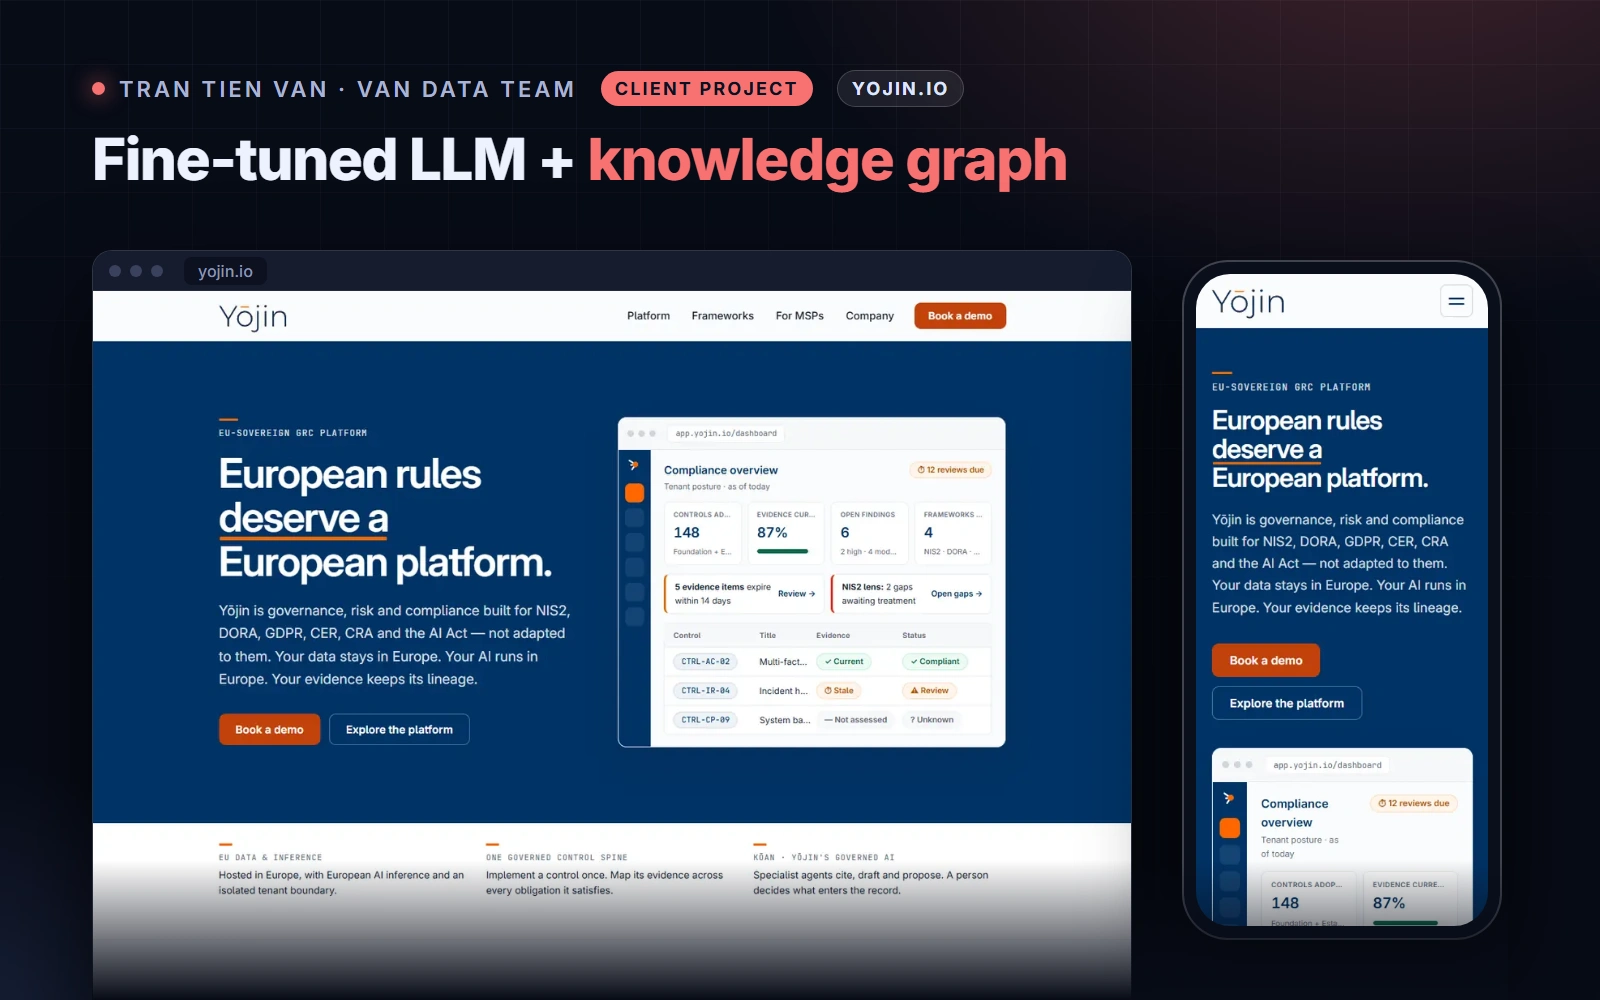
Client project. Built by Van Data Team for Yōjin, an EU-sovereign governance, risk and compliance (GRC) platform for enterprises and managed service providers. Live product: yojin.io
The challenge
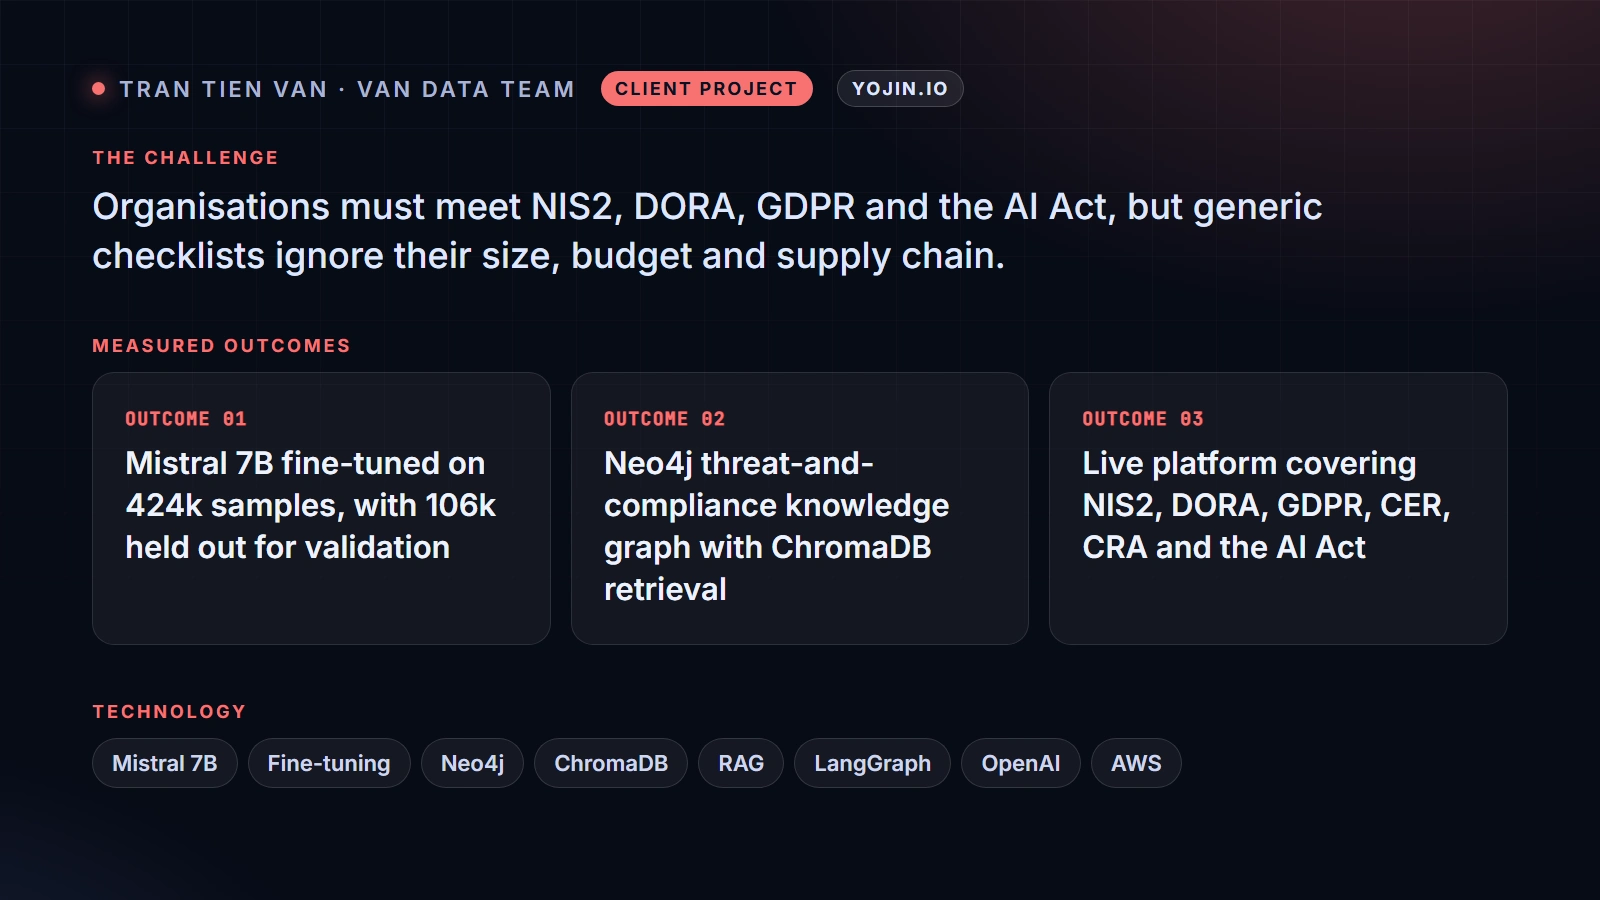
Organisations must meet NIS2, DORA, GDPR and the AI Act, but generic checklists ignore their size, budget and supply chain, and general language models do not know the frameworks well enough to advise on them.
What we built
Mistral 7B fine-tuned on 424k training samples, with 106k held out for validation, in runs of about four hours
A Neo4j graph that models threats, controls and compliance obligations
ChromaDB-backed retrieval (RAG) over the knowledge base
LangGraph orchestration across the fine-tuned model, the graph and the vector store, with OpenAI models alongside, on AWS
Results
Mistral 7B fine-tuned on 424k samples, with 106k for validation
Neo4j threat-and-compliance knowledge graph with ChromaDB retrieval
Live platform covering NIS2, DORA, GDPR, CER, CRA and the AI Act
Key decision
A fine-tuned 7B model instead of a large general one: a smaller model trained on the domain can be served where the customer's data has to stay.
Stack: Mistral 7B, fine-tuning, Neo4j, ChromaDB, RAG, LangGraph, OpenAI, AWS.
Full case study: vandatateam.com/portfolio
Like this project
Posted Nov 5, 2026
Client project for Yōjin: Mistral 7B fine-tuned on 424k samples, Neo4j knowledge graph and RAG for NIS2, DORA, GDPR and AI Act compliance on AWS.