Security review of a Supabase app before launch

Jacob Spradlin


The situation
A founder was about to launch a React Native app on Supabase, with serverless API routes, transactional email and push notifications. Before real users arrived, they wanted an independent review of security and scalability.
What I did
Read every migration and Row Level Security policy, then traced each server endpoint for authentication, authorization and input handling.
Verified the live database's actual grants and policies against what the migrations said. The two had drifted, and several of the worst problems only existed in the live database.
Ranked every finding by severity, with the file, why it mattered and the fix.
What I found
The review turned up 3 critical, 11 high and 19 medium findings, plus more from the live-database check. Examples:
Privilege escalation. A "users can update their own profile" policy also let any user set their own admin flag, because Row Level Security gates rows, not columns.
Duplicate permissive policies. A correctly scoped policy sat next to a wide-open one. Permissive policies combine with OR, so the open one won and any user could join any private conversation.
Anonymous access. The anonymous role held full read and write grants on every public table.
An open email relay. An endpoint let any signed-in user send any content to any address from the product's own domain.
Silent failures. Server code quietly fell back to anonymous permissions when a key was missing, instead of failing.
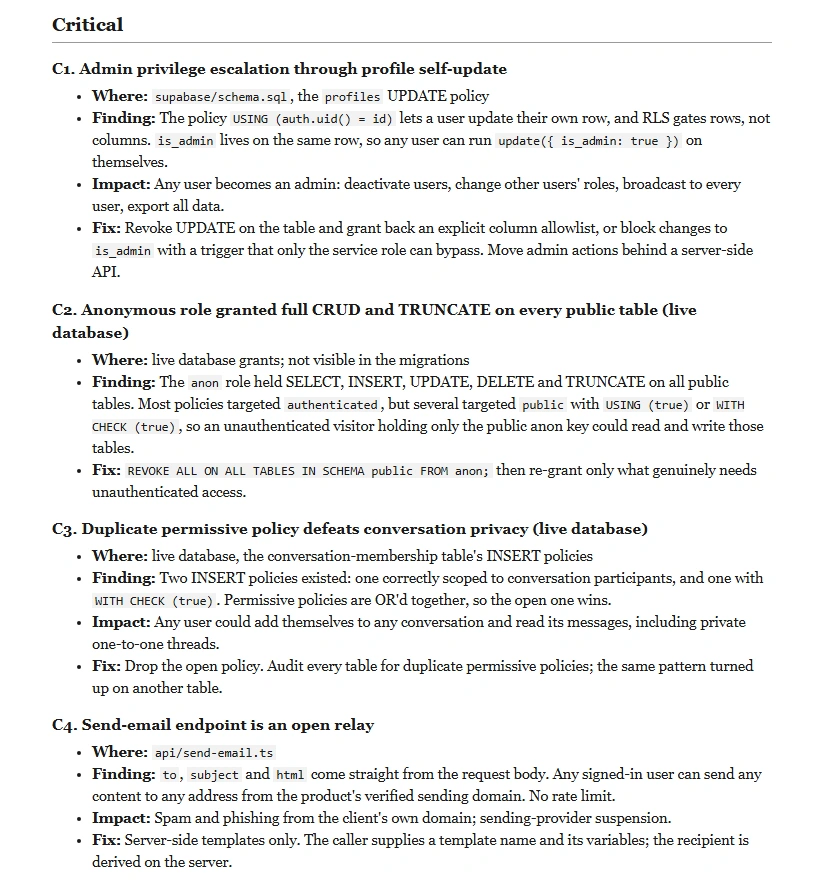
The critical findings section of the redacted sample report
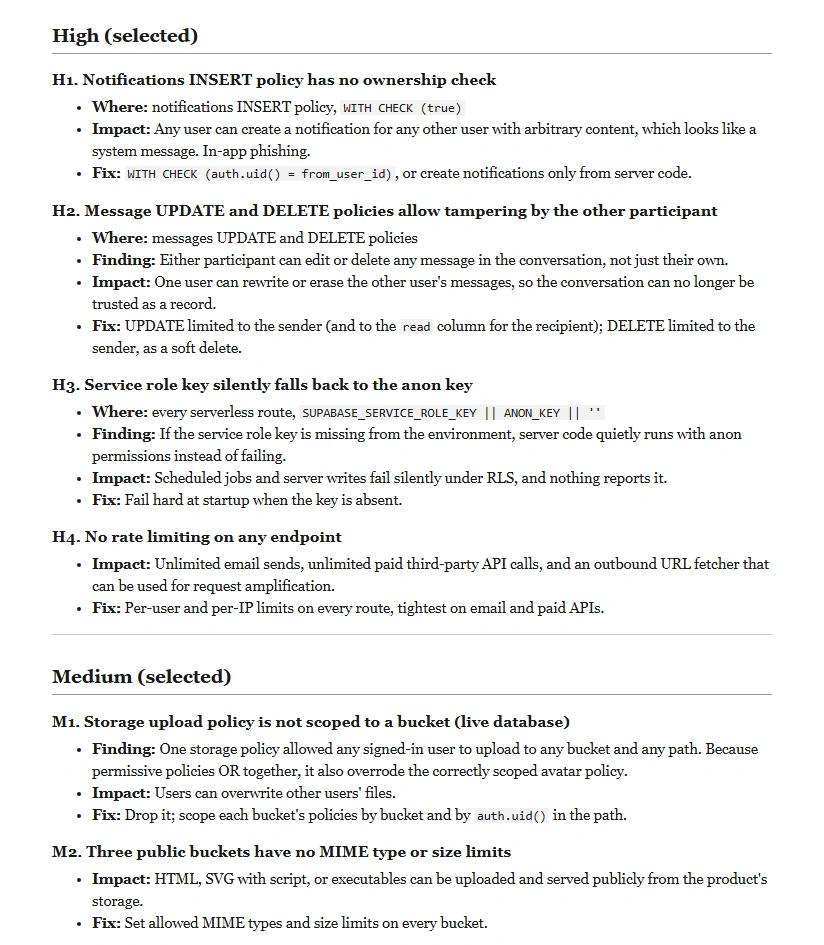
The high and medium findings sections of the redacted sample report
The result
A prioritized remediation plan: what to fix today, this week and next sprint. The work continued into a follow-up contract to fix what the review found.
Client and product details are withheld.
Like this project
Posted Oct 5, 2026
Pre-launch security and scalability review of a React Native and Supabase app: 3 critical and 11 high findings, ranked by severity, each with a fix.
Likes
0
Views
2