I built a Python CLI

Joseph Joseph


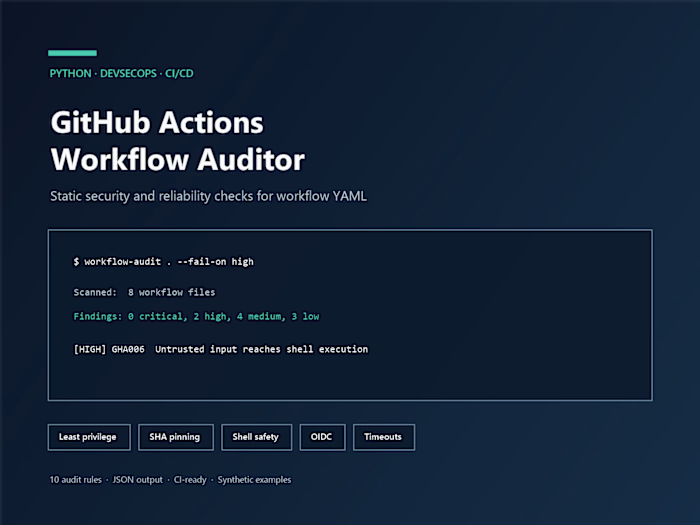
I built a Python CLI that statically reviews GitHub Actions workflows for security and reliability risks. It detects excessive permissions, mutable action references, unsafe shell interpolation, privileged pull-request patterns, missing timeouts and concurrency controls, OIDC boundary concerns, and broad secret inheritance.
The project includes 10 focused audit rules, human-readable and JSON output, CI-friendly exit codes, synthetic before-and-after workflows, 11 unit tests, and its own hardened GitHub Actions pipeline. The auditor does not execute workflow code, and all examples are public and synthetic.
Like this project
Posted Sep 12, 2026
I built a Python CLI that statically reviews GitHub Actions workflows for security and reliability risks. It detects excessive permissions, mutable action re...
Likes
0
Views
1
Timeline
Sep 11, 2026 - Sep 12, 2026