
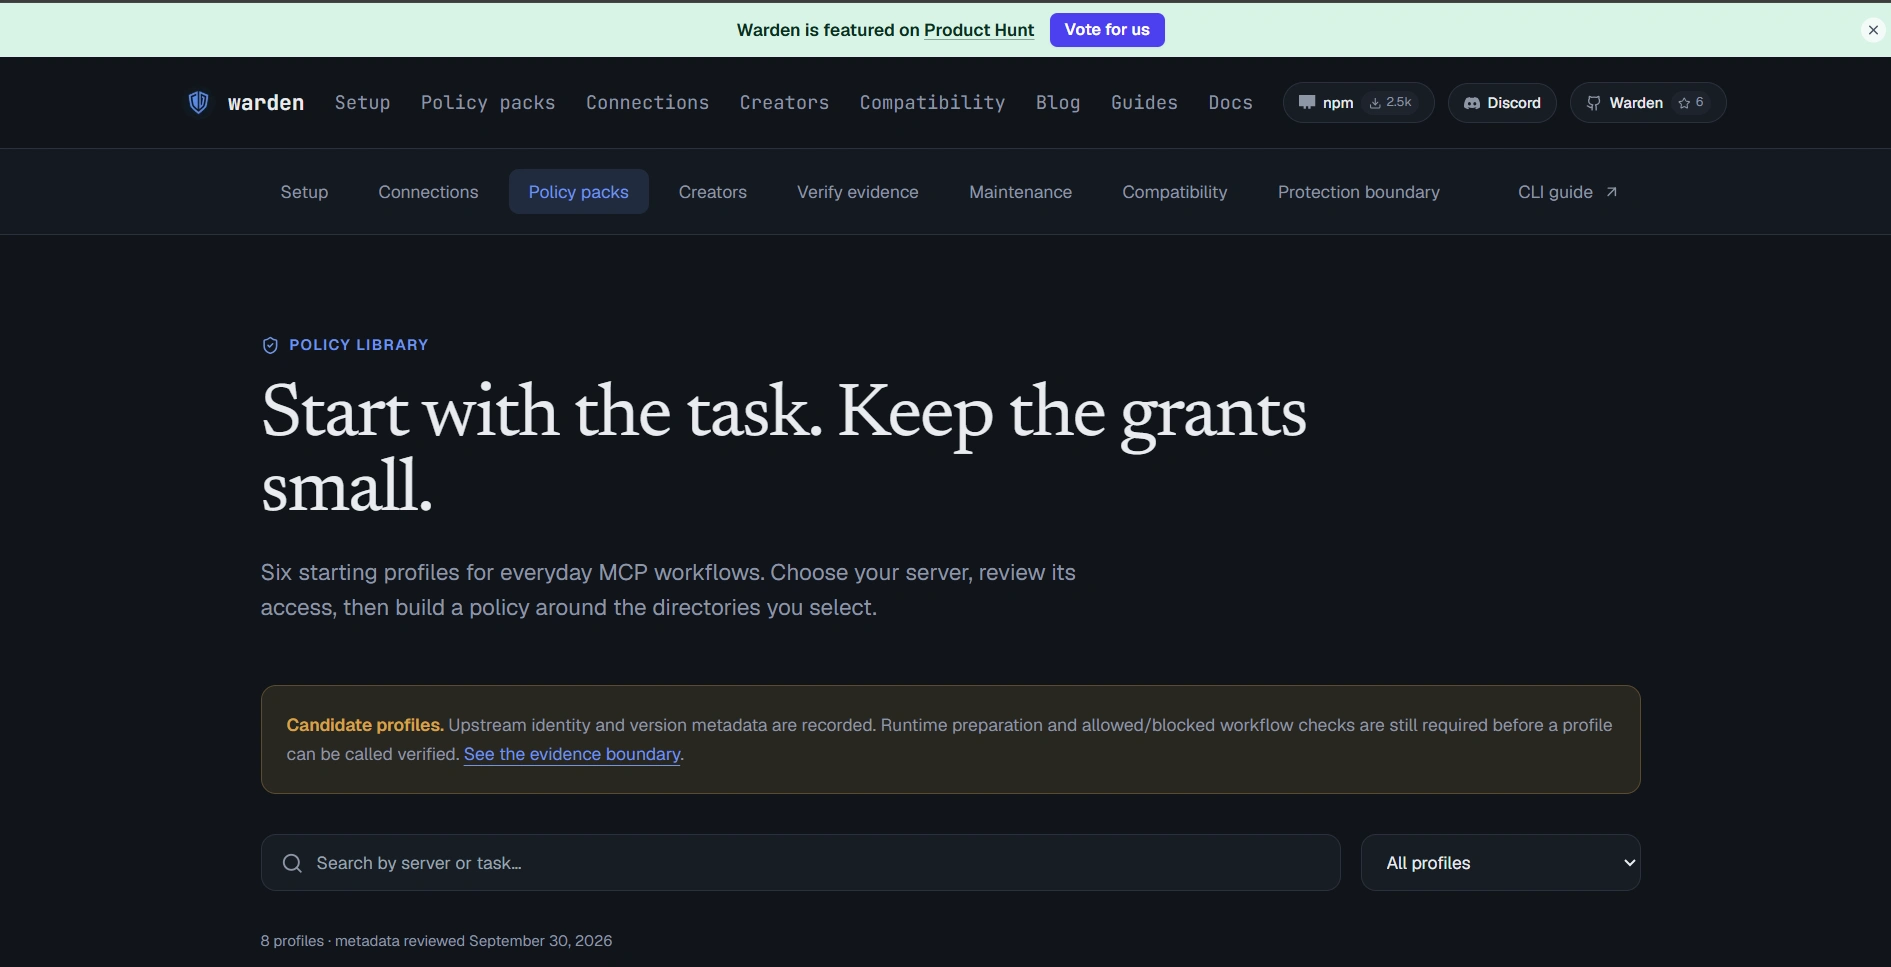
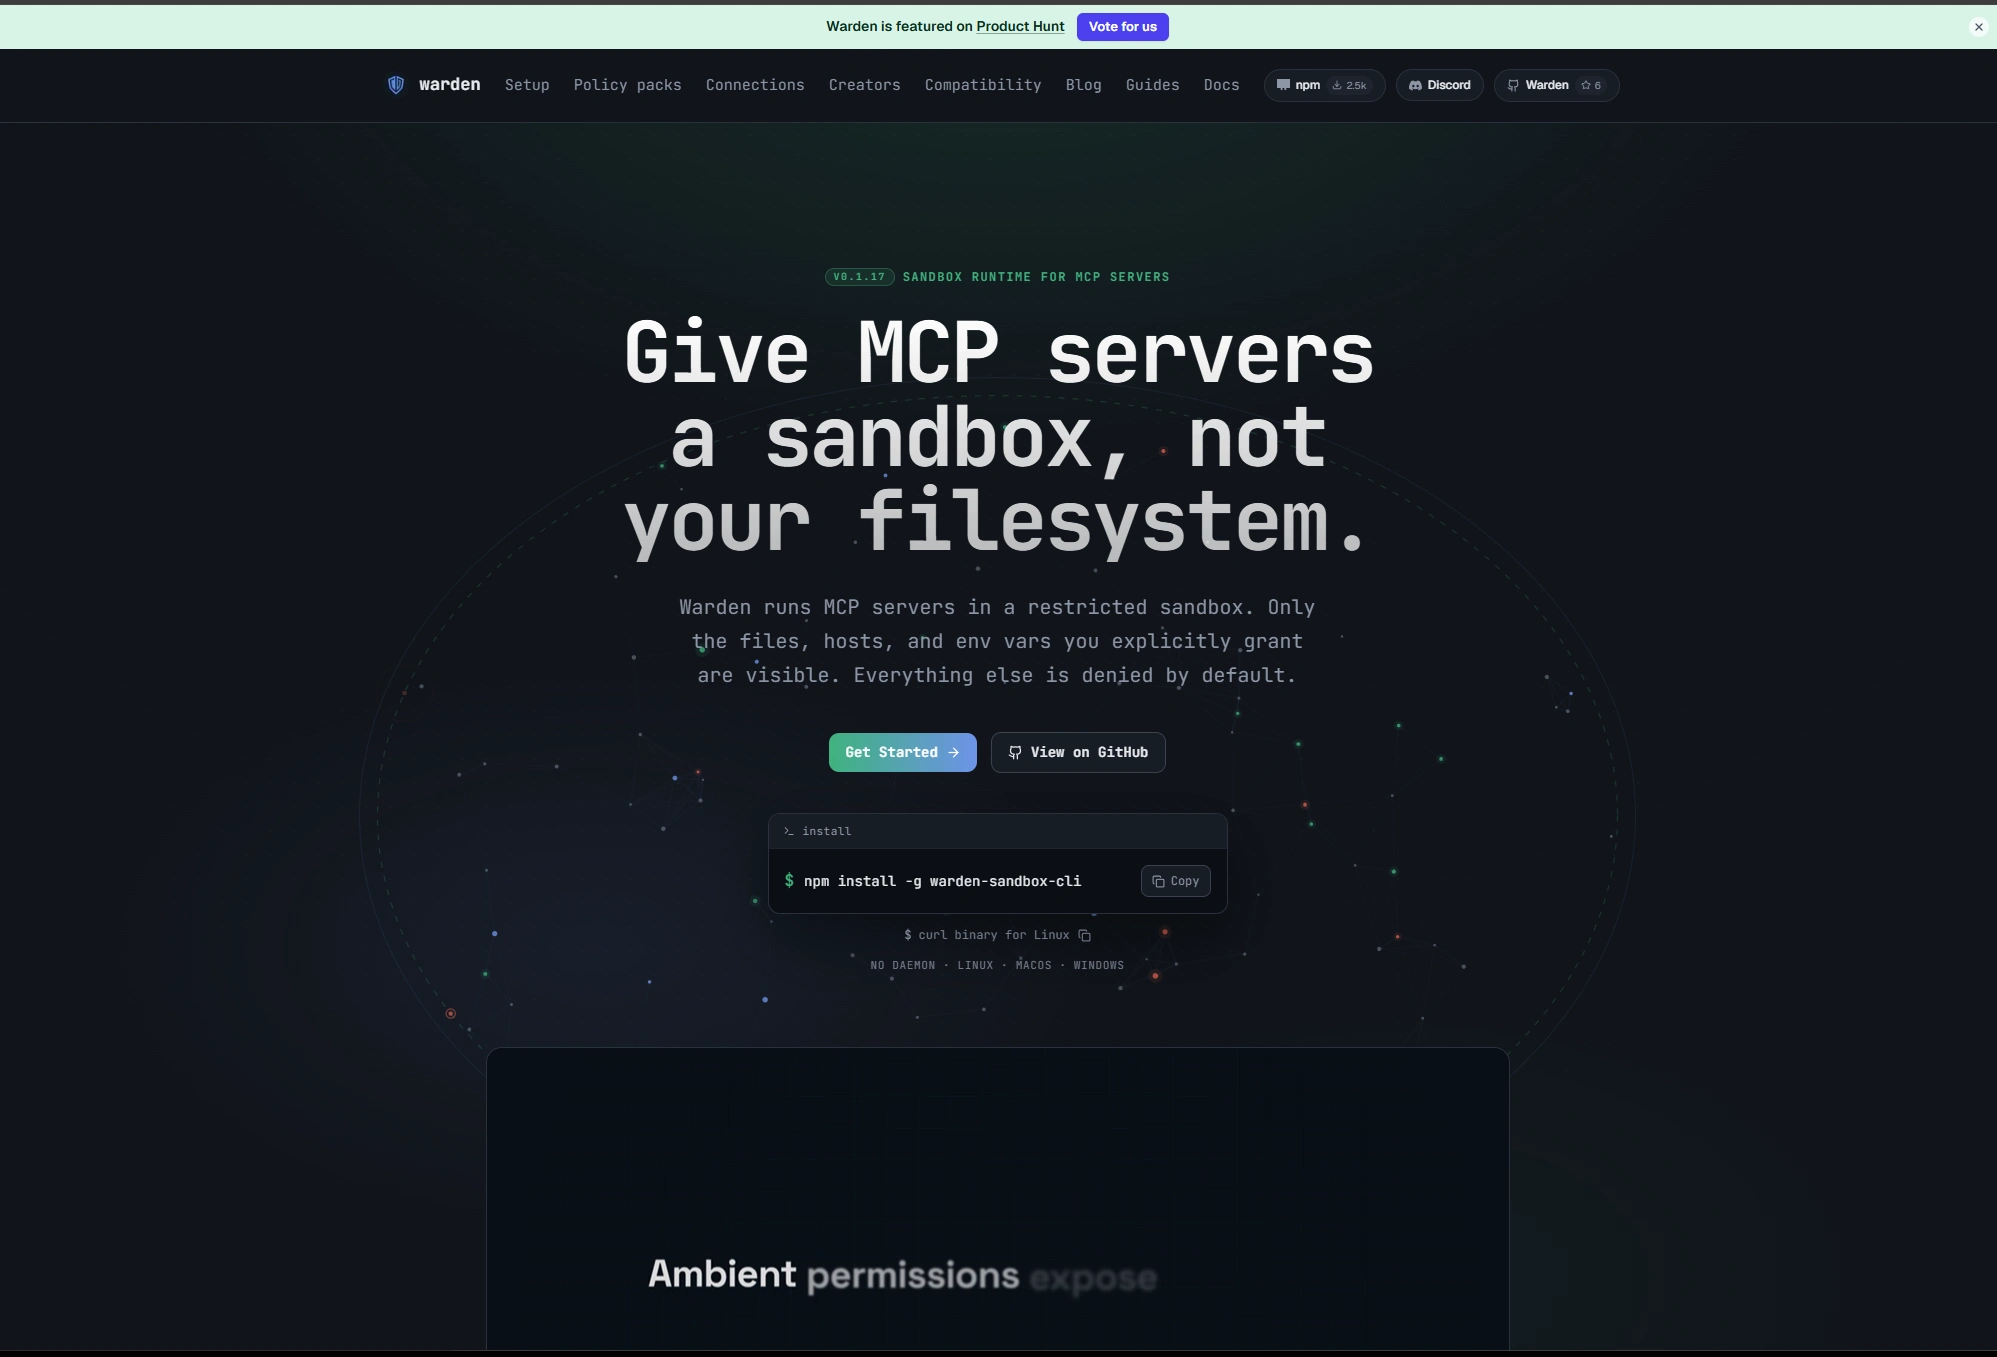
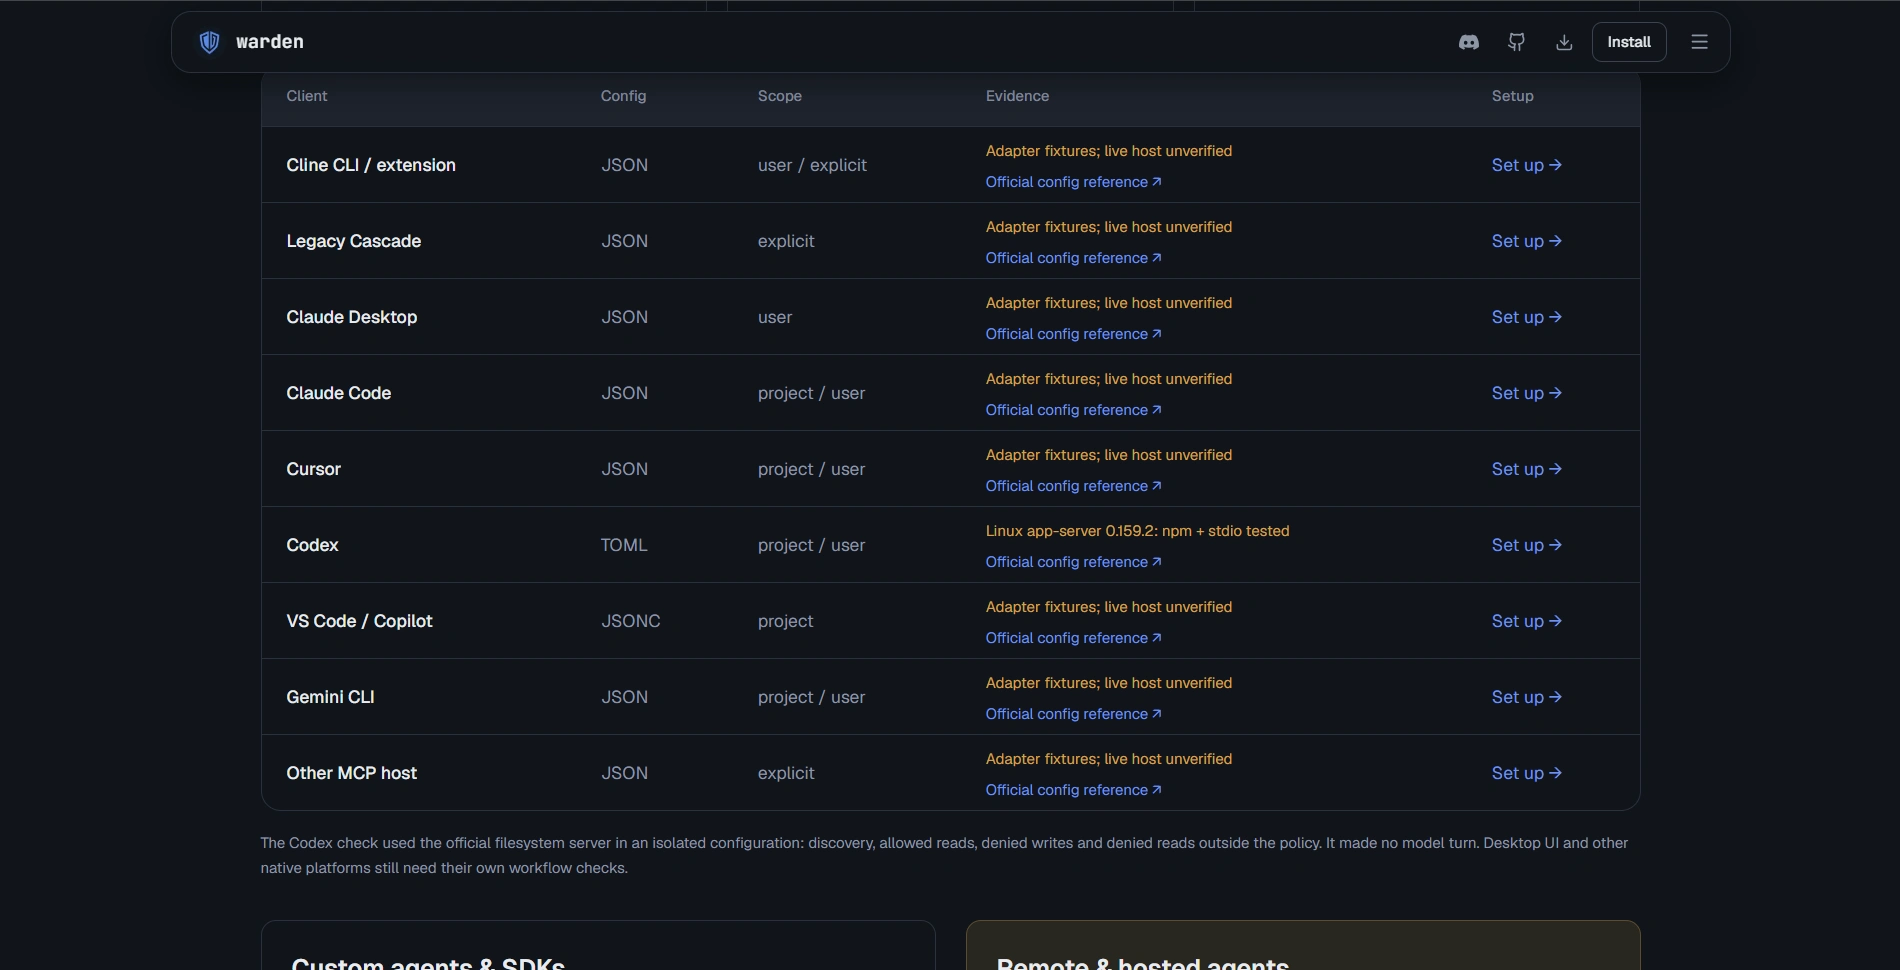
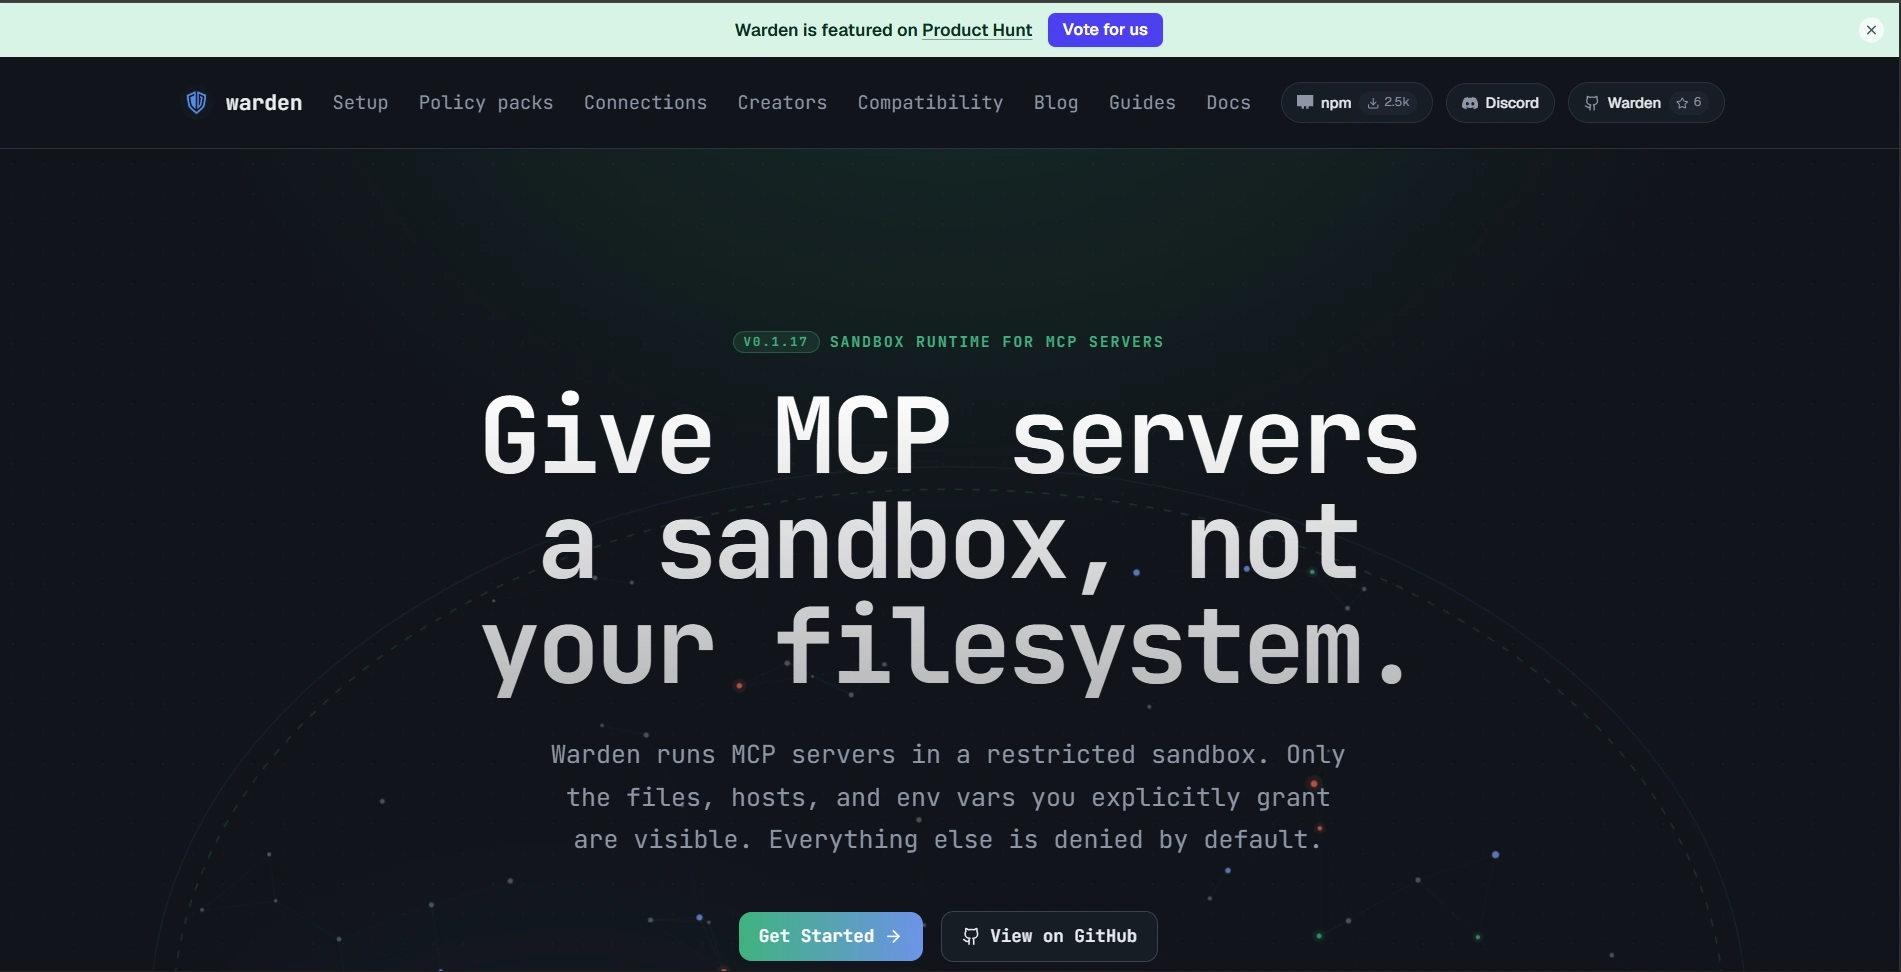
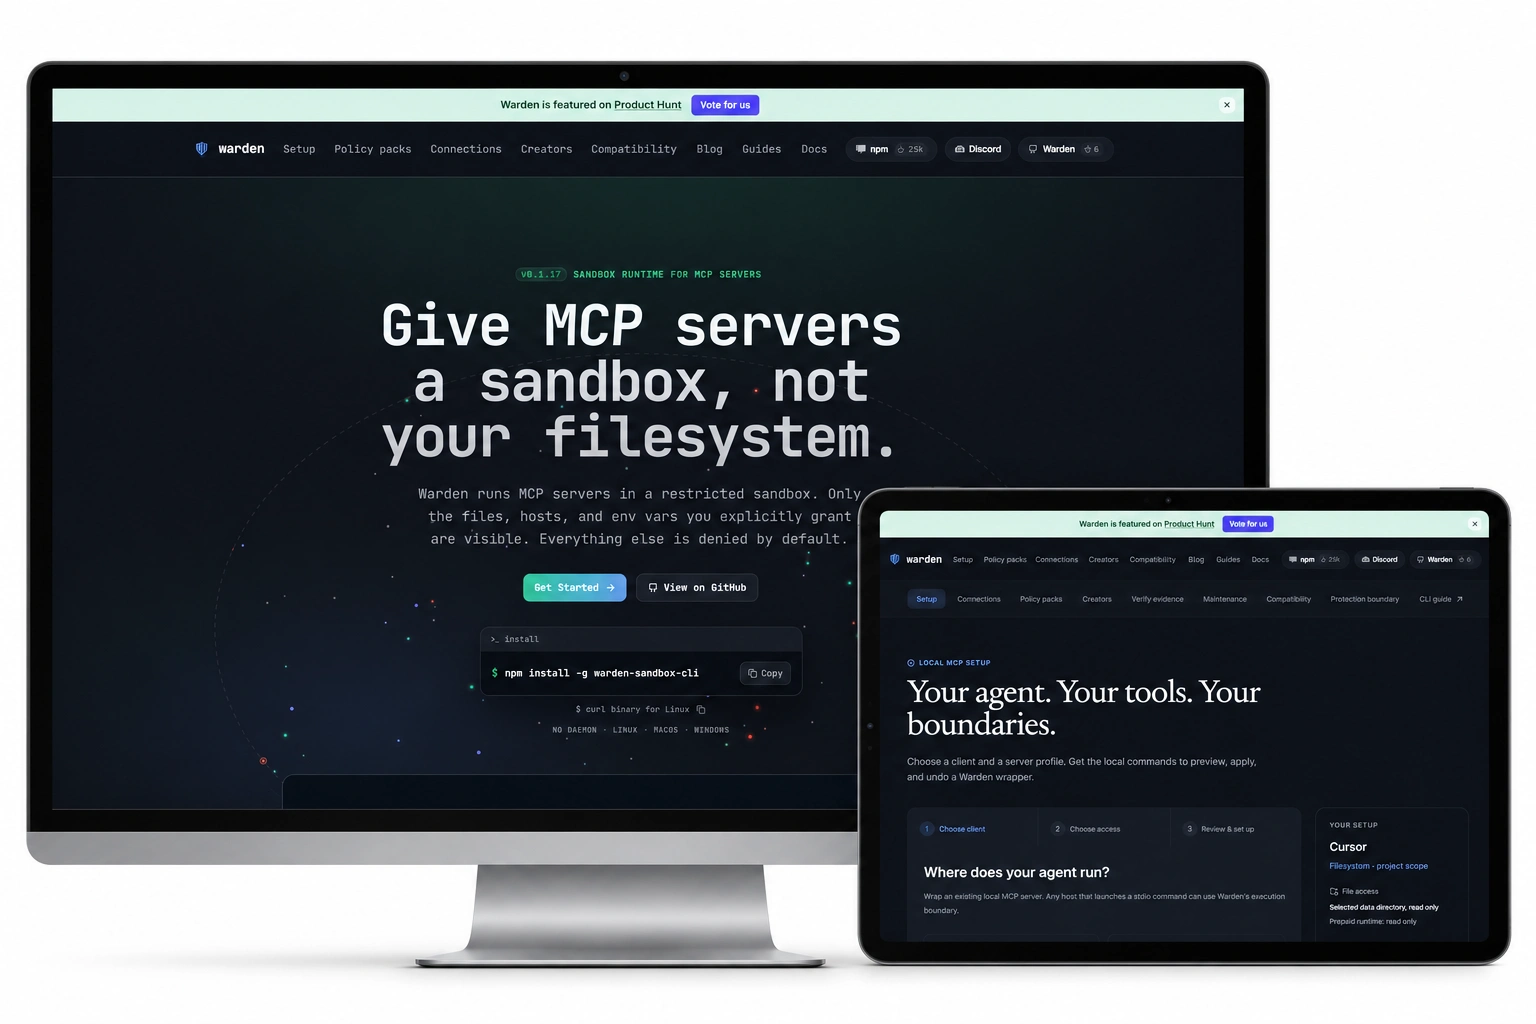
AI assistants now run MCP servers on developers' machines, and those servers can read files and run commands. One bad or compromised server can reach everything. Warden puts each MCP server in a sandbox that blocks anything not explicitly allowed.
I co-founded Warden and built the core.
Threat model first
I wrote the threat model that defines what a server may and may not touch.
Fail-closed wrapper
The core wrapper uses macOS sandbox-exec, with a Docker fallback. If the policy cannot be applied, the server does not start.
Policies checked in CI
Every policy is verified in CI on each change, so a bad rule never ships.
Open source
The code is public and anyone can audit it.
Building developer tools or AI infrastructure? Send me a message.
0 likes · 0 views · Nov 12, 2026
Co-founded and built an open-source security layer that runs AI tool servers (MCP) inside a sandbox.


