
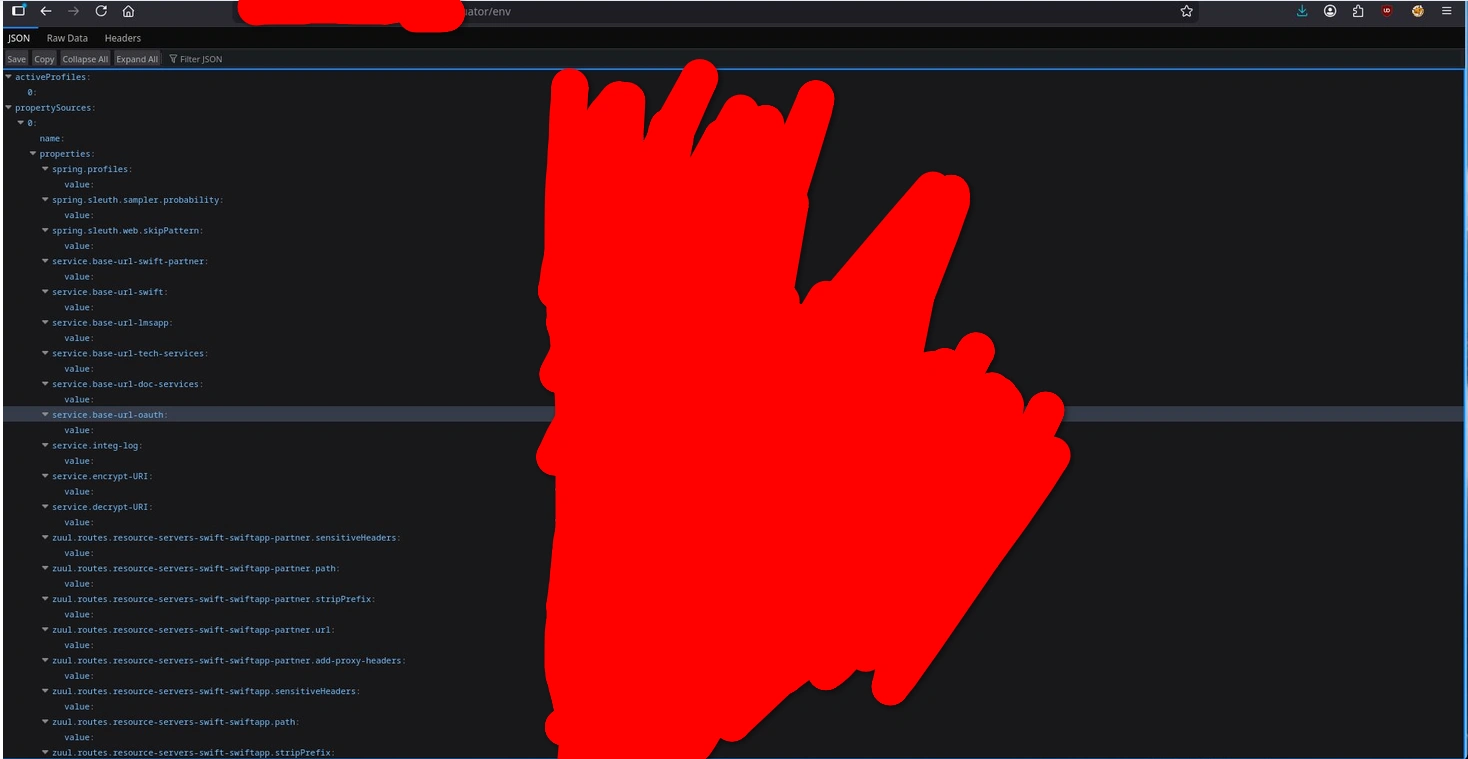
Recently identified a publicly accessible Spring Boot Actuator /env endpoint during a security assessment.
What initially appeared to be a routine configuration exposure turned out to reveal:
• Internal service architecture
• Backend microservice endpoints
• Internal hostnames and network information
• Deployment and filesystem details
• Security configuration settings
• Credentials and encryption-related secrets
This serves as a reminder that management interfaces can expose far more than operational metadata when left accessible in production environments.
Key lessons:
✓ Restrict Actuator endpoints to trusted administrative networks
✓ Avoid exposing /env in production
✓ Review environment variables and configuration repositories for secrets
✓ Rotate any exposed credentials immediately
✓ Use least-privilege exposure lists rather than wildcard endpoint exposure
Small configuration mistakes can create a complete roadmap of an organization's internal infrastructure.
#CyberSecurity #AppSec #SpringBoot #DevSecOps #BugBounty #SecurityResearch #OWASP #InfoSec
0 likes · 0 views · Jun 27, 2026
Recently identified a publicly accessible Spring Boot Actuator /env endpoint during a security assessment. What initially appeared to be a routine configurat...
Timeline
Jun 10, 2026 - Jun 11, 2026
