Approval-aware browser automation

Alejandro Silva Hermida


How to automate preparation without turning every click into an uncontrolled action
Browser automation often starts as a list of clicks. That model works for a short demo and fails in real operations. Pages change, sessions expire, forms validate data asynchronously and one final button may publish content, send a message or commit a payment. A reliable workflow needs a model of consequences, not just coordinates.
Separate preparation from commitment
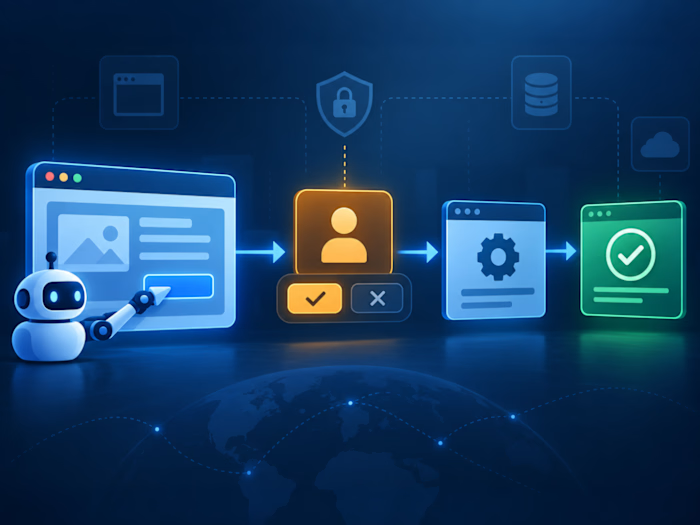
Most browser tasks contain a long reversible phase and a short consequential phase. Searching, opening records, drafting text and filling non-sensitive fields are usually recoverable. Submitting a legal acceptance, sending a message, placing an order or making a page public changes external state.
Make that boundary explicit in the workflow definition:
The automation should be able to repeat the preparation phase without repeating the commitment. This is especially important after a timeout: an unclear response does not prove that a submission failed.
Use semantic evidence
A screenshot is useful context, but it is weak evidence for many decisions. Text labels, accessible roles, field values, URLs and structured page state are easier to compare and less sensitive to layout changes. Before acting, verify the destination account, page title and expected form state from current information.
Coordinates can still be used when an interface exposes no better control, but they should follow a fresh page observation. Reusing a coordinate after navigation or a modal change is an avoidable source of errors.
Keep credentials out of the workflow record
A user can enter a password or verification code directly when needed. The automation does not need to print it, save it in a project file or include it in diagnostic output. Prefer limited access links and scoped tokens over full account credentials. If a task can be completed with a draft or preview, stop there until the account owner confirms the final action.
A useful rule: store enough context to resume the process, but never store a secret merely because it would make resuming easier.
Design for idempotency
An idempotent step can be repeated without creating a second external result. Draft preparation is naturally idempotent when it overwrites the same local artifact. Submission often is not. Add a stable operation identifier when an API supports one. When it does not, reconcile the destination before retrying: check whether the post, application or order already exists.
The same principle applies to form creation. If an account may have been created during a network timeout, try to sign in or request a password reset before submitting the registration again.
Verify the result at the correct layer
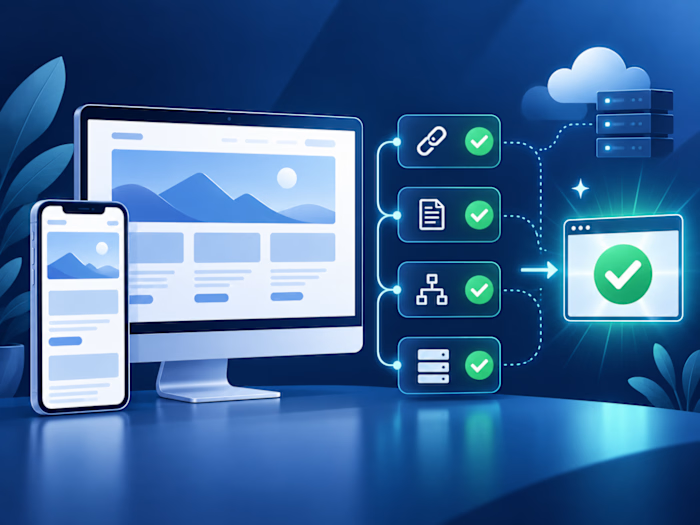
A click without an error proves very little. After commitment, check the authoritative external state: the published URL, sent-message thread, order record or account dashboard. Capture only the fields needed to show success. If the external state remains ambiguous, report that uncertainty and avoid a duplicate action.
For longer workflows, retain a compact state record with the current stage, destination, last verified result and next allowed action. This is operational recovery information, not a transcript of every screen.
A compact acceptance test
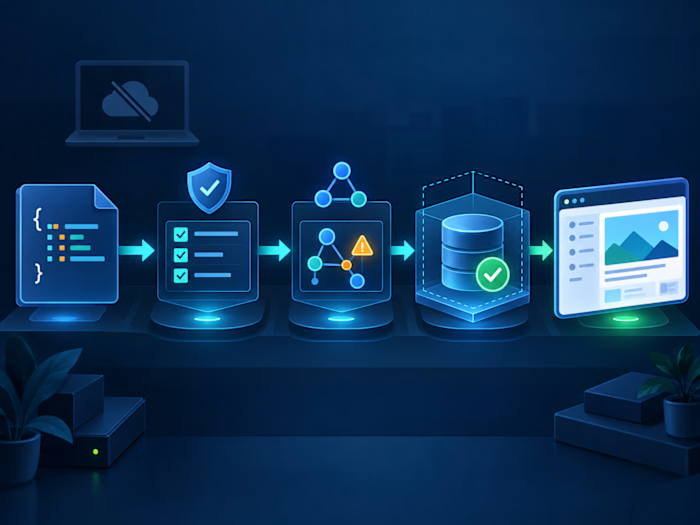
Before deploying a browser automation, test at least these cases:
the expected page and a changed-page variant;
an expired login session;
missing required data;
validation failure before submission;
a timeout immediately after submission;
a second run after the external result already exists;
withdrawn approval before the commit step.
The strongest automation handles the ordinary path quickly and makes the exceptional path safe. Preparation can be aggressive and efficient. Commitment should be deliberate, singular and verified.
Like this project
Posted Sep 20, 2026
Original AI-assisted technical note on safe, idempotent browser workflows with explicit approval boundaries and verification.
Likes
0
Views
0