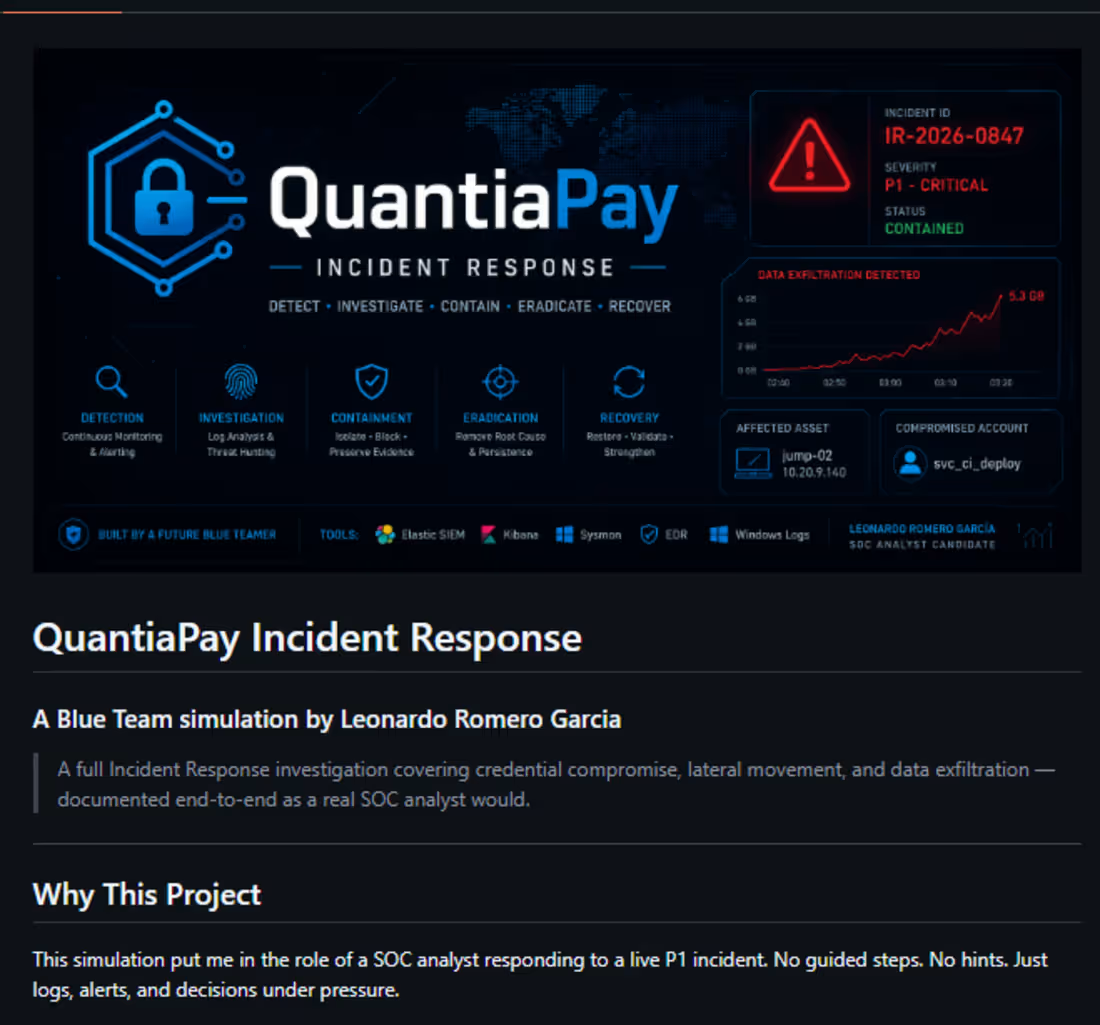
QuantiaPay Incident Response
A hands-on Blue Team incident response simulation investigating credential compromise, lateral movement, and data exfiltration. Documented end-to-end using SOC investigation workflows, attack timeline reconstruction, and incident response procedures.
0
7
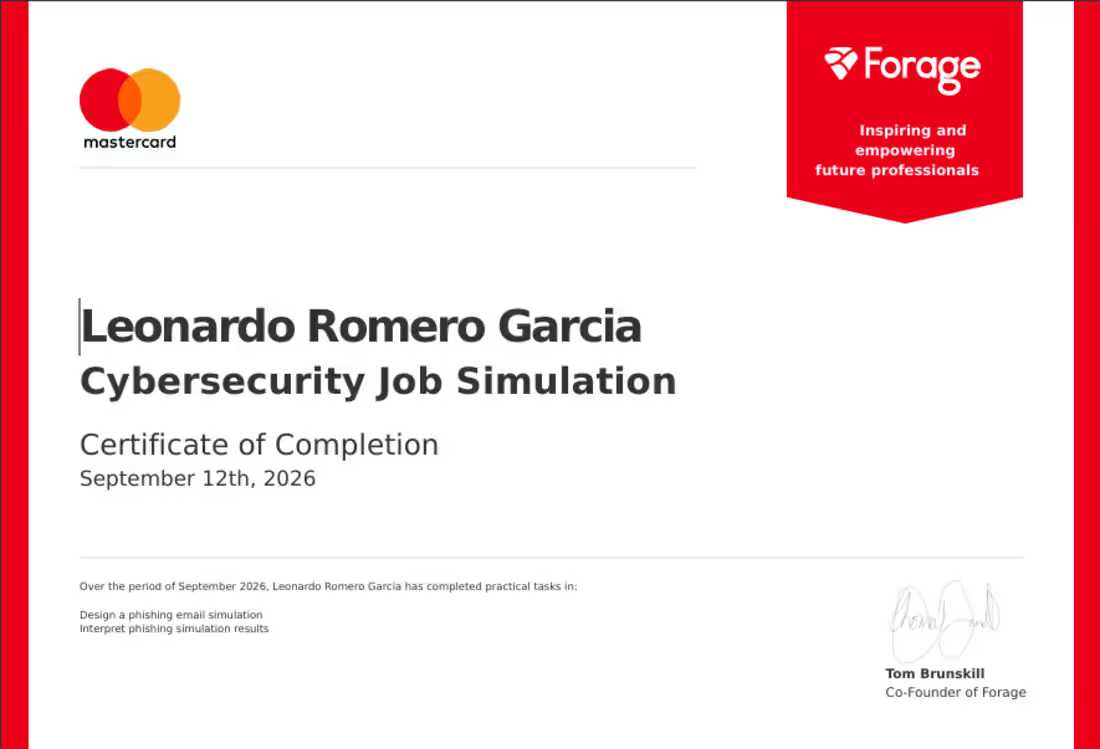
Mastercard Phishing Email Evaluation And Presentation
Completed a Cybersecurity Job Simulation in September 2026, gaining hands-on experience designing phishing email simulations and interpreting simulation results to evaluate user susceptibility and identify potential security awareness gaps.
0
11
AWS Incident Response Demonstrated
Completed hands-on incident response exercises focused on identifying, investigating, and remediating security issues in AWS cloud environments.
The practical assessment involved analyzing security findings, troubleshooting cloud configurations, prioritizing remediation tasks, and working through incident response scenarios under time constraints.
Through this experience, I strengthened my understanding of cloud security operations, incident investigation, remediation workflows, and systematic troubleshooting in AWS environments.
This project reflects my practical approach to cybersecurity: identifying the root cause of security issues, applying targeted fixes, validating the results, and documenting the work performed.
Skills: AWS Security, Cloud Incident Response, Security Remediation, Troubleshooting, Incident Investigation, and Technical Documentation.
0
14
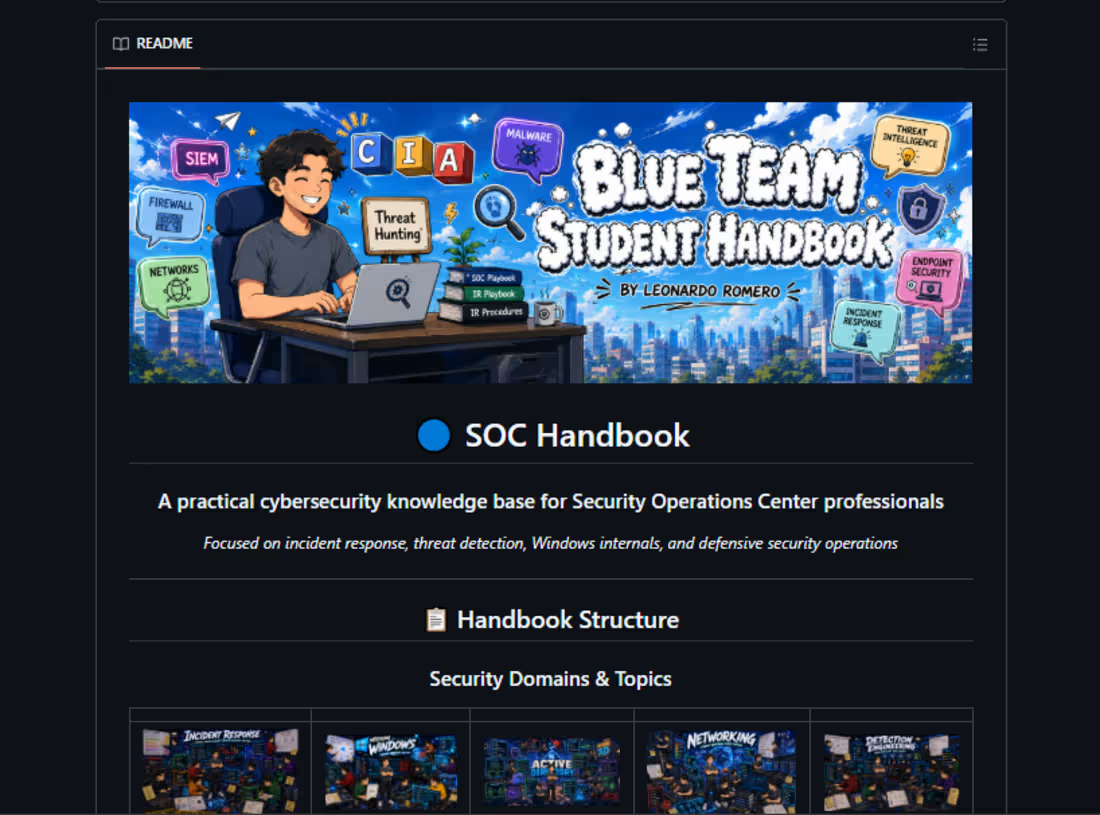
Blue Team Student Handbook
An open-source, collaborative cybersecurity handbook designed to help students and aspiring SOC analysts develop practical Blue Team skills.
The project organizes key cybersecurity concepts into a structured learning resource covering SOC fundamentals, networking, Windows and Linux security, Active Directory, log analysis, SIEM, threat hunting, incident response, DFIR, MITRE ATT&CK, detection engineering, and cloud security.
Its goal is to bridge the gap between theoretical knowledge and practical security operations by encouraging learners to investigate, reason, practice, and understand how defensive security techniques are applied in real-world scenarios.
Built as a community-oriented knowledge base, the handbook aims to make cybersecurity learning more accessible through structured explanations, practical exercises, common mistakes, and career preparation resources.
0
18