Projects in SakrandProjects in SakrandAI-Enabled Automated Vulnerability Scanner (AVS)
Project Overview
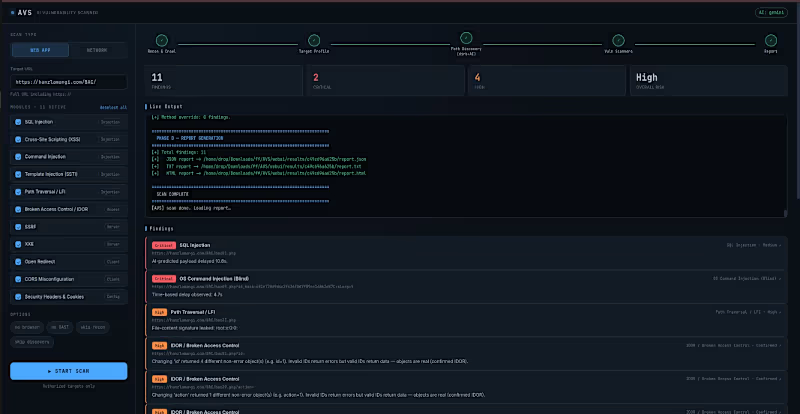
The AI-Enabled Automated Vulnerability Scanner (AVS) is a comprehensive cybersecurity application engineered to proactively identify, test, and evaluate complex network and web-based security risks. Built as a rigorous defense project, this tool streamlines the vulnerability management lifecycle by moving beyond basic static rule-matching. It leverages automated intelligence to map digital environments, expose critical security flaws, and deliver actionable, developer-ready risk assessments, enabling teams to secure their applications efficiently before deployment.
Core Architecture & Features
Intelligent Crawler Extraction: Automatically navigates and maps complex web architectures to discover hidden endpoints, directories, and exposed digital assets.
Dynamic Parameter Fuzzing: Systematically injects unexpected or malformed data into input parameters to expose unhandled exceptions and hidden injection vectors.
Method Overriding Detection: Analyzes HTTP method configurations to identify insecure API implementations, bypass attempts, and unauthorized access routes.
Contextual Risk Scoring: Evaluates discovered threats based on real-world exploitability, prioritizing critical vulnerabilities and generating structured defense documentation.
Vulnerability Detection Scope
The AVS engine is designed to automatically detect and evaluate 11 distinct classes of critical web vulnerabilities:
Injection & Execution: SQL Injection (SQLi), Cross-Site Scripting (XSS), Command Injection, and XML External Entities (XXE).
Access & Authentication: Broken Authentication, Broken Access Control, and Server-Side Request Forgery (SSRF).
System & Data Exposure: Security Misconfiguration, Insecure Deserialization, Sensitive Data Exposure, and Directory Traversal.