

Full-Stack & AI Dev | TypeScript, Next.js, React, Node
- $50k+
- Earned
- 5x
- Hired
- 5.0
- Rating
- 137
- Followers
Full-Stack & AI Dev | TypeScript, Next.js, React, Node
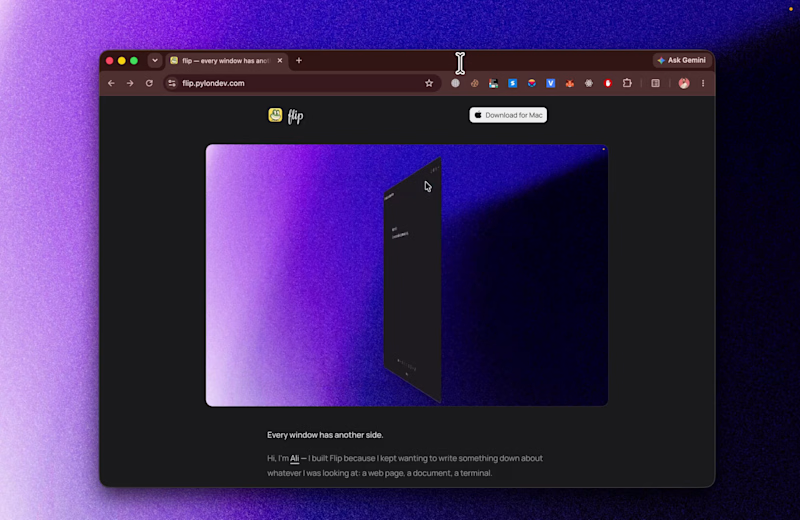
Built a little Mac app called Flip, and it somehow went viral on Twitter.
The idea is pretty simple. What if every window on your Mac had a back side where you could keep notes? So I built exactly that.
Flip any window, jot something down, flip back. Your notes stay attached to that window.
No extra apps to switch between.
Built natively for macOS, completely local, and free.
Check it out: https://flip.pylondev.com
Here’s the original tweet:
https://x.com/skimmycat20/status/2096580098506084400
2
3
188


AI Engineer | Voice AI, RAG, Document AI, n8n

Cloud Infrastructure Engineer · AWS · Kubernetes · Docker

Preview Environment System · CI-Driven · Full Stack
Automated preview environment system triggered by CI pipelines. On every PR tagged for preview, a GitHub Actions pipeline builds and pushes a branch-tagged Docker image, which triggers a Northflank webhook to instantiate a full-stack environment from a template — server, worker, PostgreSQL, migrations, and a unique subdomain URL. Environments are completely isolated per PR with no shared state, spin up in minutes, and are automatically destroyed when the PR is closed or merged. Production releases follow the same pipeline on merge to master, using Helm atomic upgrades with zero-downtime rolling updates.
0
73

Multi-Arch Docker Pipeline — GitHub Actions · GHCR
CI/CD pipeline building multi-architecture Docker images (linux/amd64 + linux/arm64) via GitHub Actions and CircleCI. Uses Docker Buildx with QEMU emulation, multi-stage Dockerfiles for minimal production images, and automatic tagging by commit SHA, branch, and latest. Images are published to GitHub Container Registry (GHCR) with a multi-arch manifest. Deployments use Helm with atomic upgrades and automatic rollback, targeting both ephemeral preview environments and production EKS clusters.
0
69

Cloud Infrastructure — AWS, EKS & CI/CD Pipeline
Architecture diagram representing the infrastructure stack I design and manage for clients. Covers a full CI/CD pipeline (GitHub Actions → Docker multi-arch build → Helm deploy), an Amazon EKS cluster with production-hardened pods (HPA, PodDisruptionBudgets, NetworkPolicies), supporting AWS services (RDS, S3, IAM), and observability via Prometheus and OpenTelemetry.
0
95

Production Helm Chart — Kubernetes Deployment
A production-grade Helm chart managing a multi-component application on Kubernetes. Includes separate server and worker deployments, HPA and PodDisruptionBudgets for resilience, NetworkPolicies for pod-level traffic control, a pre-deploy migration job, ingress with TLS, and a PostgreSQL dependency. Structured with separate values files for local dev and production environments.
0
68

Unlocking insights with AI and Data Science
Unlocking insights with AI and Data Science


Helping SaaS teams finish security questionnaires with evide


Full Stack Web & Mobile Developer




Penetration Tester - OSCP 🛡️



Sovereign AI Custody & Temporal Workflow Governance

Autonomous agents are dangerous without a custody layer. The Iron Wolf Advisor dock and OMNI Terminal allow for controlled, human-gated intake of new tasks. No workflow starts without explicit operator authority, and every intent is funnelled through a strict Service Gateway with non-bypass able decision manifests.
0
69

This portfolio visual is a case-study cover created to summarise a real evidence-backed website and SEO baseline audit delivered to a client.
The underlying deliverable included forensic capture, technical findings, performance evidence, and integrity reporting.
1
131

Regulated sectors need to know exactly what an AI agent did and why it was authorized. This Evidence Vault displays a fully orchestrated proof chain - from browser snapshot to data transformation to client report - each step hash-verified and cryptographically linked. It provides the immutable audit trail that CISOs and regulators demand.
0
116

This is not a reporting tool. This is a read-only command center that provides real-time observability over a multi-department AI pipeline. It manages worker health, intake queues, and runtime control, ensuring that every AI agent action is governed by human-gated approvals and append-only audit ledgers.
0
135