
AI Automation Expert | n8n · Make.com · Zapier · OpenAI | 10
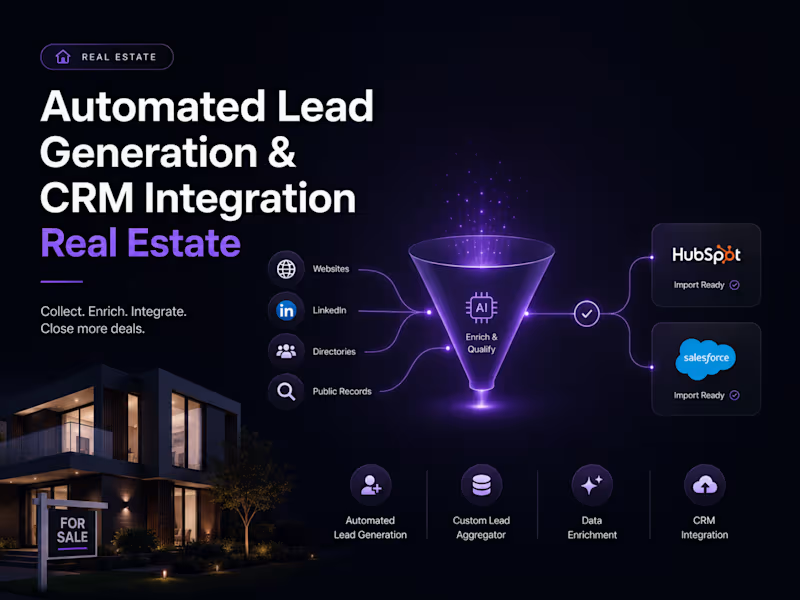
A real estate business needed an efficient system to collect, enrich, and manage high-quality sales leads from public sources — reducing manual work and enabling seamless CRM integration. We built a targeted lead collection and enrichment system, extracting publicly available data, enhancing each lead with company name, role, and industry details, and preparing everything for direct import into HubSpot and Salesforce.
✅ Industry-specific lead collection using keywords and demographics
✅ Lead enrichment with company name, role, and industry data
✅ HubSpot & Salesforce ready CSV export
✅ Scalable, repeatable lead pipeline
Result: Client significantly improved productivity, cut manual lead tasks, and scaled outreach with organized, enriched data ready for immediate use.
0
203

A brand needed to analyze competitor Instagram performance, identify content trends, and refine their marketing strategy — without manual tracking. We built a semi-automated competitor analysis system using a custom scraper, Google Sheets dashboard, and AI-assisted insights — delivering weekly automated reports with actionable strategy recommendations.
✅ Competitor engagement tracking and content analysis
✅ AI-assisted insights on high-performing content
✅ Real-time Google Sheets dashboard
✅ Weekly automated performance reports
✅ Fully policy-compliant public data sourcing
Result: Client gained clear competitor visibility, improved content strategy, and identified new audience engagement opportunities.
Skills & Tools: Web Scraping, Python, Social Media Marketing, Data Extraction, Instagram, Google Sheets, Automation
0
187

An eCommerce brand needed to streamline and scale their Shopify product listings — eliminating manual uploads and ensuring SEO-friendly, high-converting entries across their entire catalog. We built a custom Shopify scraper and automation system that extracted product details, enriched listings with keyword-optimized content, added branded image overlays, and delivered bulk import-ready CSVs.
✅ Automated product data extraction and enrichment
✅ SEO-optimized titles and descriptions
✅ Branded logo overlays on product images
✅ Bulk import-ready CSV & direct Shopify uploads
✅ Clean, uniform formatting across all listings
Result: Transformed a manual product catalog into a scalable, high-converting, hands-free sales engine.
0
198

A brand needed a streamlined DM campaign system for personalized outreach and lead generation — without violating platform policies or using spammy automation. We built a lightweight, platform-compliant DM outreach system with custom messaging templates, audience targeting using hashtags and keywords, and a semi-automated workflow maintaining a genuine human touch.
✅ Hashtag & keyword-based audience targeting
✅ Personalized messaging templates aligned with brand tone
✅ Semi-automated workflow — human touch maintained
✅ Platform-compliant outreach strategy
Result: Improved response rates, consistent outreach performance, and significant time savings — leading to stronger connections and better conversions.
0
185


Web, API and Android Penetration Tester
Comprehensive validation testing, proof-of-concept verification, and structural remediation audits to ensure complete security patch efficacy.
The Objective:
A development organization required a rigorous follow-up assessment to validate that security patches introduced after an initial audit were correctly implemented, completely neutralized the identified threat vectors, and did not introduce new regression flaws into the environment.
The Approach:
I executed a dedicated verification cycle focused specifically on replicating the original attack patterns using the exact tools and exploits from the initial assessment. Every patch was manually tested using Burp Suite Professional, custom Python exploit scripts, and runtime debuggers to confirm the vulnerability's status and measure remediation success against standard CVSS 3.1 metrics.
From a dedicated retesting scope targeting 20 original security findings, I delivered the following lifecycle results:
Closed (Remediated): Successfully verified the resolution of 16 findings, including all critical business logic bypasses and sensitive data exposure pathways, confirming they are no longer exploitable.
Bypassed (Incomplete Fixes): Identified 2 instances where a development team used client-side input validation instead of server-side sanitization, allowing the original exploit to still bypass the patch.
New Regression: Discovered 2 minor configuration errors introduced by changes made to the access control framework during the patching process.
Documentation Provided: Delivered updated Proof-of-Concept (PoC) logs and step-by-step documentation for the outstanding issues to guide the team to a permanent fix.
0
105
Comprehensive external/internal network penetration test, cloud infrastructure review, and vulnerability assessment for a production hosting ecosystem.
The Objective:
A production hosting provider required a full-scope security audit to evaluate their perimeter defense, verify compliance with the CIS Benchmarks and OWASP Top 10 for Cloud, and uncover critical misconfigurations before public deployment.
The Approach:
I executed a hybrid security assessment combining automated infrastructure reconnaissance with deep manual configuration checks. Every vulnerability was manually validated using tools like Nmap, Wireshark, and CloudBrute to eliminate false positives and scored using standard CVSS 3.1 metrics.
From a single comprehensive audit, I uncovered 31 reproducible findings:
3 High Severity: Exposed database backups publicly accessible via misconfigured AWS S3 buckets, and unauthenticated remote code execution (RCE) vectors on perimeter network appliances.
6 Medium Severity: Overly permissive IAM policies granting excessive root privileges, missing multi-factor authentication (MFA) enforcement on management panels, and outdated SSH protocol versions in use.
10 Low Severity: Unrestricted directory listings on internal staging servers, insecure network daemon configurations, and loose firewall rules permitting unnecessary inbound traffic.
12 Informational: Internal IP address disclosures in HTTP response headers, missing asset tagging, and verbose system version banners.
0
99
Comprehensive web application penetration test, API endpoint analysis, and vulnerability assessment for a production-facing infrastructure ecosystem.
The Objective:
An enterprise client required a full-scope security assessment to evaluate their external attack surface, verify strict alignment with the OWASP Application Security Verification Standard (ASVS Level 3), and uncover critical server-side and business logic flaws before deploying a major code release.
The Approach:
I executed a hybrid security assessment combining automated reconnaissance with deep manual exploitation across the application layer and its integrated APIs. Every vulnerability was manually validated using Burp Suite Professional, SQLmap, and Postman to eliminate false positives and scored using standard CVSS 3.1 metrics.
From a single comprehensive audit, I uncovered 24 reproducible findings:
2 High Severity: Broken Object Level Authorization (BOLA/IDOR) on critical billing endpoints and a SQL injection flaw in the primary authentication pathway.
5 Medium Severity: Faulty session management allowing session fixation, missing Rate Limiting on public API routes, and Cross-Site Scripting (XSS) via un-sanitized comment inputs.
7 Low Severity: Lax CORS configuration rules, missing secure flag attributes on cookies, and verbose server error disclosures.
10 Informational: Exposure of outdated software banners and missing HTTP security headers (such as Content-Security-Policy).
0
123
Comprehensive Android application penetration test, reverse engineering analysis, and vulnerability assessment for a production-ready mobile application.
The Objective:
A mobile application provider required a full-scope security audit to evaluate their client-side attack surface, verify compliance with the OWASP Mobile Application Security Verification Standard (MASVS Level 2), and uncover critical runtime flaws before public deployment.
The Approach:
I executed a hybrid security assessment combining static application security testing (SAST), dynamic instrumentation (DAST), and automated reconnaissance. Every vulnerability was manually validated using tools like Frida, Objection, Jadx-GUI, and Burp Suite to eliminate false positives and scored using standard CVSS 3.1 metrics.
From a single comprehensive audit, I uncovered 19 reproducible findings:
1 High Severity: Insecure local data storage exposing unencrypted user credentials and private API keys in the shared preferences file.
4 Medium Severity: Broken cryptography implementations, insufficient SSL pinning mechanisms permitting Man-in-the-Middle (MitM) attacks, and unprotected exported Activities allowing unauthorized internal intents.
6 Low Severity: Lack of root detection, weak code obfuscation rules, and excessive logging of sensitive debug information via Logcat.
8 Informational: Outdated third-party SDK dependencies and missing compiler exploit mitigation configurations.
0
110

Turning ideas into simple, useful web experiences
Turning ideas into simple, useful web experiences


Expert in Spring Boot & React.js Dev Solutions
Expert in Spring Boot & React.js Dev Solutions


View more →

Backend Developer | Python, Django & PostgreSQL

I developed a Restaurant Billing System using Python, Tkinter, SQLite, and PIL (Pillow). The application features menu management, bill generation, GST calculation, order management, and invoice printing through an intuitive desktop GUI. It is designed to simplify restaurant billing with a fast, user-friendly, and efficient interface.
0
75

I develop modern, secure, and scalable College ERP Systems using Python, Django, Django REST Framework, PostgreSQL, HTML, CSS, Bootstrap, JavaScript, Docker, Nginx, Gunicorn, Git, and Render. My expertise includes student information management, attendance tracking, academic records, role-based authentication, faculty and admin dashboards, course management, notifications, and responsive user interfaces. I build reliable, production-ready ERP solutions that streamline administrative workflows and improve efficiency for educational institutions.
0
58

I develop modern, secure, and scalable e-commerce websites using Python, Django, PostgreSQL, HTML, CSS, Bootstrap, and JavaScript. My expertise includes product catalogs, shopping carts, secure authentication, payment gateway integration, order and inventory management, and responsive user interfaces. I also integrate third-party services such as Cloudinary for media storage and deploy applications using Docker, Nginx, Gunicorn, and Render to deliver fast, reliable, and production-ready e-commerce solutions.
0
57

Built a real-time chat application using Django Channels, Redis, and WebSockets for instant messaging and live communication. Integrated Cloudinary for secure cloud-based media uploads and PostgreSQL for reliable data management. Designed a responsive, user-friendly interface with secure authentication and real-time updates.
Tech Stack: Python, Django, Django Channels, Redis, WebSockets, PostgreSQL, JavaScript, HTML, CSS, Bootstrap, Cloudinary.
0
99

Expert in C++ and Computer Vision 💡



Python backend developer | APIs & tools
Python backend developer | APIs & tools


