Dimorvan Fernandes
Python Developer | Data Protection & Security Tools


🚀 Built a Multi-Touch Attribution Engine & Dashboard
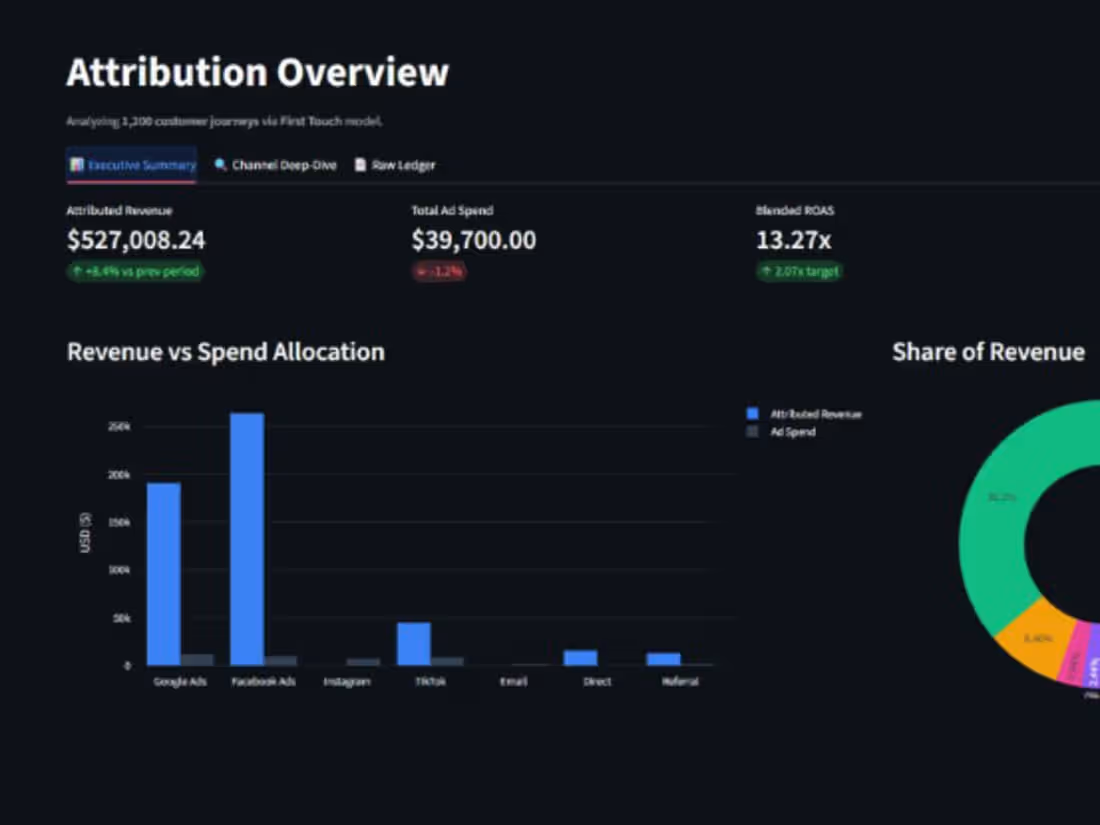
Measuring marketing impact across multi-touch customer journeys is a tough data challenge. I built Vectra Analytics to solve this—a platform that models cross-channel performance using statistical attribution models.
Tech Stack:
Frontend: Streamlit (dark mode UI)
Processing & Viz: Python, Pandas, NumPy, Plotly
Database: SQLAlchemy Async (aiosqlite)
Data Quality: Pydantic v2 validation
Core Features:
Flexible Attribution Models: Switch instantly between First/Last Touch, Linear, Time Decay, and Markov Chains.
Core Metrics: Tracks Attributed Revenue, Spend, Net Profit, and ROAS.
Executive Decision Matrix: Scatter plots mapping Spend vs. Revenue vs. ROAS for fast insights.
#Python (https://www.linkedin.com/search/results/all/?keywords=%23python) | #DataEngineering (https://www.linkedin.com/search/results/all/?keywords=%23dataengineering) | #Streamlit (https://www.linkedin.com/search/results/all/?keywords=%23streamlit) | #Analytics (https://www.linkedin.com/search/results/all/?keywords=%23analytics) | #SoftwareEngineering (https://www.linkedin.com/search/results/all/?keywords=%23softwareengineering) | #DataScience (https://www.linkedin.com/search/results/all/?keywords=%23datascience) | #GrowthAnalytics (https://www.linkedin.com/search/results/all/?keywords=%23growthanalytics)
0
52
Security in motion and at rest — built in Python 🛡️
I built Sec-Toolkit, a two-layer security tool designed to keep data
safe everywhere it goes:
🔹In-Transit:
Verifies request signatures, validates user tokens, and checks web
security headers.
🔹At-Rest:
Encrypts sensitive files using AES and creates SHA-256 fingerprints
to ensure nothing has been tampered with.
It also includes automated checks using local AI, built with a clean
terminal interface for a smooth developer experience.
#Python (https://www.linkedin.com/search/results/all/?keywords=%23python&origin=HASH_TAG_FROM_FEED) | #CyberSecurity (https://www.linkedin.com/search/results/all/?keywords=%23cybersecurity&origin=HASH_TAG_FROM_FEED) | #Coding
(https://www.linkedin.com/search/results/all/?keywords=%23coding&origin=HASH_TAG_FROM_FEED)| #SoftwareEngineering (https://www.linkedin.com/search/results/all/?keywords=%23softwareengineering&origin=HASH_TAG_FROM_FEED) | #DataProtection (https://www.linkedin.com/search/results/all/?keywords=%23dataprotection&origin=HASH_TAG_FROM_FEED) |#AppSec (https://www.linkedin.com/search/results/all/?keywords=%23appsec&origin=HASH_TAG_FROM_FEED) | #DevTools (https://www.linkedin.com/search/results/all/?keywords=%23devtools&origin=HASH_TAG_FROM_FEED)
1
186
I developed a Python CLI focused on applied cryptography (Applied Cryptography Toolkit v0.2.0).
Demonstration of the security pipeline in action:
° File encryption and decryption using AES-256-GCM
° Preservation of original file integrity
° State validation via SHA-256 Hash verification
The project's focus is to ensure a simple, fast, and secure workflow for data manipulation via the command line.
#Python | #Cybersecurity | #Cryptography | #AES256 | #CLI | #SoftwareEngineering | #PythonProgramming | #InfoSec | #Dev | #Freelance
0
84
Built a CLI Python tool (sanitizer.py (http://sanitizer.py)) to sanitize sensitive data in logs and datasets before storage or analytics pipelines.
Highlights:
° Speed: Processed 82k+ lines (~10MB) in 2.2s in masking mode (~37k lines/sec).
° Security: Native Fernet encryption using Python’s cryptography library with auto key generation.
° Flexibility: Easily switch between field masking and full encryption.
Fast PII protection without slowing down processing pipelines.
#Python #DataProtection #Cybersecurity #Cryptography #DevOps
0
82