The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

AI Code Security Analysis Platform. Agentic security analysis with graph-based system modeling and runtime validation (Playwright, OWASP ZAP) for fewer false positives. In active development.

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Related posts

Multi-Model Social Media Agent — Automated Content Workflows
Built by QuantEve Technologies | AI Automation & Full-Stack Engineering
Designed and developed an AI-powered social media workflow that streamlines content research, drafting, evaluation, approval, publishing, and performance analysis.
Rather than relying on a single model for every task, the system uses a multi-model workflow to organize content operations into manageable stages, with persistent state and human review where needed.
Core Capabilities
Content Research: Organizes topics and research inputs into a structured content workflow.
AI-Assisted Drafting: Generates social media content for platforms such as X and LinkedIn.
Multi-Model Processing: Supports model-provider alternatives and fallback handling for more resilient workflows.
Draft Evaluation: Adds an evaluation stage to review and improve content before it moves forward.
Human Approval: Keeps content review separate from publishing so drafts can be checked before external actions.
Workflow Persistence: Uses SQLite-backed queues and stored state to track content as it moves through the system.
Performance Feedback: Organizes publishing analytics and feedback to inform future content decisions.
Engineering Focus
The system brings AI model orchestration, application logic, persistent workflow state, and social media operations together in one maintainable automation pipeline.
Technology Stack
Python / Node.js (depending on the deployed component) · LLM APIs · REST APIs · SQLite · Workflow Automation · Social Platform Integrations
Built by QuantEve Technologies to demonstrate how AI can automate repetitive content operations while keeping the workflow organized, reviewable, and controllable.


Would you run a command without knowing what it could do?
A copied installation script. An automated workflow. A shell command suggested by AI.
Convenient? Yes. Worth checking before execution? Absolutely.
That’s why I built SafeShell, an open-source tool for inspecting commands, applying security policies, and running permitted commands with sandboxing on Linux.
The goal: help developers and engineering teams work faster with more control over what they execute.
Explore the code, try it, and share your feedback:
https://github.com/HamzaGhebriche/SafeShell
Building automation or CI/CD workflows that need stronger security controls? I’m available for freelance projects in DevSecOps, secure automation, and cloud security. Let’s talk through Contra.




Resolve: an AI support agent that answers from a company’s own policies, looks up orders, and escalates weak matches to a human instead of guessing. A human approves replies before they go out.
Live demo: support-resolver.vercel.app


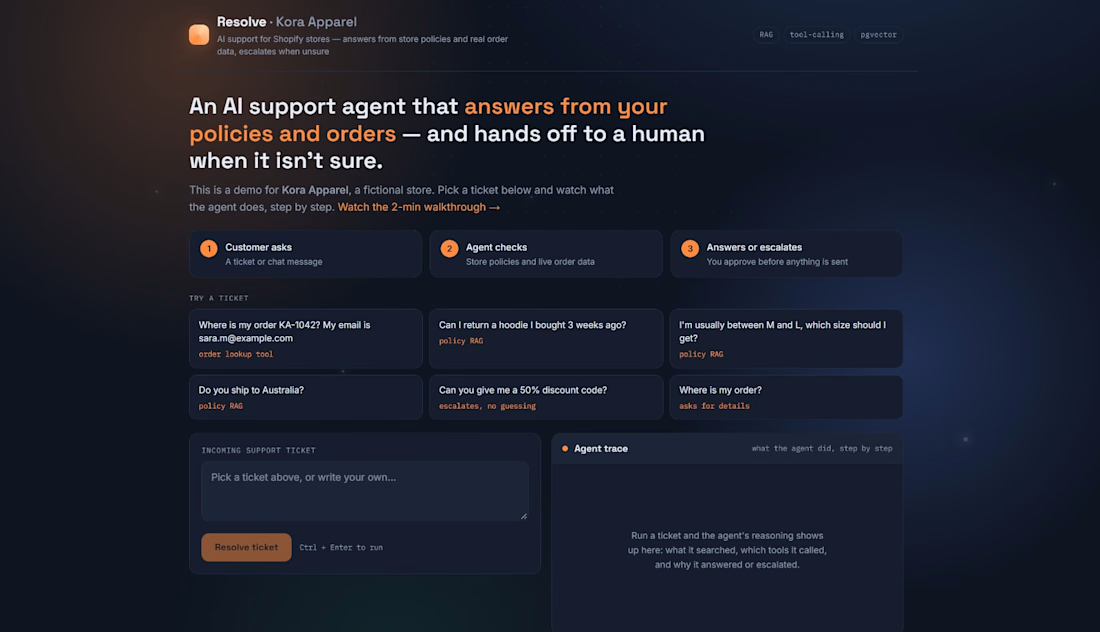

For the human approval step, I'd show the exact policy passage and its effective date beside the draft. Does Resolve flag a reply for re-review if the policy changes while it waits for approval?