The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

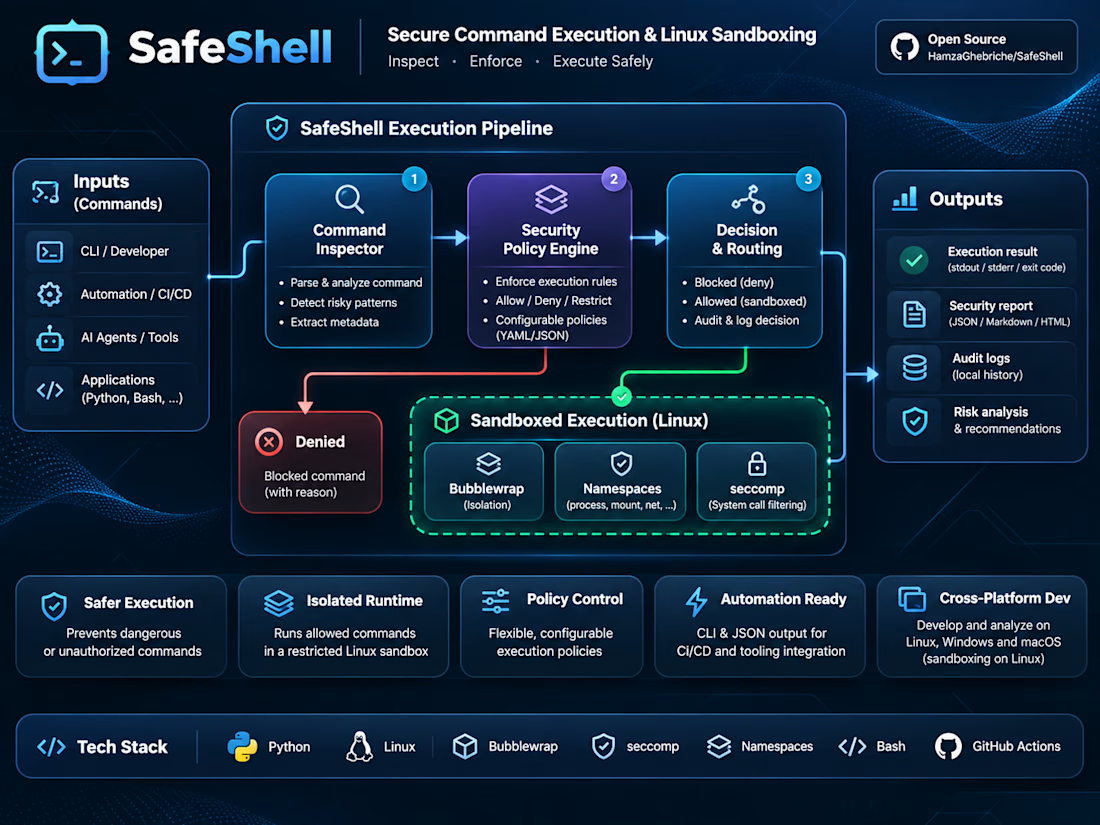
SafeShell is an open-source Python security tool I developed to inspect potentially dangerous shell commands, enforce execution policies, and run permitted commands within a restricted Linux sandbox.
The project focuses on improving command execution safety in development environments, automation workflows, and security-sensitive applications.
🔐 Key Features
1. Command Security Analysis
Inspects shell commands before execution.
Identifies potentially dangerous command patterns.
Generates structured findings and risk information.
Supports deterministic command analysis without executing the submitted command.
2. Secure Linux Sandboxing
Uses Bubblewrap and Linux security controls to restrict command execution.
Implements Linux namespaces and seccomp-based restrictions.
Reduces access to host resources through controlled filesystem and runtime configurations.
Refuses protected execution when required security mechanisms are unavailable.
3. Security Policies & Access Control
Enforces configurable offline execution policies.
Supports explicit authorization for permitted operations.
Prevents approvals from overriding hard security restrictions.
Provides structured execution decisions and status information.
4. Security Automation & Auditing
Offers a Python command-line interface.
Supports JSON output for integration with automation workflows.
Records local execution metadata for review.
Provides timeout and output-size controls.
5. Cross-Platform Development
Supports command inspection and policy management on Linux, Windows, and macOS.
Provides protected execution on supported Linux environments.
Includes automated validation through CI pipelines.
Technologies: Python, Linux, Bubblewrap, seccomp, Linux Namespaces, Bash, GitHub Actions, JSON, Security Automation.
My Role: Independent Developer & Security Engineer.
Project Type: Open-source security tool.
Current Status: Experimental alpha release (v0.1.0-alpha).
SafeShell has undergone automated testing but has not received an independent security audit. It is not intended to serve as a production-grade security boundary.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Related posts

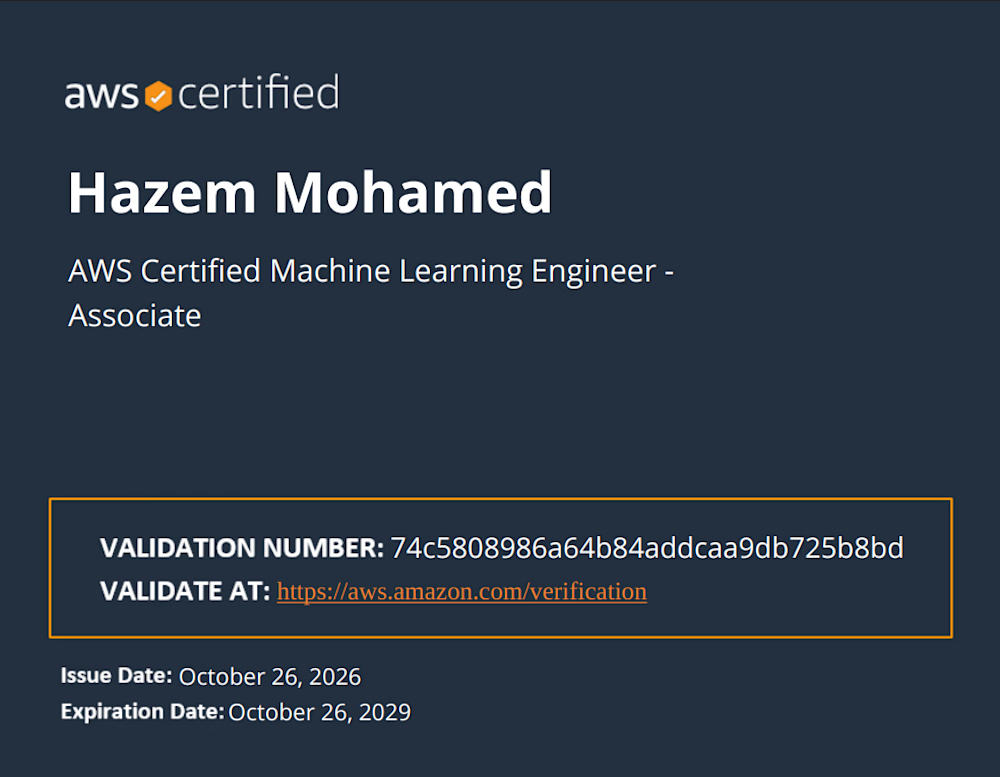
Proud to officially add the AWS Certified Machine Learning Engineer - Associate certification to my toolkit!
Building robust machine learning pipelines and scaling AI workloads securely on the cloud has always been a key focus of mine. Earning this certification has been a great deep-dive into mastering AWS ML infrastructure, MLOps best practices, and production-grade architectures.
Ready to bring these advanced capabilities to upcoming data science and engineering projects! Let's build something impactful. 💡💪
🔗 Verify Certificate:
Validation Number: 74c5808986a64b84addcaa9db725b8bd
Verification Link: https://aws.amazon.com/verification
#AWS #MachineLearning #AI #CloudComputing #DataAnalysis #MLOps


Congratulations on earning the AWS Machine Learning Engineer certification, Hazem khaled! Robust pipelines and cloud automation make all the difference for production-grade AI systems.

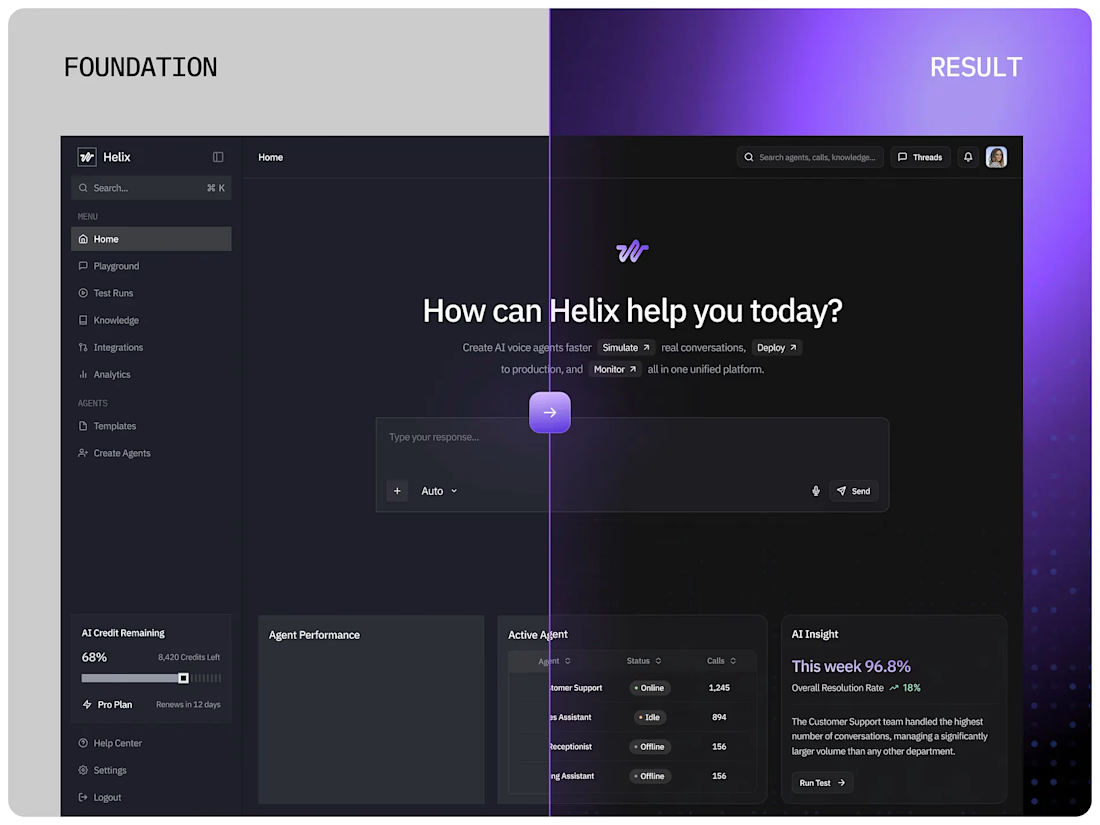
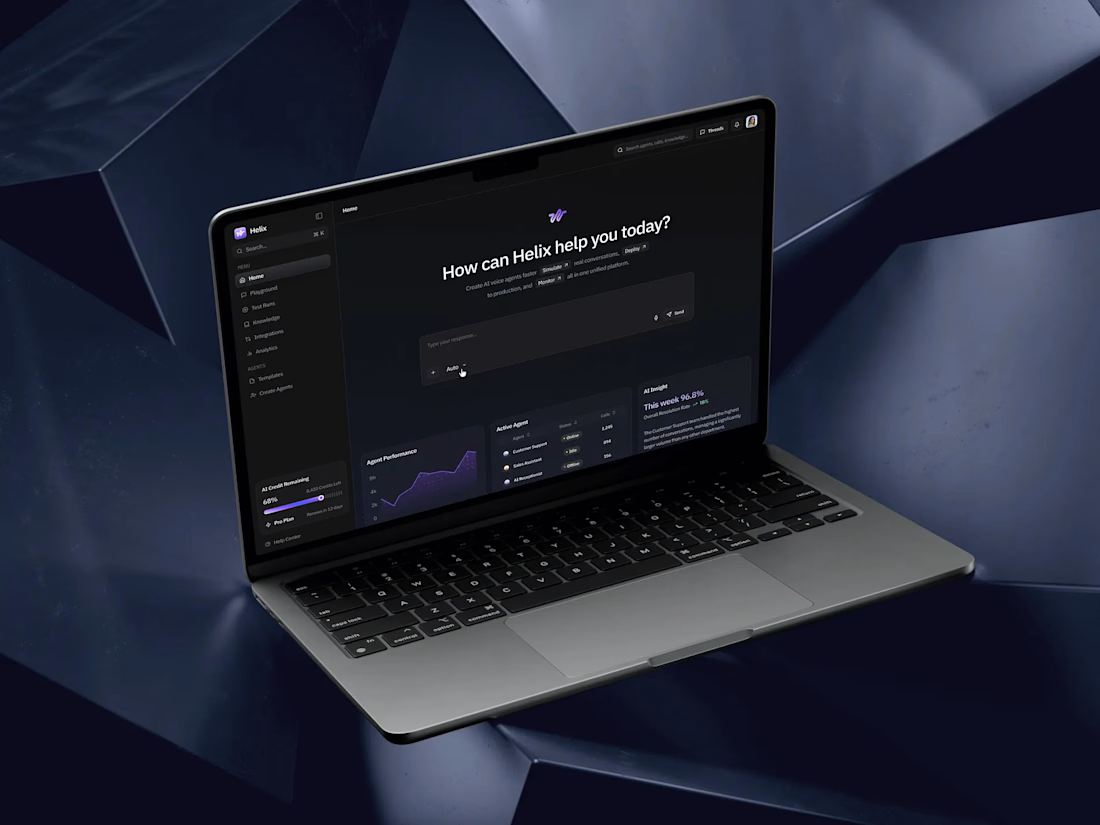
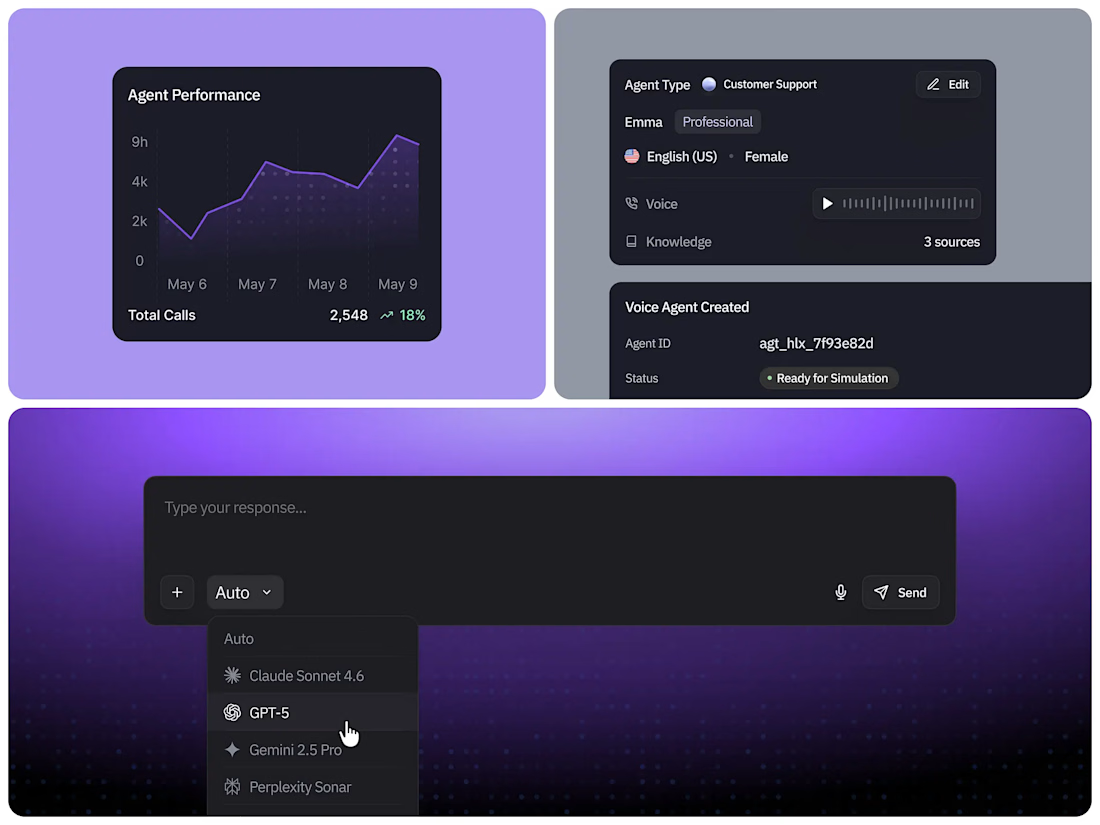
Helix — an all-in-one console to accelerate enterprise voice-agent deployment. I shaped the foundational experience and responsive web application: a smart multi-model prompt bar to attach documentation, switch between leading LLMs and inspect live synthesis previews, plus a dark-canvas dashboard with real-time call volume analytics, agent availability monitors and third-party CRM integration readiness.

Helix: Fast-tracking conversational AI with an intuitive workspace to build, simulate, and deploy autonomous voice agents.
I shaped the foundational experience and responsive web application for Helix, an all-in-one console built to accelerate enterprise voice-agent deployment....

The attention to detail here is fantastic.