The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

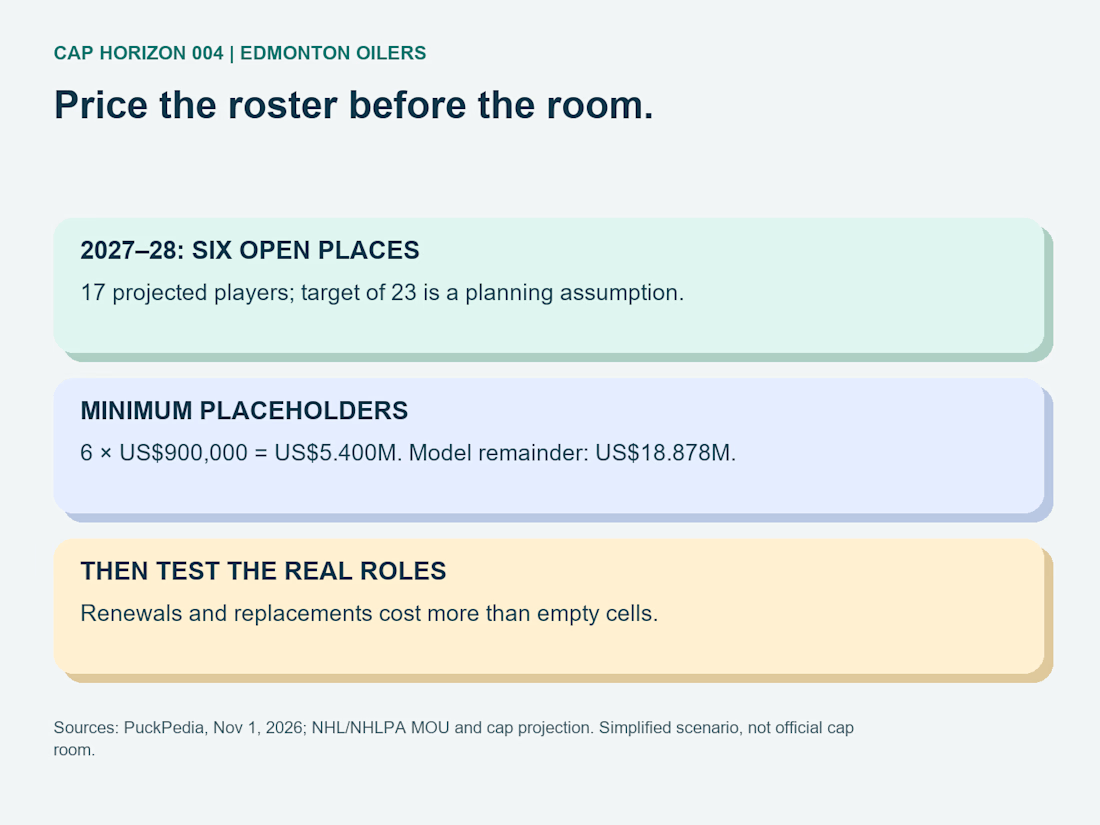
Cap Horizon — self-directed sports research and data visualization.
Original Edmonton Oilers analysis published November 1, 2026. It reconciles dated public cap estimates with official contract announcements and NHL/NHLPA rules across four seasons.
Current, projected and deadline cap space are kept distinct. Roster-floor and replacement-cost scenarios are labeled instead of treating an incomplete future roster as spendable room. The article includes transparent calculations, linked sources and an original raised-card visual.
AI-assisted research and writing with source, arithmetic and layout checks. This is self-published editorial work, not a client commission or an official NHL cap calculation. Figures and projections are dated in the article.

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started



Related posts

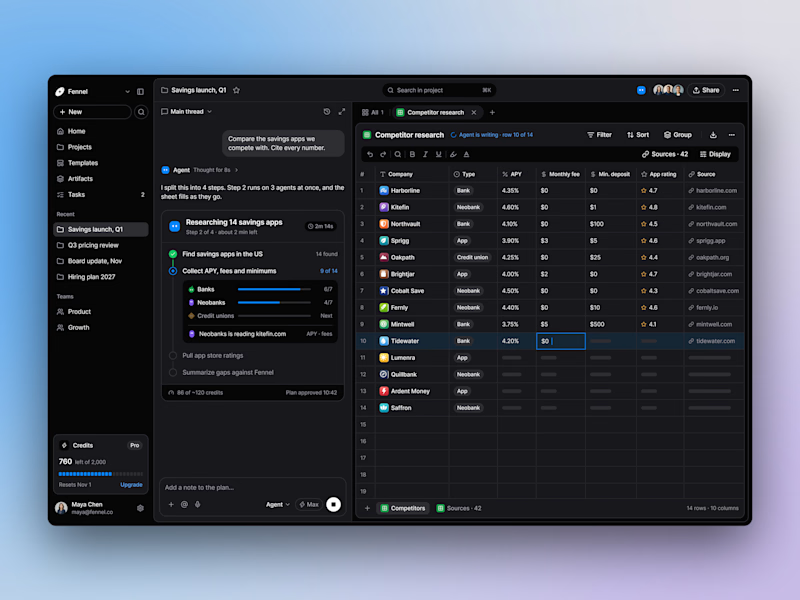
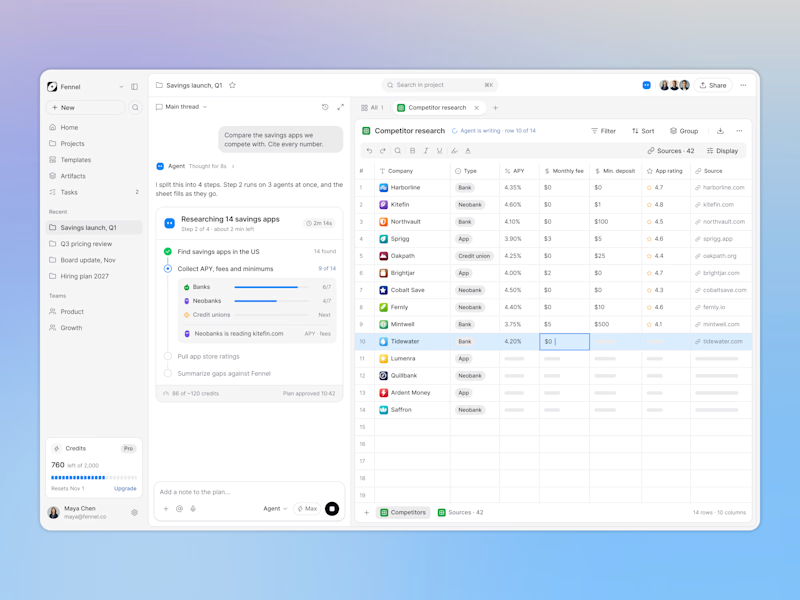
Designed an AI research workspace where the agent plans the work and fills a sheet with cited sources as it goes.
Same screen, two modes. Which one would you work in all day? 👀


13 voted
72%
5 voted
28%
18 votes
Closed

Keeping the research plan and cited results side by side is a useful way to make the agent’s work easier to inspect. I’d lean toward light mode for reading the table in daylight. How do you distinguish a verified source from one that still needs review?

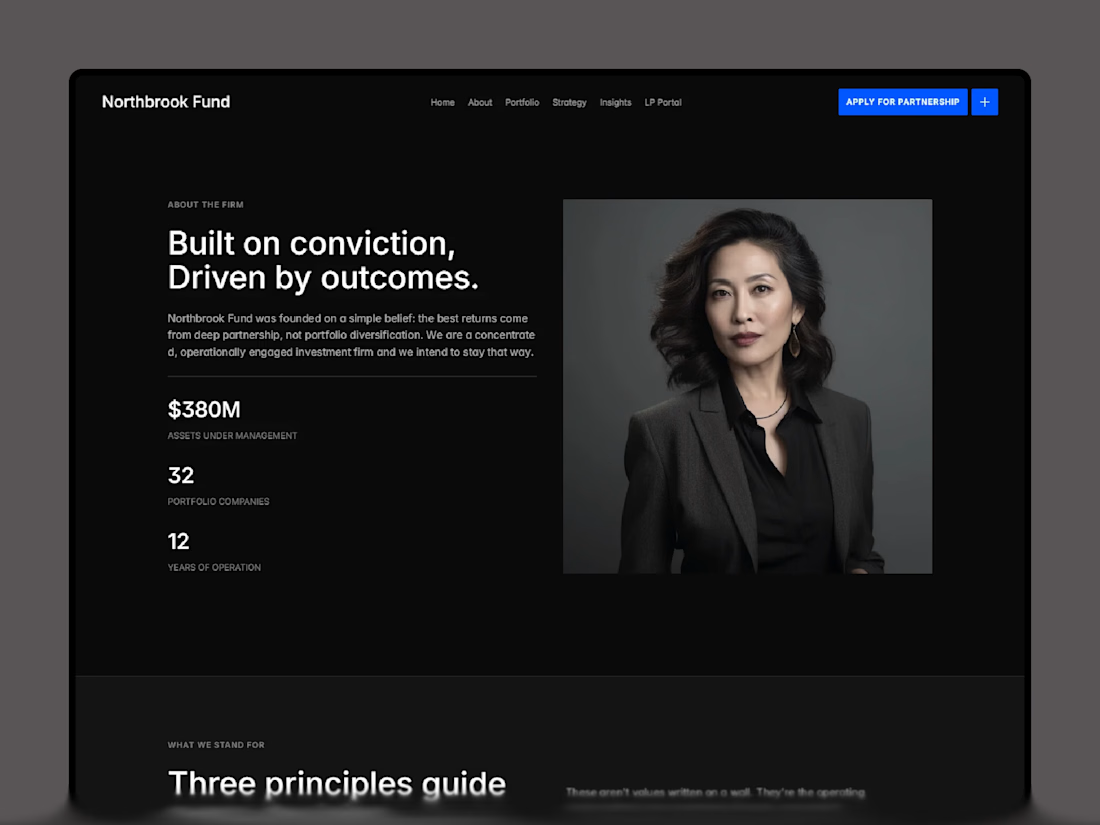
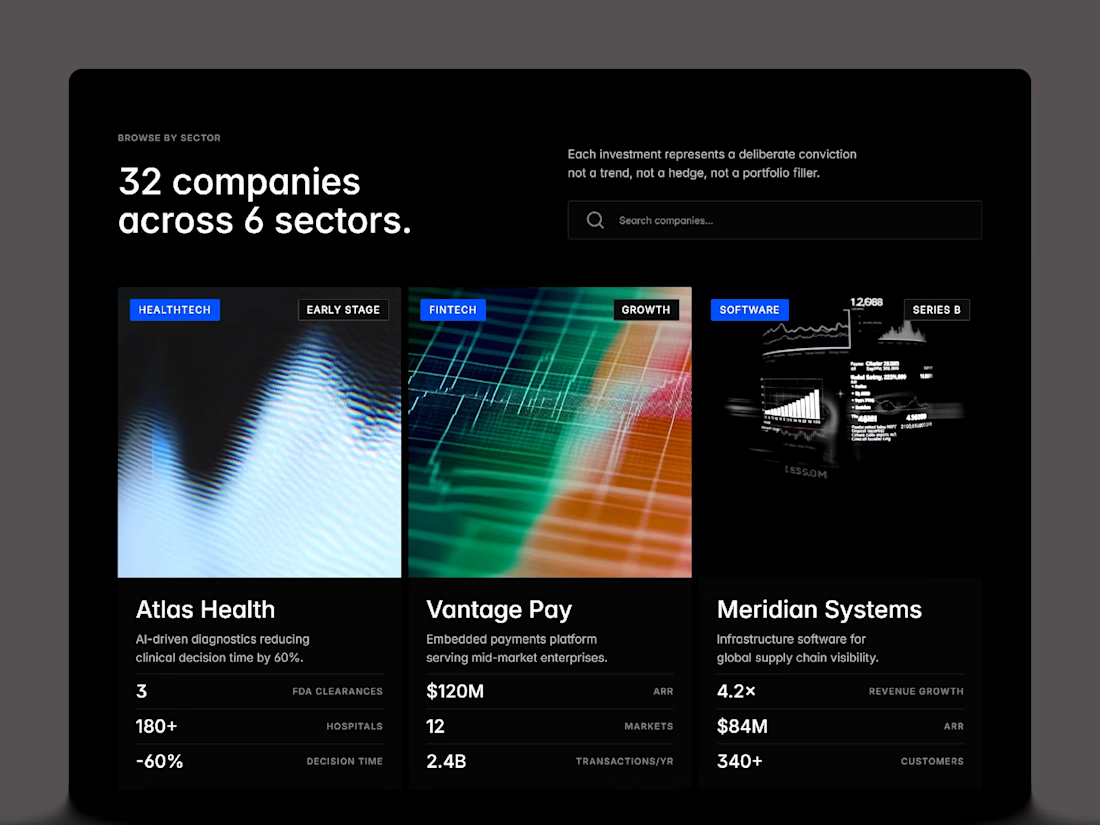
Investment firms don't all need the same website.
Tenet Capital is now free. A flexible starting point for investment managers.
Northbrook is premium. Built around how VC and PE firms present their thesis, portfolio, and team.
Two different directions, both built in Framer.
Here's a look at both ↓


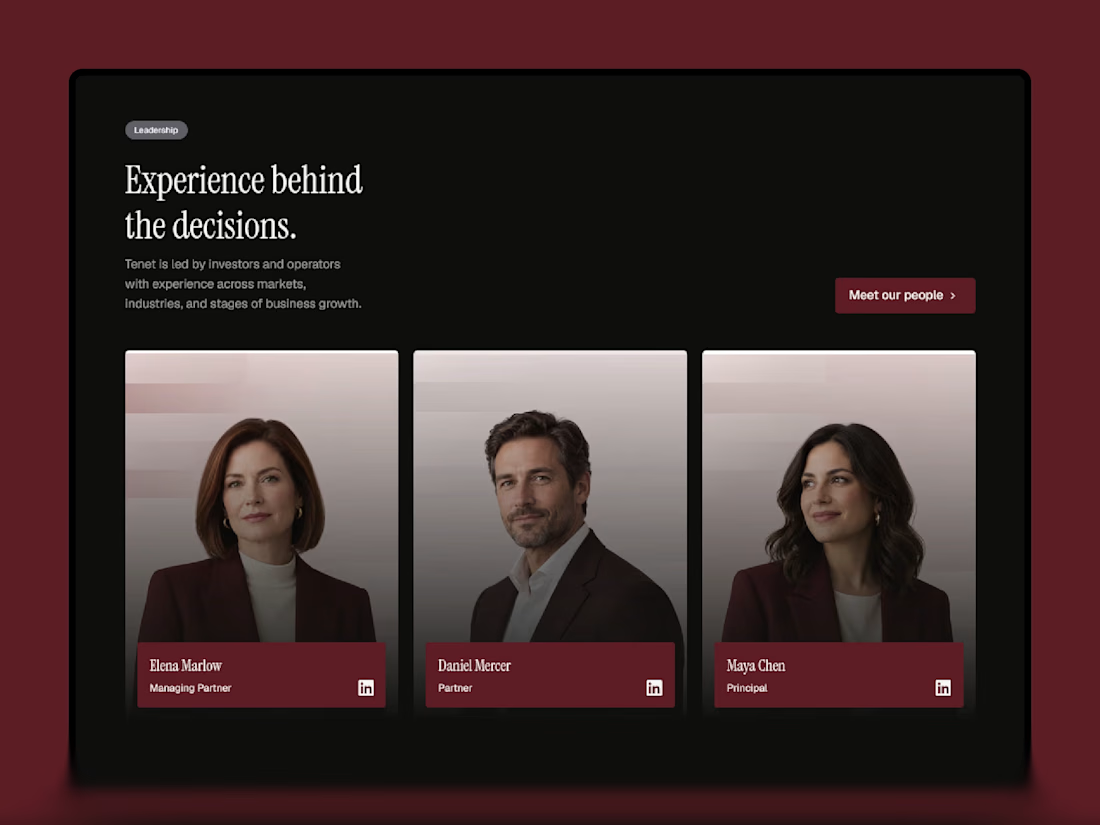
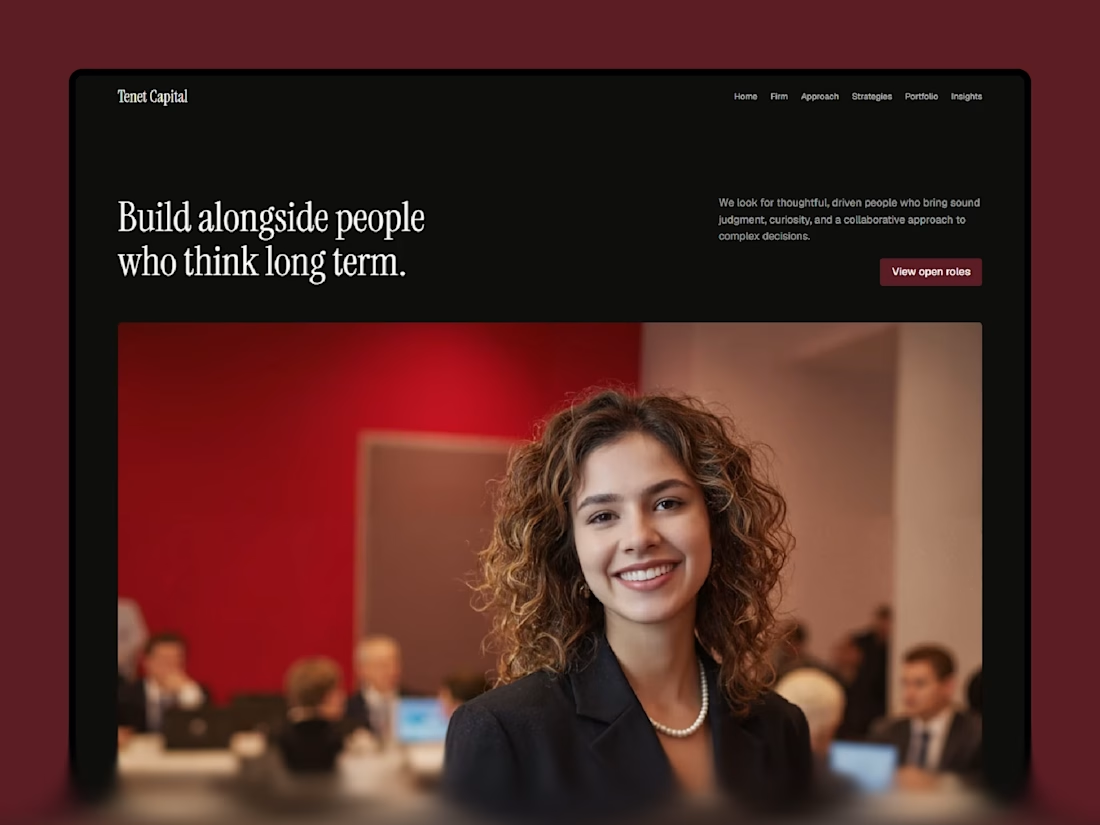

Burgundy looks rich here.

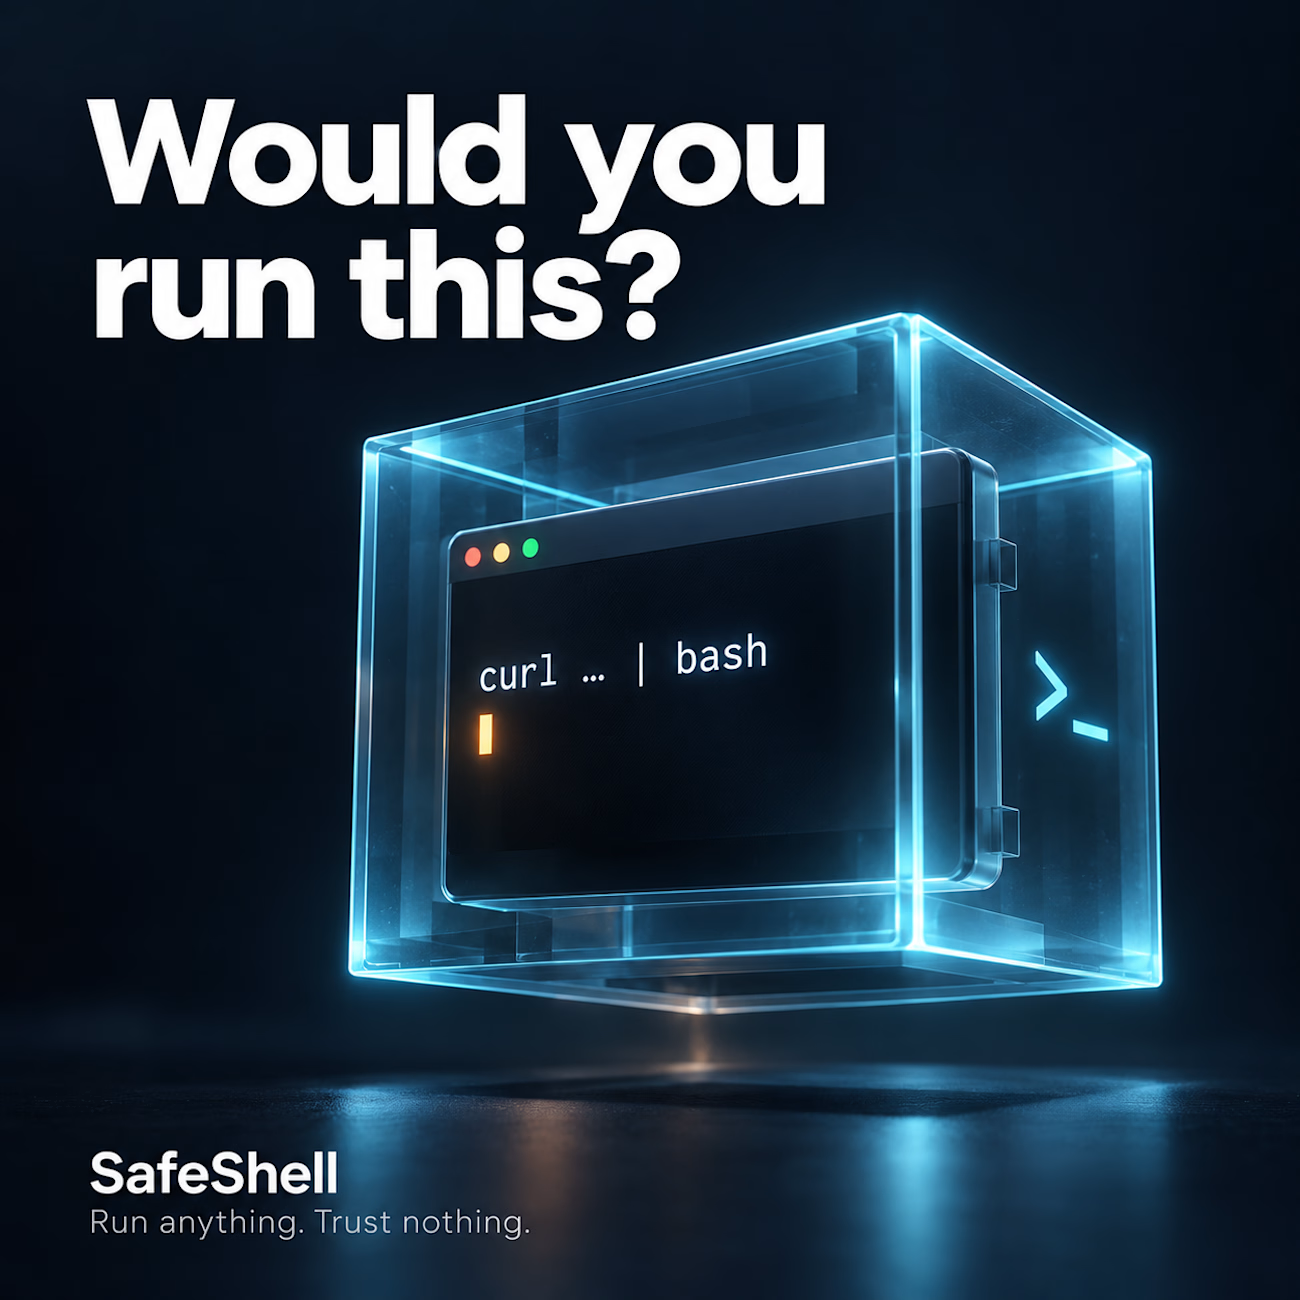
Would you run a command without knowing what it could do?
A copied installation script. An automated workflow. A shell command suggested by AI.
Convenient? Yes. Worth checking before execution? Absolutely.
That’s why I built SafeShell, an open-source tool for inspecting commands, applying security policies, and running permitted commands with sandboxing on Linux.
The goal: help developers and engineering teams work faster with more control over what they execute.
Explore the code, try it, and share your feedback:
https://github.com/HamzaGhebriche/SafeShell
Building automation or CI/CD workflows that need stronger security controls? I’m available for freelance projects in DevSecOps, secure automation, and cloud security. Let’s talk through Contra.