The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Related posts

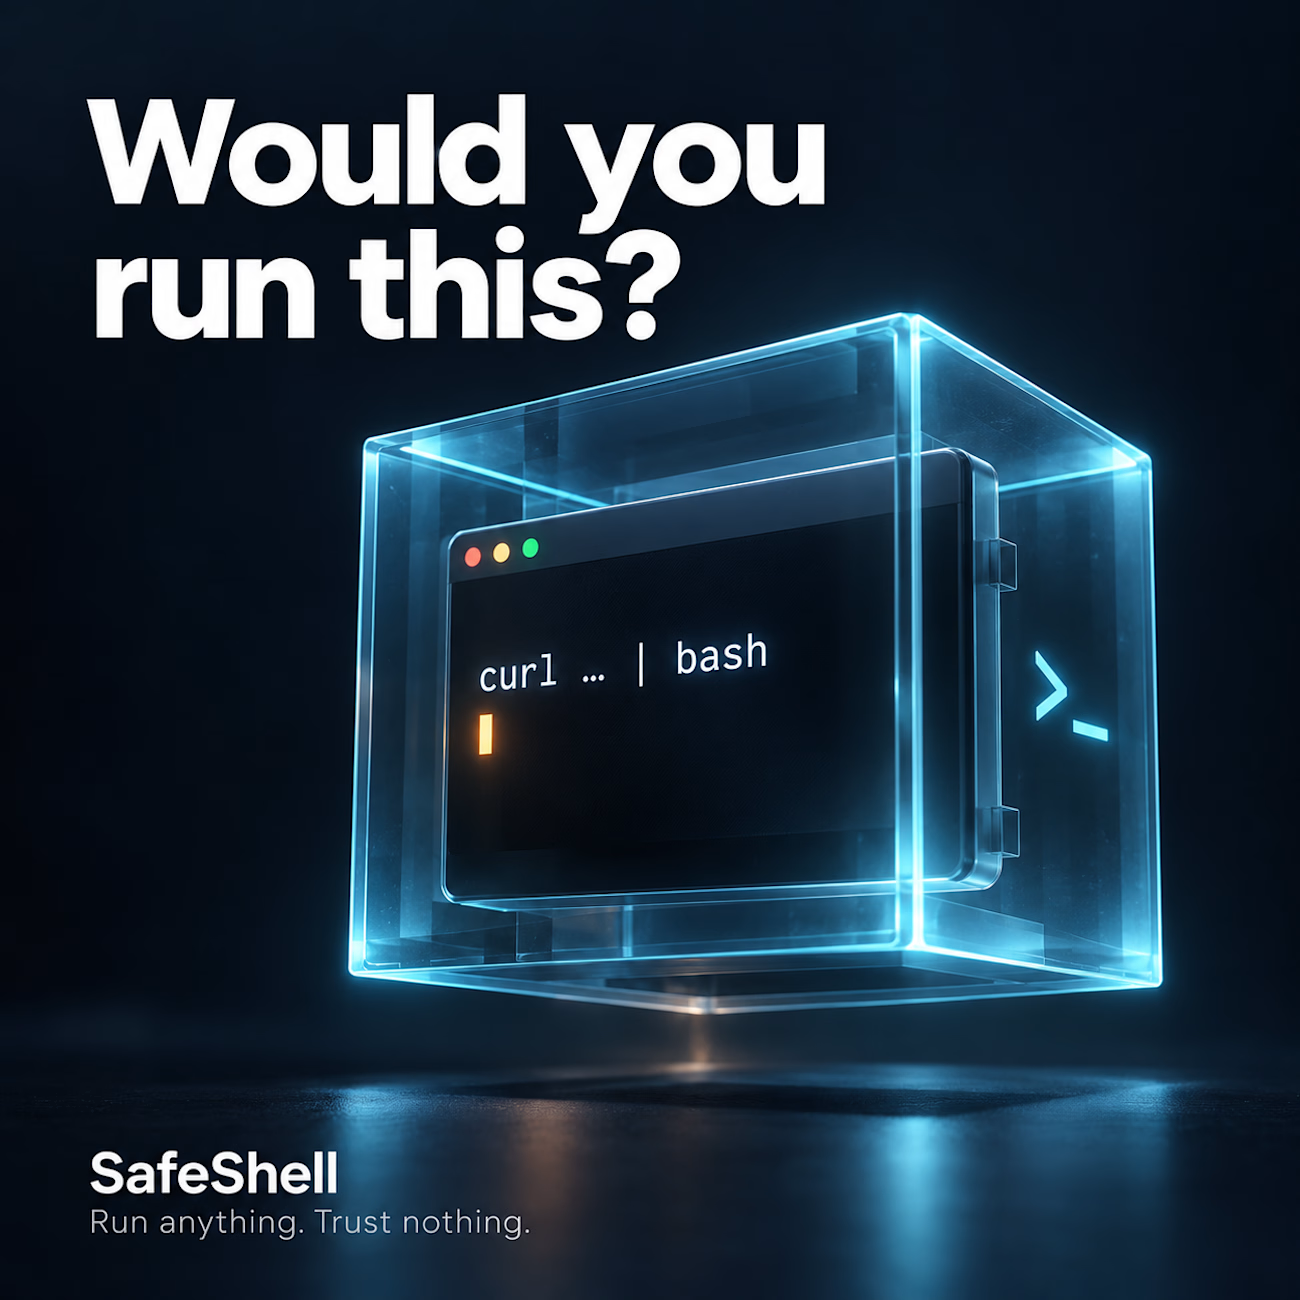
Would you run a command without knowing what it could do?
A copied installation script. An automated workflow. A shell command suggested by AI.
Convenient? Yes. Worth checking before execution? Absolutely.
That’s why I built SafeShell, an open-source tool for inspecting commands, applying security policies, and running permitted commands with sandboxing on Linux.
The goal: help developers and engineering teams work faster with more control over what they execute.
Explore the code, try it, and share your feedback:
https://github.com/HamzaGhebriche/SafeShell
Building automation or CI/CD workflows that need stronger security controls? I’m available for freelance projects in DevSecOps, secure automation, and cloud security. Let’s talk through Contra.




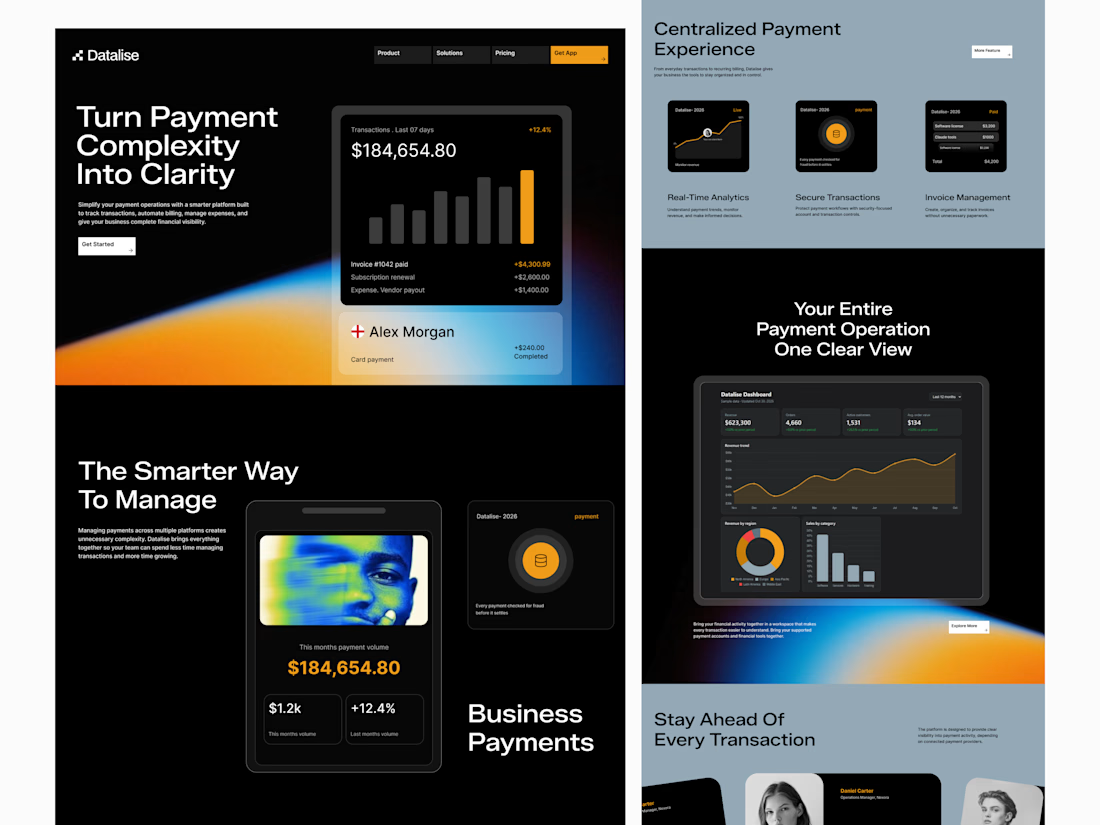
Datalise- Fintech payment Website Landing page
A modern payment management platform
The goal was to create a digital experience that makes complex financial workflows feel simple, clear, and effortless.
The Problem
Managing business payments across multiple platforms often creates unnecessary complexity. Businesses struggle with scattered transaction records, limited financial visibility, disconnected payment tools, and time-consuming invoice management.
Without a centralized system, tracking financial activity and making informed decisions becomes harder than it should be.
The Solution
Datalise brings essential payment operations into one unified experience. By combining real-time analytics, secure transaction monitoring, and simplified invoice management, the platform helps businesses stay organized and in control.
What's inside:
> Centralized payment management
> Real-time financial analytics
> Secure transaction monitoring
> Smart invoice management
> An intuitive business dashboard
> Built around a bold visual identity, clean layouts, and a data-focused interface that puts clarity first.
Have a payment platform that needs a better digital experience? Let's build something exceptional.