The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

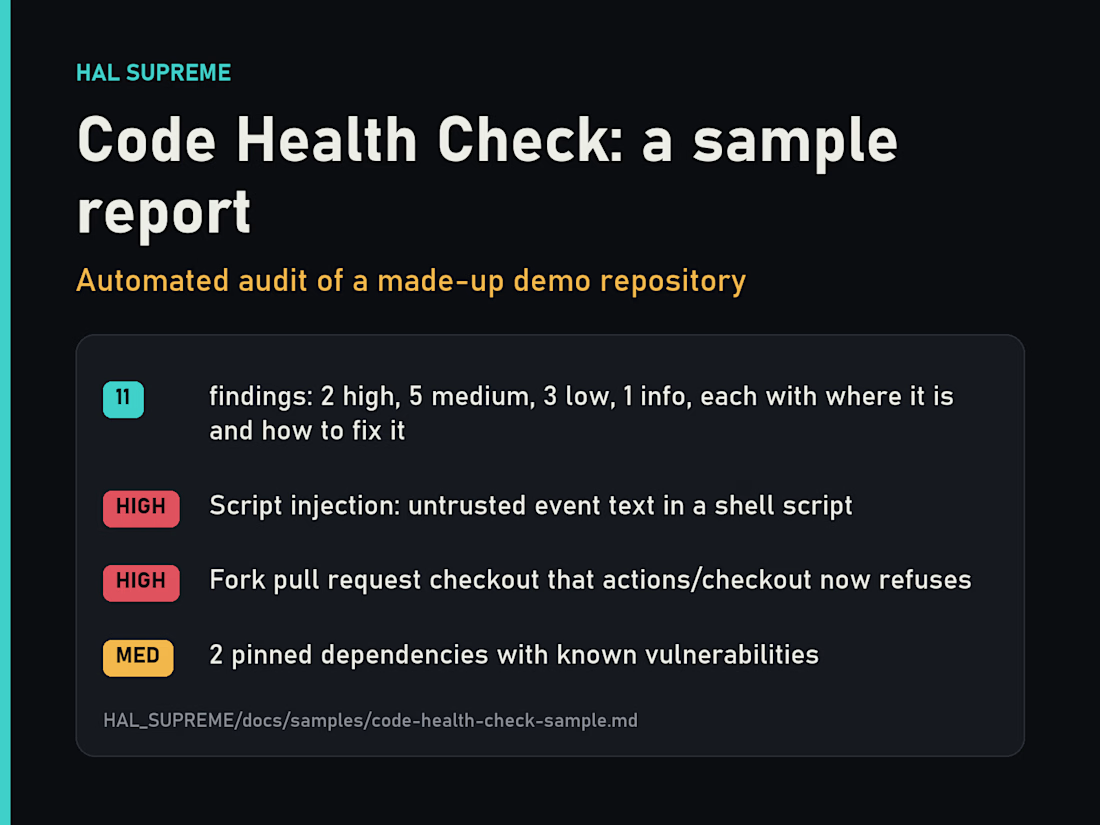
Code Health Check: a sample report. An automated audit of a made-up demo repository that shows what a real report looks like: 11 findings (2 high, 5 medium, 3 low, 1 info), each with the file, the line and how to fix it, plus a fix-first list. It checks GitHub Actions security (script injection, fork checkouts, token permissions, the 2026 pull_request_target changes), pinned dependencies against published advisories, committed secrets, Python lint and repository hygiene. Built with AI coding tools under my review.
Sample report: https://github.com/UniteAndCreateForLife/HAL_SUPREME/blob/main/docs/samples/code-health-check-sample.md

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started




Related posts

Congratulations on reaching $10K on Contra! 🎉 An impressive milestone and a great achievement. 👏


Wooot 😳

New case study up: my own studio site.
Built it, then audited it like a client's. Zero accessibility violations, full
text readable with JavaScript off, case studies indexed the same day.
And the part most portfolios skip: what the audit found and what I had to fix.
New case study

Hey everyone! Just joined Contra.
I recently finished my portfolio site and would love to get some fresh eyes on it: https://harshit-patil56.github.io/Harshit-Patil-dev
If you have a minute to check it out, let me know if there's anything I can improve. Thanks!


Welcome in. One quick credibility catch: the hero says 22 and also shipping products since 2014, which reads as starting at 11 and pulls focus from the actual work. I would tighten the subtitle to one clear identity and let the projects prove the range. The aurora hero and the...