The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

I discovered a SQL injection vulnerability in a practice web application that allowed me to bypass the login system and access the entire user database without any credentials. By inserting a simple payload into the username field, I successfully logged in as the first user in the database and extracted sensitive information including usernames, password hashes, and user email addresses. This finding was documented in a detailed report with proof-of-concept screenshots, risk analysis showing potential data breach impact, and step-by-step remediation guidance including parameterized queries and input validation. This assessment demonstrates my ability to find critical database vulnerabilities that could expose thousands of customer records.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started

Challenges
View all


Related posts

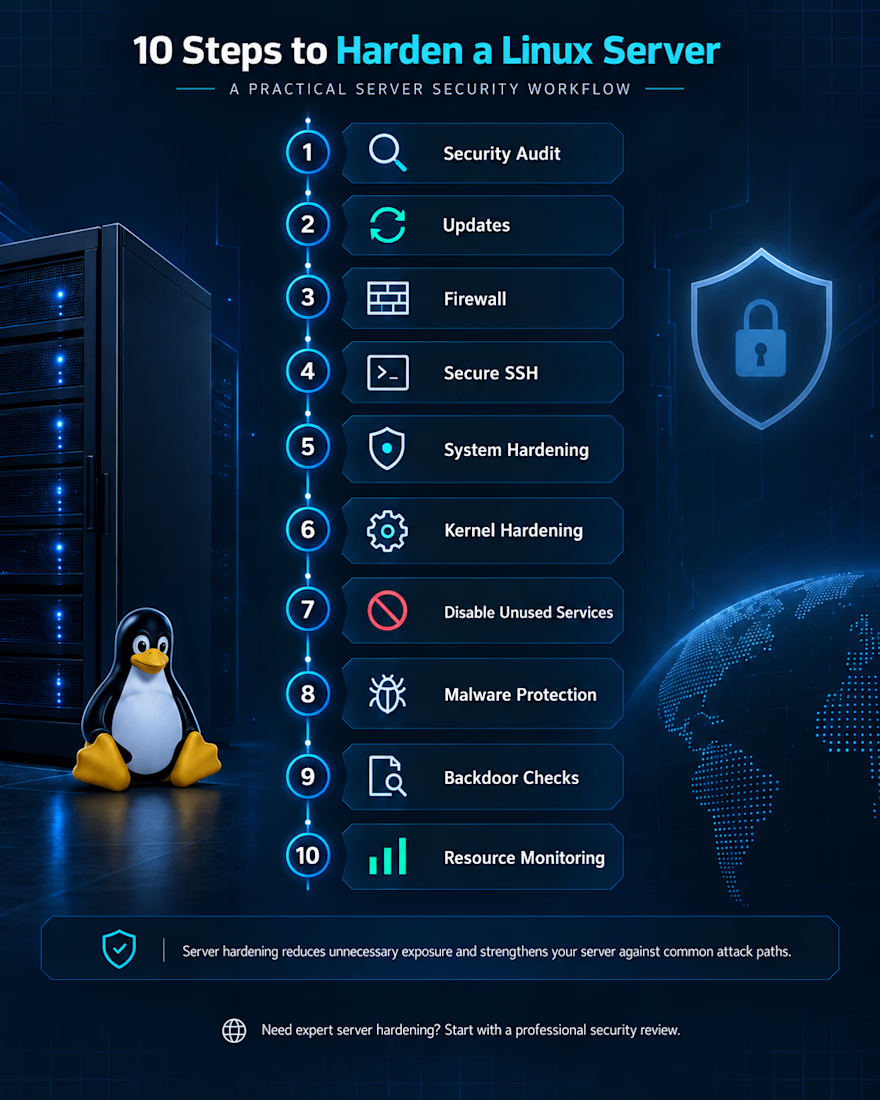
10 Essential Steps to Harden a Linux Server
Server security goes far beyond simply installing an operating system and setting a password.
A properly hardened Linux server reduces unnecessary exposure and makes common attack paths more difficult to exploit.
The process usually starts with a security audit, system updates, and reviewing open ports.
Firewall rules and secure SSH configuration help control who can access the server.
Unused services should be disabled, while system and kernel settings need to be reviewed carefully.
Regular malware and backdoor checks add another important layer of protection.
Continuous resource and activity monitoring can also help identify unusual behavior early.
A strong hardening process creates a much safer foundation for websites, applications, and business infrastructure.
Learn more about server hardening at https://serverly.host/other-services/server-hardening/
#ServerHardening #LinuxSecurity #ServerSecurity #CyberSecurity #LinuxServer #CloudSecurity #SysAdmin


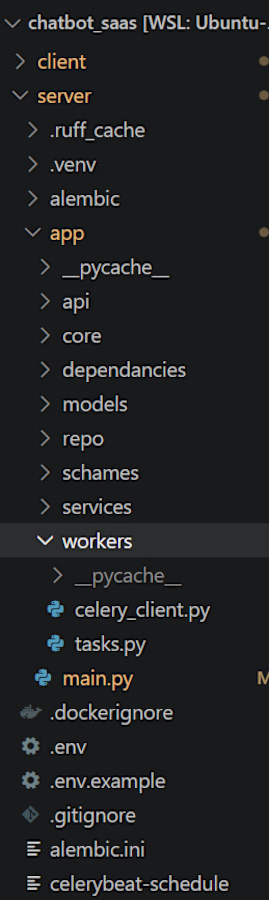
A Server Template that includes Auth logics and endpoints and used tech FastAPI Redis Postgres SQLAlchemy Alembic Docker and also it has Production Ready Structure.



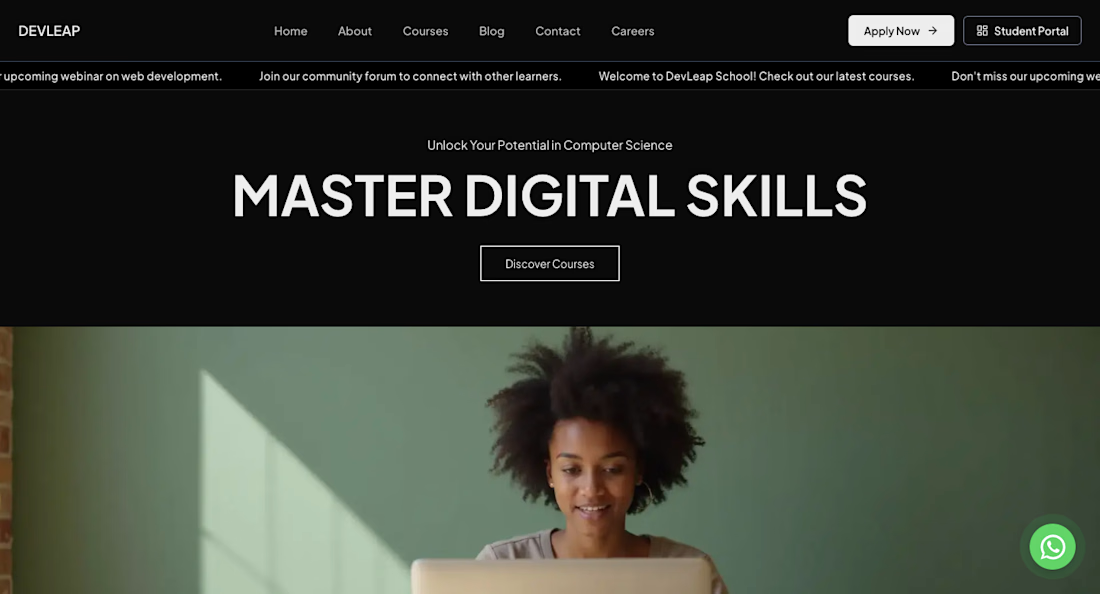
Website for my computer school, built end to end with Next.js and Postgres. Includes online enrollment, a spam-protected contact form, a student portal with secure sign-in, automated emails, and analytics.