The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Designing a Verifiable AI Agent Workflow: From Human Approval to Secure Deployment
An AI agent completing a task doesn't automatically mean the resulting artifact is safe or authorized to deploy.
I've been exploring a reference architecture that connects agent execution, artifact integrity, human approval, and deployment enforcement.
The problem
Consider an AI coding agent that:
Receives a feature request
Generates a pull request
Runs automated tests
Receives human approval
Triggers a deployment pipeline
Now consider an edge case: the release artifact changes between approval and deployment.
The conversation history may accurately show that someone approved the work, but that alone doesn't prove the deployed artifact matches what they reviewed.
Proposed architecture
1. Agent execution
The agent processes the request, implements changes, and produces test evidence.
2. Immutable artifact identification
CI creates the release artifact and calculates its cryptographic digest.
artifact_digest = SHA256(release_artifact)
3. Approval-bound authorization
The human approval record references the exact artifact digest, along with the authorized reviewer, target environment, and expiration.
4. Deployment policy enforcement
The release gate validates the signed approval, authorization scope, required test evidence, and the candidate artifact digest.
Illustrative pseudocode, not a production-ready implementation.
5. Reapproval on change
If the approved artifact is modified or rebuilt into different bytes, the digest changes and the existing approval no longer authorizes that release.
The deeper security considerations
Artifact hashing is only one layer.
A production design also needs to address:
Build provenance and trustworthy CI runners
Approval replay and revocation
Signing-key protection
Environment-specific authorization
Race conditions between verification and deployment
Auditability of agent decisions and release actions
The key architectural principle is simple:
A verifiable conversation records the decision. A deployment policy must enforce that decision against the actual release artifact.
This is an independent reference architecture concept I'm exploring at UI Trax, not a claim of a production implementation.
I'd be interested to hear how other engineers would design this boundary.
Would you place the final enforcement mechanism in CI/CD, the artifact registry, or the deployment admission controller?
#AIAgents #DevSecOps #SoftwareArchitecture #CICD #AIEngineering
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Related posts

Thinking about making a course on how I actually work with AI agents.
Not prompts.
The rules, skills and checks that make the agent build things the way my repo wants.
Would that be useful to anyone?

Yes please. The rules and checks part is what nobody teaches. Prompt tips are everywhere, repo setup isn't.

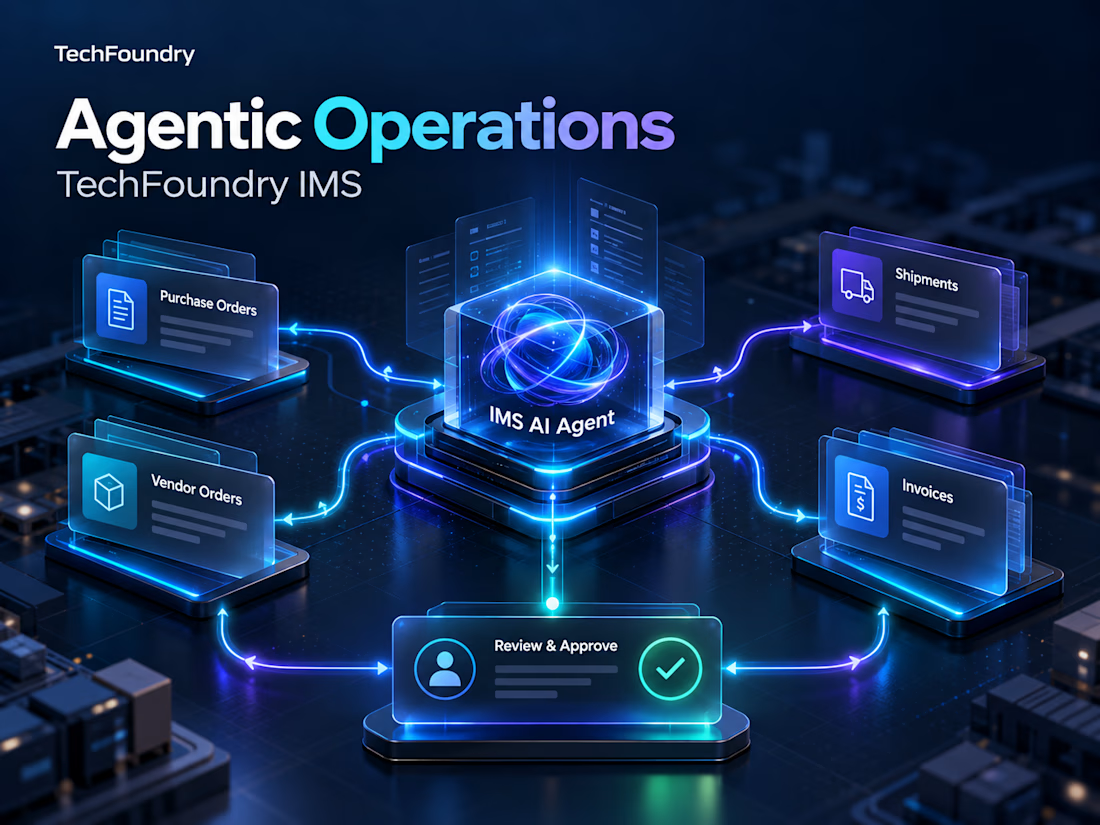
What does practical, agentic AI look like in a real business workflow?
Our new TechFoundry IMS case study walks through seven demos—from purchase-order intake and catalog conflict resolution to vendor orders, shipments, client shipping, and invoice reconciliation.
It shows how AI agents, document processing, and software integrations work together, with human review where judgment matters. I’ve also included the technology stack behind the platform.
Explore the case study:
https://contra.com/p/oWU3ssF3-tech-foundry-ims-ai-procurement-and-fulfillment-in-seven-demos
Building an agentic AI solution? Book a free initial consultation with me on Contra. We’d love to work with you.
#PracticalAI #AgenticAI #Automation #SoftwareDevelopment

Purchase-order intake and catalog conflict resolution feel like the right place to start with agents, since the pain is concrete. How do you handle the cases where the agent is unsure and a human has to step in?