The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

I've been exploring how AI can make security operations faster and more effective by reducing the manual effort required during incident investigations.
In this project, I built an AI-powered Security Investigation Agent using Claude API, AWS, and n8n.
The workflow automatically:
🔹Detects high-severity findings from GuardDuty, Security Hub, CloudTrail, and CloudWatch.
🔹 Correlates logs and infrastructure events to build a complete incident timeline.
🔹 Uses Claude to analyze the security context, identify likely attack patterns, and generate an investigation summary with recommended remediation steps.
🔹 Creates Jira tickets, notifies teams via Slack, and can trigger approved automation workflows while keeping production changes under human approval.
The goal wasn't to replace security engineers—it was to eliminate repetitive investigation work so teams can focus on making decisions faster.
Projects like this are where I see AI creating the most value: augmenting DevOps and Security teams with practical, production-ready automation.
I'd love to hear how others are using AI agents in cloud operations or security engineering.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started

Challenges
View all


Related posts

Most businesses don't need more leads. They need a better system for managing the leads they already have.
I built this GoHighLevel automation system to demonstrate how leads can move from initial contact to qualification, follow-up, appointment booking, and CRM management with minimal manual work.
The automation connects key parts of the customer journey inside one streamlined system:
• GoHighLevel CRM and pipeline management
• Automated lead capture and routing
• AI Voice lead qualification
• SMS and email follow-up
• Missed-call text-back automation
• Appointment booking and reminders
• Lead nurturing and reactivation
• Twilio communication workflows
• n8n API and workflow integrations
The objective is simple: respond faster, keep every lead organized, automate repetitive follow-up, and give sales teams a clearer path from lead to booked appointment.
This project demonstrates the type of CRM automation and AI-powered workflow systems I build for businesses that want to reduce manual processes and create a more scalable sales operation.
If your business is still manually following up with leads, managing appointments, or tracking conversations across different tools, there is probably an opportunity to automate it.
GoHighLevel CRM. AI Voice. SMS Automation. Workflow Automation. n8n. Twilio API.
Built to connect the process and keep the follow-up moving.
#GoHighLevel #AIAutomation #n8n #WorkflowAutomation #CRM #BusinessAutomation #Automation #AIvoice

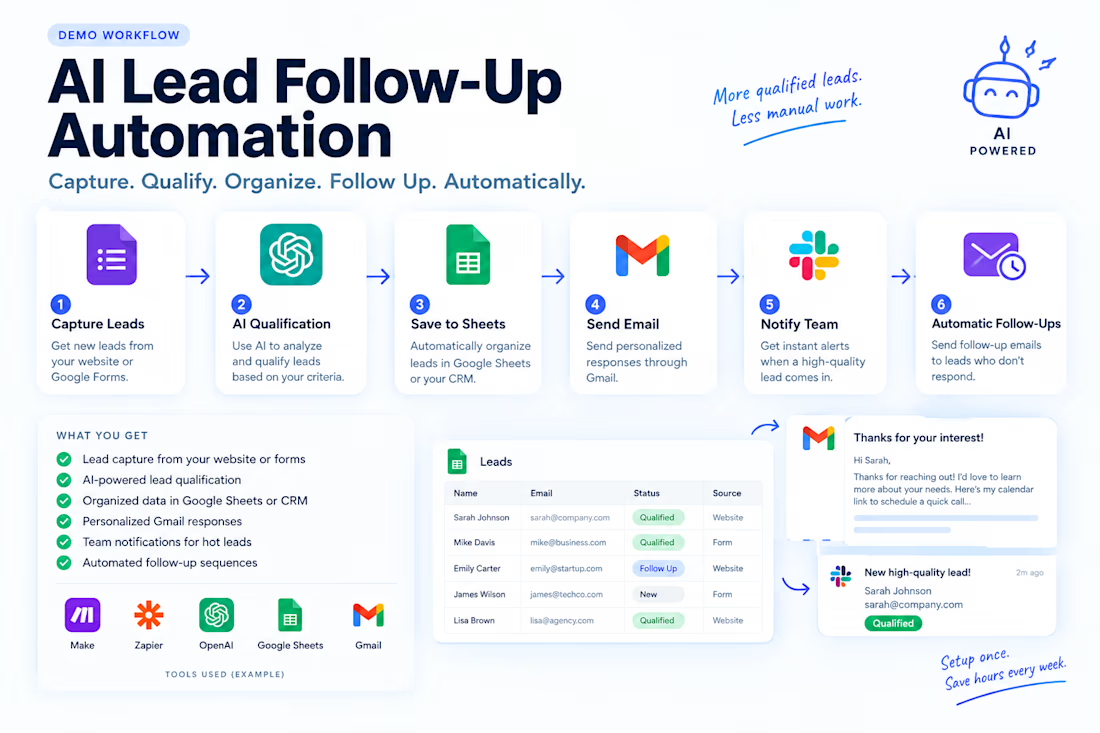
Demo AI automation workflow designed to help businesses capture, qualify, organize, and follow up with leads automatically. The workflow connects forms, AI, Google Sheets, Gmail, and team notifications to reduce manual work and improve lead response time.




👍 Here's the Material take — that marble bust recast in clear glass, catching prism light like it's about to disappear.
This is a perfect framework. For Reimagine it, you're changing the object itself. For Build the world around it, you're keeping the object and inventing everything it touches.
Which piece are you starting with? If you tell me the actual artwork, I can build you the full set — the 2125 version, the teacup skyscraper, the street outside the window, the afterlife dig.#floramuseumchallenge #SKBfloramuseumchallenge😍