The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost
Turning Healthcare Workflows into a Digital Experience
Here’s a look at E-Hospitality, a full-stack Hospital Management System I developed using React.js, Python, Django REST Framework, and PostgreSQL.
The platform brings essential hospital workflows together, including patient management, doctor scheduling, appointment booking, medical records, prescriptions, and billing.
I focused on building a responsive frontend, secure role-based authentication, reliable REST APIs, and seamless communication between the frontend and backend.
A great showcase of full-stack development, API integration, database management, and real-world business logic.
#FullStackDevelopment #ReactJS #Django #Python #RESTAPI #HospitalManagement #WebDevelopment #PostgreSQL


I modeled it with the backend as the source of truth for authorization. In Django REST, users have role-based access (Admin, Doctor, Patient), and custom permission checks are applied at the API/view level, with queryset filtering to ensure users only access the records relevant...
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started



Related posts

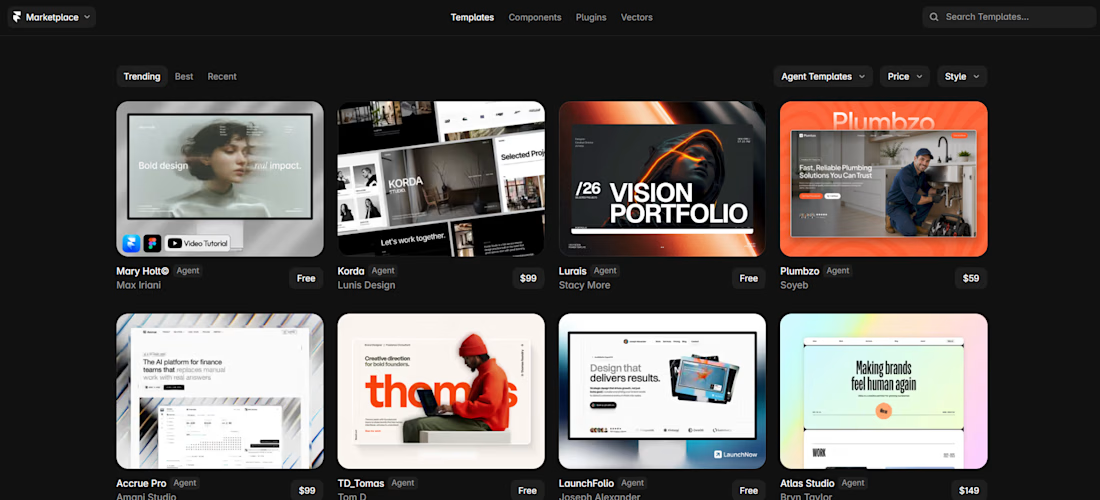
Mary Holt© is currently ranked #1 among Agent Templates on the Framer Marketplace! 🏆
For those who haven't checked out the new Agent Templates yet, they come with dedicated AI skills, a Design System page, and video tutorials to help users customize and extend the template using the Framer Agent.
Mary Holt© currently includes 4 custom skills, making it easier to build new sections, customize existing components, and keep everything consistent with the original design system.
I'm not sure how long it'll stay at #1 as more creators start converting their templates, but it's exciting to see it there!


Kajabi Website Design | Modern Coaching & Personal Brand Website
A great coaching website should do more than look professional. It should build trust, communicate your value, and make it easy for potential clients to take the next step.
This Kajabi website project focuses on clean layouts, clear messaging, intuitive navigation, and a seamless user experience designed to turn visitors into potential clients.
The goal? A professional online presence that supports brand credibility, client engagement, and business growth.
Need a Kajabi website for your coaching, consulting, or personal brand business?
I help businesses with Kajabi website design, Kajabi landing pages, website redesigns, and conversion focused sales funnels.
Open to new Kajabi projects and collaborations.


Designed a new website in Shopify for ES Beauty Lab.
The menu is built around skin concerns, so shoppers get from the homepage to the right range in one tap, and the free-shipping threshold sits in the header.
Do you organise your Shopify menu by product type or by problem solved?
esbeautylabshop.com


To your question: by problem solved. Shoppers know their skin concern before they know product names, and the close-up face circles make the choice instant. I'd add a small product type filter inside each concern page.