The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

⚡ FDA Update on Cyclospora Outbreak
The FDA has recently revised its initial findings regarding the #Cyclospora parasite, clarifying that previous results indicating a link to #TaylorFarms were false positives. Experts are diligently reviewing sample results, and the FDA, along with other health agencies, is continuing its investigation to identify the true sources of the Cyclospora outbreak.
🥬 A Note of Appreciation
I want to express my gratitude to Taylor Farms and other businesses impacted by this situation for their swift actions in removing affected products and for their cooperation with federal health agencies. As investigations proceed, it’s important for us, as the general public, to take steps to protect ourselves.
🥕 Precautionary Measures
In light of the recent developments, here are some foods you might want to avoid for now:
Salad greens
Cilantro
Basil
Green Onions
Snow Peas
Here are some ways you can prevent the spread of Cyclospora in your household:
Wash your hands with soap and hot water before and after handling produce.
Wash and scrub all fresh fruits and vegetables with clean, running water.
Remove the outer layer of leaves or skin if possible. Run the inner leaves under running water.
Cut or peel off damaged areas of produce before eating.
Here are a couple of recommended sources to continue to stay informed during this time:
🥬Check out the Taylor Farms recall page: https://www.taylorfarms.com/recall/
🥬 Read the full article by Bowdeya Tweh on WSJ:
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started








Related posts

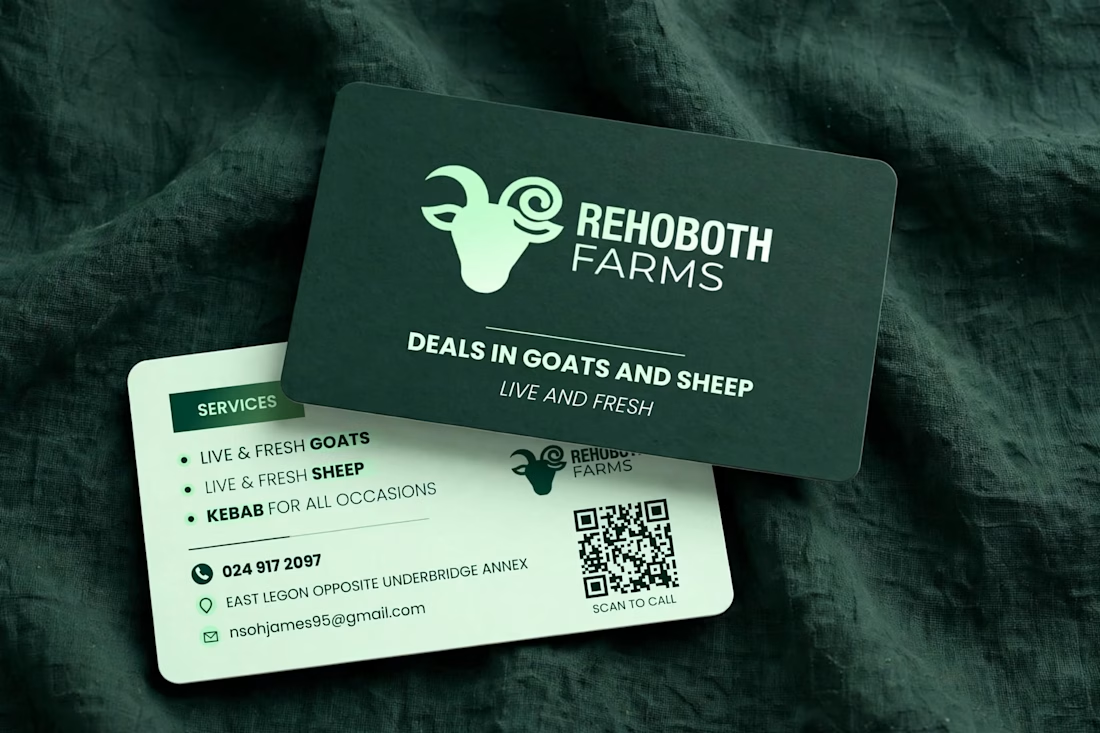
Rehoboth Farms — From Flyer to Business Card | Brand Identity
Rebranded Rehoboth Farms (Live & Fresh) from flyer to premium business card.
Dark green + mint palette, Poppins font, custom goat mark, and a working Scan-to-Call QR that dials 024 917 2097 directly.
Clean, farm-fresh, print-ready
Tools: Photoshop, Illustrator

Is your PHP server one bad request away from a takeover? 🚨
The UK's NCSC just flagged two critical PHP bugs (CVE-2026-109618 and CVE-2026-109619). An out-of-memory condition can corrupt memory and, under certain conditions, let an attacker run code on your server without logging in. Every version of PHP is affected, not just old ones.
My quick checklist:
✅ Find every PHP install, internet-facing ones first
✅ Update to the latest fixed PHP release
✅ Check bundled apps and appliances that ship PHP
✅ Can't patch yet? Apply the PHP team's temporary mitigations or take the system offline
Laravel and PHP folks: have you patched yet, or is there that one legacy box nobody wants to touch? 👇
Source: https://www.ncsc.gov.uk/news/critical-security-issue-affecting-php


Invenio — Logistics & Inventory Management Ecosystem 🚚✨
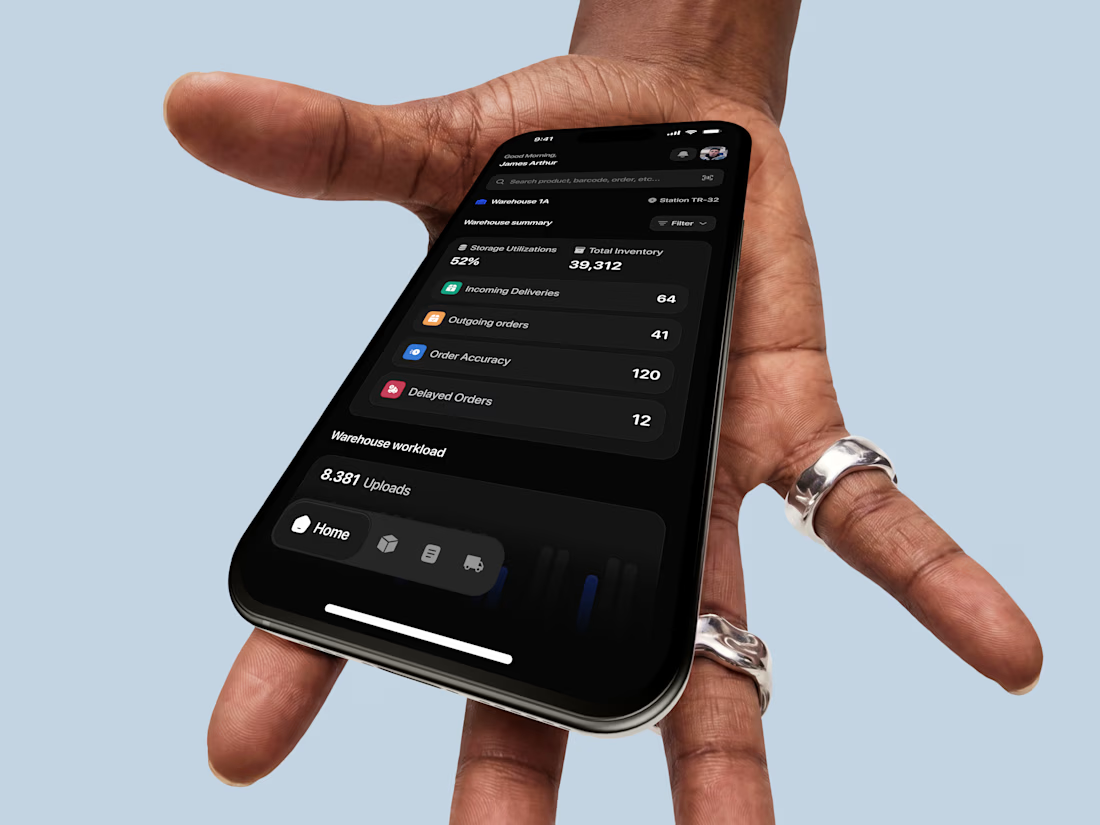
Invenio is a modern mobile supply chain application built around real-time fleet visibility, warehouse capacity tracking, and effortless dock auditing.
The goal was to eliminate operational friction for logistics leads — pairing deep OLED dark-mode surfaces with vibrant status badges and clear typography to make field management feel structured and weightless.
Special attention was given to:
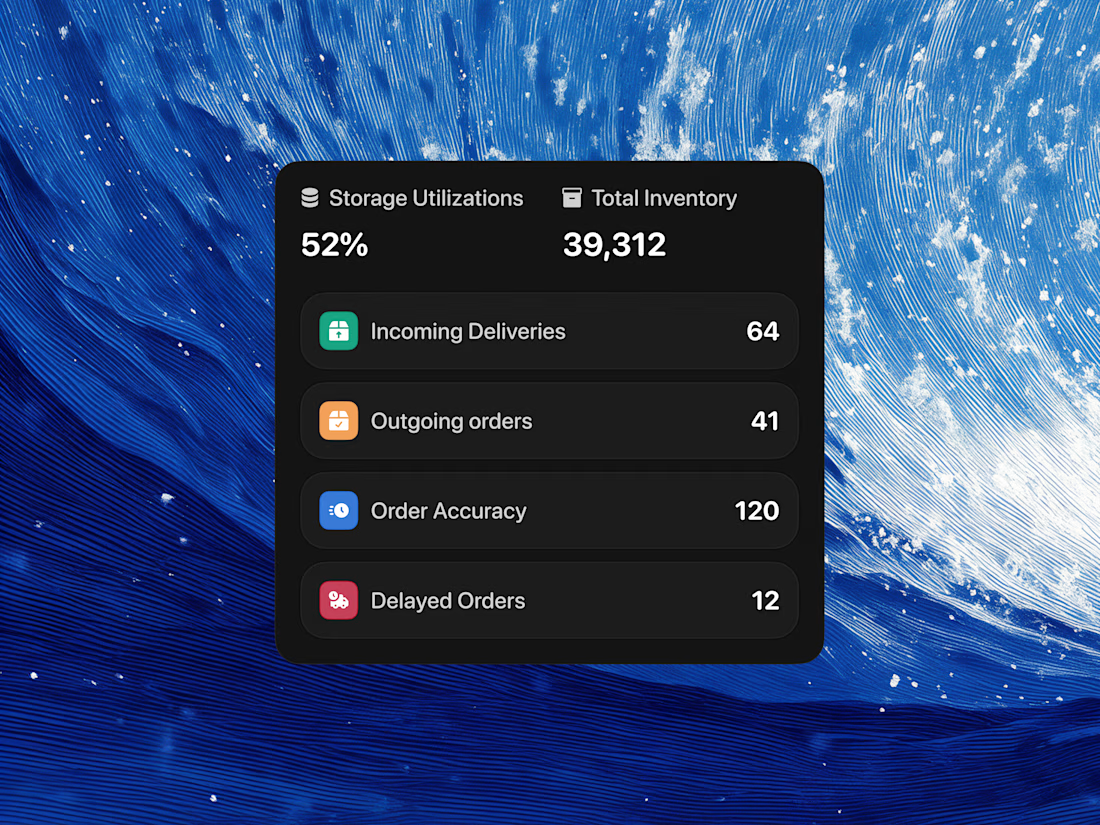
• A scannable Warehouse Summary hub displaying total stock counts (39,312 units), storage capacity gauges (52%), and incoming dispatch alerts.
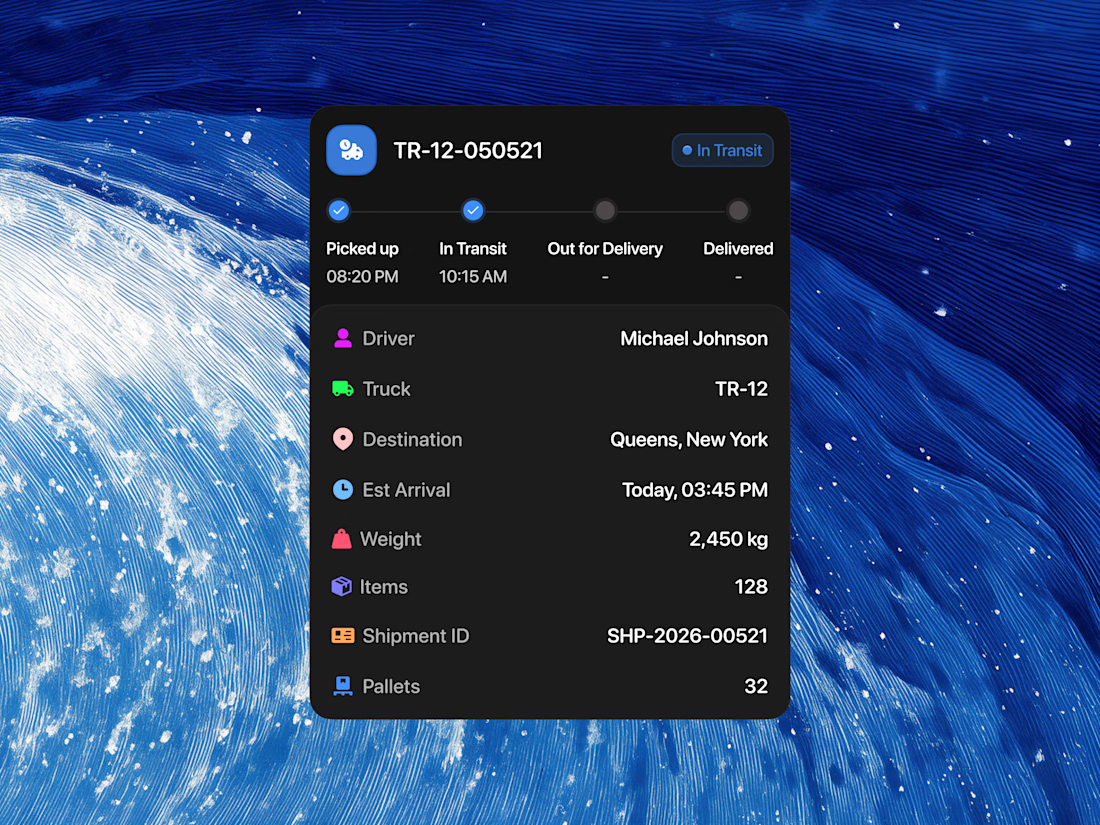
• Granular shipment tracking cards detailing truck assignments (TR-12), driver names, route destinations, shipment weight, and pallet numbers.
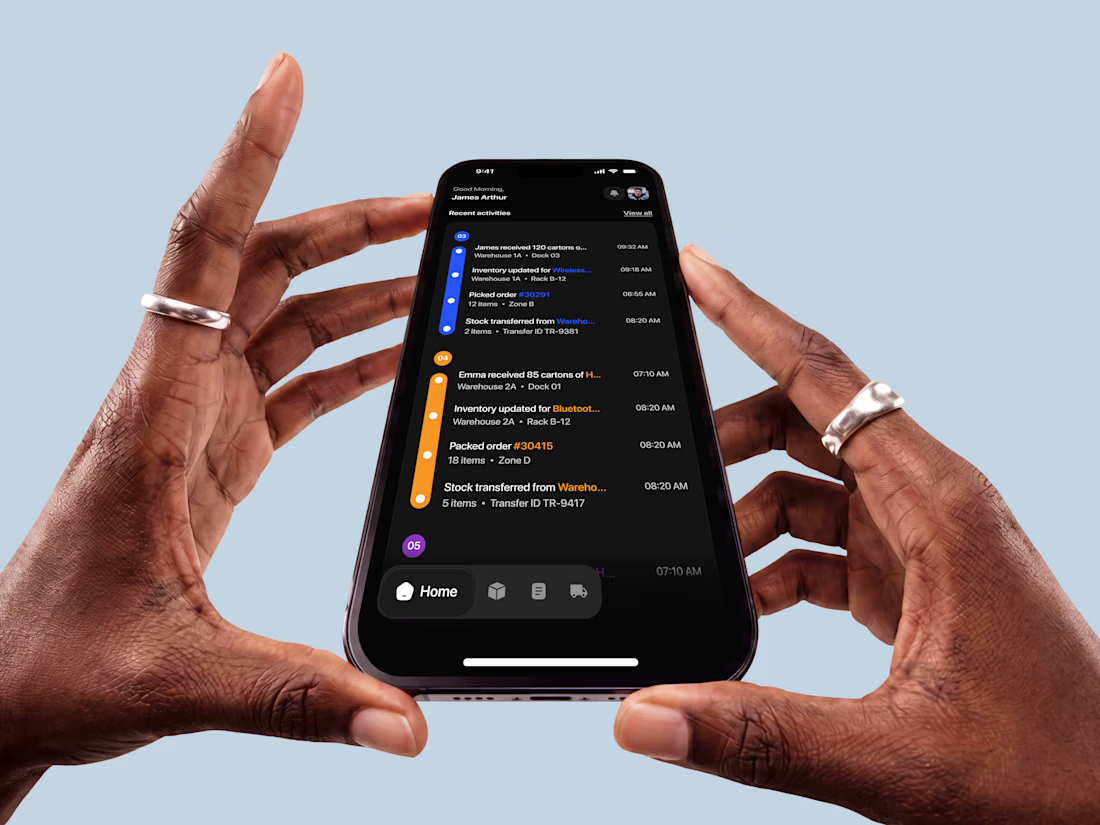
• A chronological activity node feed giving supervisors live visibility over dock transfers, picked orders, and warehouse worker actions.
• High-visibility status indicators (Picked up, In Transit, Out for Delivery, Delivered) for instant tracking during fast-paced shifts.
The result is a enterprise-ready mobile app that balances industrial utility with clean design sophistication.
Ready to transform your supply chain, logistics, or enterprise software into a seamless digital experience? Let’s partner up to build something extraordinary ✨