The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

An email address can end up in an AI prompt without anyone meaning to share it. Someone pastes a customer message, a support ticket, or part of a document, and the address travels with the rest of the text.I built a Chrome and Firefox extension that catches detected email addresses in ChatGPT requests and replaces them with [EMAIL_ADDRESS] before the request leaves the browser.The important design decision wasn’t the placeholder. It was where the masking happens. Redacting the text after it reaches the service is already too late.The scope is deliberately narrow: detect email addresses in this browser workflow, replace them locally, and leave the surrounding prompt intact. Narrow privacy controls are easier to explain, test, and trust than broad claims about “protecting all PII.”Where would you put this kind of check in your own AI workflow: the browser, an API gateway, or both?


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started


Related posts


Anybody play around with Jev from Typescript AI yet? I posted a bit about it on LinkedIn.
You can sign up for the early access waitlist at https://typesafe.ai/
https://www.linkedin.com/posts/andres-sepulveda-morales_5-ways-id-use-jev-activity-7507515068855779329-oLig?utm_source=share&utm_medium=member_desktop&rcm=ACoAAB-VMgMBP6g6pX36VvyRiHJ7gCDHQR823Jo

We’ve been playing around with JEV too!
We used it to compare two different website directions and see how it judged them from a visitor’s perspective. Really interesting to see how differently it reads visual impact vs. client usability.
We shared the breakdown here if you’re curious: https://on.contra.com/HwjnJF
on.contra.com
Can AI tell which website is actually better for a client? JEV has been everywhere lately, so we ...
Can AI tell which website is actually better for a client? JEV has been everywhere lately, so we got curious and put two different website directions we designed for the same creative studio through…

Making components with an AI agent for my new Framer project. So far, I’ve made a background with adjustable square sizes, gaps, spacing, and colors, plus an animated text box, put them together in a little shot. I’m enjoying experimenting with small animations that don’t make the screen feel too busy.


The dotted gradient stays quiet while the coral on “recurring work” carries the hero. That small text motion feels like a system, not extra noise.

Blockwave Studios – High-Fidelity Digital Creator Marketplace & Storefront
Delivered an end-to-end interactive product demo approved by a gaming creator studio to power their next-generation digital storefront. Transformed complex multi-vendor commerce requirements into a seamless user experience spanning touch-enabled media galleries, dynamic cart/bundle pricing engines, and modular creator payout dashboards.

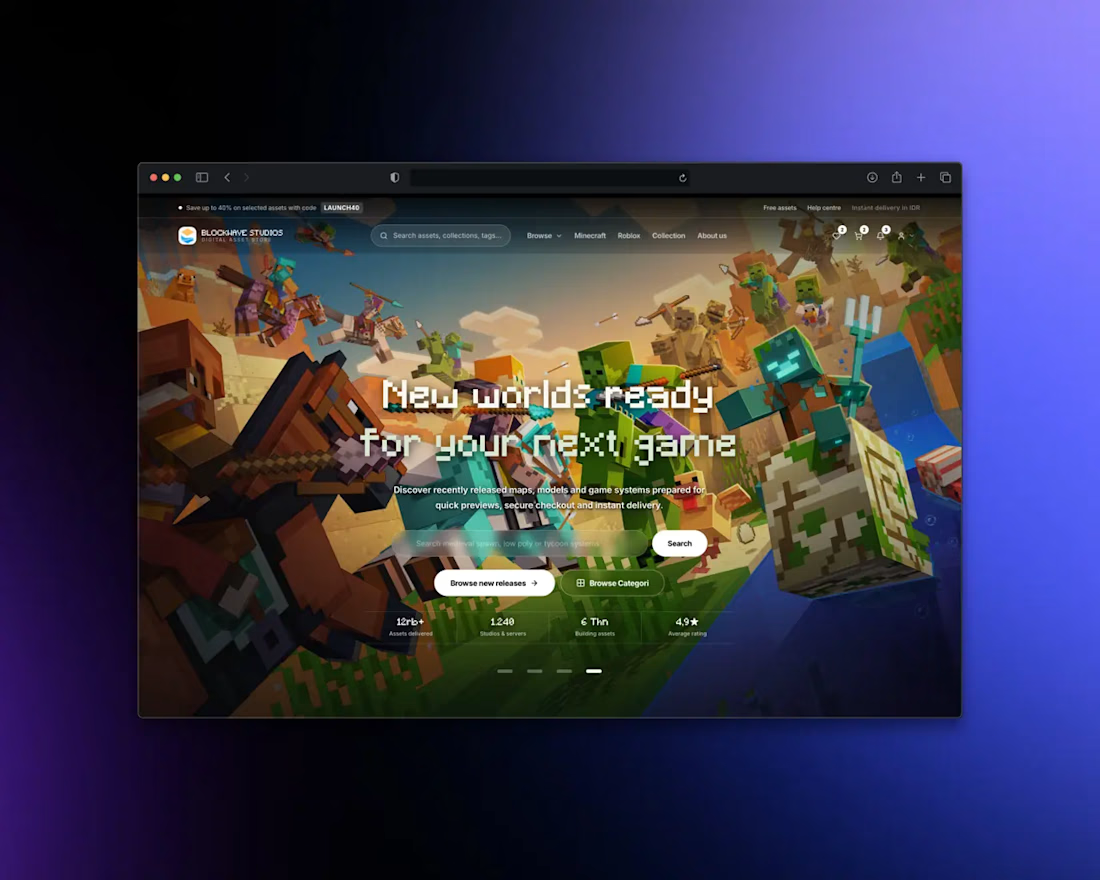

Complex marketplace requirements translated into a clear storefront.