The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Bug Bounty Research - Web Vulnerability Discovery
Conducted independent bug bounty research on public VDP and paid programs (Bugcrowd/HackerOne). Discovered and reported multiple valid vulnerabilities including IDOR exposing PII, stored XSS in user-controlled fields, SSRF via internal metadata endpoint, authentication bypass via JWT manipulation, and sensitive data exposure through misconfigured S3 buckets. Findings spanned government agencies, SaaS platforms, and financial services targets.
Documented all findings with full reproduction steps, CVSS scoring, and business impact analysis following responsible disclosure guidelines.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started







Related posts

Cybersecurity tools can feel overwhelming for small teams.
Shielda explores a cleaner dashboard experience that helps businesses monitor their digital footprint across domains, email, and social channels.
The interface surfaces password leaks, phishing clones, suspicious mentions, and brand abuse through a clear Security Score, compact threat cards, severity tags, and AI-powered summaries.
Instead of forcing users to interpret complex security data, Shielda helps them understand what happened, how serious it is, and what to do next.


Polar — Local AI Desktop Assistant
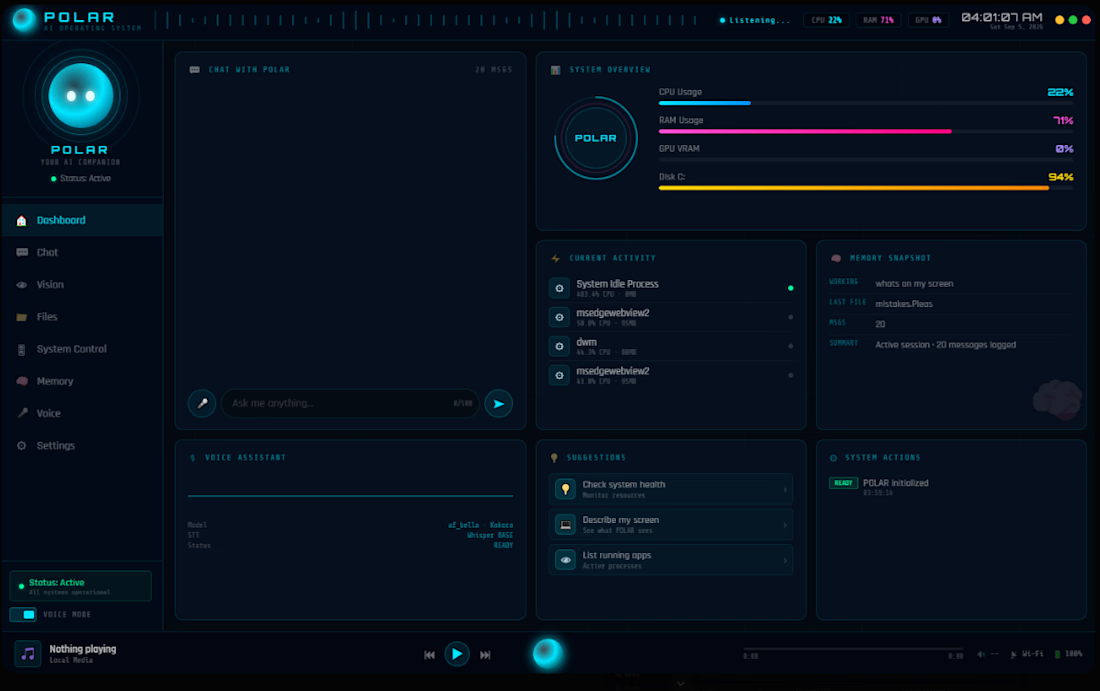
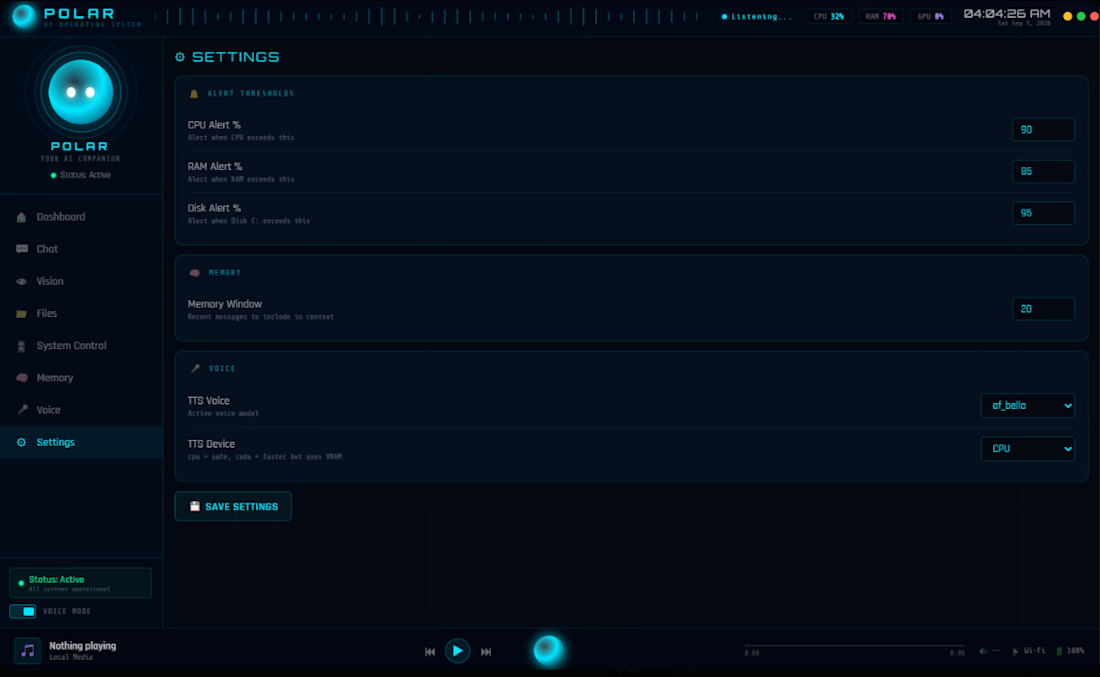
Polar is a local, privacy-focused AI desktop assistant designed around a futuristic HUD interface and system-level interaction.
The project explored how a desktop AI could understand the user's environment, process visual and voice input, and respond or perform actions without relying entirely on cloud services.
Key features:
Local AI assistant architecture
Futuristic Tauri-based desktop HUD
Screen and contextual awareness
OCR-based extraction of text from the screen
Voice interaction pipeline
AI-powered context processing and responses
System-level desktop interaction and automation
Local/offline model execution
Real-time assistant-style interface
OCR pipeline:
Screen capture → OCR → Context extraction → Local AI → Response/Action → HUD
The project combined AI, computer vision, OCR, voice interaction, desktop application development, and modern UI engineering into a single experimental personal-assistant platform.
My contribution: Architecture, application development, AI integration, OCR functionality, UI/HUD development, and system interaction.



This is beautiful

An independently built SOC platform combining host telemetry, rule-based detection, machine-learning anomaly detection, real-time incident management, and analyst collaboration in a unified interface.