The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

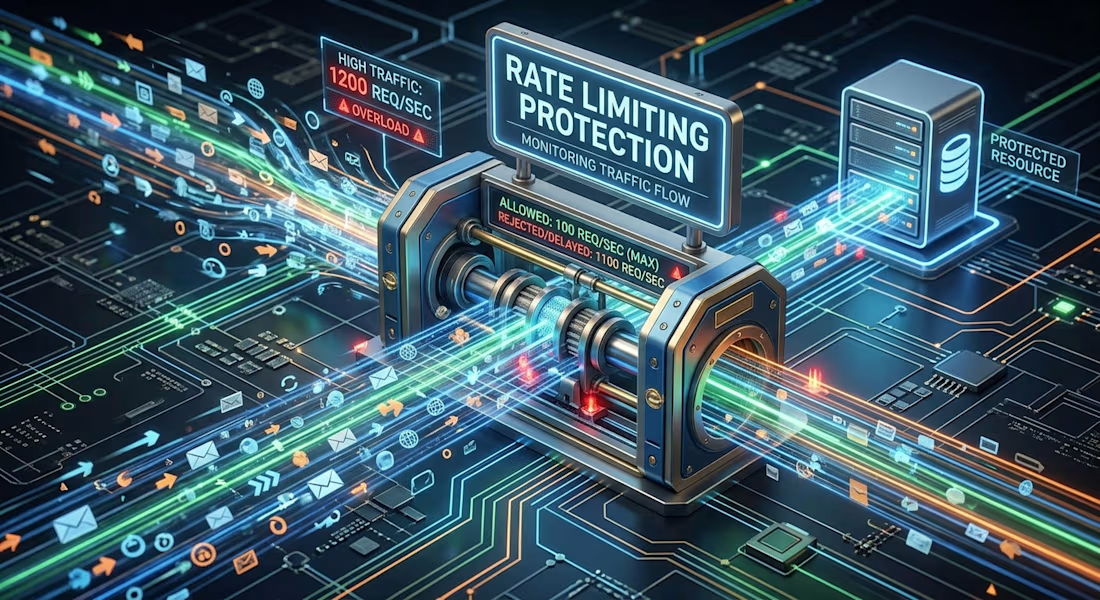
Rate limiting isn’t “npm install + two lines in nginx.”
Most tutorials make it look trivial: add a throttler package to NestJS, add limit_req to nginx, done.
Problem 1: your server sees the proxy, not the user.
Behind nginx, every request arrives from the proxy’s IP. So the whole site shared ONE rate limit. Ten login attempts per minute for everyone. Anyone could lock all users out.
The fix is one line in main.ts (app.set('trust proxy', 1)) plus forwarding X-Forwarded-For in nginx. The number matters: true trusts any client-supplied header and lets attackers spoof their IP. 1 trusts exactly one hop.
Problem 2: CSR and SSR see different IPs.
Client-side calls (login, refresh) go browser --> nginx --> API, so the API sees the real user IP.
But with Next.js SSR on a serverless platform like Vercel, the page is rendered on Vercel’s servers. The API sees a pool of cloud IPs, not your visitors. Every SSR visitor shares the same few IPs, and therefore the same quota.
The fix: the SSR layer forwards the visitor’s IP in a custom header, signed with a shared secret. The API only trusts that header when the secret matches. Without the secret check, anyone could forge the header and bypass your limits.
Lesson: rate limiting is an architecture problem, not a package. Know where your IP is lost, and who you trust.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started


Related posts

One of my posts went SUPER VIRALLLL. 🚀
80K+ views. 300+ likes. 50+ UpGoats. Hundreds of conversations.
All from one line I wrote straight from the heart.
"The miracles you're looking for are in the work you're avoiding."
I wrote it because that's genuinely how I felt. No strategy. No expectations. Just something I believed in.
I never imagined it would resonate with so many people, let alone become one of the most talked-about lines on my profile.
And now, looking at these numbers, the line hits differently. Sometimes, the sign you're waiting for is the work you've been putting off. Maybe the miracle really is on the other side of doing it. 🖤


Congratulations, Anky! It’s encouraging to see your hard work paying off. I just joined Contra and I’m still figuring things out, so seeing posts like this gives me a little extra motivation. Hopefully, I’ll have my own milestone to share here someday!

Every client has said this at least once:
"It’s just one small change."
Then auth breaks, database need a migration, one integration stops working, and somehow it’s 2 AM 😅
Writing the change is usually easy. Finding everything it can break is the real work.
What was your biggest “small change”?


This is so relatable — that line about finding everything it can break being the real work is spot on. The 2 AM part made me laugh.

Afterhours is a portfolio you can explore.
Built for my friend Stanislav Pogorskii, a full-stack developer, it connects his background in games journalism, his work as a Laravel developer, and his next steps in game development.
Switch on the radio. Open a console. Explore the workspace, browse real projects and published articles, or step onto the balcony. Each interaction reveals something about the person behind the work.
As usual, the process involved a few different tools, hehe. I developed and iterated on the project locally using my own CLI setup, pushed it to GitHub, then brought it into Base44, where I connected a CRM system.
The experience also leads to a practical next step: a short project quiz that turns a visitor’s answers into an editable email draft.
Personal details spark curiosity. Real work builds confidence. A useful interaction can help you see who you are and where you could go next.
Created for #Base44Challenge with @Base44.


I feel seen! Love this so much.