The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

⚠️ Developers: Be careful with project files sent by “clients” or "recruiters".
I recently received a project from someone, who I reported instantly after looking at the malicious codebase. After inspecting the files, I discovered it was a malicious Git repository designed to target developers. I reported the person immediately.
The project looked like a normal Next.js/NestJS application, but the malicious code was hidden inside .git and related folders.
The attack was designed to trigger through normal developer workflows such as:
- git status, git checkout, or git commit
- VS Code/Cursor Git integrations
- AI coding agents that automatically inspect a repository
- Git hooks and other automated tooling
The payload appeared designed to retrieve additional encrypted programs from attacker-controlled infrastructure and execute them with the developer's permissions. The technique also showed characteristics reported in attacks targeting developers through fake freelance/job opportunities.
Important: I did not extract or execute the repository, and I inspected it in an isolated/read-only manner.
Protect yourself. Before opening an unfamiliar project:
- Don't blindly run npm install, git status, scripts, or other commands.
- Be extremely careful with .git, .github, .husky, .claude, and Git hooks.
- Don't open suspicious repositories directly in your normal development environment or AI coding agent.
- Verify who sent the project and why they need you to download it.
- If something feels suspicious, inspect the archive without extracting/executing it.
Don't assume a professional-looking codebase is safe. A developer's normal tools can become the attack surface.
SHA-256 of the archive:
94bc839a9876138b5bdeafdac068b43ece80b42eda240caff95a8e3a35b06a1f
Stay safe out there. 🔐


Thanks for the heads up Haris

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started





Related posts

Six website templates I'd happily hand to a client. Each one comes as plain HTML (unzip, open, online) and as React. None of them make third-party requests, they're accessible by default, and the docs are written for AI tools.
It's also like my portfolio in a way.


Building zero-request clean templates with AI-ready docs is absolute developer witchcraft.


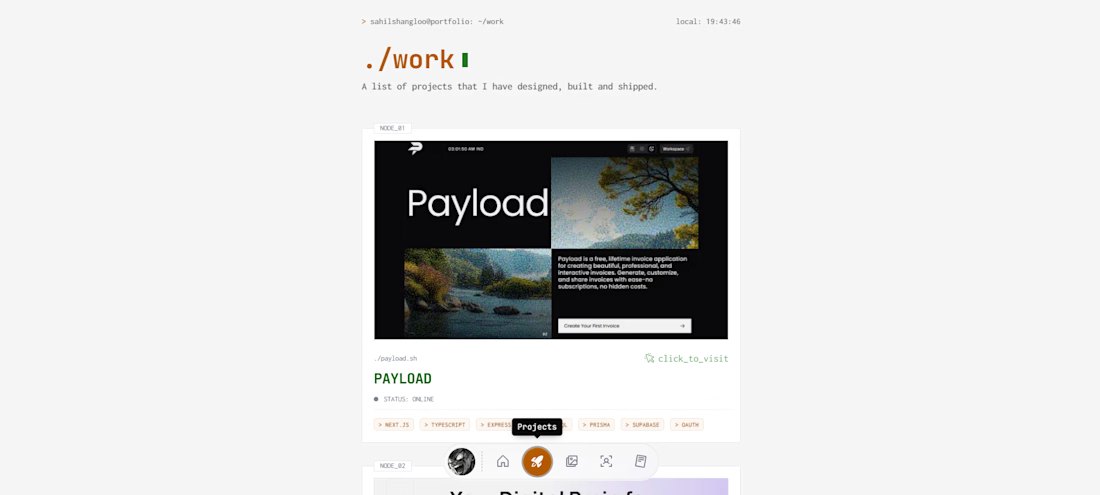
My portfolio is a collection of projects I have built across frontend and full-stack development.
It includes products like Payload, Cloak Me, Pulse Check, Brain Bucket and other experiments where I have worked on everything from UI and user experience to APIs, databases, authentication, real-time systems, and deployment.
I have kept the portfolio itself minimal and terminal-inspired because I wanted it to feel personal instead of looking like another generic developer template.
Most of the work there is built with React, Next.js, TypeScript, Node.js, PostgreSQL, and tools I actually use while building real products.