The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

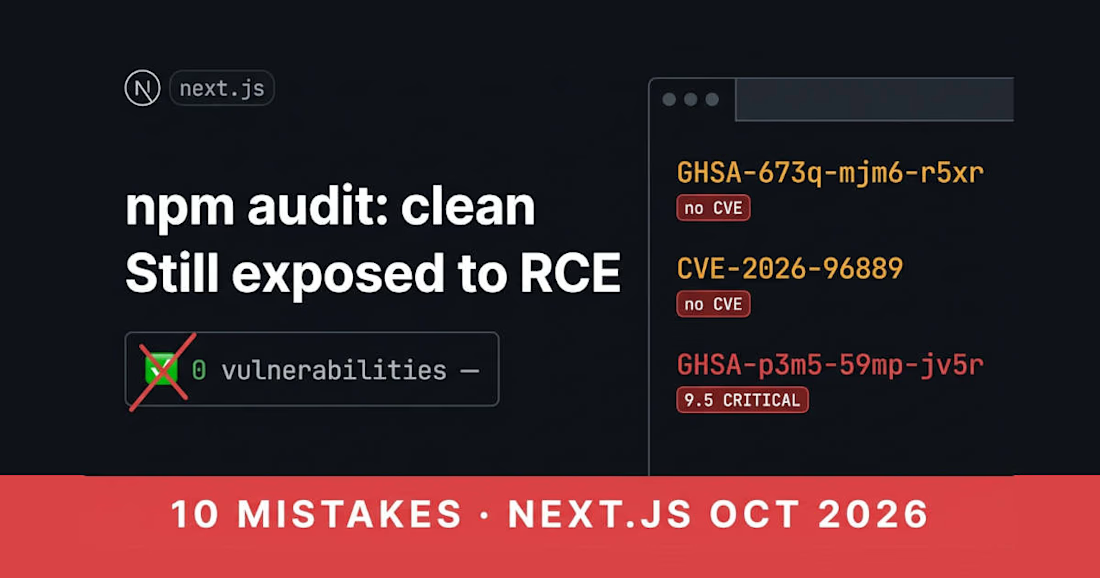
🔴 A dev on r/nextjs upgraded to 15.5.28, ran npm audit, saw green, and went home happy.
His app was still vulnerable. Here's why 👇
On v15, Next.js 15.5.28 still accepts the broken sharp 0.34.x. The upgrade looks done. The old vulnerable version just... stays there.
And npm audit? Two of the three October 14 bugs (CVSS 9.5!) had no CVE yet. Clean report. False confidence.
This is one of 10 mistakes I keep seeing since the patch dropped:
❌ Trusting a green scanner
❌ Upgrading on v15 and stopping there
❌ Forgetting dangerouslyAllowSVG is on
❌ Patching sharp and calling it a day
❌ Skipping the rebuild + redeploy
The patch takes 5 minutes. The mistakes happen around it.
Third image-processing RCE in Next.js in 3 months. This isn't a one-off — it's a dependency chain problem.
Full breakdown + exact fix commands 👇
https://blog.webdevlab.org/nextjs-security-mistakes-remote-code-execution
#NextJS #WebSecurity #JavaScript #React #CyberSecurity #WebDev
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started








Related posts

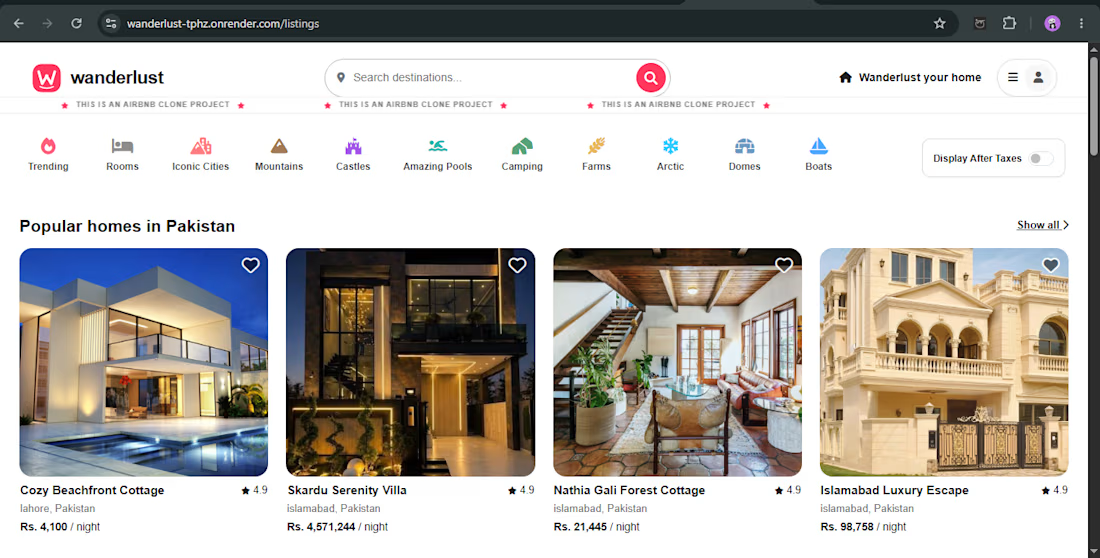
🚀 Introducing WanderLust — My Full-Stack Web Development Project
I built WanderLust, a full-stack booking web application using Node.js, Express.js, MongoDB, and EJS.
✨ Key features:
User authentication and authorization
Create, edit, and manage property listings
Reviews and booking functionality
Image uploads using Cloudinary
Interactive maps with Mapbox
Search and category filters
🛠️ Tech Stack: JavaScript, Node.js, Express.js, MongoDB, Mongoose, EJS, Passport.js, Cloudinary, and Mapbox.
This project helped me strengthen my backend development, database integration, authentication, and deployment skills.
I'm a junior full-stack developer interested in building useful web applications and collaborating on real-world projects.
🔗 Live Demo: https://wanderlust-tphz.onrender.com
💻 GitHub: https://github.com/Aabi-dev10/WanderLust
#FullStackDevelopment #MERNStack #JavaScript #WebDevelopment #NodeJS



did you build the reviews and booking flow first?

This is a website for my Italian client that I meet on upwork which includes a separate menu page with QR code


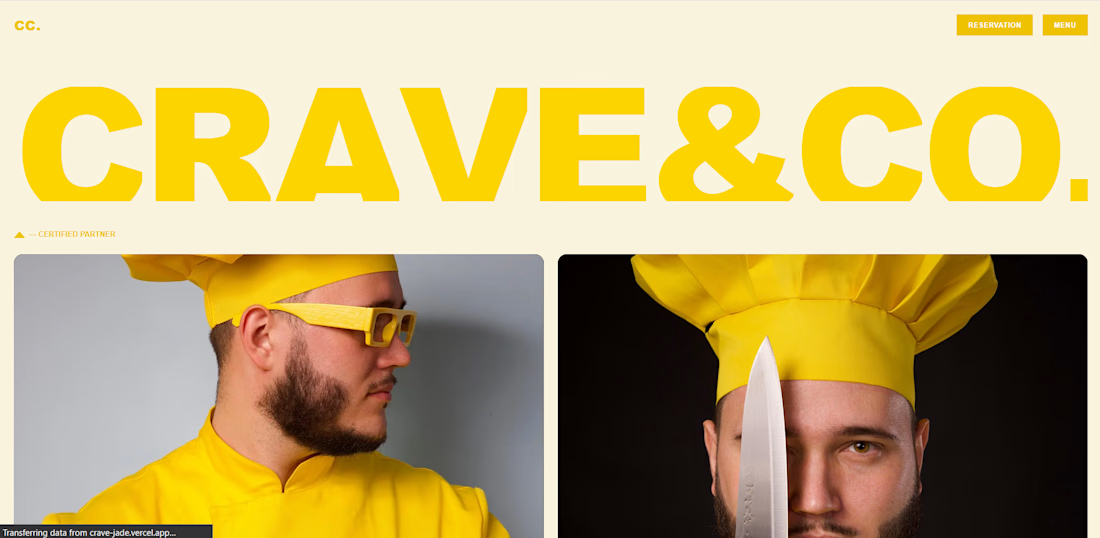

The oversized CRAVE&CO type does all the heavy lifting, Kalid. Pairing that with the chef portraits gives the brand real character. And answering the QR update question with an authenticated admin page shows you are thinking about the client long after launch. Solid work.

Turning ideas into fast, scalable, and user-friendly digital products. ⚡
From frontend experiences to backend systems, APIs, databases, and automation, great full-stack development is about making everything work together seamlessly.
Building smarter. Shipping faster. Scaling better.
What’s the biggest challenge you face when building a web product? Comment below 👇