The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

How many wrong passwords does your login page allow? On many sites: unlimited.
That's all a password bot needs. It tries thousands of passwords an hour, never gets tired, and sooner or later one of your employees' passwords works. From then on, the bot sees everything that person can see: salaries, personal data, contracts. No alarm goes off.
Here's how I build login pages: after 5 wrong passwords, that account locks for 15 minutes from that address. A bot drops from thousands of guesses an hour to 20, which isn't enough to crack a real password. The real employee still gets in from their own computer, because the lock only applies to the address the attack comes from.
I just added this to my CRM project and tested it on the live site: 5 wrong passwords, and even the right one gets "Try again in 15 minutes". Other users kept logging in as usual, and every failed attempt shows up in the admin log.
What this means for your business:
✅ Bots can't guess their way in
✅ Your team isn't locked out by someone else's attack
✅ You can see who's trying to get in
Need a website with logins, a client portal or a CRM? I'll keep the bots outside. Message me and tell me about your project.

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started




Related posts


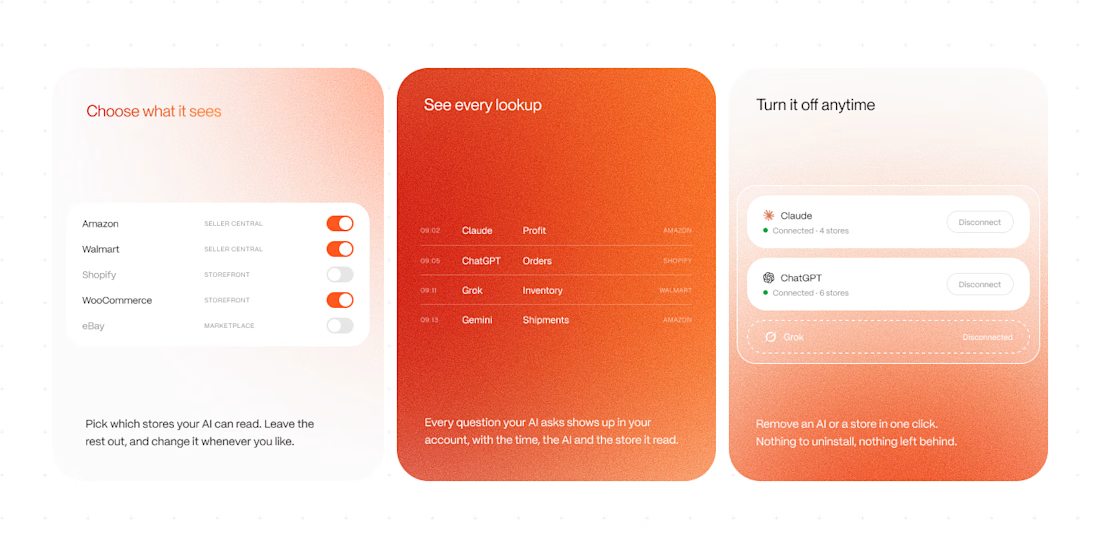
Giving an AI access to your store data is lowkey terrifying. So the website’s whole job here is making that part feel safe.
Card explorations for the trust section, wip:
→ Pick what it sees
→ See every lookup
→ Turn it off anytime
Went orange only on the middle one. The log is the proof, the other two are just controls.
Which one hits first for you?


Business website built with React and the Django REST Framework, featuring a clean, modern design and a seamless user experience.
ReactBackend DevelopmentFull Stack DevelopmentWeb DevelopmentBootstrapDjangobusinesswebsitewebsitedesignwebdevepment


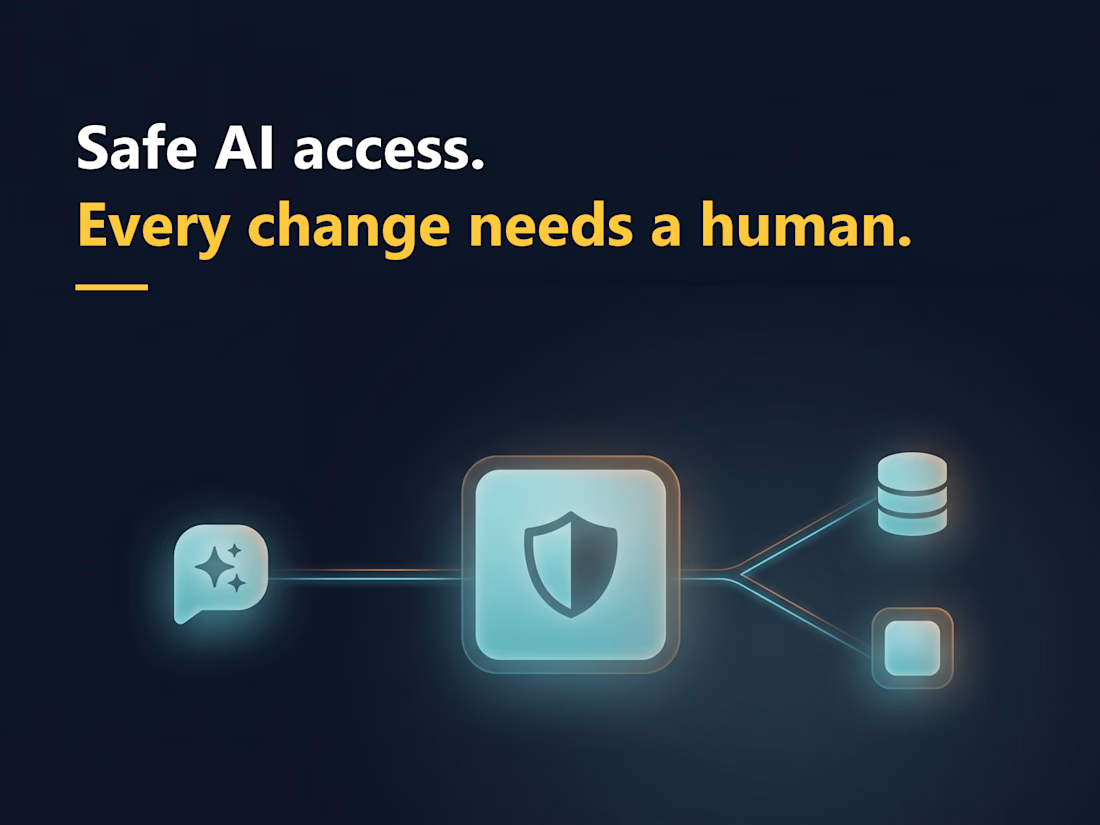
Giving AI full access to your business data is risky. Giving it no access makes it useless.
So I built a small server that sits in the middle. Claude can search and read my agency records, but it cannot change anything on its own. Every change needs a human to approve it first, and every answer shows which record it came from.
I use it every day with Claude Code.
If you want AI to work with your own systems safely, I can build the same for you.


I'd bind each approval to the proposed field changes and the record version it was reviewed against. If someone edits an agency record while a change is waiting, does your server require a fresh approval before applying the proposal to the newer data?