The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

I discovered an Insecure Direct Object Reference (IDOR) vulnerability in a practice web application that allowed unauthorized users to access other people's private snippets simply by changing a number in the URL. Using whatweb and manual inspection, I identified parameter tampering points and successfully accessed private data for five different users without authentication. The finding was documented in a comprehensive report including executive summary, technical details with screenshots, CVSS risk scoring, and step-by-step remediation instructions. This assessment demonstrates my ability to find broken access controls that automated tools miss and deliver clear, actionable fixes.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started



Related posts

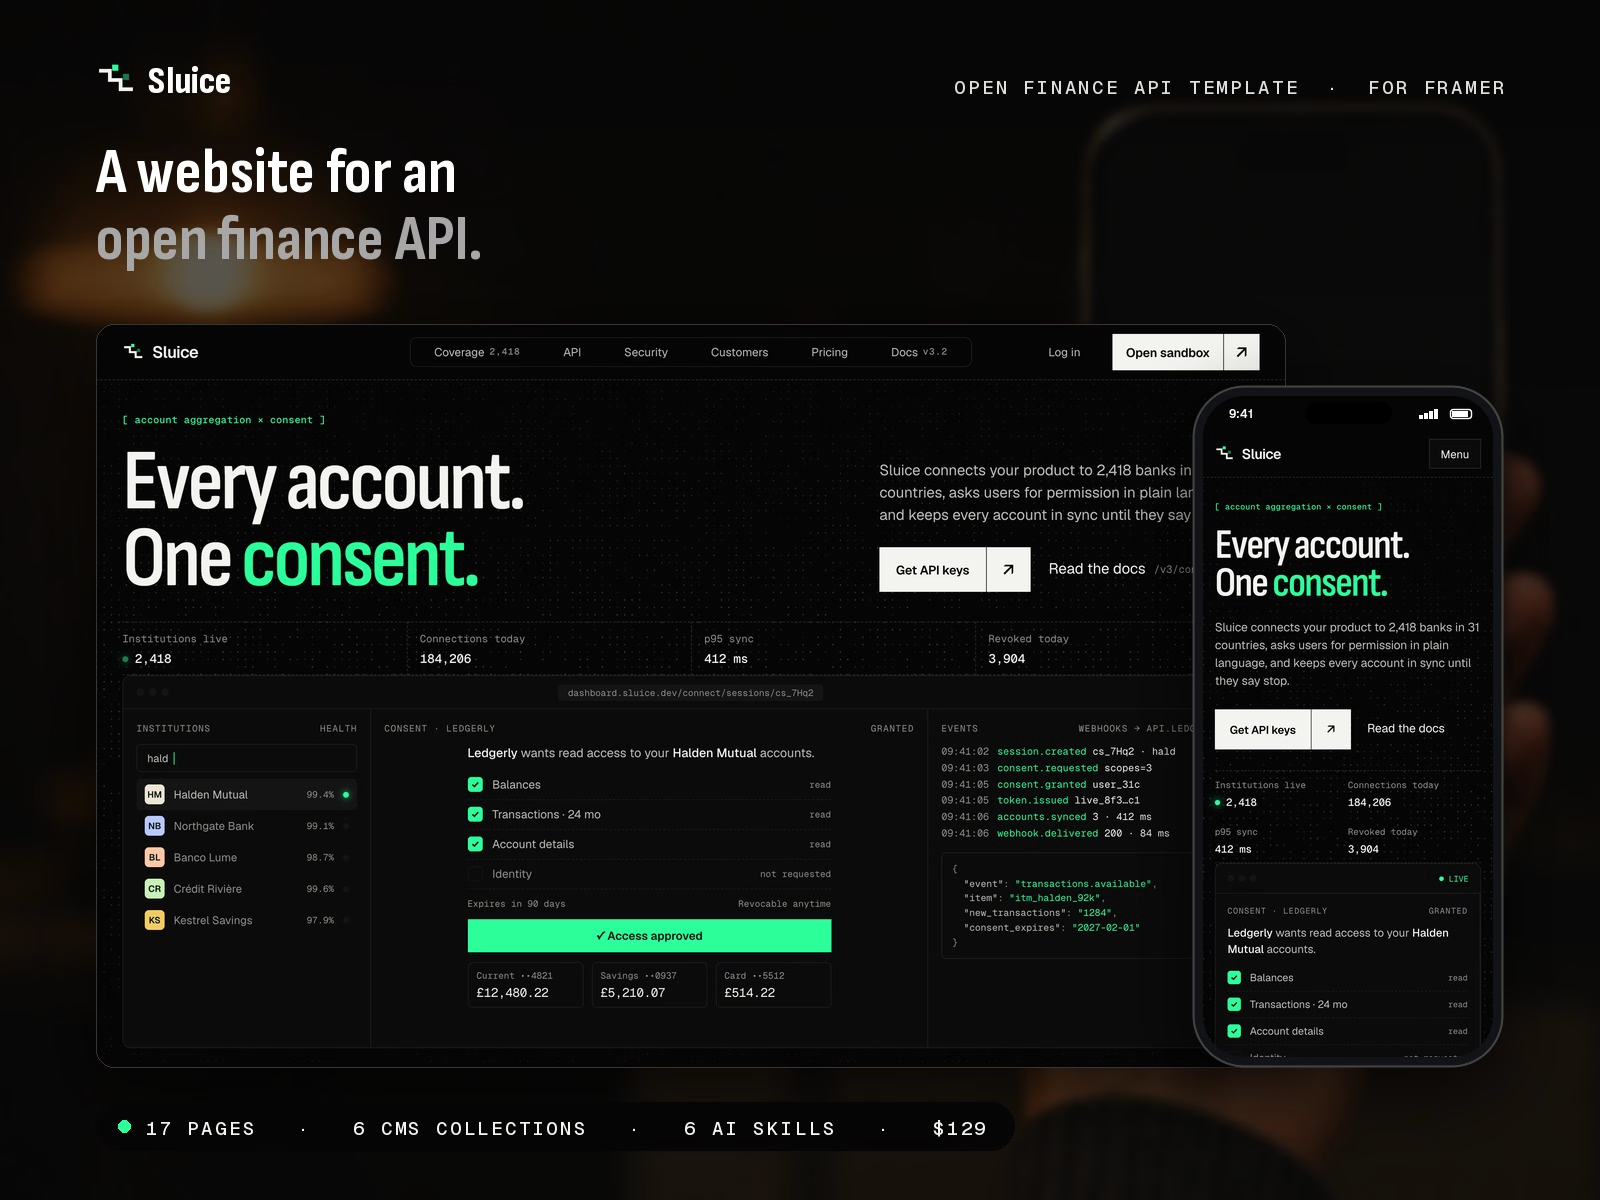
Just shipped Sluice: a Framer template for open finance APIs.
Most fintech API sites open on a gradient and a promise. Sluice opens on a live console: a user picks a bank, approves access, and the accounts and webhooks arrive.
→ The consent moment plays out on a phone: pick a bank, share exactly what is needed
→ Every bank gets its own CMS page with ninety days of health, one bar per day
→ The Security page puts every grant on a consent ledger, and plays a revoke out live
→ Twelve endpoints, signed webhooks and code in Node, Python and cURL
17 pages, 6 CMS collections, 3 code components, a Start Here page in 13 steps and 6 Agent Skills.
$129, one-time. Remix link delivered instantly after checkout:
https://contra.com/products/VQDMPmng-sluice-framer-template-for-open-finance-ap-is



MySecret: Zero-Knowledge Encryption Engine & Biometric Security for Obsidian