The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Secure your storage with AI control by Vault Desk #privacy #security #cloudflare
Link: vaultdesk.io
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started










Related posts

🕵️ RealityOS: The Hollow Hour — What if reality itself was hiding the evidence?
Built with @Base44 for the #Base44Challenge 🚀
A woman has disappeared from reality. The official records say she was never there. But the evidence tells a different story.
Welcome to RealityOS, a cinematic, interactive sci-fi detective mystery where every clue matters and your decisions determine the ending.
🔎 Investigate the impossible
Examine mysterious records, airport surveillance, and hidden clues.
Connect evidence to uncover contradictions in the timeline.
Decode a terminal and unlock a concealed room.
Discover what happened during the mysterious 11-second gap.
🧩 The mystery doesn't end with finding the truth.
Choose your verdict:
RESTORE — Bring her back.
PRESERVE — Keep her frozen in the archive.
CONTAIN — Seal the truth away.
EXPOSE — Reveal the impossible to the world.
Four choices. Four different outcomes. One mystery for you to solve.
It took around an hour of investigating with ChatGPT's help to work through the clues, uncover the hidden room, validate the evidence connections, and explore all four endings.
This project is an experiment in making an AI-built application feel like a playable world rather than just another dashboard.
🎮 Play RealityOS: The Hollow Hour
Built with @Base44 for the #Base44Challenge.
Would you RESTORE, PRESERVE, CONTAIN, or EXPOSE? 👀


This looks fantastic! 🤩

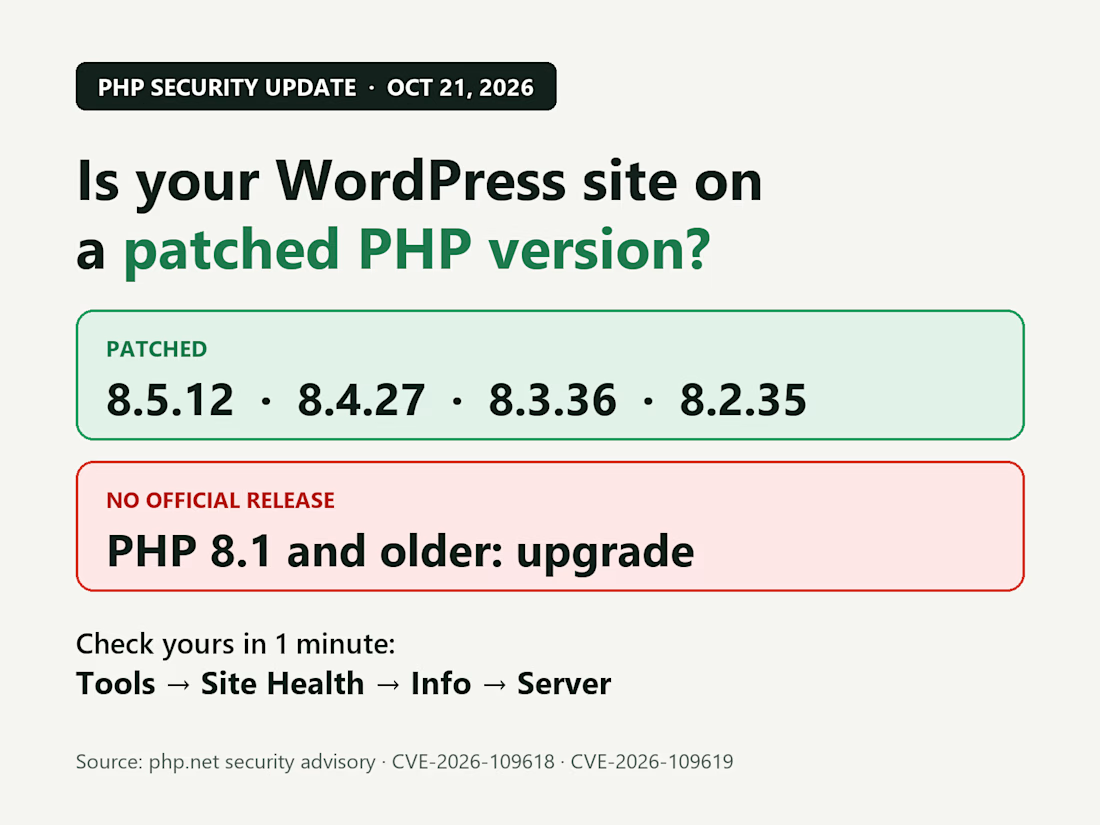
Critical PHP security update: check your WordPress site's PHP version today.
On October 21, PHP released fixes for two critical vulnerabilities (CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on CVSS v4.0) that can allow remote code execution without a login. Every PHP install serving web pages is in scope, and the PHP security team rates Apache mod_php as the most exposed, with a demonstrated exploit.
Patched versions: 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
PHP 8.1 and older get no official release from the PHP project: ask your host about a backported fix, or upgrade to a supported version.
Check yours in one minute: WordPress dashboard → Tools → Site Health → Info → Server.
I updated my own sites the same evening: backup first, key pages checked before and after. If you'd like me to check or update yours, message me here.



This is genuinely useful, Zakaria. The one-minute check path through Site Health is the kind of thing most site owners would never find on their own, and flagging that 8.1 and older get no official release is the detail that actually moves people to upgrade. Have you seen hosts...

🚀 Excited to share my project with the Contra community!
Introducing SocialFlow AI — a social media management web app built with Base44.
✨ What it offers:
📅 Content Planning
🤖 AI Caption Assistant
👥 Client Management
📊 Analytics Dashboard
✅ Content Approval Workflow
⚡ Automation Features
My goal was to create a modern, user-friendly platform that helps social media managers and freelancers organize their work more efficiently.
Building this project has been a great learning experience, and I’m excited to keep creating and improving my skills.
#Contra #ContraChallenge #Base44 #SocialMediaManagement #AI #WebApp