The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

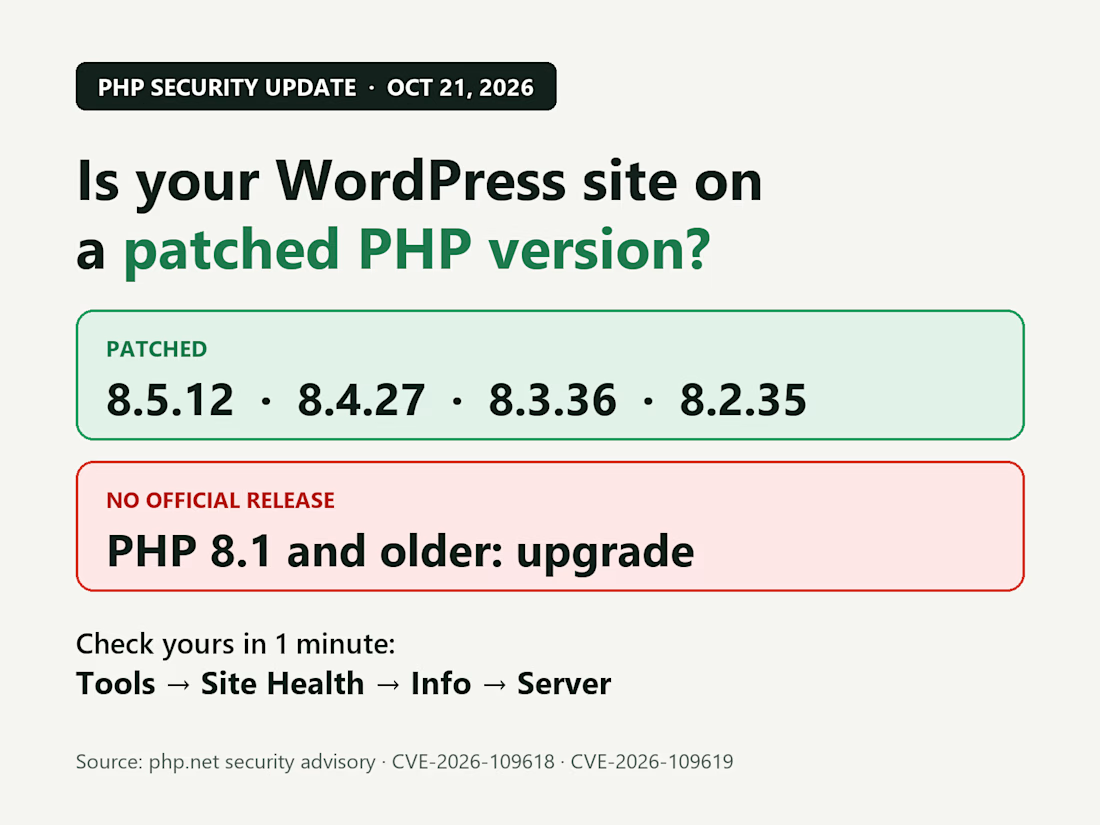
Critical PHP security update: check your WordPress site's PHP version today.
On October 21, PHP released fixes for two critical vulnerabilities (CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on CVSS v4.0) that can allow remote code execution without a login. Every PHP install serving web pages is in scope, and the PHP security team rates Apache mod_php as the most exposed, with a demonstrated exploit.
Patched versions: 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
PHP 8.1 and older get no official release from the PHP project: ask your host about a backported fix, or upgrade to a supported version.
Check yours in one minute: WordPress dashboard → Tools → Site Health → Info → Server.
I updated my own sites the same evening: backup first, key pages checked before and after. If you'd like me to check or update yours, message me here.



This is genuinely useful, Zakaria. The one-minute check path through Site Health is the kind of thing most site owners would never find on their own, and flagging that 8.1 and older get no official release is the detail that actually moves people to upgrade. Have you seen hosts...
Thanks Timothy! Honestly, one day in, it's too early to say. What the PHP team says is that Linux distributions and LTS vendors got the patches in advance, so managed hosts that use distro packages should move quickly. The gap is self-managed servers and anyone on a third-party...
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started








Related posts

Managing secrets and access credentials across repositories, cloud environments, devices, and communication tools can create significant security risks. VaultX is designed to help DevSecOps teams automate password and API key rotation, manage SSH access, and prevent data leaks.
The landing page communicates these capabilities through a dark security-focused aesthetic, electric green accents, subtle glow effects, and product-focused UI previews. A digital globe, monitoring indicators, and security architecture map help explain how VaultX connects and protects different environments.
Explore the project on Dribbble:
https://dribbble.com/shots/27814100-Landing-Page-DevSecOps-Security


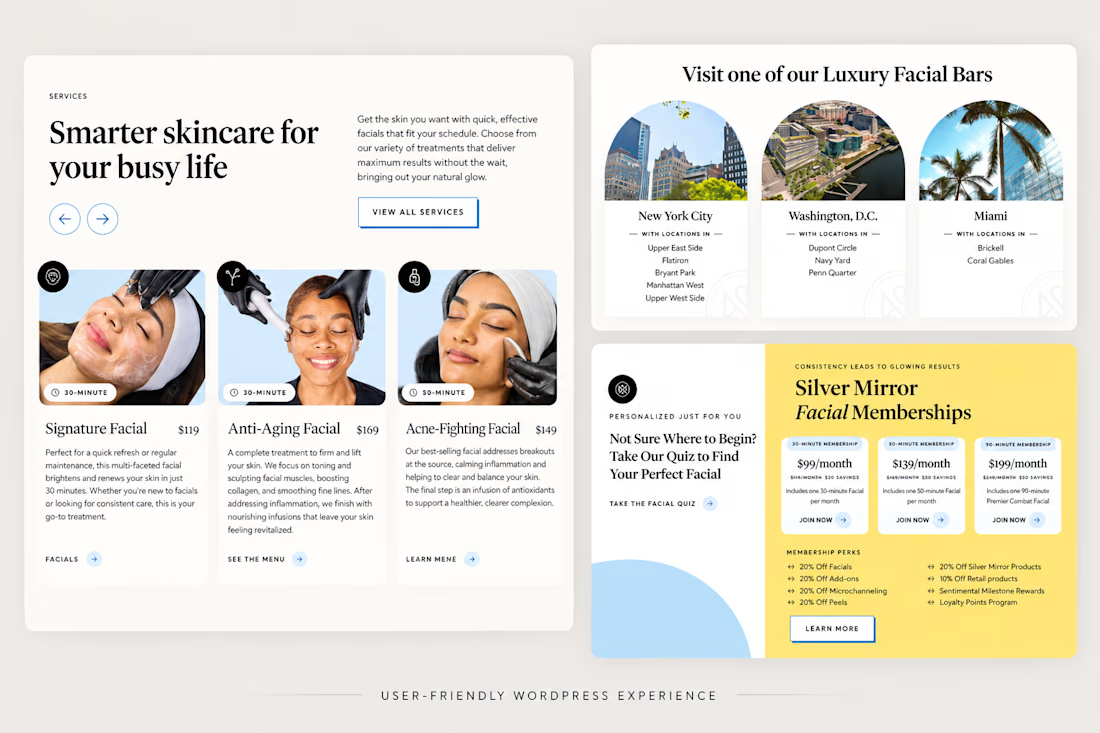
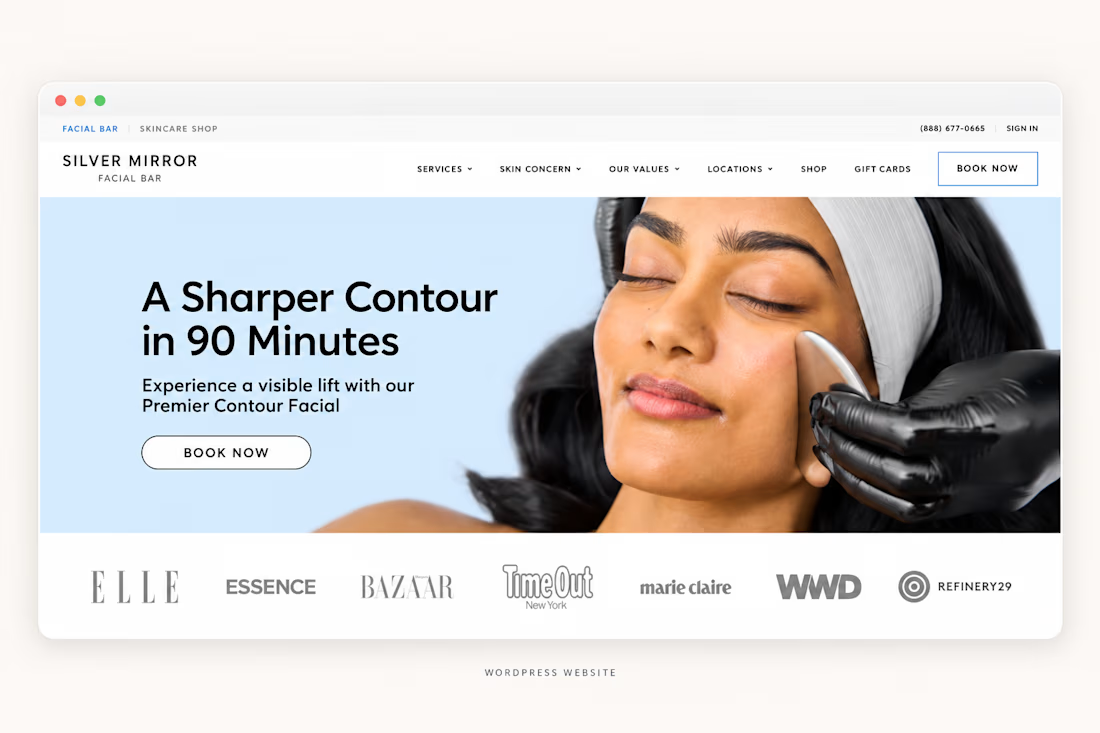
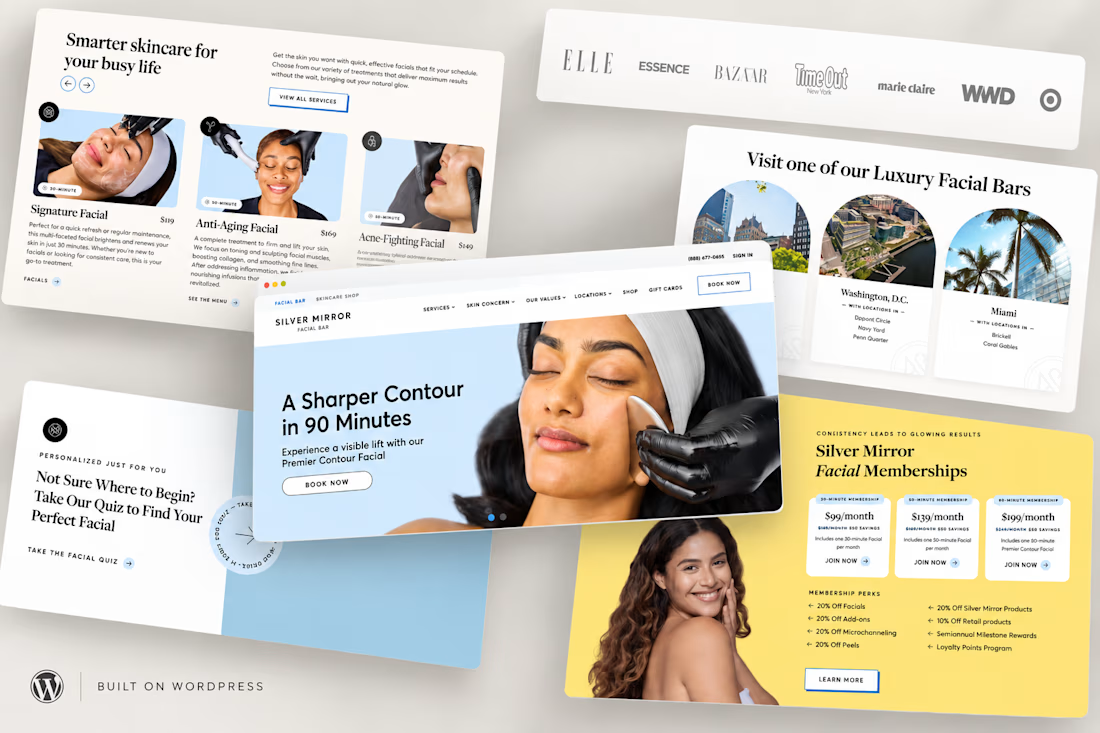
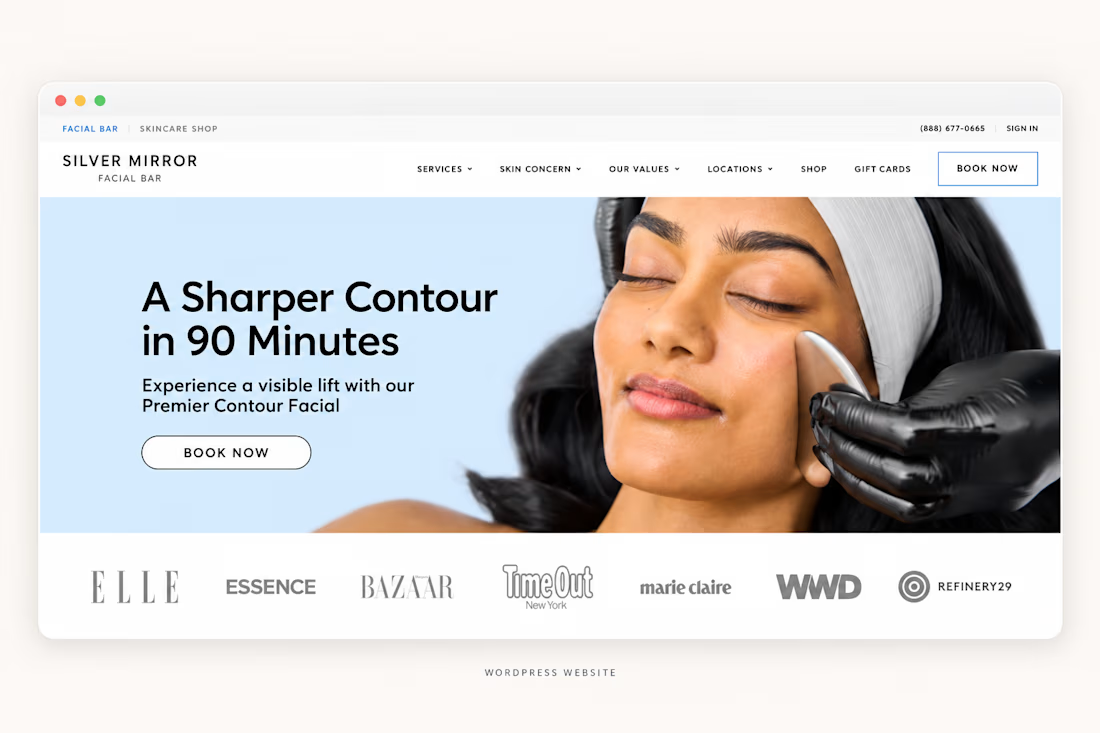
Silver Mirror | WordPress Beauty & Wellness Website UI/UX
Designed the UI/UX for Silver Mirror, a premium facial and skincare brand. I created responsive Figma layouts focused on service discovery, facial treatments, memberships, locations, booking journeys, testimonials, and skincare education. The experience balances a premium wellness aesthetic with clear navigation and conversion-focused calls to action, prepared for WordPress implementation across desktop and mobile.


This is top design. Love the overall pacing and balance on this.

Halloween is around the corner. So i made a Halloween event landing page Framer template. What do you think about the 404 page? personally i love it! check it here

