The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

A working MVP and a production-ready product are not the same thing.
Your MVP may already:
• have the core features
• connect to the database
• process payments
• use AI or third-party APIs
• look good in a demo
But production introduces a different set of questions:
-What happens when an API fails?
-Can users access data they should not see?
-Are webhooks actually verified?
-What happens when two actions happen at the same time?
-Are errors being logged?
-Can you safely deploy an update without breaking existing users?
-Are email, payments, auth, uploads and background jobs reliable outside the happy path?
This is usually where the final 20% becomes more important than the first 80%.
The goal is not to rebuild a working MVP.
It is to find the things that could hurt the product after real users arrive — and fix the important ones before launch.
That is the gap I have been focusing on lately: helping founders move from "it works" to "I am comfortable putting real users on this."
If you are building right now, what part of getting to production are you least confident about?
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started





Related posts

Just like AI, soon we will be made to believe it's not AI anymore, it's SI. Something more advanced.
But the same way AI lacks a soul, so will SI.
Mastering the tool is good. Selling it as a replacement for humans is just hype.
Be at the top of your game. Build connections, do your own research and planning, and keep finding ways to improve.
It's not that AI is bad. I always wanted something to handle the boring tasks, so I could do the work I love. Not something that takes over the work I love, and botches that too.
P.S. This is a 4-second shot I made in 2023 for Paramount Students. I just added the labels AI and SI on top, and see how perfectly it fits, picturing another ERA OF HYPE SELLING!


Si is coming sooner than expected.

Building a digital experience that feel as good as it works



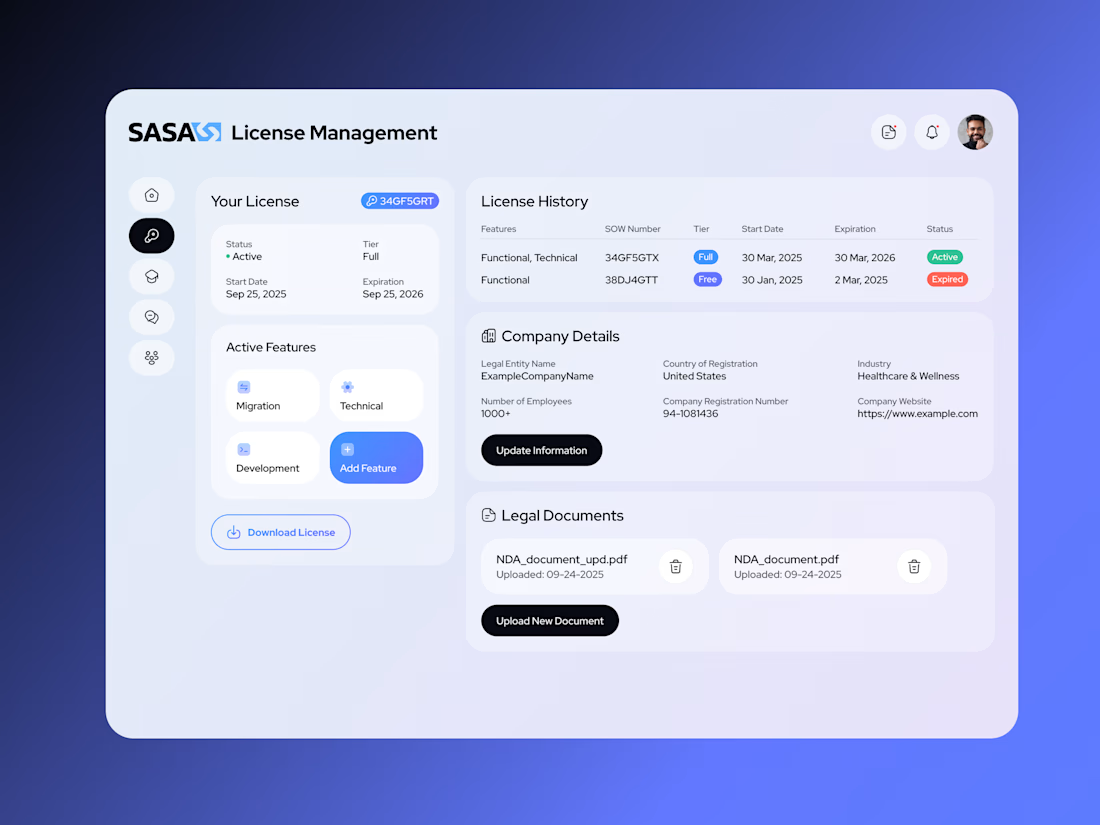
The engineering side of a B2B customer portal — designed by [@Anna Peredelskaia ]
The portal brings license management, product training, paid certifications and technical support into one place for a company's B2B clients. Anna designed the experience; I built the MVP.
My main focus was access control. Each client company has several roles, and every role should see and do only what it needs.
• Auth flow: work-email check → client-domain match → MFA
• Role-based UI across 7+ roles — employee, manager, billing, HR, admin, super admin, client admin
• Roles stored as custom claims, set by a backend function only after it validates the data
• Every protected action checked against both the auth claims and the stored record
• Writes only through API routes with verification and idempotency; database rules as a second layer
• Paid certifications on Stripe: verified webhooks, deduplicated events, idempotent processing
Stack: Next.js, TypeScript, Firebase Auth, Firestore, Cloud Functions, Stripe.
Good design makes a portal easy to use. Solid access control makes it safe to use.