The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

During a security assessment of a practice web application, I discovered an exposed FTP directory with directory listing enabled, revealing multiple sensitive files including a password database, backup configurations, compiled source code, and error logs. After finding a clue in robots.txt, I navigated to the /ftp directory and documented over ten exposed files with their associated risks. My final report included an executive summary, detailed findings with screenshots, risk ratings for each exposed file, and step-by-step remediation guidance including disabling directory listing and removing sensitive data. This finding highlights how simple misconfigurations can lead to critical data exposure.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started

Challenges
View all


Related posts

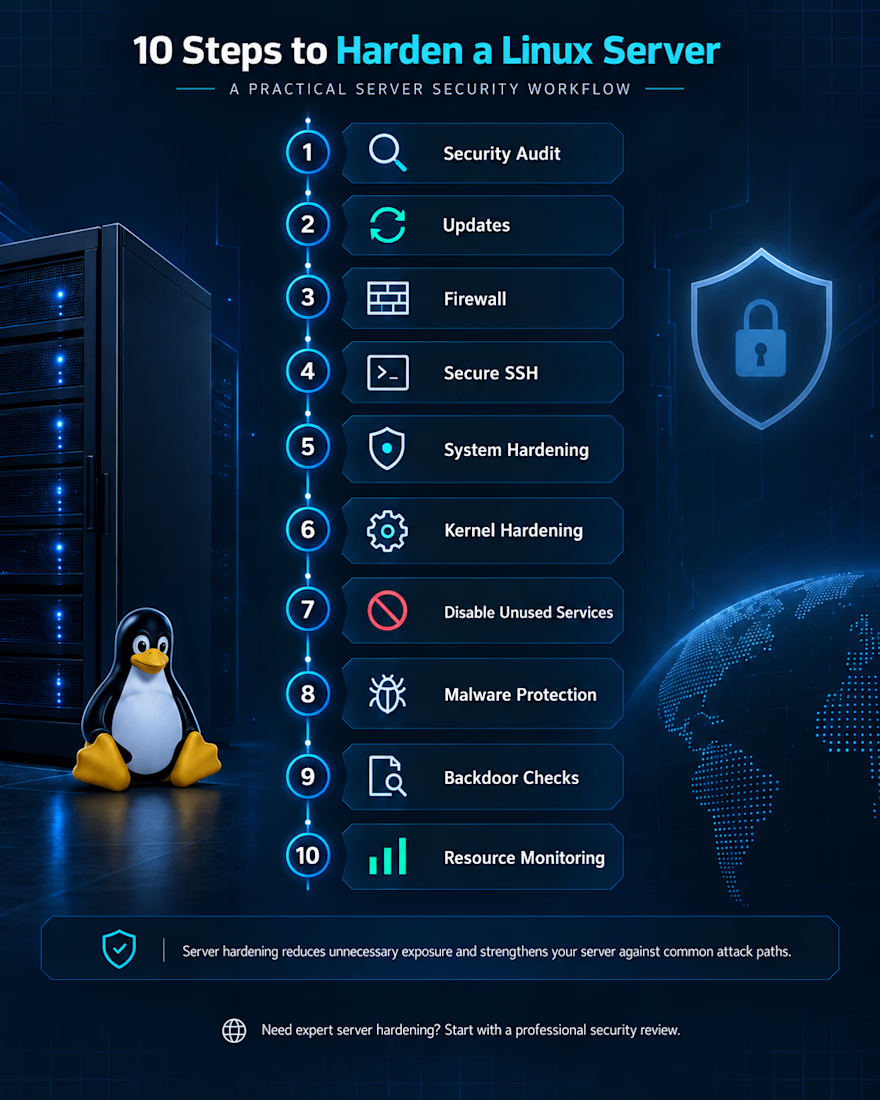
10 Essential Steps to Harden a Linux Server
Server security goes far beyond simply installing an operating system and setting a password.
A properly hardened Linux server reduces unnecessary exposure and makes common attack paths more difficult to exploit.
The process usually starts with a security audit, system updates, and reviewing open ports.
Firewall rules and secure SSH configuration help control who can access the server.
Unused services should be disabled, while system and kernel settings need to be reviewed carefully.
Regular malware and backdoor checks add another important layer of protection.
Continuous resource and activity monitoring can also help identify unusual behavior early.
A strong hardening process creates a much safer foundation for websites, applications, and business infrastructure.
Learn more about server hardening at https://serverly.host/other-services/server-hardening/
#ServerHardening #LinuxSecurity #ServerSecurity #CyberSecurity #LinuxServer #CloudSecurity #SysAdmin


A quick sneak peek at my new "cybersecurity template."
It's GATEHIVE...
15 pages, blog CMS, fully responsive, subtle animations, and a clean, professional visual direction.
Still polishing a few things before it goes live on the Framer Marketplace.
Here’s a little preview.
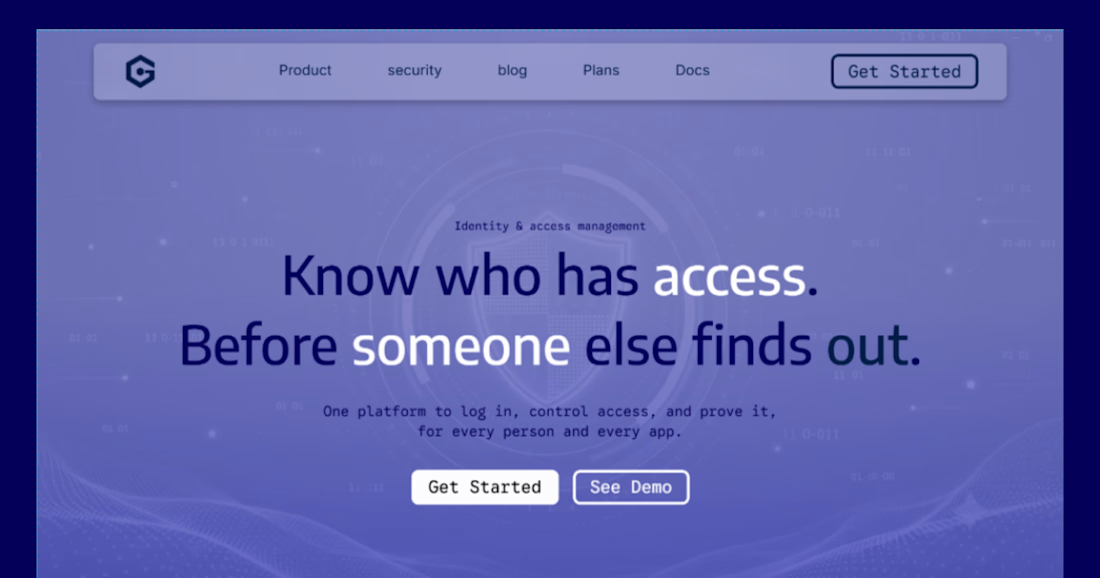

“Know who has access” is a stronger opener than a lock icon and a threat headline. The quiet purple nav already reads like a real product, which is the hard part of a cybersecurity template.


Yora is a cloud-based cyber security platform that helps you clean, monitor, and protect your website from malware, threats, and vulnerabilities with real-time detection, automated defense, and centralized security management.